GitHub CodeQL
GitHub CodeQL: Deep SAST for GitHub workflows, with free public-repository scanning. Ranked #3 of 26 in SAST Tools by our editors (9.0/10); pricing: Free plan; best for gitHub-centric development teams.
At a glance
- Editor score9.0 / 10
- PricingFree plan
- Best forGitHub-centric development teams
- Free planYes
- Paid from$30/user/mo
- Pull request scansYes
- Facts checked21 Sep 2026
Where it wins
- Semantic queries detect vulnerabilities and coding errors.
- Pull-request, GitHub Actions, and external CI scanning.
- Custom queries and SARIF support for tailored analysis.
Where it doesn't
- Private-repository scanning requires paid GitHub Code Security.
- Paid pricing is based on unique active committers.
- The feature set is centered on source-code analysis.
Our verdict on GitHub CodeQL
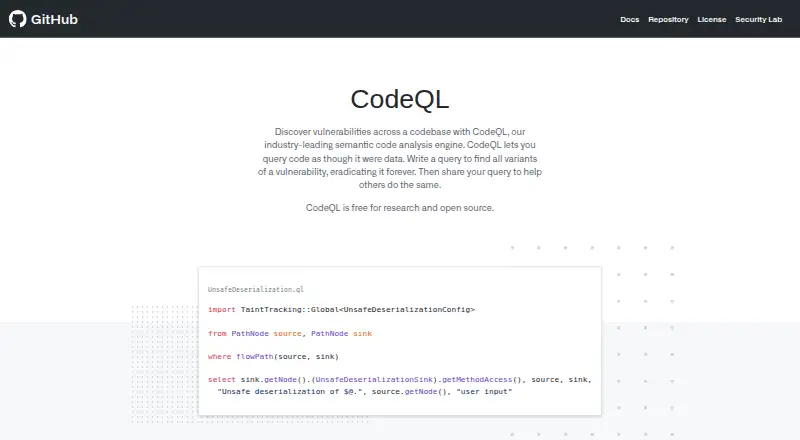
GitHub CodeQL is a semantic static-analysis engine for finding security vulnerabilities, coding errors, and other issues in source code. It represents code as data and queries that representation, giving development and security teams a way to scan repositories, pull requests, and CI workflows. It is particularly suited to GitHub-centric teams that want code-scanning alerts in GitHub, while also supporting local analysis through the CodeQL CLI and Visual Studio Code.
Pricing is split between public and eligible private repositories. Code scanning with CodeQL is available free of charge for public repositories. For eligible private repositories, GitHub Code Security starts at $30 per active committer per month, billed monthly, with billing based on unique active committers. The product connects with GitHub Actions, Azure DevOps, external CI systems, and Visual Studio Code. Teams can generate and upload SARIF results, integrate the CodeQL CLI into external CI, and view findings through GitHub code-scanning alerts.
Its standout capability is query-based analysis: teams can author custom CodeQL queries alongside the published vulnerability and coding-error detection. Pull-request scanning, CI/CD integration, IDE support, and coverage across nine listed programming-language entries support workflows from development through review. Choose CodeQL when semantic analysis, custom rules, and GitHub workflow integration are priorities. Teams that need private-repository coverage should account for the per-active-committer license, while public repositories receive the strongest pricing advantage.
Your product? Our editors can test GitHub CodeQL in depth and publish a review, labelled as paid · from $149/mo →
GitHub CodeQL pricing
All 2 GitHub CodeQL plans and prices →
GitHub CodeQL fact sheet
| Free plan | Yes |
|---|---|
| Paid from | $30/user/mo |
| Analysis targets | source code |
| Languages supported | 11 |
| Pull request scans | Yes |
| IDE support | Yes |
| CI/CD integration | Yes |
| Custom security rules | Yes |
| Automated fixes | Yes |
| Deployment | Cloud, Desktop |
| Platforms | Web, Windows, macOS, Linux |
| Support | Docs |
| Built for | Small business, Mid-market, Enterprise (editorial estimate) |
| Integrations | 4 integrations: GitHub Actions, Visual Studio Code, External CI/CD systems, GitHub code scanning |
| Pricing | Free plan (source) |
| Website | codeql.github.com |
| Facts checked | 21 Sep 2026 |
GitHub CodeQL integrations
GitHub CodeQL lists 4 integrations on its own site.
- GitHub Actions
- Visual Studio Code
- External CI/CD systems
- GitHub code scanning
Alternatives to GitHub CodeQL
- Semgrep CodeBroad SAST coverage with pull-request, CI/CD, IDE, custom-rule, and AI-assisted workflows.9.4
- Snyk CodeAffordable source-code SAST with pull-request, IDE, CI/CD, and automated-fix workflows.9.2
- OpenText Fortify SASTBroad SAST coverage for enterprises, with sales-led pricing and extensive workflow integrations.8.8
See all GitHub CodeQL alternatives →
GitHub CodeQL vs the competition
- GitHub CodeQL vs Semgrep Code
- GitHub CodeQL vs Snyk Code
- GitHub CodeQL vs OpenText Fortify SAST
- GitHub CodeQL vs Veracode Static Analysis
- GitHub CodeQL vs Klocwork
- GitHub CodeQL vs DerScanner
Compare GitHub CodeQL with any tool side by side →
Also Ranked In
GitHub CodeQL is ranked in 41 of our directories; the 6 strongest besides SAST Tools.
Used GitHub CodeQL? Be the first to review it
The editor score above is our own research. What this page doesn't have yet is a reader's view — what you used GitHub CodeQL for, what worked and what didn't. No stars are seeded and no review is paid for; an editor reads every one before it appears.
Write a reviewTwo minutes · verified accounts only · read by an editor before it appears
Featured on iTechGuides
GitHub CodeQL is listed in our SAST Tools directory. Add the badge to your site — it links back to this page.
<a href="https://www.itechguides.com/products/github-codeql/"><img src="https://www.itechguides.com/best/badge/github-codeql.svg" alt="Featured on iTechGuides" width="230" height="46"></a>
Reviewed by iTechGuides Editors · Editorial team · Updated Oct 2026
Advertiser disclosure: iTechGuides is reader-supported. Vendors can pay for top positions in our rankings and for a place on other products' pages, and we may earn a commission when you click some links. Bought places stand at the number bought; this page and our disclosure say so. Paying vendors may get a fuller, more detailed review from our editors, and that review can change their score. How we rank.
Last updated · How we research and update