
iTechGuides is reader-supported. When you buy through links on our site, we may earn an affiliate commission. As an Amazon Associate I earn from qualifying purchases. Learn more
First, run the same speed test with the VPN disconnected and connected. If the connection is slow in both tests, fix the ISP, Wi‑Fi, or local network before changing VPN settings. If the connection is fast without the VPN but slow inside the tunnel, test a nearer server, a different protocol (preferably WireGuard or OpenVPN over UDP), MTU settings, device or router capacity, routing, and DNS—changing one variable at a time.
Why a VPN can make internet access slower
A VPN encrypts traffic on your device, sends it through an intermediate VPN server, and then forwards it to the destination. That adds processing and an extra network path. The server may be farther away, congested, or connected to the internet through a less efficient route than your normal connection. Encryption can also consume CPU on a computer, phone, router, or travel router.
Some slowdown is therefore expected, but there is no provider-neutral percentage that applies to every device, protocol, server, and access link. A large drop is a troubleshooting signal rather than a number you should accept automatically. The useful question is whether the loss appears only when the tunnel is active and which part of the path is responsible.
The Tool Desk
Outbyte PC Repair FREEClear out junk files and repair common Windows errorsFree Scan →Outbyte Driver Updater FREEScan for outdated or missing drivers - takes under a minuteDriver Scan →Start with a controlled before-and-after test
Do not change settings until you have a baseline. Use the same device, Wi‑Fi or Ethernet connection, test endpoint, and time window for both measurements. Close heavy downloads, video streams, cloud backups, and other VPN clients first.
#1 Best Overall
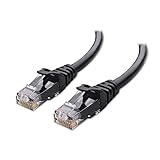
- High-Performance Connectivity: This Cat 6 ethernet cable is designed for superior performance, with a 24 AWG copper wire core. It provides universal connectivity as an ethernet cord for LAN network components such as PCs, servers, printers, routers, and more, ensuring reliable and fast network connections
- Advanced Cat6 Technology: Experience Cat6 performance with higher bandwidth at a Cat5e price. This network cable is future-proof, ready for 10-Gigabit Ethernet and backwards compatible with any existing Cat 5 cable network. It meets or exceeds Category 6 performance according to the TIA/EIA 568-C.2 standard
- Reliable Wired Network Solution: Known variously as a Cat6 network cable, ethernet cable Cat 6, or Cat 6 data/LAN cable, this RJ45 cable offers a more secure and reliable connection than wireless networks. It's ideal for internet connections that demand consistency and security
- Durable and Secure Design: The connectors of this ethernet cable feature gold-plated contacts and strain-relief boots for enhanced durability. Bare copper conductors not only improve cable performance but also comply with communication cable specifications
- High-Speed Data Transfer: With up to 550 MHz bandwidth, this ethernet cord is ideal for server applications, cloud computing, video surveillance, and streaming high-definition video. It also supports Power over Ethernet (PoE, PoE+, PoE++) for powering devices like IP cameras, VoIP phones, and wireless access points, ensuring fast and reliable network performance.
- Disconnect the VPN and run a speed test. Record download speed, upload speed, latency, and any packet-loss indicator the test provides.
- Connect the VPN without changing anything else, then run the same test again.
- Repeat each state once or twice if the results fluctuate sharply. Use the median result rather than the single highest or lowest reading.
- Write down the VPN server location, protocol, transport (UDP or TCP), device, and whether the test used Wi‑Fi or Ethernet.
| Result | Most likely area | What to do next |
|---|---|---|
| Slow with VPN off and on | ISP service, modem, Wi‑Fi, local congestion, or the test endpoint | Stabilize the raw connection first; VPN changes cannot repair a slow access link. |
| Fast off, slow on | VPN server path, protocol, encryption capacity, MTU, routing, or DNS | Continue with the VPN-specific sequence below. |
| Download falls but upload is similar | Server congestion, route asymmetry, or downstream capacity | Compare a nearer server and another protocol. |
| Latency rises sharply while throughput remains acceptable | Server distance, queueing, or an indirect route | Choose a geographically nearer endpoint and check congestion at different times. |
A wired test is valuable because weak or crowded Wi‑Fi can look like VPN overhead. Temporarily connect the computer or router to the gateway with a Cat 6 Ethernet cable, or another known-good Ethernet cable, and repeat the two-state test. The cable only isolates the wireless link; it cannot fix a distant or overloaded VPN server, a protocol mismatch, an MTU error, or an ISP limit.
Fix the VPN path in the order most likely to help
1. Choose a closer or less congested server
Open the VPN app’s server list and select a location geographically near you, then test it. Distance increases the number of milliseconds needed for packets to travel and often adds network hops. A nearby endpoint is usually the best starting point for ordinary browsing, calls, and downloads.
If the nearest location is still slow, test another nearby city or a second server in the same country. A server can be temporarily busy even when the location itself is close. Compare observed latency and throughput, not the city name alone. If the app displays a load, latency, or “recommended” indicator, treat it as a starting point and verify it with your own test.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
- Record the current server and its baseline results.
- Disconnect and select the nearest available location.
- Reconnect and run the identical test.
- Try one additional nearby location if the first change does not help.
A distant server can still be appropriate when you need an address in that region, but you should expect the longer route to affect latency. If privacy is the goal rather than a specific exit country, distance and measured performance should carry more weight than a particular city.
2. Compare protocols and transports
Protocol choice affects encryption overhead, connection setup, packet handling, and how loss is recovered. In a VPN app, open Settings or Preferences, find Protocol or Connection protocol, and test each supported option separately.
Rank #2

- Cat 6 performance at a Cat5e price but with higher bandwidth
- High Performance Cat6, 30 AWG, RJ45 Ethernet Patch Cable provides universal connectivity for LAN network components such as PCs,computer servers,printers,routers,switch boxes,network media players,NAS,VoIP phones
- Jadaol cat6 standard cable support Cat8 and Cat7 network and provides performance of up to 250 MHz 10Gbps and is suitable for 10BASE-T, 100BASE-TX (Fast Ethernet), 1000BASE-T/1000BASE-TX (Gigabit Ethernet) and 10GBASE-T (10-Gigabit Ethernet)
- UTP(Unshielded Twisted Pair) patch cable with RJ45 gold-plated Connectors and are made of 100% bare copper wire, ensure minimal noise and interference
- The unique flat cable shape allows for a cleaner and safer installation. You can easily and seamlessly make the cable run along walls, follow edges & corners or even make it completely invisible by sliding it under a carpet.
| Option | When to test it | Trade-offs |
|---|---|---|
| WireGuard | First comparison when the client supports it | Generally efficient and often faster than OpenVPN, but availability and implementation vary by client and router. |
| OpenVPN over UDP | When OpenVPN is required or WireGuard is unavailable | Usually avoids the extra retransmission behavior of TCP; UDP may be blocked on some networks. |
| OpenVPN over TCP | When UDP cannot connect or a restrictive network requires TCP | More compatible in some environments, but TCP-over-TCP can create the “TCP meltdown phenomenon,” adding delay and reducing performance. |
Do not assume that a protocol label guarantees a result. Test throughput and latency on your connection. If WireGuard is available, compare it with OpenVPN over UDP before trying TCP. If OpenVPN over TCP is the only option that connects, accept that its reliability on a restrictive network may come with lower throughput.
3. Check MTU and fragmentation
MTU is the largest packet an interface or tunnel can carry without splitting it. A VPN adds encapsulation headers, so a packet that fit on the ordinary connection may no longer fit inside the tunnel. When the path cannot fragment or reassemble it correctly, packets are retransmitted or dropped.
The classic symptom is that small pages or pings work while large downloads, uploads, video calls, or particular websites stall. An MTU problem can also appear as intermittent speed, long pauses, or a tunnel that connects successfully but performs poorly.
- Confirm that the symptom is size-dependent by comparing a small request with a large transfer or upload.
- Check the VPN client’s documented advanced networking controls for MTU, MSS, or packet-size settings. Router administrators should use the firmware’s documented VPN or WAN controls.
- Make one conservative change at a time; do not copy an MTU value from a different access technology or tunnel.
- Reconnect the tunnel and repeat the same speed test and large-transfer check.
- Restore the previous value if performance or compatibility worsens.
Do not edit configuration files or force a value when the client or router does not document the setting. The correct value depends on the access link, encapsulation, and path, so a universal “best MTU” number does not exist.
4. Check CPU, router capacity, and hardware acceleration
Encryption and packet processing use CPU cycles. A fast broadband subscription can therefore overwhelm an older laptop, phone, home router, or travel router when the VPN is terminated locally. The bottleneck may be more obvious on a router because every connected device shares the same processor and memory.
Rank #3

- 40 Gbps 2000 Mhz High Speed: The Cat 8 ethernet cable support max. 40 Gbps data transfer and 2000 MHz Brandwith, ideal for gaming and streaming, greatly improving upload and download speed, sound, image and resolution quality
- Excellent Anti-interference: The ethernet cable comes with 4 shielded foiled twisted pairs (F/FTP), pure copper core and gold-plated RJ45 connector, reducing interference, noise and crosstalk, making network speed faster and more stable
- Marvelous Durability: Internet cable wrapped with quality cotton braided cord, which makes the LAN cable stronger and more durable. The test proves that this internet cable can be bent at least 10000 times without broken, very suitable for long-term use
- PoE Supported: All lengths of ethernet cord can support the PoE power supply function except 65ft. You don't need additional power supply when installing a PoE camera, which is very convenient and safe
- Wide Compatibility: With the RJ45 Connector, network cable can be perfectly compatible with computers, laptops, modems, routers, PS5, X-Box and other networking devices. It can also be fully backward compatible with Cat7, Cat6e, Cat6, Cat5e, Cat5
- While a VPN speed test runs, watch CPU utilization on the computer or router if its administration interface exposes that metric.
- Check whether the VPN implementation supports hardware acceleration or a data-channel offload feature, and enable it only through documented settings.
- On a router, compare VPN throughput with the router’s normal routed throughput. A large gap points to encryption capacity or firmware limitations.
- Pause other high-bandwidth clients and repeat the test to rule out local contention.
- Update router firmware and the VPN client when a supported, stable release is available, then retest rather than assuming an update solved the issue.
Router-based VPNs centralize protection for every device, but they also make the router’s CPU, memory, firmware, and VPN implementation the shared bottleneck. A device-based tunnel can be faster when the computer or phone has more processing headroom; a router-based tunnel can be preferable when every device must follow the same policy. Measure both designs if your hardware supports them.
Recommended Free Tools
5. Use split tunneling when full tunneling is unnecessary
Full tunneling sends ordinary public internet traffic through the VPN server. That provides broader coverage, but it also adds the VPN server’s load, egress path, and geographic detour to traffic that may not need protection. Split tunneling routes only selected applications, destinations, or private resources through the VPN and sends the rest directly.
Open the client’s Split tunneling, App exclusion, or similarly named setting. Add only the applications or private networks that require the tunnel, then verify which traffic is protected. The exact controls differ by operating system and client.
| Design | Privacy coverage | Performance and DNS implications |
|---|---|---|
| Full tunnel | All eligible traffic uses the VPN | More traffic traverses the VPN; server load, route length, and VPN DNS affect everything. |
| Split tunnel | Only selected apps or networks use the VPN | Direct traffic avoids the VPN path, but some traffic and DNS queries may no longer receive VPN protection. |
Split tunneling is a performance tool, not a free speed setting. Excluded applications can reveal the device’s normal IP address, use the ISP’s DNS, or bypass an organizational policy. Decide which consequence is acceptable before enabling it.
6. Review DNS and routing
Throughput can be healthy while browsing feels slow because name lookups or route selection are wrong. When all client internet traffic is routed through a VPN, the client generally needs the VPN server’s DNS servers or explicitly configured servers. Split-DNS configurations can send selected domains to VPN-provided DNS while resolving other names normally.
Rank #4
- High-Performance Connectivity: This Cat 6 ethernet cable is designed for superior performance, with a 24 AWG copper wire core. It provides universal connectivity as an ethernet cord for LAN network components such as PCs, servers, printers, routers, and more, ensuring reliable and fast network connections
- Advanced Cat6 Technology: Experience Cat6 performance with higher bandwidth at a Cat5e price. This network cable is future-proof, ready for 10-Gigabit Ethernet and backwards compatible with any existing Cat 5 cable network. It meets or exceeds Category 6 performance according to the TIA/EIA 568-C.2 standard
- Reliable Wired Network Solution: Known variously as a Cat6 network cable, ethernet cable Cat 6, or Cat 6 data/LAN cable, this RJ45 cable offers a more secure and reliable connection than wireless networks. It's ideal for internet connections that demand consistency and security
- Durable and Secure Design: The connectors of this ethernet cable feature gold-plated contacts and strain-relief boots for enhanced durability. Bare copper conductors not only improve cable performance but also comply with communication cable specifications
- High-Speed Data Transfer: With up to 550 MHz bandwidth, this ethernet cord is ideal for server applications, cloud computing, video surveillance, and streaming high-definition video. It also supports Power over Ethernet (PoE, PoE+, PoE++) for powering devices like IP cameras, VoIP phones, and wireless access points, ensuring fast and reliable network performance.
Check the VPN connection details and the operating system’s active DNS and route tables while connected and disconnected. Look for these failure patterns:
- Websites take a long time to begin loading, but a direct IP or an already open connection transfers quickly: DNS delay is a possibility.
- Private names resolve only when the VPN is connected: the private zone must use the VPN DNS path.
- Some sites work while others time out: an incorrect route, DNS split, or unreachable IPv4/IPv6 path may be involved.
- All traffic leaves through the VPN even when you intended exceptions: the split-tunnel routes are incomplete or overridden by a full-tunnel rule.
Use the VPN client’s documented DNS and routing controls rather than manually replacing settings at random. After every change, verify both name resolution and the public address seen by an application that should be inside or outside the tunnel.
7. Retest after every change
Change one variable, reconnect if necessary, and run the same test. Record the server, protocol, transport, MTU or MSS value, connection type, and results. Testing a new server and a new protocol simultaneously may produce a better number, but it prevents you from knowing which change helped and makes a later regression harder to diagnose.
Keep the test endpoint and device constant. A speed-test server can itself be busy, and internet conditions vary by time of day. If a result is surprising, repeat it rather than comparing unrelated tests from different locations or networks.
Use symptoms to narrow the cause
| Symptom | Likely causes | First checks |
|---|---|---|
| Everything is slow, including ordinary sites | Slow raw link, distant or congested server, protocol overhead | Run the VPN-off baseline, choose a nearer server, compare WireGuard and OpenVPN UDP. |
| Small pages load but large files stall | MTU mismatch, fragmentation, packet loss | Check documented MTU/MSS controls and test a large transfer after each adjustment. |
| Speed falls only on Wi‑Fi | Wireless interference, weak signal, local congestion | Repeat on Ethernet; move closer to the access point or fix Wi‑Fi before judging the VPN. |
| Router VPN is much slower than a laptop VPN | Router CPU, memory, firmware, or VPN implementation | Check router utilization, hardware acceleration, firmware, and device-based performance. |
| Browsing is slow but a transfer already in progress is fast | DNS or route selection | Compare active DNS servers and routes inside and outside the tunnel. |
| Only TCP mode is reliable on one network | UDP blocked or filtered | Use OpenVPN TCP if required, but expect possible TCP-over-TCP performance loss. |
Full-tunnel, split-tunnel, router, or device: choosing the right design
The fastest configuration is not automatically the most appropriate. Decide where encryption should occur and which traffic must be covered.
Best Value

- High Performance Cat6 Cable - The Cat6 ethernet cables 100ft supports frequencies of up to 500 MHz and high-speed 10GB internet connection for LAN network applications such as PCs,computer servers,printers,routers,switch boxes,network media players,NAS,VoIP phones and more, while remaining fully backward compatible with your existing network.
- Outdoor&Indoor Ethernet Cable - The cat 6 ethernet patch cable features 8 solid copper conductors 24 AWG. Each of the 4 unshielded twisted pairs (UTP) are separated by a PE cross insulation to isolates pairs and prevent crosstalk and covered by a 5.8mm PVC jacket with RJ45 connectors and gold-plated contacts. The molded strain relief boots help avoid snags that will damage your cables. They are molded for flexibility and resist common wear and tear.
- Lan Cable with RJ45 - UTP(Unshielded Twisted Pair) patch cable with RJ45 gold-plated Connectors, this cat6 cable support Cat8 and Cat7 network and provides performance of up to 500 MHz 10Gbps and is suitable for 10BASE-T, 100BASE-TX (Fast Ethernet), 1000BASE-T/1000BASE-TX (Gigabit Ethernet) and 10GBASE-T (10-Gigabit Ethernet)
- High Quality Control - are designed with extremely well-matched components for outstanding uniform impedance and very low return loss, providing lower crosstalk, and a higher signal-to-noise ratio. Each Cat 6 internet cable 6 ft goes through rigorous testing to ensure a secure wired internet connection with exceptional speed and reliability.
- Support – Cat6 Ethernet cable with CM grade PVC jacket complies with TIA/EIA 568-C.2, is ETL verified and RoHS compliant. If an item is defective or breaks within a year, we will issue a replacement. For questions or concerns please contact our friendly, USA-based customer Support team.
| Approach | Best fit | Main performance constraint | Important caveat |
|---|---|---|---|
| VPN app on one device | A single computer or phone needs protection | That device’s CPU and the chosen server path | Other devices remain outside the tunnel. |
| VPN on the home or travel router | Many devices need one policy | Router CPU, memory, firmware, and VPN acceleration | One weak router can slow every client. |
| Full tunnel | All eligible traffic must use the VPN | Server load, route length, encryption, DNS | More traffic and DNS queries traverse the VPN. |
| Split tunnel | Only selected apps or private resources need the VPN | Rules and route correctness | Excluded traffic may use the normal IP address and DNS. |
When the VPN is not the real problem
If the VPN-off measurement is already poor, troubleshoot the access connection first. Restart the modem or router, test near the access point, try Ethernet, pause competing traffic, and compare at another time. Persistent slowness in both states belongs with the ISP or local-network investigation, not with VPN protocol tuning.
If the raw link is fast but every VPN server and protocol is slow, inspect CPU utilization, router limits, MTU behavior, packet loss, and the VPN account or server configuration. OpenVPN’s diagnostic guidance groups limited bandwidth, high CPU use, insufficient encryption performance, packet loss or high latency, TCP transport behavior, MTU fragmentation, incorrect routing, and unnecessary network hops among the common causes.
Safe troubleshooting checklist
- Measure with the VPN off and on using the same endpoint and device.
- Confirm whether Ethernet changes the result.
- Try the nearest available server, then one alternative nearby server.
- Compare WireGuard with OpenVPN over UDP when supported.
- Use OpenVPN over TCP only when compatibility requires it.
- Investigate MTU or MSS only through documented client or router controls.
- Watch CPU and memory on the device or router during a test.
- Check firmware, hardware acceleration, routes, and DNS behavior.
- Use split tunneling only after deciding which traffic and DNS queries may bypass the VPN.
- Retest after every single change and keep a record of the result.
What to do when none of the changes help
Compile the baseline and retest notes before contacting the VPN provider, network administrator, or ISP. Include the VPN-off and VPN-on speeds, latency, packet-loss observations, server locations, protocols, transport modes, device model, router model and firmware, wired or wireless status, and any MTU or split-tunnel changes. This information distinguishes a congested endpoint from a local encryption bottleneck and gives support a reproducible comparison.
Quick wins for a faster PC:
Clear out junk files and repair common Windows errorsFree Scan →Fix the driver behind crashes, sound loss and screen glitchesFind Drivers →Repair Windows errors before they cause bigger problemsFix Now →Do not treat a single excellent result as proof that the problem is solved. A server can be temporarily less busy, an ISP route can change, or Wi‑Fi conditions can improve. The fix is credible when the same controlled test remains better after reconnecting and at more than one time.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

