
Free tools Windows power users keep installed
One-click scans. No signup required.
iTechGuides is reader-supported. When you buy through links on our site, we may earn an affiliate commission. As an Amazon Associate I earn from qualifying purchases. Learn more
Short answer: The headline was based on a real discovery of exposed credential datasets, but it did not describe one new breach containing 16 billion unique passwords. Cybernews reported finding 30 exposed datasets containing approximately 16 billion raw records. The records were not deduplicated, and the total may include repeated, outdated, invalid, non-credential, and mixed personal-data records.
There is no public evidence that Apple, Google, Facebook, Meta, or another major platform suffered one centralized breach producing that total. The material appears to have been assembled from multiple thefts, infostealer logs, older breach compilations, and exposed databases. The risk is still serious: some records may contain working passwords, browser cookies, or session tokens that can enable account takeover.
The accurate version of the 16-billion-password story
Cybernews originally published its report on June 18, 2025, saying researchers had identified 30 exposed datasets totaling about 16 billion records. The datasets ranged from tens of millions of records to more than 3.5 billion records in one collection. Cybernews updated its reporting several times through June 25, 2025. Its own description included infostealer logs, credential-stuffing collections, and recycled data rather than a single newly created database. Read Cybernews’s original report.
The Associated Press characterized the material as data stolen during multiple events over time, then compiled and briefly exposed publicly. It also noted that duplicates made it impossible to determine how many people or accounts were actually affected. The AP’s account of the incident is a useful independent summary.
#1 Best Overall

- Secure, Private Browsing Anywhere You Go - Protect your personal data with a portable privacy browser that keeps your online activity private and secure. Designed for use on public or shared computers, it helps prevent tracking, data theft, and unwanted access. Ideal for travel, work, or everyday privacy needs.
- All-in-One Privacy Toolkit on a USB Drive - This portable browser combines a private browser, an anonymous browser, and password manager in one convenient solution. Store sensitive files, login credentials, and personal data safely in one place. Everything you need for digital privacy travels with you.
- Built-In Password Manager for Easy Access - Manage and store your usernames and passwords securely with the integrated password manager. Because the portable web browser is private, it does not store any personal data or passwords. Easily import existing login credentials and access them whenever needed. Simplifies secure logins without compromising safety.
- Portable USB Drive with Browser - Includes a 32GB USB drive to securely store files, documents, and personal information. Advanced encryption capability helps protect your data from unauthorized access. Perfect for safeguarding sensitive content on the go.
- Designed for Windows – Simple Plug & Play Setup. Built specifically for Windows computers, ensuring smooth performance and reliable functionality. No complicated installation—just plug in the USB and launch the software instantly. A straightforward, dependable privacy solution for Windows users at home, work, or on the go.
| Sensational wording | More accurate wording |
|---|---|
| 16 billion passwords | Approximately 16 billion raw records across 30 exposed datasets |
| One colossal breach | Multiple thefts, collections, and exposed databases assembled together |
| 16 billion people were affected | The number of unique people and accounts is unknown |
| Apple, Google, and Facebook were hacked | Records associated with those services appeared in mixed datasets |
| All the information was newly stolen | The collections included older, duplicated, recycled, and possibly current data |
So the most defensible description is: a large exposed compilation of credentials and other datasets, collected from multiple sources over time, with an unknown amount of duplication, stale information, non-credential data, and currently valid material.
Was this one breach or many?
These terms describe different events, and the distinction matters:
- A company breach: An attacker breaks into one organization and steals data from that organization’s systems.
- A stealer-log collection: Infostealer malware takes information from many infected computers or phones and sends it to criminals. The victims may use dozens of unrelated websites.
- A breach compilation: Someone combines records from older breaches, criminal marketplaces, Telegram channels, infostealer logs, and previous public exposures.
- An exposed database: A collection is left accessible because infrastructure such as an Elasticsearch instance, cloud storage bucket, or similar service is misconfigured or insufficiently protected.
The June 2025 story involved the latter three categories much more than the first. Cybernews identified 30 separate datasets; the AP described multiple theft events followed by compilation and exposure. A CERT-EU Cyber Brief likewise treated the event as a repackaged compilation rather than evidence of one new breach at a central technology provider.
That means the phrase data breach is not entirely wrong in the broad sense, but calling it one 16-billion-password breach gives readers the wrong idea about where the data came from and who must respond.
What does 16 billion actually count?
It is best understood as a raw record count, not a count of users, accounts, or unique passwords. A single record might contain:
- A login URL, username or email address, and password.
- A duplicate of the same login appearing in another collection.
- An old password that has since been changed.
- A cookie or active session token rather than a password.
- Autofill details, browser metadata, or other information taken from a device.
- A personal-data or social-profile record with no login credential at all.
- A record copied, reformatted, or resold multiple times.
- A credential for an account that has been deleted, disabled, or reset.
Cybernews acknowledged that it could not effectively compare all 30 datasets and that overlap was definitely present. Independent researcher JayeLTee reported finding datasets included in the calculation that contained social-profile or personal records but no login credentials, and identified links to older leaks and Telegram compilations. That analysis is an independent critique, not a complete audit of every dataset, but it reinforces why the 16-billion figure should not be presented as 16 billion passwords. Read JayeLTee’s analysis.
Cybernews also said one collection containing approximately 184 million records had already been reported elsewhere, and reported that the largest newly discussed dataset exceeded 3.5 billion records. Those figures describe the size of collections, not the number of individuals whose current accounts were compromised.
Quick wins for a faster PC:
Repair Windows errors before they cause bigger problemsFix Now →Scan for outdated or missing drivers - takes under a minuteDriver Scan →Were Apple, Google, or Facebook hacked?
No centralized breach of Apple, Google, Facebook, or Meta was established by this report. Samples apparently included login URLs or credentials associated with services such as Apple, Google, Facebook, GitHub, Telegram, Zoom, Twitch, VPN providers, corporate tools, and government platforms. That tells us which services the exposed credentials may access. It does not tell us that those companies’ password databases were the source of the theft.
A useful way to think about it is:
Seeing
google.com,facebook.com, orapple.comin a stealer log identifies the service a captured credential may access. It does not identify that service as the place where the credential was stolen.
A user might have entered a password into a phishing page, logged in on a computer infected with an infostealer, or reused the password on a smaller website that was breached. Google separately told Axios that the incident did not stem from a Google data breach, while researcher Bob Diachenko said there was no centralized breach at the named companies. Axios’s report includes Google’s response and its later clarification of the headline.
Rank #2
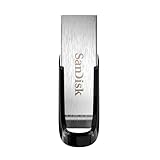
- High-speed USB 3.0 performance of up to 150MB/s(1) [(1) Write to drive up to 15x faster than standard USB 2.0 drives (4MB/s); varies by drive capacity. Up to 150MB/s read speed. USB 3.0 port required. Based on internal testing; performance may be lower depending on host device, usage conditions, and other factors; 1MB=1,000,000 bytes]
- Transfer a full-length movie in less than 30 seconds(2) [(2) Based on 1.2GB MPEG-4 video transfer with USB 3.0 host device. Results may vary based on host device, file attributes and other factors]
- Transfer to drive up to 15 times faster than standard USB 2.0 drives(1)
- Sleek, durable metal casing
- Easy-to-use password protection for your private files(3) [(3)Password protection uses 128-bit AES encryption and is supported by Windows 7, Windows 8, Windows 10, and Mac OS X v10.9 plus; Software download required for Mac, visit the SanDisk SecureAccess support page]
How infostealers turn an infected device into an account risk
Infostealers are malware designed to extract information from an infected device. Depending on the malware and the operating system, the stolen material can include:
- Passwords saved in a web browser.
- Autofill information and browser history.
- Cookies and active authentication sessions.
- Email, VPN, corporate, and developer credentials.
- Cloud-access tokens and cryptocurrency-wallet information.
- Local documents and other metadata.
Many records in the reported collections followed a format similar to URL:username:password, which is commonly associated with infostealer logs. Cybernews also warned that some collections contained cookies, tokens, and metadata. Cybernews explains the observed formats and data types.
The practical consequence is important: this may be a device-security problem, not just a website-security problem. If malware is still active, changing a password on the infected computer can simply provide the attacker with the replacement password. An infected browser may also retain a valid session even after the password is changed.
A typical theft chain looks like this:
infected device → browser passwords, autofill, cookies, or tokens stolen → stealer log or criminal collection → compilation or exposed database → credential stuffing, phishing, or account takeover
Why old credentials can still be dangerous
An old credential is not automatically harmless. It remains useful when:
Recommended Free Tools
- The password is still used on the original service.
- The same password, or a predictable variation, is used elsewhere.
- The affected email account is still active.
- The account does not have effective MFA.
- An attacker has a valid session cookie or refresh token.
- The exposed email address can be used for convincing follow-up phishing.
- The account can reset other accounts or access sensitive files.
Credential stuffing is the automated testing of a known username-and-password combination against many websites. The attacker does not need to crack the password; reuse does the work. Password spraying is different: an attacker tries a small number of common passwords against many accounts to avoid triggering account lockouts. MFA makes both attacks substantially less useful because a password alone is not enough. CISA’s identity and access guidance covers these attack patterns and MFA.
Session theft creates a separate problem. A stolen browser cookie can represent an already-authenticated session, so the attacker may not need to enter the password at all. Password changes do not necessarily invalidate every cookie or token at every provider. Proofpoint discusses credential stuffing, password spraying, session-cookie theft, and adversary-in-the-middle phishing in its analysis of the incident. Read Proofpoint’s risk assessment.
Can you check whether you were affected?
No public tool can conclusively search every record in the 16-billion-record compilation. The datasets were not established as one searchable breach entry, and some may be private, newly circulating, duplicated, or absent from public services.
1. Check your email address at Have I Been Pwned
Have I Been Pwned can show known breaches associated with an email address. A match means that address appeared in one or more datasets in HIBP’s available corpus; it does not necessarily mean the password currently used on an account is exposed.
The Tool Desk
Outbyte Driver Updater FREEScan for outdated or missing drivers - takes under a minuteDriver Scan →Outbyte PC Repair FREERepair Windows errors before they cause bigger problemsFix Now →A clean result is not proof that you are safe. It only means the address was not found in the service’s available data. HIBP cannot identify unknown, private, unsubmitted, or newly circulating datasets, and it cannot determine whether a particular device was infected.
Rank #3

- SECURE PASSWORD STORAGE: Keep all your passwords safely encrypted and stored directly on a USB key for easy access.
- 4 GB CAPACITY: Ample storage space to save numerous passwords, credentials, and sensitive login information.
- CROSS-PLATFORM COMPATIBLE: Works seamlessly with both PC and Mac, making it versatile for any desktop or laptop setup.
- PORTABLE AND CONVENIENT: Compact USB key design allows you to carry your passwords with you wherever you go.
- EASY TO USE: Simply plug into any USB port to access your securely stored passwords quickly and efficiently.
2. Check passwords through an official service
Have I Been Pwned’s Pwned Passwords service uses a privacy-preserving range-search process. Your device sends only the first five characters of a password’s SHA-1 or NTLM hash; the full password is not sent to HIBP. Use the official service or a reputable password manager, not an unfamiliar website asking you to paste all of your passwords.
A password match means that password has appeared in HIBP’s corpus. It does not identify which of your accounts still uses it, and it does not prove that the 16-billion-record collection contains it.
3. Run your password manager’s security check
For Google Password Manager, use Google Password Manager → Checkup → Check passwords. You can also visit passwords.google.com and select Password Checkup. Google’s menu labels can vary slightly by device, browser, and account version. Google’s official Password Checkup instructions explain the current path.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
Apple Passwords, Microsoft Edge, and other reputable password managers may also identify reused or compromised passwords. Treat their alerts as a prioritization tool, not as a universal scan of every criminal dataset.
4. Review accounts directly
Open the official app or type the provider’s address yourself and review:
- Recent sign-ins and unfamiliar devices.
- Active sessions and trusted devices.
- Password-reset and MFA changes.
- Recovery email addresses and phone numbers.
- Connected apps, OAuth permissions, and app passwords.
- Email forwarding rules, filters, sent mail, deleted mail, and archived messages.
- Banking, payment, cryptocurrency, cloud, and workplace activity.
Do not rely on a breach-checking result alone. Account activity can reveal compromise even when the relevant dataset has never been indexed by a public service.
What to do now: a safe response sequence
Step 1: Ignore links in unexpected breach-alert messages
News of a major leak creates an ideal pretext for phishing. Do not click a link in an email or text claiming to check your exposure, reset your password, or claim compensation. Go directly to the service’s official website or use its official app. CERT-MU specifically warned about phishing messages exploiting this story.
Do these 3 things before closing this tab:
1Fix the driver behind crashes, sound loss and screen glitches2Repair Windows errors before they cause bigger problems3Scan for outdated or missing drivers - takes under a minuteStep 2: Check and clean the device before changing dozens of passwords
If you suspect an infostealer, do not change every password from that computer. Update the operating system and security software, run a reputable malware scan, and investigate:
As an optional Windows cleanup step after securing the device, Outbyte PC Repair can help address common PC issues, but it should not replace a malware scan or incident-response investigation.
- Unknown browser extensions.
- Recently installed or suspicious applications.
- Pirated software and fake software updates.
- Unexpected remote-access tools.
- Unusual browser behavior or unexplained sign-ins.
The FTC recommends scanning for and removing suspicious software when an account may have been hacked. If the device belongs to an employer, contact IT or the security team rather than relying only on a consumer antivirus scan. Preserve relevant evidence if an incident investigation may be needed.
If an important account is actively being taken over, use a known-clean device to secure it immediately; do not wait for a lengthy scan. The key rule is that password changes should happen from a device you trust.
Outdated Drivers Are Slowing You Down
One free scan finds every outdated or missing driver and matches the right update for your exact hardware.Free scan · exact hardware matchWindows Errors? Fix Them Before They Spread
Repair common Windows errors and clear accumulated junk for a smoother, more stable PC - no reinstall needed.Free scan · no reinstallRank #4

- 🔑 RESET WINDOWS PASSWORDS IN MINUTES Quickly reset forgotten local Windows user and administrator passwords without reinstalling Windows or losing important files. Fast and simple offline recovery process.
- 💻 WORKS WITH MOST WINDOWS PCS & LAPTOPS Compatible with many Windows desktop and laptop systems. Supports USB boot startup for convenient and reliable password recovery access.
- ⚡ EASY PLUG & PLAY USB DESIGN No complicated setup required. Simply insert the USB, boot from it, and follow the included step-by-step instructions to reset passwords quickly.
- 🔒 SAFE OFFLINE PASSWORD RECOVERY Runs completely offline with no internet connection required. Helps protect your privacy while keeping your files and operating system intact.
- 🛠 BEGINNER-FRIENDLY WITH INCLUDED INSTRUCTIONS Designed for home users, students, technicians, and IT professionals. Includes easy-to-follow written instructions and boot menu guidance for hassle-free recovery.
Step 3: Secure your primary email account first
Email is often the recovery channel for every other account. From a known-clean device:
- Change the email password to a genuinely unique password or use a passkey.
- Enable MFA, preferably with a passkey, hardware security key, or authenticator app.
- Sign out of all other devices and sessions.
- Check recovery email addresses, phone numbers, and backup codes.
- Remove unknown connected apps, OAuth permissions, and app passwords.
- Inspect forwarding rules and filters for hidden copies of messages.
- Review sent, deleted, and archived folders for unauthorized activity.
Email access can let an attacker reset passwords for banking, shopping, social, and workplace accounts. If recovery details were changed or you cannot sign in, use the provider’s official account-recovery process and contact support through its published website. Do not use a phone number or link supplied in a suspicious message.
Step 4: Replace reused or exposed passwords
Prioritize accounts in this order:
- Primary and backup email.
- Banking, payment, and investment services.
- Cloud storage and password-manager accounts.
- Apple, Google, and Microsoft accounts.
- Work, VPN, developer, administrator, and government accounts.
- Social-media and messaging accounts.
- Shopping, travel, health, and other services containing personal information.
Use a password manager to generate a different password for every service. Do not turn Summer2025! into Summer2026!; predictable variations are easy for attackers to test. Also change any password that was used on a service named in an alert, even if the account itself shows no suspicious activity.
NIST’s current digital-identity guidance recommends blocking known compromised passwords, allowing password managers, and changing passwords when compromise or exposure is suspected. It does not recommend forcing arbitrary periodic changes without evidence of compromise. NIST SP 800-63B-4, published in July 2025, specifies at least 15 characters for single-factor passwords in covered systems, but that is guidance for applicable digital-identity systems, not a universal legal requirement for every consumer website. See NIST’s current password guidance.
Step 5: Revoke sessions and tokens
Password resets and session revocation address different risks. After changing a high-value password, look for controls labeled:
- Sign out of all devices.
- Log out of other sessions.
- Revoke sessions or refresh tokens.
- Remove trusted devices.
- Revoke app passwords.
- Disconnect unknown applications.
Do this for email, cloud storage, social accounts, developer platforms, VPNs, banking services, and workplace systems where the provider offers the option. Some providers invalidate sessions automatically after a password reset; others may leave certain cookies, tokens, or trusted devices active.
Step 6: Strengthen authentication
Where available, prefer:
- Passkeys or hardware security keys.
- Authenticator-app MFA.
- SMS or email codes when stronger methods are unavailable.
CISA identifies phishing-resistant MFA as the preferred approach for organizations, and the FTC says authenticator apps and security keys are generally safer than SMS when available. CISA’s MFA guidance and the FTC’s consumer MFA guide explain the choices.
MFA reduces the value of a stolen password, but it is not an absolute guarantee. Stolen session cookies, phishing that captures a live authentication exchange, MFA-prompt fatigue, SIM swapping, a compromised recovery email, malicious OAuth applications, or malware on an already-authenticated device can still cause trouble.
Step 7: Use passkeys for important accounts
Passkeys use public-key cryptography instead of transmitting a reusable password. They are tied to the intended website or app, which makes them resistant to many ordinary phishing and credential-reuse attacks. Google’s passkey documentation explains how they work and where to manage them.
Passkeys do not remove every threat. A compromised device, hijacked account used to synchronize credentials, stolen recovery method, or malicious support interaction can still put an account at risk. They are a major improvement over reused passwords, not a promise of perfect security.
Best Value

- FOR FULL INSTRUCTION PLEASE READ DESCRIPTION
- Step 1: Boot from the USB Flash Drive - Insert the USB flash drive into an available USB port on your computer. - Turn on your computer or restart it if it’s already on. - As the computer starts, press the key that opens the boot menu. This key varies by manufacturer and model, but it’s often F2, F10, Esc, or Delete. - In the BIOS/UEFI setup menu, locate the Boot Options or Boot Order section. - Use the arrow keys to select your USB drive and move it to the top of the boot priority list. - Save your changes and exit the BIOS/UEFI setup. Your computer will now boot from the USB flash drive.
- After that its will take few minutes to reset Windows login password
- Package includes instruction how to use "Password reset USB" software
Do you need to freeze your credit?
Not solely because of this headline. The publicly described incident primarily concerns login credentials, cookies, tokens, and infostealer data; it was not established as one release of Social Security numbers or complete credit files.
Consider a credit freeze or the equivalent protection available in your country when you have evidence that identity or financial information was exposed, see signs of identity theft, or receive a notification specifically mentioning those data types. Otherwise, focus first on account security, malware checks, session revocation, and monitoring financial accounts.
What not to do
- Do not download the leaked datasets. Dumps, samples, magnets, Telegram channels, and underground-forum links may contain malware, credential-harvesting pages, illegal material, or further criminal distribution.
- Do not change every password blindly from a possibly infected computer. Secure the device or use a known-clean one first.
- Do not assume a password change alone ends an intrusion. Revoke sessions, cookies, tokens, app passwords, and connected applications.
- Do not interpret a clean HIBP result as a clean bill of health. It cannot cover every private or newly circulating dataset.
- Do not reuse a password with a small variation. Generate a truly unique credential.
- Do not turn on MFA by approving unexpected prompts. Deny unexplained requests and investigate them.
What businesses and IT teams should check
Organizations should treat the story as a reminder to look beyond perimeter breaches. Review identity-provider sign-ins, impossible-travel alerts, new OAuth grants, app passwords, VPN access, developer tokens, mailbox forwarding rules, and endpoints that may have browser credentials or cookies stolen.
Prioritize accounts with administrative, cloud, source-code, financial, VPN, or email-recovery privileges. If a corporate endpoint may have an infostealer, isolate it and involve the security or incident-response team. Resetting credentials without investigating the endpoint can leave the attacker in possession of newly issued passwords or active tokens.
Organizations should also enforce MFA, prefer phishing-resistant methods for privileged access, block known compromised passwords, permit password managers, and monitor for credential stuffing. CISA’s MFA guidance and NIST’s digital-identity guidance provide the relevant defensive framework.
The practical conclusion
The 16-billion figure is not a verified count of unique passwords, accounts, or people. It is an approximate total of raw records across 30 exposed datasets, and some of the methodology and contents were disputed. Neither Apple, Google, nor Meta was shown to have suffered one centralized breach that produced the total.
Recommended Free Tools
That correction should not be mistaken for reassurance. Reused passwords, infostealer malware, stolen cookies, and exposed recovery accounts can still lead to account takeover. The most effective response is targeted and sequenced: use official sites, check or isolate suspicious devices, secure email, replace reused passwords, revoke active sessions, enable strong MFA or passkeys, and monitor important accounts.
Sources and further reading
- Cybernews: the original report on the exposed datasets
- Associated Press: multiple thefts, compilation, duplicates, and unknown affected-user count
- Axios: Google’s response and clarification of the breach claim
- JayeLTee: independent critique of the dataset claims
- CERT-MU: consumer warning and phishing advice
- Have I Been Pwned API and privacy documentation
- Google Password Manager Checkup
- Google passkey documentation
- FTC hacked-account recovery guidance
- NIST SP 800-63B-4 password and authentication guidance
Frequently Asked Questions
Should I change every password because of the 16-billion-record leak?
No. Change passwords that are reused, exposed, or associated with suspicious activity, beginning with email, banking, cloud storage, password managers, work systems, and major identity accounts. Use a known-clean device, generate a unique password for each service, and revoke active sessions as well.
Does a clean Have I Been Pwned result mean my account is safe?
No. HIBP checks the datasets available to that service, not every private, new, or criminally circulated collection. A clean result does not rule out an infected device, a stolen session cookie, phishing, or a dataset that has not been indexed.
Can MFA protect me if my password was stolen?
MFA substantially reduces the risk from password-only attacks such as credential stuffing, but it is not perfect. Stolen session cookies, phishing, MFA-prompt attacks, SIM swapping, compromised recovery accounts, and malware on an authenticated device can still bypass or undermine MFA. Passkeys and hardware security keys provide stronger phishing resistance where supported.
Should I freeze my credit after hearing about this incident?
Not automatically. The publicly described material primarily involved credentials, cookies, tokens, and infostealer data, not a confirmed single release of credit files or government identity numbers. Consider a freeze or equivalent protection when you have evidence that financial or identity data was exposed or you see signs of identity theft.
The Bottom Line
Bottom line: There was no verified single breach of 16 billion unique passwords and no established centralized hack of Apple, Google, or Meta. The figure represented approximately 16 billion raw records across 30 exposed datasets, with unknown duplication and uncertain validity. Protect yourself by checking from official services, scanning or isolating suspicious devices, securing email first, replacing reused passwords, revoking sessions and tokens, and enabling MFA or passkeys.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

