Wisec
Wisec: Wisec combines build traceability, SBOM controls, vulnerability scanning, and compliance evidence. Ranked #6 of 24 in Software Supply Chain Security Software by our editors (7.2/10); pricing: Free plan · paid from €5,000/yr · 14-day trial; best for compliance-focused teams needing build evidence.
At a glance
- Editor score7.2 / 10
- PricingFree plan · paid from €5,000/yr · 14-day trial
- Best forCompliance-focused teams needing build evidence
- Free planYes
- Dependency analysisYes
- Facts checked20 Sep 2026
Where it wins
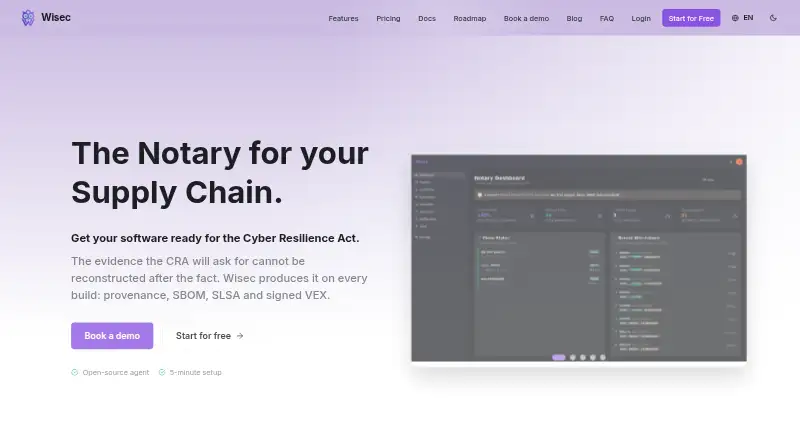
- Immutable CI/CD build traceability with SLSA provenance and timestamping
- Signed, diffable CycloneDX SBOMs and OpenVEX attestations
- Policy gates and compliance reports for NIS2, SOC2, CRA, and ISO 27001
Where it doesn't
- Advanced controls and archives require the €15,000-per-year Pro plan
- Enterprise self-hosting requires contacting sales
- The free plan provides community support rather than priority support
Our verdict on Wisec
For DevSecOps teams, CISOs, and auditors, Wisec provides cloud-based software supply chain security across web and Linux. It monitors CI/CD builds, scans dependencies with OSV, generates and certifies CycloneDX SBOMs, and records build activity for traceability. The platform also covers anomaly detection, policy-as-code release gates, signed VEX attestations, provenance records, and compliance evidence. Teams that need auditable build evidence alongside vulnerability management are the clearest fit; smaller teams seeking only basic dependency scanning may find its broader focus unnecessary.
Wisec has a free plan with vulnerability scans, SBOM generation, anomaly detection, Policy as Code and CI gates, public IPFS verification, and community support. The Business plan costs €5,000 per year and adds linked notarization chains, SBOM diffing, SLSA provenance, Sigstore/Rekor timestamping, signed VEX attestations, and compliance reports. Pro costs €15,000 per year, adding unlimited projects and builds, lifetime archives, SSO, multi-admin management, advanced audit exports, and priority support. Enterprise adds self-hosting and uses contact sales. Paid plans include a 14-day trial.
Its ecosystem covers GitLab, GitHub Actions, Jenkins, Azure DevOps, CodeQL, Semgrep, Snyk, and Trivy, with alerts for Slack and Microsoft Teams. OIDC single sign-on and role-based access control support organizational governance, while open-source availability and public verification can suit teams that value inspectable supply-chain evidence. Choose Wisec when provenance, signed artifacts, release controls, and regulatory reporting need to work together. Consider an alternative if you need a lower-cost paid tier, a simpler standalone scanner, or enterprise terms without a sales process.
Wisec pricing
All 4 Wisec plans and prices →
Wisec fact sheet
| Free plan | Yes |
|---|---|
| Paid from | Not verified |
| Source & repo security | Yes |
| Dependency analysis | Yes |
| SBOM management | Yes |
| Build provenance | Yes |
| Artifact signing | Not verified |
| Provenance attestations | Yes |
| Release policy gates | Yes |
| Free trial | 14 days |
| Deployment | Cloud, Self-hosted |
| Platforms | Web, Linux |
| Compliance & security | SOC 2, ISO 27001, GDPR |
| Support | Email, Community, Docs |
| Built for | Solo, Small business, Mid-market, Enterprise (editorial estimate) |
| Integrations | 10 integrations: GitLab, GitHub Actions, Jenkins, Azure DevOps, Slack, Microsoft Teams … |
| Pricing | Free plan · paid from €5,000/yr · 14-day trial (source) |
| Website | wisec.io |
| Facts checked | 20 Sep 2026 |
Wisec integrations
Wisec lists 10 integrations on its own site.
- GitLab
- GitHub Actions
- Jenkins
- Azure DevOps
- Slack
- Microsoft Teams
- CodeQL
- Semgrep
- Snyk
- Trivy
Alternatives to Wisec
- DevGuardBroad supply-chain security coverage with self-hosted and managed deployment options.10.0
- ChainloopOpen-source evidence management with policy gates and enterprise governance options.8.8
- KosliA broad governance layer for provenance, policy controls, and audit evidence.7.4


Wisec vs the competition
- Wisec vs DevGuard
- Wisec vs Chainloop
- Wisec vs Kosli
- Wisec vs SafeDep Platform
- Wisec vs Anchore Enterprise
- Wisec vs OX Security


Compare Wisec with any tool side by side →
Used Wisec? Be the first to review it
The editor score above is our own research. What this page doesn't have yet is a reader's view — what you used Wisec for, what worked and what didn't. No stars are seeded and no review is paid for; an editor reads every one before it appears.
Write a reviewTwo minutes · verified accounts only · read by an editor before it appears
Featured on iTechGuides
Wisec is listed in our Software Supply Chain Security Software directory. Add the badge to your site — it links back to this page.
<a href="https://www.itechguides.com/products/wisec/"><img src="https://www.itechguides.com/best/badge/wisec.svg" alt="Featured on iTechGuides" width="230" height="46"></a>
Guides on software supply chain security software
Reviewed by iTechGuides Editors · Editorial team · Updated Sep 2026
Advertiser disclosure: iTechGuides is reader-supported. We may earn a commission when you click some links. How we rank.
Last updated · How we research and update