
Free tools Windows power users keep installed
One-click scans. No signup required.
iTechGuides is reader-supported. When you buy through links on our site, we may earn an affiliate commission. As an Amazon Associate I earn from qualifying purchases. Learn more
A dependable website maintenance plan is a recurring operating procedure, not a reminder to click “Update.” It assigns owners, inventories every component and dependency, sets risk-based update windows, creates verified file-and-database backups, protects administrator access, monitors changes, and provides a tested rollback and recovery path. For WordPress, a complete restore requires both the site files and its database, while current, functional backups should exist before patching. The schedule below gives you a practical baseline; adjust its timing to your site’s traffic, business impact, acceptable data loss, and recovery-time target.
What is a website maintenance plan, and why does it matter?
A maintenance plan is a written cycle for keeping a production website secure, available, and recoverable. It turns ad-hoc updates into controlled changes: someone reviews an advisory, another person can approve a high-risk release, a named operator performs it, and an identified responder can restore service if verification fails.
Security updates close known weaknesses, but an update can also conflict with a theme, plugin, package, custom integration, PHP version, database schema, or hosting configuration. Backups reduce the blast radius only when they contain everything needed to rebuild the site and have been proven restorable. Access controls and monitoring address a different failure mode: an attacker or unauthorized administrator changing content, DNS, certificates, code, or backup settings.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
Use the plan to define five outcomes:
- Every production asset and dependency has an owner and support status.
- Routine and emergency changes have explicit priority rules and maintenance windows.
- A current, functional backup exists before a risky change.
- Post-update checks cover the journeys that matter to customers.
- A tested runbook states exactly how to roll back, restore, communicate, and preserve evidence.
NIST describes patch management as identifying, prioritizing, acquiring, installing, and verifying patches and upgrades throughout an organization. See NIST SP 800-40 Rev. 4 for the formal framework.
#1 Best Overall

- Slim durable design to help take your important files with you
- Vast capacities up to 6TB[1] to store your photos, videos, music, important documents and more
- Back up smarter with included device management software[2] with defense against ransomware
- Help secure your important files with password protection and hardware encryption
- 3-year limited warranty
What should a website maintenance plan include?
Start with one authoritative inventory and a responsibility matrix. Do not limit it to the CMS dashboard; a forgotten DNS account or payment callback can take down a site just as easily as an outdated plugin.
| Area to record | Minimum details | Accountable role |
|---|---|---|
| Production and staging | URLs, hosting account, server or container, operating system, runtime versions, deployment method, and environment differences | Technical owner |
| CMS and code | Core version, themes, plugins or packages, custom code, repositories, build tools, licenses, and end-of-life dates | Application owner |
| Data stores | Database engine and version, media storage, search indexes, queues, caches, and required environment variables | Application or data owner |
| Network and identity | Domains, DNS provider, TLS certificates, CDN, administrator accounts, MFA method, SSO, and emergency access | Infrastructure or security owner |
| Business integrations | Payment, email, analytics, CRM, forms, webhooks, APIs, and vendor contacts | Service owner |
| Recovery assets | Backup destinations, encryption keys, retention, restore target, recovery-time target, and recovery-data-loss target | Recovery lead |
| Change governance | Approver for high-risk work, maintenance windows, communication channels, change records, and rollback criteria | Change owner |
For each entry, capture the vendor’s support status and end-of-life date. Record who can approve a high-risk change, who can execute it, and who can recover the service when the usual operator is unavailable. Review operational websites for vulnerabilities and keep role definitions current; staff turnover and vendor changes are common sources of orphaned access.
How often should you update a website?
There is no safe universal deadline for every site. Use the vulnerability’s severity and exploitability, whether it is being actively exploited, the exposure of the affected component, compatibility risk, and your business impact to set a deadline. Critical, actively exploited issues should trigger an out-of-band response rather than wait for the next monthly window. The UK National Cyber Security Centre’s secure deployment and maintenance guidance supports urgent fixes for critical vulnerabilities and thorough testing.
The following operating calendar is a practical starting point, not a published universal standard:
| Cadence | Work | Expected evidence |
|---|---|---|
| Daily or continuous | Watch uptime, backup-job failures, security alerts, administrator logins, unexpected file or content changes, and suspicious redirects when the site is business-critical. | Alert history, uptime record, and acknowledged incidents |
| Weekly | Review available security updates, confirm backup completion, inspect high-value forms, checkout, login, contact flows, and check for expiring certificates or domains. | Update review and smoke-test checklist |
| Monthly | Apply routine updates in a planned window; review administrator accounts and installed extensions; check storage capacity; and restore-test a representative backup when feasible. | Change record, test results, and access review |
| Quarterly | Reconcile the asset inventory, vendor support status, disaster-recovery contacts, retention rules, and lessons from incidents or near misses. | Signed review with action owners and due dates |
| Out of band | Respond immediately to critical vulnerabilities, active exploitation, compromise indicators, emergency vendor instructions, or a failing control. | Incident timeline, decision rationale, and recovery evidence |
WordPress recommends frequent maintenance, update checks, backups, and site checks. Choose more frequent backups and shorter update windows for a high-transaction store than for a low-change brochure site, and revisit the targets after a major release or incident.
Rank #2
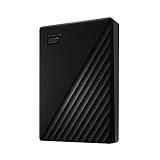
- Slim durable design to help take your important files with you
- Vast capacities up to 6TB[1] to store your photos, videos, music, important documents and more
- Back up smarter with included device management software[2] with defense against ransomware
- Help secure your important files with password protection and hardware encryption
- 3-year limited warranty
How do I design backups that can actually restore the site?
Back up both the files and the database. WordPress explains that you need both to fully restore a typical site; a downloaded site directory does not contain database content such as posts, settings, users, orders, and form submissions. Its backup guidance describes weekly backups for smaller sites, daily backups for high-activity sites, and at least three to five recent copies in different locations as an adaptable example.
Define what each backup contains
- Files: uploaded media, themes, plugins, custom code, configuration files, deployment artifacts, and any server-side assets required to run the site.
- Database: all production tables, including content, accounts, settings, transactions, and integration data.
- Rebuild information: CMS and runtime versions, dependency manifests, environment-variable names, DNS and certificate details, and instructions for retrieving secrets without placing them in plain-text backups.
- Operational metadata: creation time, source environment, retention expiry, encryption status, and the person or system that produced the copy.
Choose frequency, retention, and separation
Set the schedule from your recovery-data-loss target: how much recent work can the business afford to lose? A site with frequent orders or registrations may need daily or more frequent database captures; a rarely changed site may accept weekly backups. Keep several generations so a corruption or compromise discovered days later does not overwrite every usable copy.
Store copies in separate failure domains, such as the host, a separately controlled cloud account, and a local computer or protected external hard drive. An external drive can add an offline or separately stored copy, but it must not be the only copy; protect it from theft, physical loss, ransomware, and hardware failure. The Australian Cyber Security Centre lists cloud storage and an external hard drive as possible destinations and recommends regular backups and current software.
Separation should include credentials and, where practical, accounts or regions. If an attacker can delete the production site, log in with the same credentials, and erase its backup destination, the apparent redundancy is not recovery protection.
Verify every job and test restores
A successful job message proves that a process ran, not that the archive is complete or usable. Monitor failures and record the backup timestamp, size, component coverage, and destination. On a schedule appropriate to your risk, restore a representative copy into an isolated environment, confirm that the database connects, media loads, administrator login works, and critical user journeys behave correctly, then retain the test evidence.
Rank #3
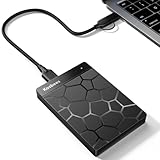
- 【Plug-and-Play Expandability】 With no software to install, just plug it in and the drive is ready to use in Windows(For Mac,first format the drive and select the ExFat format.
- 【Fast Data Transfers 】The external hard drives with the USB 3.0 cable to provide super fast transfer speed. The theoretical read speed is as high as 110MB/s-133MB/s, and the write speed is as high as 103MB/s.
- 【High capacity in a small enclosure 】The small, lightweight design offers up to 500GB capacity, offering ample space for storing large files, multimedia content, and backups with ease. Weighing only 0.35 Lbs, it's easy to carry "
- 【Wide Compatibility】Supports PS4 5/xbox one/Windows/Linux/Mac and other operating systems, ensuring seamless integration with game consoles,various laptops and desktops .
- Important Notes for PS/Xbox Gaming Devices: You can play last-gen games (PS4 / Xbox One) directly from an external hard drive. However, to play current-gen games (PS5 / Xbox Series X|S), you must copy them to the console's internal SSD first. The external drive is great for keeping your library on hand, but it can't run the new games.
CISA’s patch-management guidance calls for a current, functional backup or archive before deployment and says the plan should define backup frequency, verification, retention, and storage locations. Quarantine a backup that shows signs of compromise; do not restore it over clean production data until it has been investigated.
Crashes, No Sound, or Screen Glitches?
Random freezes, missing sound and display glitches usually trace back to one bad driver. Find and replace yours safely.Free scan · under a minutePC Slower Than It Used to Be?
A free scan shows the junk files, broken settings and background clutter dragging Windows down - then fixes them in one click.Free scan · Windows 10 & 11How do I safely update WordPress plugins and core?
Use a repeatable change procedure that separates preparation, testing, release, and verification. The same sequence works for themes, core updates, server packages, and custom deployments.
- Review the change. Read the vendor advisory and release notes. Identify the affected component, severity, exploitability, compatibility requirements, supported runtime versions, and business functions at risk. Check whether exploitation is active or an emergency fix is requested.
- Inventory dependencies. Confirm the current WordPress, PHP, database, theme, plugin, integration, and hosting versions. Note custom modifications that an update could overwrite.
- Create and verify a recovery point. Capture both files and database, record its timestamp and location, and confirm the backup completed before proceeding.
- Prepare the window. Confirm monitoring is working, notify affected staff, ensure you can access hosting, DNS, and the rollback path, and define the exact condition that will stop the release.
- Test in staging. Clone production data safely or use representative test data. Apply the update, inspect logs, and exercise authentication, forms, checkout, payments, search, email, and any critical API or webhook. NCSC advises that updates be signed and thoroughly tested.
- Release in a controlled order. Apply the highest-risk exposure with an available fix first, while respecting documented compatibility dependencies. Avoid bundling unrelated changes that make a failure hard to diagnose.
- Verify immediately. Confirm the installed version, check server and application logs, render key page types, submit forms, test login and permissions, run a safe transaction test where appropriate, and inspect redirects and security headers.
- Monitor after release. Watch error rates, uptime, queue backlogs, failed payments, administrator events, unexpected file changes, and security alerts for a defined observation period.
- Close or recover. Record the result and evidence. If a critical check fails, place the site in a safe state, roll back the component when that is known to be safe, or restore the verified recovery point. Document the cause and the next corrective action.
Do not assume that an update is safe because the dashboard reports success. A plugin can activate correctly while breaking a checkout callback, scheduled job, cache rule, or mobile layout that only a real journey exposes.
How should I prioritize security updates?
Rank work by risk rather than by the date a notification arrived. A useful decision record includes the vulnerability’s severity, evidence of exploitation, internet exposure, privileges required, affected data, compensating controls, compatibility risk, and the time needed to test and recover.
| Priority | Typical trigger | Plan response |
|---|---|---|
| Emergency | Active exploitation, compromise indicators, remote unauthenticated access, or an emergency vendor instruction | Start an incident response, restrict exposure if possible, take a verified backup, test the fix or mitigation rapidly, and release out of band with executive or security approval. |
| High | Critical exposure with a trusted fix, but no evidence of current compromise | Schedule the shortest practical window, test in staging, communicate impact, and verify enhanced monitoring after release. |
| Routine | Important security, compatibility, or maintenance update without immediate exploitation evidence | Bundle only compatible work into the planned monthly window, with a tested rollback point. |
| Deferred | Low-impact change, unsupported feature, or update blocked by an identified compatibility issue | Document the reason, apply compensating controls, assign an owner and deadline, and escalate if the deadline expires. |
Prioritization does not mean skipping verification. NIST’s process explicitly includes verifying installation, and NCSC says updates should not be treated as a premium feature. If testing reveals an incompatibility, record the exposure and mitigation instead of silently leaving the component unpatched.
Do these 3 things before closing this tab:
1Clear out junk files and repair common Windows errors2Scan for outdated or missing drivers - takes under a minute3Repair Windows errors before they cause bigger problemsRank #4

- Slim durable design to help take your important files with you
- Back up smarter with included device management software[2] with defense against ransomware
- Help secure your important files with password protection and hardware encryption
- 3-year limited warranty
How do I protect administrator access and detect unauthorized changes?
Require multi-factor authentication for administrator, hosting, DNS, code-repository, and backup accounts. Use HTTPS, unique strong passwords or an approved password manager, least-privilege roles, and separate accounts for routine work and emergency administration. Remove dormant users and review vendor access after every contract or staffing change.
Monitor the events that can alter availability or trust:
- Administrator logins, privilege changes, failed-login bursts, and new API keys.
- Core, plugin, theme, package, configuration, and file changes.
- DNS records, nameservers, certificates, CDN rules, and deployment credentials.
- Backup-job failures, deletion requests, unusual archive downloads, and encryption-key changes.
- Unexpected redirects, new content, altered payment destinations, spam pages, or unexplained outbound traffic.
Forward logs to a location an attacker cannot easily rewrite, set alert thresholds that someone will acknowledge, and retain enough history to compare a suspected change with the approved change record. The Australian guidance above specifically calls for MFA, secure hosting, strong passwords, access controls, regular updates, backups, and review for suspicious activity. WordPress also emphasizes keeping core, plugins, and themes current and maintaining recovery plans in its security guidance.
How do I restore a website after an update breaks it?
Use a short, rehearsed runbook. The objective is to restore a known-good state while preserving evidence and avoiding a second failure.
The Tool Desk
Outbyte Driver Updater FREEScan for outdated or missing drivers - takes under a minuteDriver Scan →Outbyte PC Repair FREEClear out junk files and repair common Windows errorsFree Scan →- Declare the incident. Record the time, symptoms, affected journeys, recent changes, and incident lead. Decide whether the problem is an outage, data-integrity issue, or possible compromise.
- Stabilize. Put the site in maintenance mode or disable the failing feature if that protects users. Stop automated deployments and avoid repeated update attempts that could overwrite evidence.
- Confirm the last known-good point. Match the change timestamp to a verified backup and, if available, a staging test. Ensure the selected copy predates the failure and is not suspected of compromise.
- Choose rollback or restore. Roll back a single component only when its previous version and dependencies are known. Restore files and database together when the update changed schema, content, configuration, or multiple components.
- Validate in isolation first. Restore to a temporary environment when time and capacity allow. Check database integrity, media, login and permissions, forms, payments, email, integrations, and logs.
- Return to service. Apply the approved recovery, invalidate caches safely, verify DNS and certificates, and run the critical smoke tests from an independent connection.
- Monitor and communicate. Watch errors, traffic, authentication, transactions, and suspicious activity. Tell stakeholders what is working, what remains degraded, and when the next update will occur.
- Learn and harden. Preserve logs and the failed package, identify the incompatibility or control failure, update the inventory and test coverage, and schedule the corrective change.
Never treat an untested archive as proof of recoverability. A backup that has not been restored is an assumption; a restore test with recorded results is operational evidence.
Best Value

- World’s First 6TB 2.5” Portable Hard Drive
- Slim durable design to help take your important files with you
- Vast capacities up to 6TB[1] to store your photos, videos, music, important documents and more
- Back up smarter with included device management software[2] with defense against ransomware
- Help secure your important files with password protection and hardware encryption
Should maintenance be managed, self-managed, automated, or manual?
Choose an operating model based on the skills, coverage, and recovery responsibility you can sustain—not on the label alone.
| Decision axis | Questions to answer | Trade-off |
|---|---|---|
| Managed versus self-managed | Who applies patches, watches failures, communicates incidents, and performs recovery at night or on holidays? | Managed service can provide coverage and specialist skills; self-management preserves direct control but requires assigned staff and on-call capacity. |
| Automation versus manual control | Which updates, backups, tests, and alerts can run automatically, and where is human approval required? | Automation improves consistency and speed; manual gates reduce surprise changes but add delay and effort. |
| Backup architecture | Are files and database complete, encrypted, retained, separated, monitored, and restore-tested? | More copies and isolation improve resilience while increasing storage, access-management, and test overhead. |
| Recovery objectives | How much data loss is acceptable, and how quickly must the site return? | Shorter targets usually require more frequent capture, standby capacity, and rehearsed procedures. |
| Testing and compatibility | Is there staging, representative data, rollback support, and coverage for integrations? | Better coverage lowers release risk but costs time to maintain. |
| Access and monitoring | Are MFA, role controls, alerting, audit logs, and incident response included? | Strong controls reduce unauthorized-change risk but require ongoing review and alert ownership. |
| Provider assurance | What is the support lifecycle, security practice, data location, incident notice process, and contractual responsibility? | Documented commitments make accountability clearer; they do not replace your own restore tests. |
What should the maintenance runbook and checklist look like?
Keep a one-page emergency runbook and a fuller change record. The emergency page should be usable by someone who did not build the site.
Emergency runbook fields
- Primary and backup contacts, escalation order, and approved communication channel.
- Hosting, DNS, certificate, CMS, repository, monitoring, and backup access paths, with MFA recovery instructions stored separately and securely.
- Current production version, last verified backup timestamp, backup locations, and restore target.
- Commands or UI paths for maintenance mode, deployment freeze, rollback, cache invalidation, and restore.
- Stop conditions, customer-impact criteria, evidence-preservation steps, and notification obligations.
- Recovery-time and recovery-data-loss targets, plus the person authorized to accept a temporary degraded state.
Change-record fields
- Requestor, owner, approver, affected components, advisory links, severity, and planned window.
- Pre-change backup identifier and verification result.
- Staging environment, test cases, expected results, and observed results.
- Release time, versions before and after, logs, monitoring period, and communication timestamps.
- Rollback decision, restore identifier, incident notes, root cause, and follow-up owner and deadline.
Review the plan after incidents, major architecture changes, ownership changes, or a vendor reaching end of support. A calendar that nobody updates becomes inaccurate documentation, so assign a person to maintain it and a manager to verify the review occurred.
What does a complete website maintenance plan achieve?
It gives every change a safe starting point, a clear owner, observable success criteria, and a credible way back. The strongest plans are risk-based rather than calendar-only: they patch urgent exposures quickly, test routine changes, keep independent file-and-database backups, restrict administrative access, and prove recovery through repeatable restore exercises.
Frequently Asked Questions
Can my hosting provider’s automatic snapshot replace an independent backup?
Not necessarily. A provider snapshot may share the same account, region, credentials, or failure domain as the live site and may not include every external database or integration. Keep an independently controlled copy and perform a restore test that demonstrates the snapshot contains the data you need.
How should backup encryption keys be handled?
Store keys separately from the backup repository, limit decryption rights to the recovery role, and document an emergency retrieval path. Test key recovery during a restore exercise; an encrypted archive is unusable if its key is lost.
What if I do not have a staging site?
Create a small representative test environment or clone the application without exposing production secrets. If that is impossible, schedule a short window, take a verified recovery point, apply one change at a time, and expand post-release monitoring and smoke tests.
Quick wins for a faster PC:
Clear out junk files and repair common Windows errorsFree Scan →Fix the driver behind crashes, sound loss and screen glitchesFind Drivers →Repair Windows errors before they cause bigger problemsFix Now →How can I tell whether a failed update is actually a security incident?
Treat unexpected administrator accounts, altered payment destinations, new redirects, unexplained files, credential prompts, or backup deletion as possible compromise rather than an ordinary bug. Preserve logs, restrict access, avoid restoring a suspicious backup, and involve your incident-response contact while you stabilize service.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

