
Free tools Windows power users keep installed
One-click scans. No signup required.
iTechGuides is reader-supported. When you buy through links on our site, we may earn an affiliate commission. As an Amazon Associate I earn from qualifying purchases. Learn more
Before employees use ChatGPT, Gemini, Copilot, or another AI service for company work, decide which tools are approved, what information may be entered, and who checks the results. Then inventory existing AI use, verify each vendor’s data practices, protect accounts and integrations, and prepare for incidents. These steps matter even if your other business systems are secure: AI use can introduce separate data-leak and privacy risks.
What should a small business check before using AI?
Use this checklist to set up a practical baseline, whether your business is considering its first AI service or already has employees experimenting with several tools. It is designed to work for small teams without a dedicated security department: assign owners, make decisions explicit, and revisit them when tools or business needs change.
- Inventory AI services, extensions, APIs, plug-ins, and agents already in use.
- Write an acceptable-use policy that names approved tools and prohibited data.
- Classify information before employees submit it to an AI service.
- Check vendor terms and security practices, not just marketing claims.
- Secure accounts, devices, networks, and integrations.
- Require a person to review consequential outputs.
- Train staff and rehearse incident response and recovery.
NIST SP 1300 is intended for small and medium-sized organizations, including those with modest or no cybersecurity plans. That makes an inventory and written rules a useful starting point even if your business does not have a formal security team.
Recommended Free Tools
How do I find out which AI tools employees are using?
Start with a working inventory rather than assuming that employees only use the services management has purchased. Include AI features embedded in other products, browser extensions, plug-ins, APIs, and agents as well as standalone chat services.
#1 Best Overall

- POWERFUL SECURITY KEY: The Security Key C NFC is the essential physical passkey for protecting your digital life from phishing attacks. It ensures only you can access your accounts.
- WORKS WITH 1000+ ACCOUNTS: Compatible with Google, Microsoft, and Apple. A single Security Key C NFC secures 100 of your favorite accounts, including email, password managers, and more.
- FAST & CONVENIENT LOGIN: Plug in your Security Key C NFC via USB-C and tap it, or tap it against your phone (NFC) to authenticate. No batteries, no internet connection, and no extra fees required.
- TRUSTED PASSKEY TECHNOLOGY: Uses the latest passkey standards (FIDO2/WebAuthn & FIDO U2F) but does not support One-Time Passwords. For complex needs, check out the YubiKey 5 Series.
- BUILT TO LAST: Made from tough, waterproof, and crush-resistant materials. Manufactured in Sweden and programmed in the USA with the highest security standards.
Record the details needed to make a decision
- Tool and owner: Record the service or integration and the person or team responsible for it.
- Purpose: Note the business task it supports, such as drafting or analysis, so you can judge whether the data access is appropriate.
- Connected accounts: Identify which business accounts or systems it can access. A connected agent or plug-in may create a different exposure from a chat window used without integrations.
- Data touched: Describe the information employees enter or the systems the tool can read or change.
- Approval status: Mark whether the tool is approved, awaiting review, or should no longer be used.
Ask staff and team leads what they use for work, including tools they may have tried informally. Give every entry an owner who can confirm whether the tool is still needed and whether its access or use has changed. NIST’s small-business guidance can help organizations structure a cybersecurity program without assuming they already have one.
What should an AI acceptable-use policy say?
A useful policy tells employees what they may use, what they may share, when a person must review an output, and who can approve a new service. A general instruction to “use AI responsibly” does not give staff enough guidance to make those decisions consistently.
Make the rules operational
- Approved tools: Name the services employees may use for company work, and state who authorizes additions.
- Prohibited information: Identify data that must not be entered unless the service’s relevant terms and protections have been verified.
- Human review: Specify which kinds of output require checking and approval before anyone acts on or shares them.
- Retention expectations: Explain what employees should expect about submitted information and where to direct questions about retention.
- Reporting: Tell staff how to report an accidental disclosure, unexpected access, or other suspected incident.
Cyber.gov.au’s AI checklist asks businesses to understand the benefits and risks, what information can be shared, and how the vendor handles data. Use those questions to shape rules people can follow in their actual work. A policy also needs an owner and a process for authorizing changes; otherwise, employees may not know whether a newly encountered tool is allowed.
Crashes, No Sound, or Screen Glitches?
Random freezes, missing sound and display glitches usually trace back to one bad driver. Find and replace yours safely.Free scan · under a minutePC Slower Than It Used to Be?
A free scan shows the junk files, broken settings and background clutter dragging Windows down - then fixes them in one click.Free scan · Windows 10 & 11What information should employees keep out of AI prompts?
Classify information before prompting, not after it has been submitted. Keep confidential, personal, regulated, customer-identifying, credential, and unreleased business information out of a service until you have verified the relevant collection, storage, ownership, retention, and model-training terms.
Turn data classification into a prompt decision
- Check whether the information identifies a customer, employee, or other person.
- Check whether it is confidential, regulated, or not yet public.
- Remove credentials and other access secrets from prompts and connected workflows.
- If a task appears to require restricted information, pause and ask the designated policy or tool owner whether the service is approved for that data.
This is not just a question of whether a prompt feels sensitive. The service’s collection and storage practices, who owns submitted data, how long it is retained, and whether it may be used to train models all affect the decision. Cyber.gov.au’s checklist captures the central issue with the question: “I have confirmed whether my business’ data will be used to train AI models.” Verify the answer for the service and use in question rather than assuming one AI tool’s terms apply to another.
Rank #2

- POWERFUL SECURITY KEY: The YubiKey 5C NFC is the most versatile physical passkey, protecting your digital life from phishing attacks. It ensures only you can access your accounts
- WORKS WITH 1000+ ACCOUNTS: Compatible with popular accounts like Google, Microsoft, and Apple. A single YubiKey 5C NFC secures 100+ of your favorite accounts, including email, password managers, and more
- FAST & CONVENIENT LOGIN: Plug in your YubiKey 5C NFC via USB and tap it, or tap it against your phone (NFC), to authenticate. No batteries, no internet connection, and no extra fees required
- MOST SECURE PASSKEY: Supports FIDO2/WebAuthn, FIDO U2F, Yubico OTP, OATH-TOTP/HOTP, Smart card (PIV), and OpenPGP. That means it’s versatile, working almost anywhere you need it
- PRIMARY & SPARE KEYS: Just like having a spare house key, we recommend buying two YubiKeys - one for daily use and one as a spare. That way you’ll never get locked out of your accounts
How do I vet an AI vendor’s security and data practices?
Ask for concrete answers about data handling, protections, and incident response before employees submit business information or connect accounts. Vendor claims alone are not enough; the business needs to understand the applicable terms and commitments.
Questions to resolve before approval
- Collection and storage: What information does the service collect, and where is it stored?
- Training and ownership: Is submitted data used to train models, and who owns the submitted data?
- Retention and deletion: How long is information retained, and what deletion process or terms apply?
- Security controls: What encryption and access controls are offered? Are security attestations, such as ISO 27001 or alignment with the NIST AI Risk Management Framework, relevant and documented?
- Third parties: Which subprocessors handle data?
- Incident handling: What are the breach-notification terms, and how does the business contact the vendor during an incident?
Keep the answers with the inventory entry and identify who reviewed them. If the vendor’s terms do not let the business establish how information is collected, stored, used, or deleted, do not treat that uncertainty as approval to submit sensitive information. Recheck the terms when the service, its integrations, or the business’s intended use changes.
Quick wins for a faster PC:
Scan for outdated or missing drivers - takes under a minuteDriver Scan →Clear out junk files and repair common Windows errorsFree Scan →Fix the driver behind crashes, sound loss and screen glitchesFind Drivers →How should we secure AI accounts and access?
Protect AI services with the same identity controls you use for other sensitive business accounts. Require unique passwords, multi-factor authentication (MFA), least privilege, separate administrator accounts, and prompt off-boarding when someone no longer needs access.
Apply access controls deliberately
- Give employees their own accounts so access can be assigned and removed individually.
- Require MFA for accounts that support it. The FTC identifies an authenticator app, a one-time passcode, and a hardware token such as a USB device as MFA methods.
- Limit each account’s permissions to what its user needs for the assigned task.
- Keep administrative access separate from everyday use and restrict who can grant it.
- Remove access promptly when roles change or a worker leaves.
The FTC’s guidance says, “Require multi-factor authentication to protect sensitive information.” MFA adds a verification step to account access; it does not replace unique passwords or careful permission management. Check the service’s available login controls during vendor review so the business knows which access protections it can actually enforce.
What devices, networks, and backups need protection?
AI services do not replace basic device and network security. Keep business devices updated, encrypt devices and sensitive data, protect routers and networks, separate guest Wi-Fi, and maintain backups that are offline or otherwise isolated.
Rank #3
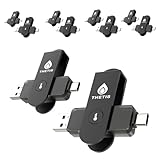
- FIDO2 & Passkey Ready: Business-ready and FIDO2 L1 certified. This key is supported by major management suites and is ideal for both individual and enterprise deployment. Works seamlessly with Gmail, Facebook, GitHub, Dropbox, Coinbase, and more.
- Dedicated Manager App: Use the Thetis Manager App for the initial hardware PIN setup. Setting the PIN on the device first ensures a smooth registration process. Once the PIN is configured, you can begin registering the key across your favorite FIDO2-compatible online services.
- Universal Connectivity (USB-C, USB-A, & NFC): Designed for PCs, Macs, iPhones, and Android. For mobile use, simply unfold the key, align it with your phone’s NFC antenna, and hold for a few seconds to authenticate.
- Enhanced MFA (FIDO2 & TOTP/HOTP): Strengthen your security with flexible options. Use the Manager App to access TOTP/HOTP features for accounts that do not yet support FIDO2.
- Check FIDO2 compatibility before purchase - Known limitations: ID Austria is not supported (requires FIDO2 Level 2). Windows Hello login only works with Windows Enterprise editions that support Entra ID. NFC is supported only through mobile authentication, Not MacOS/windows.
Baseline safeguards
- Turn on automatic updates for supported devices and software so security fixes are applied in a timely way.
- Encrypt business devices and sensitive stored data.
- Secure routers and protect business networks; keep guest Wi-Fi segmented from business systems.
- Maintain offline or otherwise isolated backups so a problem affecting connected systems does not automatically affect every copy.
- Use strong, unique passwords alongside MFA and account controls.
The FTC’s small-business cybersecurity guidance specifically calls for updates, backups, encryption, strong passwords, and network protection. These safeguards help protect the systems and data around AI use; they do not establish that a particular AI vendor is safe to use with confidential information.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
How do I secure AI plug-ins, APIs, and agents?
Treat an AI integration according to what it can access and do, not just what it is called. Limit API keys and agent permissions, avoid unrestricted access to sensitive systems, log important actions, and monitor for unusual activity.
Review each connection
- Scope access: Give an integration only the permissions needed for its stated purpose.
- Protect keys: Limit who can access API keys and avoid granting broader access than the integration needs.
- Constrain actions: Do not give an agent unrestricted access to sensitive systems when narrower permissions are possible.
- Keep records: Log important actions so the business can investigate unexpected changes or access.
- Watch for anomalies: Monitor unusual activity and know who responds if it occurs.
CISA’s secure-deployment guidance focuses on confidentiality, integrity, and availability, and on detecting and responding to malicious activity. In practical terms, an integration needs both boundaries and oversight: permissions reduce what it can do, while logs and monitoring help the business identify and investigate what it did.
Which AI outputs need a human review?
Have a person fact-check AI-generated code, customer communications, financial analysis, legal text, and security recommendations before use. AI output can be unreliable or manipulated, so a plausible answer should not be treated as verified evidence.
Define what “review” means for the task
- Check factual claims against appropriate, reliable information rather than relying on the output’s confidence or fluency.
- Review code before it is used, especially where it affects business systems or data.
- Check customer-facing communications for accuracy and appropriateness before they are sent.
- Have qualified people examine financial, legal, or security analysis before the business relies on it.
- Make clear who is responsible for approval and what to do when the reviewer cannot verify a claim.
Cyber.gov.au asks businesses where and how AI outputs will be fact-checked. The UK National Cyber Security Centre identifies unreliable or manipulated outputs as a risk. A review process should therefore be tied to the consequence of the task: the person responsible must be able to check the result before it is sent, deployed, or used to make a decision.
Do these 3 things before closing this tab:
1Repair Windows errors before they cause bigger problems2Fix the driver behind crashes, sound loss and screen glitches3Clear out junk files and repair common Windows errorsRank #4

- POWERFUL SECURITY KEY: The Security Key NFC is the essential physical passkey for protecting your digital life from phishing attacks. It ensures only you can access your accounts.
- WORKS WITH 1000+ ACCOUNTS: Compatible with Google, Microsoft, and Apple. A single Security Key NFC secures 100 of your favorite accounts, including email, password managers, and more.
- FAST & CONVENIENT LOGIN: Plug in your Security Key NFC via USB-A and tap it, or tap it against your phone (NFC) to authenticate. No batteries, no internet connection, and no extra fees required.
- TRUSTED PASSKEY TECHNOLOGY: Uses the latest passkey standards (FIDO2/WebAuthn & FIDO U2F) but does not support One-Time Passwords. For complex needs, check out the YubiKey 5 Series.
- BUILT TO LAST: Made from tough, waterproof, and crush-resistant materials. Manufactured in Sweden and programmed in the USA with the highest security standards.
How should we train employees to use AI safely?
Train staff on the rules and the security habits that make them usable: phishing resistance, safe prompting, data classification, approved tools, and how to report concerns. Repeat training when tools or threats change, and include it for new employees.
Make training match workplace decisions
- Show staff how to check whether a tool is approved and where to ask about a new one.
- Explain how to recognize restricted information before including it in a prompt.
- Practice the human-review expectations for work products that could affect customers or business decisions.
- Teach employees how to report accidental disclosure, suspicious activity, or unexpected tool behavior.
- Refresh the training when the business adopts new tools or faces new threats.
FTC and CISA guidance both treat workforce education as a core small-business control. Training should reinforce the written policy, not substitute for it: staff need clear approved-tool and data-sharing rules to apply what they learn.
Independent reader supportYour contribution helps us test, update, and keep practical guides available for everyone.What should a small business do if an AI-related incident occurs?
Prepare a response plan before an incident so employees know who acts, how to contain access, and how to preserve information needed for follow-up. Include AI accounts and integrations in the plan, not only conventional business systems.
Write down the response and recovery roles
- Identify who can isolate an account or integration when access or activity appears unsafe.
- Name who contacts the vendor and where the vendor’s incident contact information is kept.
- Explain how relevant evidence is preserved for investigation.
- Assign responsibility for deciding whether customers or regulators must be notified, and for making required notifications.
- Document how systems and data are restored from backups.
Test the plan with an exercise, then update it after exercises or actual incidents. CISA’s emphasis on detecting and responding to malicious activity complements the operational steps in the plan: the business should know how a suspected problem reaches the person who can contain it and how normal operations are restored.
The Tool Desk
Outbyte PC Repair FREERepair Windows errors before they cause bigger problemsFix Now →Outbyte Driver Updater FREEScan for outdated or missing drivers - takes under a minuteDriver Scan →How should we compare AI services for business use?
Compare services against the same criteria and the same intended use. A tool suitable for a low-sensitivity task may not be appropriate for confidential or regulated information, and a feature that matters for one integration may not matter for another.
Best Value

- FIDO2 & Passkey Ready: Business-ready and FIDO2 L1 certified. This key is supported by major management suites and is ideal for both individual and enterprise deployment. Works seamlessly with Gmail, Facebook, GitHub, Dropbox, Coinbase, and more.
- Dedicated Manager App: Use the Thetis Manager App for the initial hardware PIN setup. Setting the PIN on the device first ensures a smooth registration process. Once the PIN is configured, you can begin registering the key across your favorite FIDO2-compatible online services.
- USB TYPE A Connectivity & DONGLE Design: Designed for PCs, Macs, laptops and Android devices that utilize a USB-A port. Plug and stay, or carry it on a keychain. (Item Size: 0.75 X 0.74 IN x 0.25 IN)
- Enhanced MFA (FIDO2 & TOTP/HOTP): Strengthen your security with flexible options. Use the Manager App to access TOTP/HOTP features for accounts that do not yet support FIDO2.
- Check FIDO2 compatibility before purchase - Known limitations: ID Austria is not supported (requires FIDO2 Level 2). Windows Hello login only works with Windows Enterprise editions that support Entra ID. NFC functionality is not supported.
- Data handling: Collection, retention, model-training use, ownership, deletion, and storage geography.
- Security and access: Encryption, access controls, MFA, single sign-on (SSO), and audit logs.
- Third-party and incident terms: Subprocessors, incident-notification commitments, and support arrangements.
- Use and oversight: Output reliability, review controls, and the permissions needed for integrations.
- Business fit: Whether the service meets the task’s needs and its total cost.
Record the decision and its owner so employees know which service is approved for which purpose. The comparison is not simply about which service produces the most useful answer: data handling and access need to fit the business’s risk and the information involved.
Frequently Asked Questions
Should employees use personal AI accounts for company work?
Set a clear rule in the acceptable-use policy rather than leaving the choice to individual employees. Before authorizing any account for business information, establish who owns and controls access to it and whether its data terms meet the business’s requirements.
Can we use AI with customer information if names are removed?
Removing names does not, by itself, establish that information is safe to submit. Consider whether the remaining details identify a person or are otherwise confidential, and verify the service’s data terms before use.
Who should own AI security in a small business without an IT team?
Assign a named person to maintain the tool inventory, policy, vendor answers, and incident contacts, even if that person has other responsibilities. Give that owner a clear route to involve leadership or qualified advisers when a decision involves sensitive data or required notifications.
How often should we review our AI security rules?
Revisit them when the business adds or changes a tool, integration, data use, or employee workflow, and after a security exercise or incident. Training should also be refreshed when new tools or threats change what employees need to recognize.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

