njsscan
njsscan: A free, CI-ready Node.js SAST scanner with flexible reporting and rule controls. Ranked #18 of 25 in Static Application Security Testing Software by our editors (7.0/10); pricing: Open source; best for node.js teams needing free CI-integrated SAST.
At a glance
- Editor score7.0 / 10
- PricingOpen source
- Best forNode.js teams needing free CI-integrated SAST
- Paid fromFree
- Analysis targetSource
- Facts checked22 Sep 2026
Where it wins
- Free open-source scanning for Node.js source code
- Supports SARIF, GitLab SAST, HTML, JSON, and other reports
- Integrates with GitHub, GitLab CI/CD, Docker, and major CI tools
Where it doesn't
- Analysis is limited to Node.js applications
- No IDE support or fix guidance
- Self-hosted deployment requires local or container execution
Our verdict on njsscan
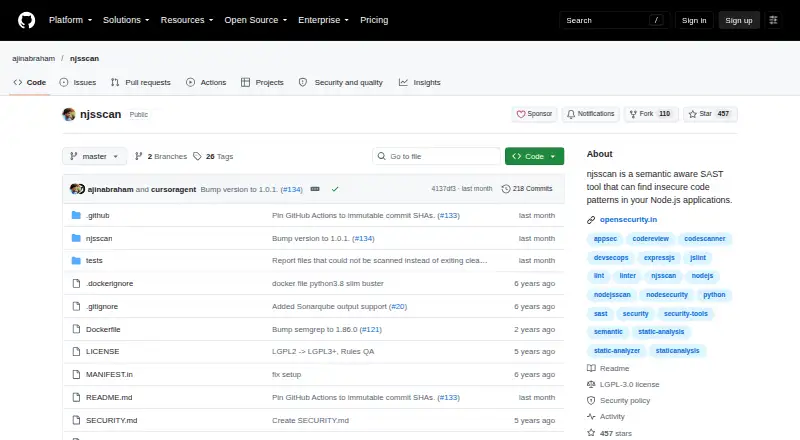
njsscan is an open-source static application security testing tool for Node.js applications. It scans source files or directories from the command line, combining pattern matching with syntax-aware semantic analysis to detect insecure code patterns. It is suited to Node.js teams that want a free scanner they can place in CI/CD workflows, run locally, or execute through Docker without moving source analysis to a hosted platform.
Its strongest area is pipeline fit and output flexibility. njsscan integrates with GitHub Actions, GitHub Code Scanning, GitLab CI/CD, Travis CI, and CircleCI, while its Docker image supports container-based execution. Findings can be exported as JSON, SARIF, HTML, SonarQube, DefectDojo, or GitLab SAST reports, giving teams several ways to feed results into existing security and development workflows. Configurable rules, ignored paths, severity filters, severity overrides, and inline suppression help teams adjust scanning behavior. A Python API is also available for programmatic use.
The pricing model is open source with a free plan, making njsscan a clear fit for teams seeking Node.js coverage without paid tiers. Its focus is also its main boundary: the verified analysis target is Node.js source code, so teams with broader language requirements should look elsewhere. The product does not provide IDE support or fix guidance, which may limit its usefulness for developers who want findings surfaced during editing or accompanied by remediation direction. Choose njsscan for configurable, CI-integrated Node.js scanning and multiple report formats; choose another SAST option when broader language coverage, IDE workflows, or fix guidance are priorities.
Your product? Our editors can test njsscan in depth and publish a review, labelled as paid · from $149/mo →
njsscan pricing
njsscan fact sheet
| Free plan | Not verified |
|---|---|
| Paid from | Free |
| Analysis target | Source |
| Supported languages | Not verified |
| IDE support | Not verified |
| CI/CD support | Yes |
| Deployment | Self-hosted |
| SCA included | Not verified |
| Fix guidance | Not verified |
| Deployment | Self-hosted |
| Platforms | macOS, Linux |
| Built for | Solo, Small business, Mid-market (editorial estimate) |
| Integrations | 5 integrations: GitHub Actions, GitHub Code Scanning, GitLab CI/CD, Travis CI, CircleCI |
| Pricing | Open source |
| Website | github.com |
| Facts checked | 22 Sep 2026 |
njsscan integrations
njsscan lists 5 integrations on its own site.
- GitHub Actions
- GitHub Code Scanning
- GitLab CI/CD
- Travis CI
- CircleCI
Alternatives to njsscan
- Semgrep CodeBroad SAST coverage with strong pull-request, IDE, CI/CD, and custom-rule support.9.2
- GitHub CodeQLA strong fit for GitHub teams that want customizable semantic code scanning.8.9
- Veracode Static AnalysisA broad cloud SAST service for enterprises securing mixed application targets.8.7
See all njsscan alternatives →
Used njsscan? Be the first to review it
The editor score above is our own research. What this page doesn't have yet is a reader's view — what you used njsscan for, what worked and what didn't. No stars are seeded and no review is paid for; an editor reads every one before it appears.
Write a reviewTwo minutes · verified accounts only · read by an editor before it appears
Featured on iTechGuides
njsscan is listed in our Static Application Security Testing Software directory. Add the badge to your site — it links back to this page.
<a href="https://www.itechguides.com/products/njsscan/"><img src="https://www.itechguides.com/best/badge/njsscan.svg" alt="Featured on iTechGuides" width="230" height="46"></a>
Reviewed by iTechGuides Editors · Editorial team · Updated Oct 2026
Advertiser disclosure: iTechGuides is reader-supported. Vendors can pay for top positions in our rankings and for a place on other products' pages, and we may earn a commission when you click some links. Bought places stand at the number bought; this page and our disclosure say so. Paying vendors may get a fuller, more detailed review from our editors, and that review can change their score. How we rank.
Last updated · How we research and update