nftables
nftables: A programmable, free Linux firewall framework for administrators who prefer local control. Ranked #60 of 76 in Firewall Software by our editors (3.2/10); pricing: Free plan; best for linux administrators needing programmable packet filtering.
At a glance
- Editor score3.2 / 10
- PricingFree plan
- Best forLinux administrators needing programmable packet filtering
- Free planYes
- Paid fromFree
- Outbound controlAdvanced
- Facts checked22 Sep 2026
Where it wins
- Filters IPv4 and IPv6 traffic in both inbound and outbound directions
- Supports stateful tracking, NAT, logging, sets, maps, and JSON rulesets
- Matches traffic by originating socket UID or GID
Where it doesn't
- Linux-only, with no support for other platforms
- Managed locally through command-line and configuration workflows
- No centralized management for administering multiple systems
Our verdict on nftables
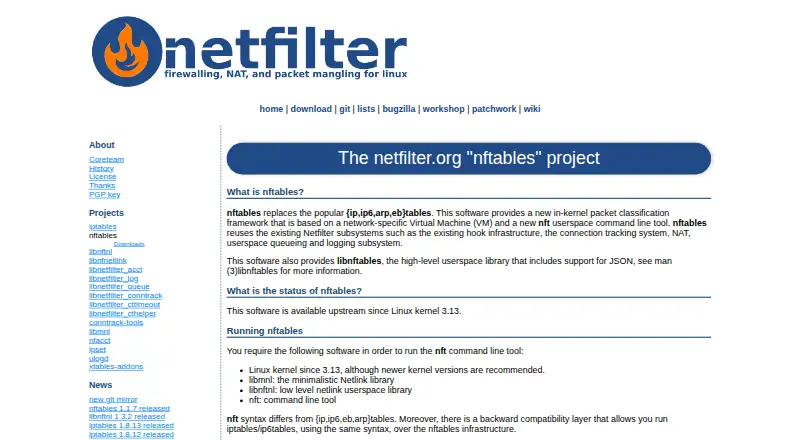
nftables is an open-source packet filtering framework for Linux, combining the nft command-line tool with a kernel subsystem for defining, inspecting, and maintaining firewall rules. It is suited to Linux administrators managing standalone hosts, servers, routers, and network appliances who need programmable control over IPv4 and IPv6 traffic. Inbound and outbound filtering hooks, stateful connection tracking, NAT, logging, and application-aware matching by socket UID or GID give it a broad foundation for host and network firewall policies.
Its strongest differentiator is the depth of its ruleset model. Administrators can organize policies with tables, chains, named sets, and maps, then list, replace, and represent rulesets in JSON. That combination supports structured rule management as well as command-line administration, while userspace log delivery provides a path for handling matching traffic outside the kernel. For teams comfortable with Linux firewall concepts, nftables offers detailed control without a commercial plan structure: the published model is free and open source.
The trade-off is operational scope. nftables is Linux-only and operates as a local framework and command-line tool rather than a hosted service with centralized management. That makes it a strong fit for administrators who want direct control on Linux systems, but a less suitable choice for organizations seeking a unified console across multiple platforms or centrally administered firewall policies. Choose nftables when programmable packet filtering, JSON ruleset handling, and local Linux management matter most; choose a centrally managed or multi-platform firewall when those requirements take priority.
Your product? Our editors can test nftables in depth and publish a review, labelled as paid · from $149/mo →
nftables pricing
nftables fact sheet
| Free plan | Yes |
|---|---|
| Paid from | Free |
| Outbound control | Advanced |
| Rule direction | Both |
| Connection alerts | No |
| Application rules | Yes |
| Supported platforms | Linux |
| Central management | Not verified |
| Deployment | Self-hosted |
| Platforms | Linux |
| Support | Community, Docs |
| Built for | Small business, Mid-market, Enterprise (editorial estimate) |
| Pricing | Free plan |
| Website | netfilter.org |
| Facts checked | 22 Sep 2026 |
Alternatives to nftables
- FortiGateA broad hybrid firewall platform for organizations that need deep security and network controls.9.4
- Arista NG FirewallA broad firewall platform with a free plan and extensive network controls.9.3
- Google Cloud NGFWGoogle Cloud-native firewall protection with free rule evaluation and usage-priced advanced controls.9.2

See all nftables alternatives →
Also Ranked In
nftables is ranked in 2 of our directories.
Used nftables? Be the first to review it
The editor score above is our own research. What this page doesn't have yet is a reader's view — what you used nftables for, what worked and what didn't. No stars are seeded and no review is paid for; an editor reads every one before it appears.
Write a reviewTwo minutes · verified accounts only · read by an editor before it appears
Featured on iTechGuides
nftables is listed in our Firewall Software directory. Add the badge to your site — it links back to this page.
<a href="https://www.itechguides.com/products/nftables/"><img src="https://www.itechguides.com/best/badge/nftables.svg" alt="Featured on iTechGuides" width="230" height="46"></a>
Reviewed by iTechGuides Editors · Editorial team · Updated Oct 2026
Advertiser disclosure: iTechGuides is reader-supported. Vendors can pay for top positions in our rankings and for a place on other products' pages, and we may earn a commission when you click some links. Bought places stand at the number bought; this page and our disclosure say so. Paying vendors may get a fuller, more detailed review from our editors, and that review can change their score. How we rank.
Last updated · How we research and update