netsniff-ng
netsniff-ng: A capable free Linux CLI toolkit for high-performance local packet capture and PCAP work. Ranked #28 of 30 in Network Protocol Analyzers by our editors (6.3/10); pricing: Free plan; best for high-performance Linux command-line capture.
At a glance
- Editor score6.3 / 10
- PricingFree plan
- Best forHigh-performance Linux command-line capture
- Free planYes
- Paid fromFree
- Facts checked20 Sep 2026
Where it wins
- Zero-copy RX_RING and TX_RING packet processing
- Captures, reads, replays, converts, and rotates PCAP files
- Includes BPF filtering, flow tracking, and packet-generation tools
Where it doesn't
- Linux-only platform support
- Command-line focus may not suit graphical workflows
- Live capture is centered on local Linux interfaces
Our verdict on netsniff-ng
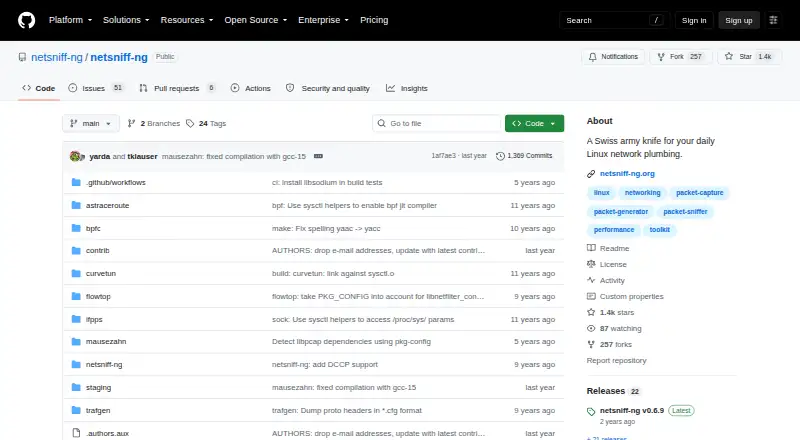
netsniff-ng is a free, open-source networking toolkit for Linux network developers, security practitioners, and administrators. Its utilities cover live packet capture, PCAP file handling, protocol dissection, traffic filtering, flow tracking, tracing, replay, and packet generation. The toolkit is distributed under the GNU GPL version 2.0 and is designed for command-line network diagnostics and analysis on Linux systems.
Performance is a central focus. Zero-copy RX_RING and TX_RING packet processing support high-performance capture and transmission, while kernel-level Berkeley Packet Filter filtering helps narrow traffic at the kernel level. The core utility can capture from Linux network interfaces, read and write PCAP files, replay captures, convert files, and rotate captures by file size or time interval. Built-in dissection covers Ethernet, WLAN, ARP, VLAN, IPv4, IPv6, ICMP, TCP, and UDP. These capabilities make netsniff-ng a strong fit for engineers who need direct control over packet workflows rather than a guided graphical interface.
The broader toolkit adds flow tracking through flowtop, along with packet-generation, tracing, and BPF compilation utilities. That breadth makes it useful when capture, replay, filtering, and flow inspection belong in one Linux-oriented workflow. Its main trade-off is focus: the platform is Linux-only, and live capture is centered on local Linux interfaces. Teams seeking a cross-platform analyzer, remote-host capture workflow, or primarily graphical experience should choose another tool. Linux users who value open-source software, CLI operation, PCAP control, and packet-processing performance should find netsniff-ng a focused option.
Your product? Our editors can test netsniff-ng in depth and publish a review, labelled as paid · from $149/mo →
netsniff-ng pricing
netsniff-ng fact sheet
| Free plan | Yes |
|---|---|
| Paid from | Free |
| Deployment | Not verified |
| Capture sources | Local |
| PCAP support | Yes |
| Traffic decryption | Not verified |
| CLI tools | Yes |
| Remote capture | Not verified |
| Flow analysis | Yes |
| Deployment | Self-hosted |
| Platforms | Linux |
| Support | Email, Community |
| Pricing | Free plan |
| Website | github.com |
| Facts checked | 20 Sep 2026 |
Alternatives to netsniff-ng
- WiresharkA broad, free desktop analyzer for live captures, PCAP files, filtering, and protocol inspection.9.4
- TSharkA free, scriptable Wireshark-based analyzer for live captures, PCAP files, and protocol workflows.9.2
- ScapyA free, programmable toolkit for crafting, capturing, decoding, and analyzing packets.9.0


See all netsniff-ng alternatives →
Used netsniff-ng? Be the first to review it
The editor score above is our own research. What this page doesn't have yet is a reader's view — what you used netsniff-ng for, what worked and what didn't. No stars are seeded and no review is paid for; an editor reads every one before it appears.
Write a reviewTwo minutes · verified accounts only · read by an editor before it appears
Featured on iTechGuides
netsniff-ng is listed in our Network Protocol Analyzers directory. Add the badge to your site — it links back to this page.
<a href="https://www.itechguides.com/products/netsniff-ng/"><img src="https://www.itechguides.com/best/badge/netsniff-ng.svg" alt="Featured on iTechGuides" width="230" height="46"></a>
Reviewed by iTechGuides Editors · Editorial team · Updated Oct 2026
Advertiser disclosure: iTechGuides is reader-supported. Vendors can pay for top positions in our rankings and for a place on other products' pages, and we may earn a commission when you click some links. Bought places stand at the number bought; this page and our disclosure say so. Paying vendors may get a fuller, more detailed review from our editors, and that review can change their score. How we rank.
Last updated · How we research and update