Falco
Falco: A focused, open-source choice for real-time Linux and Kubernetes runtime detection. Ranked #18 of 26 in Container Security Software by our editors (5.7/10); pricing: Free plan; best for open-source runtime threat detection.
At a glance
- Editor score5.7 / 10
- PricingFree plan
- Best forOpen-source runtime threat detection
- Free planYes
- Paid fromNone
- Founded2016
- Facts checked22 Sep 2026
Where it wins
- Real-time syscall monitoring with eBPF and kernel-module drivers
- Customizable YAML rules with container and Kubernetes metadata
- Forwards alerts to files, syslog, programs, and HTTP endpoints
Where it doesn't
- Primarily focuses on runtime detection and alerting
- Self-hosted deployment requires Linux or Kubernetes infrastructure
- Does not cover image, registry, admission, or SBOM workflows
Our verdict on Falco
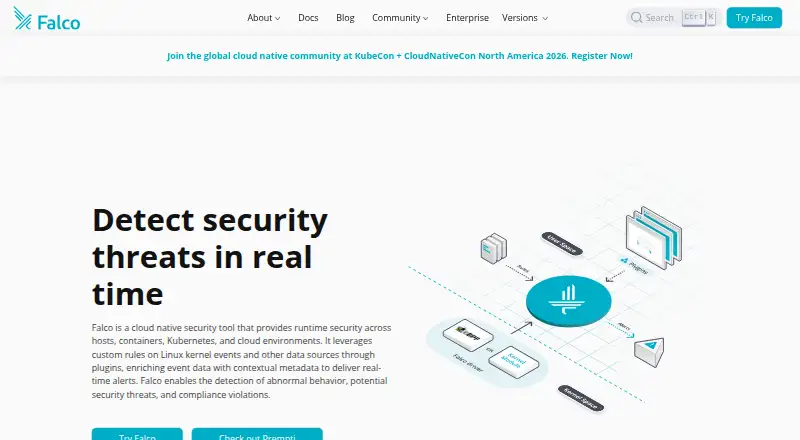
Falco is an open-source cloud-native runtime security tool for monitoring Linux hosts, containers, Kubernetes, and cloud environments. It is aimed at teams that need real-time detection of abnormal behavior, potential threats, and compliance violations without adopting a paid plan. Falco observes Linux kernel events and plugin-provided data sources, enriches them with container and Kubernetes metadata, evaluates customizable rules, and generates alerts. It can run on Linux hosts, in containers, or on Kubernetes clusters, with Kubernetes deployment available through Helm.
Its strongest capability is focused runtime visibility. Linux syscall monitoring is supported through eBPF and kernel-module event drivers, while YAML-based rules let teams customize detection logic. Plugin-based event sources extend the event inputs beyond kernel activity, and integrations include Kubernetes, AWS CloudTrail, GitHub, Okta, SIEM systems, and data lakes. Alert forwarding to files, syslog, programs, and HTTP endpoints gives teams several ways to connect Falco with existing operational and security workflows. These features make it a practical fit for organizations building their own detection and response pipeline around open-source components.
Falco’s scope is intentionally narrower than a full container security suite. It centers on runtime detection and alerting rather than image scanning, registry scanning, admission control, or SBOM generation. The self-hosted model also places deployment and operational responsibility with the adopting team, including the Linux or Kubernetes environment where Falco runs. Choose Falco when open-source runtime monitoring, customizable rules, and Kubernetes-aware alerts are the priority. Teams seeking a broader platform for securing images, registries, admission policies, and software inventories should choose a product built around those workflows instead.
Falco pricing
Falco fact sheet
| Free plan | Yes |
|---|---|
| Paid from | None |
| Image scanning | Not verified |
| Runtime protection | Yes |
| Kubernetes security | Yes |
| Registry scanning | Not verified |
| Admission control | Not verified |
| SBOM generation | Not verified |
| Deployment model | Self_hosted |
| Deployment | Self-hosted, Cloud |
| Platforms | Linux |
| Support | Community, Docs |
| Built for | Small business, Mid-market, Enterprise (editorial estimate) |
| Integrations | 50+ integrations: Kubernetes, AWS CloudTrail, GitHub, Okta |
| Pricing | Free plan |
| Website | falco.org |
| Facts checked | 22 Sep 2026 |
Falco integrations
Falco lists 50+ integrations on its own site — the 4 named here are the ones its pages call out.
- Kubernetes
- AWS CloudTrail
- GitHub
- Okta
Alternatives to Falco
- Trend Vision One Container SecurityBroad container security coverage with transparent usage-based pricing.9.0
- Qualys Container SecurityBroad container coverage with a free visibility tier and sales-led paid access.8.2
- Snyk ContainerAffordable supply-chain scanning with broad registry, CI/CD, and Kubernetes coverage.7.9


Also listed in
Used Falco? Be the first to review it
The editor score above is our own research. What this page doesn't have yet is a reader's view — what you used Falco for, what worked and what didn't. No stars are seeded and no review is paid for; an editor reads every one before it appears.
Write a reviewTwo minutes · verified accounts only · read by an editor before it appears
Featured on iTechGuides
Falco is listed in our Container Security Software directory. Add the badge to your site — it links back to this page.
<a href="https://www.itechguides.com/products/falco/"><img src="https://www.itechguides.com/best/badge/falco.svg" alt="Featured on iTechGuides" width="230" height="46"></a>
Reviewed by iTechGuides Editors · Editorial team · Updated Sep 2026
Advertiser disclosure: iTechGuides is reader-supported. We may earn a commission when you click some links. How we rank.
Last updated · How we research and update