
CRACI
CRACI: A focused CRA compliance platform with broad controls but a high starting price. Ranked #24 of 24 in Software Supply Chain Security Software by our editors (6.8/10); pricing: Paid; best for teams needing CRA-focused compliance controls.
At a glance
- Editor score6.8 / 10
- PricingPaid
- Best forTeams needing CRA-focused compliance controls
- Free planNo
- Paid from€330/mo
- Dependency analysisYes
- Founded2025 · Helsinki, Finland
- Facts checked20 Sep 2026
Where it wins
- Generates build-time SBOMs with SPDX and CycloneDX export
- Combines signing, provenance attestations, vulnerability tracking, and release gates
- Produces CRA compliance reports and ENISA reporting
Where it doesn't
- Starts at €330 per month with no free plan
- Integration is limited to GitHub Actions
- Web-only platform with advanced enterprise features reserved for Enterprise
Our verdict on CRACI
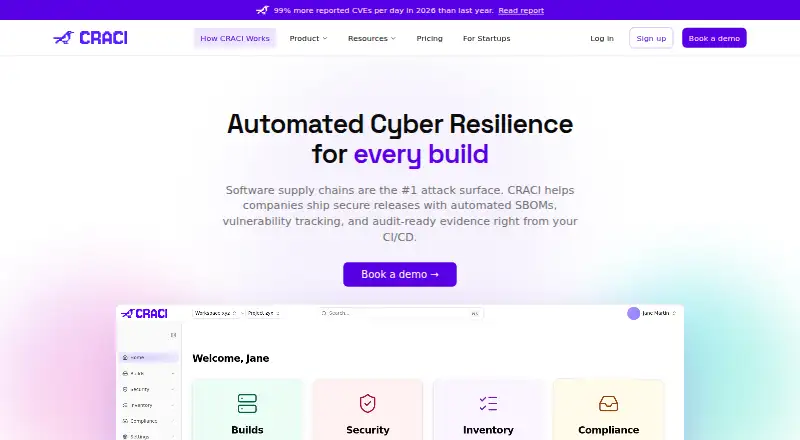
CRACI is a software supply chain security platform for teams that build and ship software. It runs GitHub Actions-compatible builds on managed runners, analyzes dependencies and components, generates verifiable SBOMs, tracks vulnerabilities, signs artifact provenance, and produces compliance evidence. Its feature set is aimed at startups, SaaS providers, enterprises, agencies, and hardware makers addressing Cyber Resilience Act requirements. Teams seeking CRA-focused controls will find a focused fit, while organizations needing broader platform coverage may need to look elsewhere.
The published plans show a paid-only model. Pro costs €330 per month and is designed for growing teams and businesses, with 1–20 users, one actively monitored SBOM, 10,000 build minutes, and Standard support. Enterprise is intended for large organizations with specific needs and adds EU data residency, custom data retention, SAML and SSO, ISO 27001 and SOC 2, and Priority support. That structure makes the product easier to evaluate by organization size and governance requirements, but the Pro starting price places it toward teams with a defined compliance budget rather than smaller projects seeking an entry-level option.
CRACI’s strongest distinction is the way its build controls connect operational security with compliance reporting. Dependency analysis, continuous vulnerability tracking, artifact signing, provenance attestations, and deploy and release compliance gates cover key stages from build to release. CRA and ENISA reporting further support evidence collection. The platform is web-based and currently integrates with GitHub Actions through compatible managed runners, so teams already centered on that workflow are the clearest match. Organizations requiring multiple CI/CD integrations, a broader ecosystem, or a lower-cost starting point should consider an alternative.
Your product? Our editors can test CRACI in depth and publish a review, labelled as paid · from $149/mo →
CRACI pricing
All 2 CRACI plans and prices →
CRACI fact sheet
| Free plan | No |
|---|---|
| Paid from | €330/mo |
| Source & repo security | Not verified |
| Dependency analysis | Yes |
| SBOM management | Yes |
| Build provenance | Yes |
| Artifact signing | Yes |
| Provenance attestations | Yes |
| Release policy gates | Yes |
| Deployment | Cloud |
| Platforms | Web |
| Compliance & security | SOC 2, ISO 27001, SSO/SAML |
| Support | Email, Docs |
| Built for | Small business, Mid-market, Enterprise (editorial estimate) |
| Integrations | 1 integrations: GitHub Actions |
| Pricing | Paid (source) |
| Website | craci.com |
| Facts checked | 20 Sep 2026 |
CRACI integrations
CRACI lists 1 integrations on its own site.
- GitHub Actions
Alternatives to CRACI
- DevGuardBroad supply-chain security coverage with self-hosted and managed deployment options.9.4
- ChainloopOpen-source evidence management with policy gates and enterprise governance options.9.2
- Anchore EnterpriseDeep SBOM, vulnerability, malware, secrets, and policy controls for hybrid pipelines.9.0


Used CRACI? Be the first to review it
The editor score above is our own research. What this page doesn't have yet is a reader's view — what you used CRACI for, what worked and what didn't. No stars are seeded and no review is paid for; an editor reads every one before it appears.
Write a reviewTwo minutes · verified accounts only · read by an editor before it appears
Featured on iTechGuides
CRACI is listed in our Software Supply Chain Security Software directory. Add the badge to your site — it links back to this page.
<a href="https://www.itechguides.com/products/craci/"><img src="https://www.itechguides.com/best/badge/craci.svg" alt="Featured on iTechGuides" width="230" height="46"></a>
Reviewed by iTechGuides Editors · Editorial team · Updated Oct 2026
Advertiser disclosure: iTechGuides is reader-supported. Vendors can pay for top positions in our rankings and for a place on other products' pages, and we may earn a commission when you click some links. Bought places stand at the number bought; this page and our disclosure say so. Paying vendors may get a fuller, more detailed review from our editors, and that review can change their score. How we rank.
Last updated · How we research and update