bundler-audit
bundler-audit: A focused, open-source Gemfile.lock auditor for Ruby teams, with offline scans and JSON output. Ranked #61 of 65 in Software Composition Analysis Software by our editors (5.3/10); pricing: Open source; best for ruby teams auditing Bundler dependencies.
At a glance
- Editor score5.3 / 10
- PricingOpen source
- Best forRuby teams auditing Bundler dependencies
- Paid fromFree
- Founded2013
- Facts checked19 Sep 2026
Where it wins
- Finds vulnerable gem versions and insecure HTTP or Git sources.
- Prints advisory details and remediation versions; exports JSON.
- Supports custom lockfiles, Rake tasks, and offline operation.
Where it doesn't
- Limited to Ruby gems and Bundler projects.
- Does not provide SBOM generation or reachability analysis.
- Does not scan pull requests.
Our verdict on bundler-audit
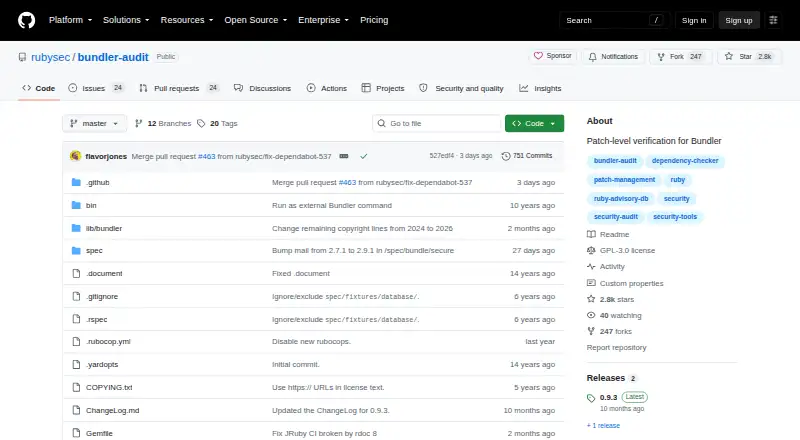
bundler-audit is an open-source command-line tool for Ruby and Bundler projects. It checks Gemfile.lock files for vulnerable gem versions and insecure gem sources, using ruby-advisory-db for vulnerability information. Ruby teams can use it in local development or CI to audit dependencies and inspect advisory details, including remediation versions. Its narrow scope suits teams looking specifically for Bundler dependency checks rather than a broader software composition analysis platform.
The tool focuses on lockfile auditing: it can update the advisory database, scan a custom Gemfile.lock path, and ignore selected advisories. Results can be printed as advisory information or exported as JSON. Rake tasks cover auditing and database updates, fitting projects that already use Rake. It can also run without a network connection, which supports offline audit workflows, though database updates require access to the advisory database. The published repository lists version 0.9.3 as its latest release.
bundler-audit is self-hosted, installed as a Ruby gem, and runs on Linux and macOS. It integrates with Rake and ruby-advisory-db; this is a focused Ruby ecosystem fit, not a multi-language dependency management layer. Teams needing SBOM generation, reachability analysis, or pull request scanning should choose a broader tool. For Ruby teams seeking a free, open-source way to check Bundler lockfiles and review remediation versions, its limited scope is also its practical advantage.
Your product? Our editors can test bundler-audit in depth and publish a review, labelled as paid · from $149/mo →
bundler-audit pricing
bundler-audit fact sheet
| Free plan | Not verified |
|---|---|
| Paid from | Free |
| Supported ecosystems | Ruby gems and Bundler |
| SBOM generation | Not verified |
| Reachability analysis | Not verified |
| Pull request scanning | Not verified |
| Monitored projects | Not verified |
| Deployment options | Self_hosted |
| Deployment | Desktop |
| Platforms | Linux, macOS |
| Integrations | 2 integrations: Rake, ruby-advisory-db |
| Pricing | Open source |
| Website | github.com |
| Facts checked | 19 Sep 2026 |
bundler-audit integrations
bundler-audit lists 2 integrations on its own site.
- Rake
- ruby-advisory-db
Alternatives to bundler-audit
- Snyk Open SourceBroad SCA coverage with reachability, SBOMs, pull-request scanning, and monitoring.9.4
- FOSSAA mature SCA platform covering dependencies, SBOMs, containers, licenses, and policy controls.9.3
- Safeguard SCAA budget-conscious SCA platform with reachability analysis, SBOMs, and remediation workflows.9.1

See all bundler-audit alternatives →
Also Ranked In
bundler-audit is ranked in 2 of our directories.
Used bundler-audit? Be the first to review it
The editor score above is our own research. What this page doesn't have yet is a reader's view — what you used bundler-audit for, what worked and what didn't. No stars are seeded and no review is paid for; an editor reads every one before it appears.
Write a reviewTwo minutes · verified accounts only · read by an editor before it appears
Featured on iTechGuides
bundler-audit is listed in our Software Composition Analysis Software directory. Add the badge to your site — it links back to this page.
<a href="https://www.itechguides.com/products/bundler-audit/"><img src="https://www.itechguides.com/best/badge/bundler-audit.svg" alt="Featured on iTechGuides" width="230" height="46"></a>
Reviewed by iTechGuides Editors · Editorial team · Updated Oct 2026
Advertiser disclosure: iTechGuides is reader-supported. Vendors can pay for top positions in our rankings and for a place on other products' pages, and we may earn a commission when you click some links. Bought places stand at the number bought; this page and our disclosure say so. Paying vendors may get a fuller, more detailed review from our editors, and that review can change their score. How we rank.
Last updated · How we research and update