BruteShark
BruteShark: A free, extraction-focused analyzer for PCAP investigations on Windows and Linux. Ranked #21 of 31 in Network Packet Analyzer Software by our editors (6.6/10); pricing: Free plan; best for free extraction-focused investigations.
At a glance
- Editor score6.6 / 10
- PricingFree plan
- Best forFree extraction-focused investigations
- Free planYes
- Paid fromFree
- Operating systemsWindows and Linux
- Facts checked21 Sep 2026
Where it wins
- Extracts credentials, passwords, authentication hashes, DNS queries, and files
- Reconstructs TCP, UDP, SIP, and RTP sessions from captured traffic
- Combines a Windows GUI with command-line processing on Windows and Linux
Where it doesn't
- Windows is required for the graphical application
- No AI features are included
- Maintenance status is not clearly documented
Our verdict on BruteShark
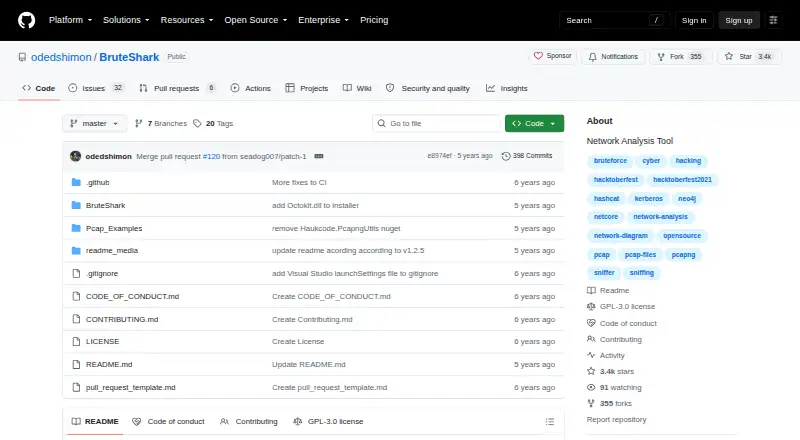
BruteShark is an open-source network forensic analysis tool for security researchers and network administrators. It analyzes PCAP and PCAPNG traffic, while also supporting live capture from a network interface. The Windows application provides a graphical interface, and the command-line tool runs on Windows and Linux. Its focus is investigative extraction rather than general network monitoring, with features for credentials, authentication hashes, DNS queries, sessions, files, and VoIP calls.
BruteShark is free and open source, with no paid workflow to compare across plan tiers. The platform fit is clear: Windows users can access the GUI and CLI, while Linux users can use the CLI. Command-line processing can handle files or directories and export results to standard output or files. Hashcat export supports a password-analysis workflow, and Neo4j integration connects network-map output with that ecosystem. PCAP and PCAPNG support also gives investigators a defined capture-file scope.
Its standout value is the breadth of extraction in one forensic workflow. BruteShark can capture traffic, generate visual network maps, extract DNS activity, reconstruct TCP and UDP sessions, carve files, and extract VoIP calls from SIP and RTP traffic. Credential and password extraction, plus authentication-hash extraction with Hashcat export, make it suited to focused investigations. Choose BruteShark when free, open-source analysis and extraction are priorities. Choose another tool if you need a graphical application on Linux, support for platforms beyond Windows and Linux, or AI features.
Your product? Our editors can test BruteShark in depth and publish a review, labelled as paid · from $149/mo →
BruteShark pricing
BruteShark fact sheet
| Free plan | Yes |
|---|---|
| Paid from | Free |
| Live capture | Yes |
| Command-line tool | Yes |
| Traffic decryption | Not verified |
| Operating systems | Windows and Linux |
| Capture file formats | PCAP and PCAPNG |
| Protocol dissectors | Yes |
| Deployment | Desktop |
| Platforms | Windows, Linux |
| Support | Email, Community, Docs |
| Built for | Solo, Small business, Mid-market (editorial estimate) |
| Integrations | 2 integrations: Hashcat, Neo4j |
| Pricing | Free plan |
| Website | github.com |
| Facts checked | 21 Sep 2026 |
BruteShark integrations
BruteShark lists 2 integrations on its own site.
- Hashcat
- Neo4j
Alternatives to BruteShark
- WiresharkA complete free analyzer for live capture, offline analysis, protocol inspection, and packet decryption.9.4
- TSharkA free, open-source choice for structured, scriptable packet analysis.9.2
- tcpdumpA free, open-source choice for precise capture, filtering, and PCAP inspection.9.0


See all BruteShark alternatives →
Used BruteShark? Be the first to review it
The editor score above is our own research. What this page doesn't have yet is a reader's view — what you used BruteShark for, what worked and what didn't. No stars are seeded and no review is paid for; an editor reads every one before it appears.
Write a reviewTwo minutes · verified accounts only · read by an editor before it appears
Featured on iTechGuides
BruteShark is listed in our Network Packet Analyzer Software directory. Add the badge to your site — it links back to this page.
<a href="https://www.itechguides.com/products/bruteshark/"><img src="https://www.itechguides.com/best/badge/bruteshark.svg" alt="Featured on iTechGuides" width="230" height="46"></a>
Reviewed by iTechGuides Editors · Editorial team · Updated Oct 2026
Advertiser disclosure: iTechGuides is reader-supported. Vendors can pay for top positions in our rankings and for a place on other products' pages, and we may earn a commission when you click some links. Bought places stand at the number bought; this page and our disclosure say so. Paying vendors may get a fuller, more detailed review from our editors, and that review can change their score. How we rank.
Last updated · How we research and update