
Free tools Windows power users keep installed
One-click scans. No signup required.
GCHQ’s “ghost” proposal was a 2018 discussion of targeted, provider-assisted access to encrypted communications—not legislation and not a universal key for unlocking every conversation. Its core idea was that a service provider could silently add an authorised law-enforcement participant to a particular chat or call. The debate is whether that can be done without weakening the authentication and trust users rely on when they believe a conversation is end-to-end encrypted.
What GCHQ’s ghost proposal described
On 29 November 2018, Ian Levy and Crispin Robinson, technical officials associated with GCHQ and the National Cyber Security Centre, published an essay in Lawfare proposing a way to obtain what they called “exceptional access.” They did not propose a new law in that essay. They described targeted government-authorised access carried out with help from a communications provider. Read the essay on Lawfare.


Their example was a provider adding a law-enforcement participant to a group conversation. Because the service manages user identities and introduces participants, the authors argued, it could add another endpoint without breaking the encryption algorithm. They also contemplated suppressing the usual notification of that membership change—on the target’s device and potentially on other participants’ devices. The essay’s account of the mechanism.
Levy and Robinson framed the proposal as a response to “going dark”: investigators’ difficulty accessing communications when services use strong encryption. They wrote, “In a world of encrypted services, a potential solution could be to go back a few decades.” Their analogy was to adding a participant to a conversation, rather than defeating encryption by recovering a master key.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
#1 Best Overall
What the authors said should constrain access
The essay set out six principles for an exceptional-access approach. These are the authors’ stated aims; listing them does not establish that a ghost mechanism would satisfy them in practice.
- Legal authorisation and least intrusion: access should be authorised through legal process and limited to what is necessary.
- Investigative tradecraft should evolve: lawful investigative methods should adapt as communications technology changes.
- Access cannot be universal: the authors said investigators should not expect access in every case, writing, “Even when we have a legitimate need, we can’t expect 100 percent access 100 percent of the time.”
- No unfettered government access: the proposal was not presented as a general power to enter conversations at will.
- Preserve the provider-user relationship: providers would remain involved in the service and in any access mechanism.
- Transparency: the authors included transparency as a guiding principle, though a covert addition would necessarily raise questions about what could be disclosed and when.
They explicitly rejected global key escrow in their essay. That distinction matters: their proposal was for provider-assisted access to selected communications, not a single stored key intended to decrypt everyone’s messages.
Why critics say a “ghost” still changes the security model
End-to-end encryption is intended to let only the communicating endpoints read message content. The authors’ argument was that adding a participant through the service’s identity and participant-management functions would leave the encryption algorithm intact. Critics focused on a different layer: if the provider can silently change who counts as an endpoint, users may not be able to authenticate who is actually present in the conversation.
Rank #2
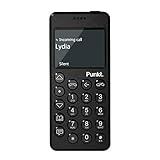
- Distraction Free: The MP02 4G cell phone makes it easier to be where you are—whether that’s a weekend away or an important business meeting. Keep what matters close with calls and SMS-first texting, without the constant onslaught of designed-for-addiction notifications.
- Privacy & Security Focused: Built with security in mind from the start, the MP02 is designed to help safeguard your information without requiring you to share more personal data than necessary. Enjoy peace of mind with a phone experience that prioritizes discretion and control.
- Carrier Compatibility & Connection: AT&T is supported (coverage verified, VoLTE supported). T-Mobile is supported, but VoLTE is not supported. Verizon is not supported. Many US carriers use VoLTE for voice calls - if VoLTE isn’t supported on your carrier, call performance may be limited even with signal. The MP02 supports 4G LTE across key bands (2G: 850/900/1800/1900 3G: WCDMA 1/2/4/5/6/8/19 4G: FDD LTE 1/2/3/4/5/7/8/12/17/19/20).
- Simple By Design: A minimalist interface keeps everyday actions straightforward. Call and text buttons provide quick access, while a streamlined menu helps you stay focused on essentials. Note: messaging is SMS-first (MMS group chats aren’t supported), helping to keep communication simple.
- Built for Everyday: Designed for comfortable one-handed use with a clean, minimalist silhouette. Reinforced glass fiber construction supports daily use, while the lightweight shape makes it easy to carry anywhere.
A coalition letter coordinated by New America’s Open Technology Institute and published through Lawfare in May 2019 warned that the proposal could undermine authentication systems, introduce vulnerabilities, and create risks of abuse or misuse. It argued that users need to know who is on the other end of a conversation for encryption to protect them. The letter stated: “This proposal to add a ‘ghost’ user would violate important human rights principles, as well as several of the principles outlined in the GCHQ piece.” These are the coalition’s objections, not evidence that a deployed ghost system was breached. Read the coalition letter.
The disagreement is therefore not simply whether encryption is switched on or off. It concerns whether the service can secretly alter the set of participants and whether users can detect or verify that change. Even if the cryptographic algorithm remains unchanged, changing authentication or participant-handling rules may alter the service’s security and trust properties.
Questions that determine whether targeted access stays targeted
The 2018 essay and 2019 letter make several questions central to evaluating any proposed implementation. The sources establish these as design and governance issues; they do not provide a public implementation specification or demonstrate how a real system would behave.
- Can the provider silently change group membership? The example depends on adding a participant without normal notification. That capability is the mechanism, not a side issue.
- Can participants verify who is present? A system’s assurances depend partly on whether users can authenticate participants and detect membership changes.
- Who authorises and executes a request? The authors argued for legal authorisation and provider involvement. Those principles still leave practical questions about approvals, controls, auditability and implementation.
- How is a target defined and limited? The proposal is described as targeted, but the available sources do not specify an operational design that proves an intervention cannot affect other users or conversations.
- What risks reach people beyond the target? A change to identity or participant-management functions could have consequences for the other people in a chat or call, as well as for the target.
How UK law and parliamentary scrutiny fit into the debate
The ghost proposal should not be confused with the UK’s warrant framework or treated as a power created by the 2018 essay. GCHQ says interception warrants under the Investigatory Powers Act 2016 require authorisation by a Secretary of State and approval by an independent Judicial Commissioner, and must meet necessity and proportionality tests on specified grounds. GCHQ’s explanation of exceptional access and warrants. That describes formal legal oversight; it does not settle whether a particular engineering approach would preserve security.
During scrutiny of the draft Investigatory Powers Bill in 2016, the Joint Committee supported seeking access to protected communications when required by a warrant, while recommending that the legislation make clear it would not require compromised encryption keys or installed backdoors. The committee also called for clarity about cases where a provider offering end-to-end encryption could not practicably supply decrypted content. Its recommendation said: “We agree with the intention of the Government’s policy to seek access to protected communications and data when required by a warrant, while not requiring encryption keys to be compromised or backdoors installed on to systems.” Joint Committee report on the draft Investigatory Powers Bill.
In a later response to consultation on revised notices regimes, the UK government said it “fully support[s] the responsible use of strong encryption, including end-to-end encryption,” while also arguing that encryption had reduced law-enforcement and intelligence capabilities. The response discussed proposed notice changes and objections concerning security, innovation and product decisions. That is later policy context, not part of the specific 2018 ghost proposal. Government response on the revised notices regime.
What is—and is not—established about the proposal
The public sources describe the 2018 idea and the objections it prompted. They do not establish that a ghost mechanism was deployed, provide a public technical specification for one, or resolve whether a specific implementation could meet the authors’ safeguards. The accurate takeaway is that the proposal was a policy argument for targeted, provider-assisted lawful access—and that its central technical controversy is whether covertly changing participant membership can be reconciled with the authentication and trust users expect from end-to-end encrypted services.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

