
Free tools Windows power users keep installed
One-click scans. No signup required.
Choose the boundary according to what the agent can execute, what it can access, and what else shares its host. A standard container shares the host kernel; gVisor adds a userspace isolation layer while retaining container workflows; a VM or microVM gives the workload a guest kernel behind a hypervisor. None is a complete security solution: mounts, credentials, network access, tools, and resource limits remain separate decisions.
Start with the kernel boundary
A container is not a small virtual machine. It packages an application and uses operating-system mechanisms to isolate processes, but the container and host still share the host kernel. That distinction matters when untrusted code can probe the kernel or exploit a vulnerability in it. NIST’s Application Container Security Guide, published September 25, 2017 and updated May 4, 2021, describes containers as operating-system virtualization combined with application packaging.
A VM runs a guest operating system, including its own kernel, on virtualized hardware managed by a hypervisor. This creates a different boundary from a conventional container, but it does not make the host, hypervisor, guest configuration, or interfaces invulnerable. A microVM is a lightweight VM design that retains the guest-kernel and hypervisor-style boundary; the label alone does not establish a particular security level or performance result.
gVisor takes another approach. Its userspace Sentry implements an application-kernel interface, handling system calls rather than passing them directly to the host kernel in the conventional container model. Google’s living gVisor architecture and security documentation describes this as a way to reduce direct exposure to the host kernel, not as a guarantee against every escape or configuration failure.
#1 Best Overall
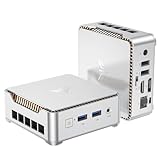
- 【Ryzen 5 3500U Processor】KAMRUI Essenx E2 Mini PC is equipped with AMD Ryzen 5 3500U (4-cores/8-threads, up to 3.7GHz) with integrated Radeon Vega 8 Graphics(1200MHz, 8 Core). The 3500U CPU operates at a base frequency of 2.1 GHz and a Boost frequency of 3.7 GHz. This DDR supports upgradable up to 32GB, SSD supports up to 2TB.(NOT INCLUED), KAMRUI E2 3500U Mini PC is ideal for light office work and home entertainment. KAMRUI E2 3500U is more than 35% more powerful and smoother in operation than the Intel N150, 33% faster than Intel N95, 28% performance boost over Intel i3-10110U, and 42% stronger processing power than AMD Ryzen 3 3200U.
- 【16GB DDR4 & 256GB SSD】The KAMRUI E2 mini computers is equipped with 16GB DDR4(Expandable up to 32GB) for faster multitasking and smooth application switching. 256GB M.2 SSD ensures fast startup times,fast file transfers and plenty of storage space,eliminating slow loading times and ensuring fast responsiveness.Storage space can RAM supports up to 32 GB, SSD supports up to 2TB (Not included)make file storage easier.
- 【4K Dual Display & USB 3.2 Type-A Port】KAMRUI E2 3500U mini desktop pc is equipped with an HDMI 2.0+DP 1.4 interfaces for faster transmission, Support Dual 4K@60Hz Display, E2 mini desktop computers is ideal for visual home entertainment, home office, conference rooms, etc. USB3.2 Gen1 Type-A Port×2 with a transfer speed of up to 5Gbps (10 times faster than USB 2.0) for efficient data transfer. The RJ45 1000M Gigabit Ethernet Port ensures a stable network connection.
- 【WiFi+Bluetooth stable connection】The Kamrui E2 micro pc have reliable and stable wireless connection, open websites in seconds, watch movies without buffering and download files smoothly, connect your monitor from WiFi or Ethernet, use a wireless keyboard and mouse through bluetooth, which will be powerful workstation for you.
- 【Versatile Ports】This KAMRUI E2 Small pc is equipped with HDMI 2.0×1(4K@60Hz)、DP1.4×1(4K@60Hz)、Gigabit Ethernet Port (RJ45, 10/100/1000Mbps) ×1、USB3.2 Gen1 Type-A Port×2(5Gbps)、USB2.0 Type-A Port×2、3.5mm Audio Jack ×1、DC In ×1、Power Button ×1
Compare the four approaches
| Approach | Main boundary | Best fit | Trade-offs to evaluate |
|---|---|---|---|
| Standard container | Process isolation using host-kernel mechanisms; shares the host kernel. | Trusted workloads, or cases where the threat model accepts a shared-kernel boundary and conventional container workflows are valuable. | The host kernel remains in the attack path. Least privilege, namespaces, seccomp, and other controls need deliberate configuration; hardening does not make a container equivalent to a VM. (NIST SP 800-190; Google gVisor architecture documentation.) |
| gVisor / sandboxed container | A userspace Sentry provides an application-kernel interface and reduces direct host-kernel exposure. | Workloads that benefit from OCI/container ergonomics but need an additional isolation layer. | Check system-call and feature compatibility, filesystem and network behavior, runtime configuration, and workload-specific performance. (Google gVisor architecture, overview, and security documentation.) |
| VM | A guest kernel and OS run behind a hypervisor on virtualized hardware. | Untrusted code or tenant workloads for which a separate guest-kernel boundary justifies the operating cost. | Account for guest OS and image management, startup and resource needs, hypervisor and device-emulation attack surface, and lifecycle operations. Costs vary by workload and implementation; no universal figure is established here. (Google gVisor architecture documentation.) |
| MicroVM | A lightweight VM design with a guest kernel and hypervisor-style boundary. | Ephemeral or agent execution where VM-style separation is desired alongside a focused virtual-machine design. | Check platform support, provisioning and image lifecycle, compatibility, network and filesystem sharing, and measured per-workload cost. Docker’s product documentation describes an implementation for agent sandboxes, not a universal or independent performance comparison. (Docker Sandboxes documentation; Kubernetes SIGs Agent Sandbox threat model.) |
Choose based on trust, tenancy, and blast radius
Before choosing a runtime, write down what must remain protected if a prompt-injection attempt succeeds or the workload is compromised. Ask whether the agent can run arbitrary or model-generated code, install packages, start subprocesses or containers, access tenant data, or act without a person approving each operation. Also identify whether workloads from different customers or trust levels share a host.
The Kubernetes SIGs Agent Sandbox threat model identifies untrusted LLM-generated code, isolation escape, attacks on other resources, control-plane access, cross-tenant network attacks, and resource exhaustion as relevant threats. Treat that as a useful threat checklist, not proof that any single sandbox design prevents those outcomes.
Rank #2

- 【Great power in a small computer】Get fast performance from the AMD Ryzen 5 3500U CPU (2.1GHz-3.7GHz, 4 Cores 8 Threads) inside this mini pc, TDP 15W up to 25W. It's perfect for all your home office and business use, like daily computing, web browsing, and smooth media streaming. This small desktop computer handles everyday tasks easily and quietly.
- 【Work on many things at once with lots of storage】This mini PC comes with 16GB of fast DDR4 RAM (expandable up to 32GB), allowing you to smoothly run multiple programs, dozens of browser tabs, and large files all at once. It also features a spacious 512GB NVMe SSD that provides ample storage and delivers dramatically faster boot-ups, app launches, and file transfers compared to a traditional hard drive.
- 【See everything clearly on one or two 4K screens】Connect one or two monitors for more space to work or play. Dual HDMI ports on this mini pc support super sharp 4K Ultra HD video. It's great for doubling your work area for business or watching movies in high definition.
- 【Fast modern connections in a tiny box】Enjoy a better and more stable internet connection with the latest WiFi 6. Use Bluetooth 5.3 to connect wireless headphones, keyboards, and mice without wires. This small pc is very compact to save desk space and has extra USB ports (USB 2.0×2, USB 3.0×2, Type-c 2.0×1, Type-c 3.2 full featured×1, HDMI×2) for your printer, webcam, or other computer accessories.
- 【Reliable Warranty and Support】We provides 1 year warranty for each Mini computers. So you don't need to worry about any product problems. If you have any questions about the product, please contact our customer service, we will provide 24-hour professional technical support and serve you at any time.
- Trusted, tightly constrained work: A standard container may be proportionate when the team accepts a shared host kernel and has narrowly constrained the workload’s access.
- Untrusted code with container workflow requirements: Evaluate gVisor against the actual workload and configuration; verify required system calls and filesystem and network behavior.
- Untrusted or multi-tenant execution requiring a separate guest-kernel boundary: Consider a VM or microVM, then include its image, hypervisor, provisioning, and operational responsibilities in the design.
These are decision starting points, not security rankings. A stronger runtime boundary cannot compensate for a reachable host service, overpowered credential, exposed control plane, or unsafe tool server.
Review every path out of the sandbox
Workspace and mounts
A read-write host workspace lets agent changes reach those host files. A private clone instead gives the operator a review point before changes are brought back. Docker Sandboxes documentation describes mountless, direct-mount, and clone workflows as product-specific options; choose based on which files the agent must read or modify, not simply on the runtime label.
PC Slower Than It Used to Be?
A free scan shows the junk files, broken settings and background clutter dragging Windows down - then fixes them in one click.Free scan · Windows 10 & 11Outdated Drivers Are Slowing You Down
One free scan finds every outdated or missing driver and matches the right update for your exact hardware.Free scan · exact hardware matchRank #3

- 【AMD Ryzen 3 5300U CPU: Outperforms N150 & 3500U】 BOSGAME E5 mini PC is powered by the TSMC 7nm FinFET architecture AMD Ryzen 3 5300U processor (4 Cores, 8 Threads, up to 3.8GHz boost, 6MB total cache). Compared to low-end Intel N150 or 3500U chips which only have 4 single threads and throttle under load, the 5300U delivers over 30% faster multi-core speed. Run 30+ browser tabs, large Excel sheets, and Zoom meetings simultaneously without system lag.
- 【8GB DDR4 RAM & 256GB NVMe SSD Storage】 Installed with high-speed 8GB DDR4 dual-channel memory and a fast 256GB M.2 2280 SSD, eliminating slow boot times and application loading delays. To accommodate growing data requirements, the upgradeable hardware design features dual SODIMM slots that allow you to expand memory up to 64GB RAM, ensuring smooth operation during heavy multitasking.
- 【High-Capacity Dual M.2 SSD Storage Expansion】 Never worry about running out of space for your business files. In addition to the pre-installed 256GB system drive, the motherboard houses an extra empty internal M.2 2280 NVMe PCIe 3.0 slot. This allows you to easily add a second solid-state drive for up to an additional 2TB of storage capacity (upgrades not included) without needing to remove or reinstall the original operating system.
- 【Radeon 6-Core Graphics & Triple 4K Displays】 Integrated with official AMD Radeon Graphics (6 Graphics Cores, 1500 MHz frequency) for casual gaming, photo editing, and crisp 4K media decoding. Featuring 1x HDMI 2.0 port, 1x DisplayPort, and 1x Full-Function Type-C port, the E5 outputs true 4K@60Hz resolution to three monitors at once. This multi-screen setup eliminates constant window-switching for traders, programmers, and office workers.
- 【Dual 2.5GbE LAN Ports for Advanced Networking】 Experience fast wired network transmission speeds up to 2500Mbps without lagging or buffering. The integration of dual 2.5 Gigabit Ethernet ports (powered by Realtek RTL8125 controller) makes this compact computer an exceptional hardware choice for tech enthusiasts. Easily configure it into software routers, hardware firewalls (pfSense, OpnSense), home NAS servers, or local homelabs.
Docker access and local tools
Do not casually expose the host Docker socket to untrusted code: access to the host daemon can confer broad capability. A separate daemon inside a VM changes that boundary, but inspect any external helper or local tool independently. A tool server running on the host may perform actions outside the sandbox even when the agent process itself is isolated. Trace each registered tool’s process location, permissions, and credentials.
Credentials
A VM does not hide credentials deliberately forwarded into it. Docker’s Sandboxes isolation-layer documentation explains that an SSH agent can be forwarded while private keys remain on the host. In that arrangement, sandbox code may still ask the agent to authenticate or sign. Decide which operations and repositories each forwarded credential can reach, and avoid forwarding access the workload does not need.
Rank #4
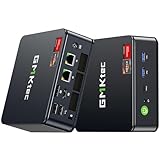
- Office Gaming Mini PC - UPGRADED GMKtec Nucbox M5 Ultra Series is equipped with the powerful AMD Ryzen 7 7730U processor, 8 Cores/16 Threads, Base 2.00GHz (Power Saving Quiet Mode) with Turbo Boost up to 4.50GHz (Performance Mode) in BIOS settings, Based on the ZEN 3+ architecture, this small but powerful mini pc delivers satisfying results in productivity, office work, and gaming. 35% Performance increase over AMD Ryzen 5 7430U/ Ryzen 7 5700U, 5600U, 5560U, 5500U.
- 16GB DDR4 RAM & 256GB PCIe SSD - Installed with DDR4 16GB RAM (1x16GB), the Nucbox M5 Ultra mini pc support expansion to 64GB RAM. Featured with 256GB M.2 2280 PCIe 3.0 SSD, support dual slot expansion to 4TB SSD. (Upgrades not included)
- DUAL NIC LAN 2.5G RJ45 - Fast Network Speeds: Enjoy up to 2500Mbps data transmission speed without worrying about lagging. Ideal for working, gaming, and surfing the internet. Great for Untangle, Pfsense or as a server office PC.
- Mini Desktop Computer with 4K Triple Screen Display - Nucbox M5 Ultra integrates AMD Radeon Graphics 8 Cores 2000 MHz GPU to deliver powerful graphics processing power to easily handle the demands of complex design software, 4K@60Hz UHD video editing, and playback. It can connect to 3 display screens simultaneously.
- Fast Internet WiFi 6E + BT5.2 Connection - GMKtec Mini PC with WiFi-6E Wireless, have 2.5G/5G/6G triple band, more faster and lower latency. Bluetooth 5.2 allowing you more quickly to connect other wireless devices (headset, mouse, keyboard, etc.) Interface features 2*USB3.2 ports, 2*USB2.0 ports, 1*HDMI 2.0 port(4K@60Hz), 1*USB-C port(PD/DP/DATA), 1*DP Port, 1*Audio 3.5mm (HP&MIC), 1*DC Power Port.
Network and control-plane access
Restrict destinations, deny access to internal services and metadata endpoints where appropriate, and block sandbox-to-sandbox traffic by default unless the workload requires it. Avoid exposing Kubernetes API credentials to workload pods by default; grant explicit authorization only when necessary. The Kubernetes SIGs Agent Sandbox documentation describes default restrictions for its managed NetworkPolicy mode, but network-policy behavior and defaults are implementation- and version-specific.
Resource exhaustion and cleanup
Set CPU, memory, and storage limits for workloads, and ensure ephemeral execution environments and their data are cleaned up. Isolation from other processes does not by itself prevent a workload from consuming shared capacity.
Best Value

- WHY CHOOSE G3 ULTRA MINI PC PENTIUM GOLD 7505 - Choose the Intel Pentium Gold 7505 for snappier everyday responsiveness: It delivers up to 30% faster single-core performance than the Ryzen 5 3500U, making office apps and web browsing feel noticeably quicker, while its Intel UHD Graphics (48 EUs) provides 2.4x the GPU performance of the N100 & N150's 24-EU graphics, ensuring smoother 4K streaming and light photo editing.
- 16GB RAM MEMORY & 512GB STORAGE - GMKtec Nucbox G3 Ultra mini computer is prebuilt with 16GB LPDDR4 RAM at 3200 MT/s, you will enjoy a speedier experience with Built-in 512GB M.2 SATA Hard Drive. Our mini desktop pc boots up in seconds, work on multiple browser tabs, software applications and quickly transfers files. There is a primary slot and secondary expansion storage. Primary slot is M.2 2280 PCIE and secondary slot is M.2 2280 SATA.
- RICH INTERFACE - Nucbox pentium mini computer is equipped with 3* USB 3.2 Gen2 ports, up to 10Gbps/S, 1*USB 2.0, HDMI(4K@60Hz)*2, 3.5mm Audio Jack. Supports WiFi 6, and Gigabit Ethernet RJ45 2.5GbE network connectivity, Bluetooth 5.2. This Mini PC supports multiple device connection and can be used with servers, monitoring equipment, office equipment, displays, projectors, televisions, etc.
- 4K DUAL SCREEN DISPLAY - Mini desktop computer is equipped with upgraded Intel Graphics(max 1000MHz), supports 4K video playback and AV1 decoding, connect the pc with a projector as a home theatre, enjoy a variety of entertainments. Two HDMI 2.0 ports allows you to multi-task efficiently on two 4K@60Hz displays.
- UPGRADED COOLING FAN - The G3 Ultra has upgraded the cooling fan to reduce fan noise and thermals. We are using an upgraded thermal paste as well to help reduce heat on the CPU.
Validate the chosen runtime before relying on it
- Enumerate capabilities: Record code execution, package installation, subprocess or container launch, workspace writes, network destinations, credentials, and tool calls the agent actually needs.
- Define protected assets and tenants: State what must be inaccessible after workload compromise, including host files, other tenants, internal services, and control-plane resources.
- Select the boundary to test: Decide whether shared-kernel isolation is acceptable, whether a userspace application-kernel layer fits, or whether a guest-kernel boundary is required.
- Test the exact workload and configuration: Check compatibility and behavior for required system calls, filesystem and network access, mounts, tool servers, and credentials. Do not infer compatibility or performance from a runtime category alone.
- Measure operational cost in your environment: Compare startup, resource use, provisioning, image maintenance, and cleanup using the versions, hardware, workload, and configuration you plan to deploy. There is no supported universal boot-time, density, memory, throughput, escape-rate, or cost figure for these options.
- Recheck interfaces and defaults on upgrades: Runtime and platform defaults can change. Verify the exact version’s network, credential, mount, service-account, and resource-limit behavior before rollout.
What the available comparisons do—and do not—establish
Google’s gVisor materials explain its architecture and security model; they do not establish that every workload will be compatible or faster or slower than a VM. Docker’s living product documentation describes Docker Sandboxes and its isolation layers, while the Kubernetes SIGs Agent Sandbox threat model frames risks for that project. Those product and project documents are useful for understanding their implementations, but they are not independent comparative benchmarks across all containers, VMs, and microVMs. Treat performance and operational cost as properties to measure for your workload rather than assume from the name of the isolation technology.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

