
Crashes, No Sound, or Screen Glitches?
Random freezes, missing sound and display glitches usually trace back to one bad driver. Find and replace yours safely.Free scan · under a minutePC Slower Than It Used to Be?
A free scan shows the junk files, broken settings and background clutter dragging Windows down - then fixes them in one click.Free scan · Windows 10 & 11Choose a PLC that meets the facility’s process and safety requirements, fits its existing control environment, and has model- and firmware-specific security and support evidence. There is no universally secure PLC for every water or wastewater facility: security also depends on how the controller is configured, connected, maintained, monitored, and recovered.
Use a documented risk and compatibility review to compare candidates. Keep the PLC off the public internet, and build network boundaries and controlled remote access around it rather than expecting the purchase alone to secure the system.
What makes PLC selection a water-sector security decision?
Programmable logic controllers (PLCs) are industrial computers used to monitor and control processes. EPA and CISA guidance notes that water and wastewater systems frequently use PLCs as part of supervisory control and data acquisition (SCADA) systems. A controller may support treatment, pumping, chemical feed, alarms, or other functions whose interruption or unauthorized modification can affect safety, service continuity, water quality, or the ability to operate.
Those consequences vary by facility and by the controller’s role. NIST’s OT security guidance therefore emphasizes requirements particular to operational technology, including performance, reliability, and safety. The right choice starts with understanding the process and its risks, not with a generic “secure PLC” label.
Do these 3 things before closing this tab:
1Fix the driver behind crashes, sound loss and screen glitches2Repair Windows errors before they cause bigger problems3Scan for outdated or missing drivers - takes under a minute#1 Best Overall

- Powerful Processing with 600MHz ARM9 CPU: This device features a 600MHz ARM9 processor, equipped with integrated 8MB DDR2 memory and 16M NAND FLASH memory, achieving a download speed of 38.4KB for efficient performance
- Vivid Display with 4.3 Inch Screen: The product boasts a 4.3inch TFT LCD touch screen, offering a 480x272Px resolution, 260,000 colors, and a brightness of 400cd/m², making it easy to observe statuses with its backlit display
- Main Purpose: Primarily intended for use with various PLCs or intelligent controllers that have communication ports, this device is known for its low power consumption, fast operating speed, and
- Secure Use with High Safety Standards: Designed with safety in mind, the front panel complies with IP65 standards for flat panel installation, while the rear shell meets IP20 requirements, ensuring a secure setup
- Simplified Setup with Easy Installation: Installation is straightforward, thanks to a hole size of 130x80mm and the inclusion of screws and fixing accessories, enabling direct screen mounting
Define requirements before comparing models
Map process impact and availability needs
Document what each candidate controller would do, what depends on it, and the operational consequences of a failure, lost communications, unauthorized logic change, or loss of operator visibility. Identify safety constraints, required availability, recovery objectives, and the facility’s approved maintenance windows. Use this assessment to set minimum requirements before weighing optional features.
Inventory compatibility and dependencies
For the existing system and each proposed replacement, record the controller family and exact model, firmware, I/O, communications, engineering software, HMI/SCADA relationships, field-device dependencies, and vendor or integrator access paths. Include support and patch status. An incompatible controller or engineering tool can create operational and recovery risks even if the replacement has attractive security controls.
Separate minimums from weighted preferences
First exclude candidates that fail process, safety, compatibility, lifecycle, or essential security requirements. Then use a weighted technical review to compare the remaining candidates against the facility’s priorities. Record the evidence and rationale rather than relying on a single overall security score.
Rank #2

- -- PLC Type: Fully compatible with FX1S, 7 Input 5 Relay Output (24V pulse single). Have additional 4 Transistor Output: 2 for high speed pulse 100KHz & 2 for direction, can drive 2 servos or 2 steppers with pulse
- -- PLC software: Use GX Workers 2 or Developer (pls download from GX Workers 2 website, we only have Chinese version), support Command + T Ladder Diagram + SFC for programming
- -- HMI Software: YKBuilder V5.3/7.0 (Pls contact us, we will share it and the video instruction and guidelines). For HMI model: pls choose FE Serial, 280D
- -- Use the same Cable for download program from PC to PLC/HMI: Use the: mini port – USB cable, pls install HMI & PLC’s USB driver first, which we will share.
What security evidence should you request?
Ask the manufacturer and integrator for documentation specific to the exact model and firmware under consideration. Confirm whether a control is built into the PLC, provided by engineering software, or depends on external network equipment. Do not assume that a product label, general security statement, or standards reference proves that a particular configuration has the controls you need.
| Review area | Questions to answer | What to retain in the procurement record |
|---|---|---|
| Authentication and authorization | Who can access management functions? Can users be assigned different privileges? How are credentials managed, and can unauthorized access be restricted? | Model- and firmware-specific documentation, configuration requirements, and any exceptions. |
| Logic and operating-mode changes | How are program or logic changes controlled? Can changes to operating mode be limited to authorized users? What protections apply to device-state modification? | Documented controls, required engineering-tool settings, and the roles permitted to make changes. |
| Unused access methods and services | Can unused authentication methods, features, services, or communications paths be disabled? Could disabling them affect required operations? | Supported hardening options and any known operational dependencies. |
| Monitoring and events | What audit or event information is available, and can it be sent to or reviewed by the facility’s monitoring systems? | Event details, export or integration limits, and monitoring responsibilities. |
| Vulnerability and patch handling | How does the vendor report vulnerabilities and notify customers? Which firmware branches receive security updates, and how are patches released? | Advisory channel, patch process, supported branches, and stated support lifecycle. |
| Operational compatibility | Do security functions work with the required I/O, protocols, engineering software, SCADA/HMI, and field devices? What happens to control or availability when they are enabled? | Written compatibility confirmation, known limitations, and required testing. |
CISA’s PLC security advisory recommends authenticating access before device-state, logic, or program modification; disabling unused authentication methods or features; and limiting operating-mode changes to authorized users. Ask vendors to show how the proposed configuration meets those needs, rather than assuming every PLC implements them in the same way.
Check lifecycle and support before committing
A controller’s security posture changes over its service life. Ask the manufacturer for supported firmware branches, security-advisory history and notification process, patch-release practices, expected support term, end-of-life and end-of-support policies, and the compatibility consequences of updates. Confirm who will receive notices and who is responsible for evaluating and installing patches.
Rank #3

- -- PLC Type: Fully compatible with FX1S, 10 Transistor Input (NPN Type), 7 Relay Output. Have additional 4 Transistor Output: 2 for high speed pulse 100KHz & 2 for direction, can drive 2 servos or 2 steppers with pulse, built-in 2AD(0-10V) and 2DA(0-10V), also 2 NTC10K B3435 probe. Just read the address of AD DA NTC's will ok, 2 high speed input 100KHz X0 X1 to control encoder
- -- PLC software: Use GX Workers 2 or Developer (pls download from GX Workers 2 website, we only have Chinese version), support Command + T Ladder Diagram + SFC for programming
- -- HMI Software: YKBuilder V5.3 and Choose FE serial 380 model in HMI software. (Pls contact us, we will share it and the video instruction and guidelines), very easy to use, just create the buttun and set the address
- -- Use the same Cable for download program from PC to PLC/HMI: Use the: mini port – USB cable, pls install HMI & PLC’s USB driver first, which we will share.
Plan safe maintenance, testing, and rollback procedures with the people responsible for process operations and safety. A patch that cannot be applied safely or a controller that no longer receives support can leave the facility with a difficult operational choice. CISA advises keeping PLCs updated with manufacturer patches and knowing the device’s support and patch status.
Design network boundaries and remote access
Restrict ordinary access paths
Keep PLCs off the public internet. Define which source systems may communicate with each controller, which protocols are required, and which paths are used for management. Use segmentation—such as appropriate zones, firewalls, proxies, or gateways—to limit unnecessary connections between the PLC, enterprise networks, other control assets, and external networks.
Recommended Free Tools
Put controlled infrastructure in front of remote sessions
If remote access is necessary, route it through controlled infrastructure such as a proxy, gateway, firewall, or VPN. Apply authentication, least privilege, monitoring, and time-bounded vendor access where operationally feasible. CISA notes that a VPN or gateway can provide multifactor authentication even when a PLC cannot support it directly. That infrastructure also requires maintenance and secure configuration; it does not remove the need for PLC-level controls.
Rank #4
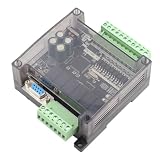
- STRONG ANTI-INTERFERENCE AND SPEED:This programmable logic controller uses industrial-grade 32-bit MCU with strong anti-interference and speed.
- STRONG ANTI-INTERFERENCE AND SPEED:This programmable logic controller uses industrial-grade 32-bit MCU with strong anti-interference and speed.
- chip, on-line download, on-line monitoring, automatic save when power off
- SUPPORT:Program written in ladder logic programming language, supports for GX-Developer, GX-work2, supports HMI connection
- HMI COMMUNICATION:Programming port the port for program upload, download and HMI communication
Agree on the access path and responsibilities with the vendor or integrator before commissioning. Avoid unmanaged direct connections that bypass the facility’s normal approval, monitoring, or change-control process.
Plan backups, recovery, and continuity
Maintain strong backups of controller logic and configuration, protect them from unauthorized changes, and test that they can be restored. Keep the engineering files and recovery instructions accessible to authorized staff. For processes where replacement time would create unacceptable risk, evaluate compatible cold-standby or replacement hardware, including whether it can be obtained and commissioned when needed.
CISA recommends tested PLC logic and configuration backups and planning for cold-standby or replacement hardware of similar models. The facility’s own process and risk assessment should determine the appropriate recovery arrangement.
Best Value

- 4 Relays - 1A, 28VAC, 24VDC
- 4 Digital Inputs - Non-Isolated Opto-Coupler | 4-26VDC
- Supports up to 16 Temperature/Humidity Sensors
- Receive Email/Text Alerts
- Requires 9-28VDC Power Supply (Sold Separately) or POE Switch (POE version only)
Use a documented comparison to make the purchase decision
- Set the requirements: document process, safety, availability, compatibility, and security minimums based on the facility’s risk assessment.
- Shortlist compatible candidates: verify exact model, firmware, I/O, communications, engineering tools, and dependencies with the manufacturer or integrator.
- Collect evidence: obtain written answers for authentication, change control, disablement of unused features, events, vulnerability handling, support lifecycle, and compatibility.
- Review the architecture: specify allowed communications, segmentation boundaries, and controlled remote-access arrangements around the PLC.
- Compare lifecycle and recovery: assess patch support, maintenance and rollback needs, backup restoration, and replacement-hardware plans.
- Record the decision: document evidence, exceptions, residual risk, compatibility decisions, lifecycle terms, weighting, and each party’s configuration and support responsibilities.
- Validate before deployment: test the proposed configuration and changes through the facility’s change-management and safety procedures. CISA recommends impact analysis and risk assessment before defensive changes to control systems.
Use standards as a framework for requirements and evidence, not as a shorthand guarantee. NIST SP 800-82 Rev. 3 discusses the ISA/IEC 62443 series, which includes general, policy and procedure, system, and component categories. If a vendor claims alignment or certification, verify the scope, version, and details with the vendor or issuing organization.
What the water-sector threat example does—and does not—show
CISA reported that actors using the “CyberAv3ngers” persona began targeting and compromising Israeli-made Unitronics Vision Series PLCs and HMIs in November 2023. The advisory includes water and wastewater facilities among affected sectors and recommends device hardening and broader controls. It is a concrete reason to take internet exposure, default credentials, remote programming, and patch and support practices seriously; it does not establish that one PLC brand is categorically unsafe or that such attacks are common across all water facilities.
The sources cited here do not provide a comparable authoritative incident-rate statistic for water-sector PLC compromise or a tested security ranking of PLC brands and models. NIST reported more than 3 million cumulative downloads of SP 800-82 since its initial release in 2006 in 2023; that figure describes downloads of the guidance, not cyber incidents or the number of PLCs deployed.
Which NIST guidance is current?
NIST SP 800-82 Rev. 3 was published on September 28, 2023. As of October 3, 2026, NIST lists SP 800-82 Rev. 4 as an initial public draft published September 21, 2026, with comments due November 30, 2026. The Rev. 4 text is a draft, not a final revision. A draft can inform awareness, but do not describe it as a final or binding requirement.
The Tool Desk
Outbyte PC Repair FREEClear out junk files and repair common Windows errorsFree Scan →Outbyte Driver Updater FREEFix the driver behind crashes, sound loss and screen glitchesFind Drivers →What a PLC purchase cannot decide for you
The sources do not establish a best PLC brand or model for every water facility. They provide a selection and security framework, not a model-by-model product comparison. Exact security features, price, availability, lifecycle status, and compatibility must be verified for the shortlisted model and firmware in the facility’s configuration. A marketplace listing alone is not adequate procurement evidence for a critical facility; confirm authenticity, support, compatibility, and service arrangements with the manufacturer and integrator.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

