
Yes—Check Point reported in January 2019 that a crafted link could let an attacker capture an Epic Games authentication token and access a Fortnite account without the victim entering a password. The victim still had to click the link. Check Point and Epic said the vulnerabilities were fixed; the report is historical, not evidence that the same flaw remains exploitable or that current Epic accounts are compromised.
How the Fortnite account takeover worked
The reported attack abused weaknesses in Epic Games’ web infrastructure and sign-in flow. Rather than stealing a password through a fake login page, it targeted an authentication token issued during single sign-on (SSO). A token can act as proof that a user has signed in, so capturing it could let an attacker act as that account holder without needing the password for the subsequent access.
- The victim clicked a crafted link. Check Point said the link could appear to come from an Epic Games domain, making its origin less obviously suspicious. The click was necessary; this was not an account takeover requiring no user action. (Check Point’s disclosure; technical account of the attack)
- A redirect and vulnerable subdomain were abused. The chain used an unvalidated redirect and a vulnerable, unused Epic subdomain to run injected JavaScript. Check Point described the flaws as part of a linked attack path, not as a password-guessing technique.
- An SSO token was captured. The injected script caused an SSO provider to resend an authentication token, which could then be redirected into an attacker-controlled flow. Check Point named Facebook, Google, and Xbox as examples of providers involved in the reported sign-in scenario; that historical list should not be read as a current, exhaustive list of Epic sign-in options.
- The attacker could use the token to access the account. The victim did not need to type login details into a counterfeit page for this reported chain to capture the token. The exposed credential-like item was the token, not necessarily the password.
Check Point’s technical account explains the redirect, subdomain, and token flow. Its disclosure also describes the potential account impact.
What access could a stolen token provide?
Check Point said an attacker with a stolen token could potentially access account information and in-game contacts, make purchases using payment-card details associated with the account, and view in-game or related conversations. These are capabilities researchers described—not evidence that a particular number of accounts were compromised or that the attack was used against players in the wild.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
#1 Best Overall

- 8-piece game-themed figurines – This figurine set contains 8 game characters, each with a unique weapon, perfectly restoring the classic game image, suitable for collection and display.
- High-quality materials & exquisite details – Made of high-quality environmentally friendly PVC material, it feels smooth, non-toxic and odorless, and the fine carving and coloring process make the characters lifelike.
- Multi-purpose collection ornaments – Suitable for game enthusiasts to collect, birthday gifts, cake decorations, party decorations, desktop ornaments, etc., to add a personalized atmosphere.
- Perfect gift choice – Suitable for relatives, friends, game fans and collectors, suitable for various holiday occasions such as birthdays, Christmas, Children's Day, etc.
- Moderate size, easy to place – The height of the figurine is about 5in, suitable for placing on desks, cabinets, display racks, etc., so that you can enjoy your favorite game characters at any time.
Check Point researcher Oded Vanunu characterized the privacy risk as “a massive invasion of privacy.” The sources do not establish a reliable count of affected users, confirmed account takeovers, or real-world exploitation.
Did Epic fix the vulnerability?
Check Point said it notified Epic and that the vulnerabilities had been fixed. Epic spokesperson Nick Chester told TechCrunch, “We were made aware of the vulnerabilities and they were soon addressed,” and thanked Check Point for reporting them. Neither source gives a precise patch date, a list of affected builds or versions, or a public CVE identifier. (TechCrunch’s January 2019 report)
Rank #2
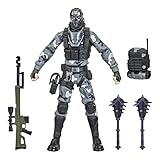
- UNLOCK VICTORY ROYALE SERIES: Unlock the Fortnite universe in the real world with the Victory Royale Series! Upgrade your collection with premium figures based on the Fortnite video game. You never know who’s dropping next, so ready up!
- SHOW YOUR STYLE: What lies behind that sinister smile? This 6-inch Metal Mouth action figure shows the fan-favorite character outfit in game-level detail, taking the on-shelf Battle Royale to the next level!
- EXPAND YOUR LOCKER: Comes with 2 Spiked Mace Harvesting Tools, Catalyst Back Bling, and weapon accessories. Mix and match accessories between figures (Each sold separately. Subject to availability)
- POSE WITH PERSONALITY: Pose out the Metal Mouth figure in an epic battle stance or bust a move in a dance emote with more than 20 points of articulation!
- UPGRADE YOUR COLLECTION: Look for other Fortnite Victory Royale Series figures to level up your collection! (Each sold separately. Subject to availability)
This disclosure dates to January 2019. It does not establish that the reported flaw is currently exploitable, nor does it show that present-day Epic accounts are compromised.
Independent reader supportYour contribution helps us test, update, and keep practical guides available for everyone.What to do if someone accessed your Epic account
- Contact Epic customer support. For login trouble or suspected unauthorized access, use the Epic support page. Epic’s terms say users must notify support if they suspect unauthorized access and must maintain their account security.
- Secure the account. Check the account’s sign-in and security settings, change a reused or exposed password, and use a strong, unique password. Epic spokesperson Nick Chester advised players not to reuse passwords, to use strong passwords, and not to share account information. These are general safeguards, not a guarantee against every kind of account takeover.
- Use the right channel for vulnerability reports. If you have found a security flaw in an Epic service, Epic’s security page directs vulnerability reports to its security email address or HackerOne program. Those channels are for reporting vulnerabilities, not resolving an individual account-access problem.
Check Point also said two-factor authentication could mitigate the reported account-takeover vulnerability. That advice concerns the 2019 incident; it should not be treated as a guarantee against all account-security risks.
Free tools Windows power users keep installed
One-click scans. No signup required.
Quick Recap
Rank #3

- GILDED TROOPER: Board the Battle Bus and drop in with Fortnite Legendary Skull Trooper (Gilded)!
- FORTNITE: 6-inch action figure is inspired by the video game Fortnite
- ARTICULATED: Feature 28 points of articulation to win any Battle Royale
- ACCESSORIES: Comes equipped with Back Bling and Harvesting Tools
- BONUS CODE: Code for virtual item included: Mecha-jolly
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

