
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
Exabeam’s October 1, 2026 announcement adds AI-assisted investigation and AI-activity monitoring to its cloud New-Scale platform and extends generative-AI workflows to on-premises LogRhythm SIEM environments. The company describes Nova AI as gathering context and running follow-up searches while analysts retain judgment over decisions and response. These are vendor-described capabilities, not independently verified effectiveness results.
What is an agentic SOC?
An agentic SOC uses AI agents to carry out bounded security operations tasks—such as collecting context, searching for related activity, and organizing investigations—within workflows overseen by people. It does not necessarily mean that software independently decides whether an incident is real or takes response actions without review. Exabeam frames its approach as human-AI collaboration: agents handle investigative work and analysts apply judgment and control response.


That distinction matters in practice. Automation may speed up repetitive steps, but the quality of an investigation still depends on the available telemetry, the way the system is configured, and the review and response policies a security team puts in place.
What Exabeam announced
Nova AI as a persistent investigator
Exabeam says Nova AI now works across its platform as incidents unfold, gathering context, running secondary searches, and retrieving entity profiles. Related Cases groups connected incidents to help analysts see a wider pattern instead of treating every alert in isolation. The company describes these features in its October 1, 2026 announcement and related product material.
Recommended Free Tools
#1 Best Overall

- APPLIANCE ONLY: Hardware unit sold without a service subscription — security services, firmware updates and support are NOT included and must be purchased separately to activate protection.
- PERFORMANCE: Up to 2.5 Gbps firewall inspection, 1 Gbps threat prevention and 1.2 Gbps IPSec VPN throughput driven by SonicWall's patented Reassembly-Free Deep Packet Inspection (RFDPI) engine.
- CONNECTIVITY: 8x1GbE + 2x1G SFP in a desktop form factor; zero-touch deploy and manage on-box or via cloud Network Security Manager (NSM).
- THREAT PROTECTION: SonicOS 8 delivers intrusion prevention, gateway anti-malware, application control, TLS/SSL decryption, Capture ATP multi-engine sandboxing (RTDMI) and reputation-based content & DNS filtering with an active service subscription.
- BUILT FOR SMALL BUSINESS & BRANCH: Secure SD-WAN, IPSec and SSL VPN plus Zero-Trust Network Access through Cloud Secure Edge keep distributed sites and remote workers protected.
Exabeam reports that its own security operations team averaged approximately 10 minutes per case with Nova AI, compared with five hours for a human analyst. This is the company’s measurement, not an independent benchmark; the announcement does not establish that the same result will apply to other teams, case types, or deployments.
Guided investigation through AI coding assistants
The Exabeam Agentic SOC Plugin for Anthropic Claude Code and OpenAI Codex is described as offering guided workflows for alert triage, case prioritization, and natural-language investigation. Exabeam says it is the first in a planned series of skills for its Agent Skills Marketplace. The announcement does not provide a complete deployment specification, so teams evaluating it should confirm supported versions, access controls, and feature availability with Exabeam.
Visibility into Claude Enterprise activity
For Claude Enterprise, Exabeam says it normalizes prompts, tool calls, and actions into a timeline. Event-time analysis and behavior-based correlation are intended to help identify rogue agents and behavioral drift. The goal is to give security teams visibility into AI use and non-human identities, rather than treating agent activity as an opaque source of events.
Executive reporting and risk-score controls
Executive Digest provides security metrics, while Outcomes Navigator Overrides lets teams tailor risk scoring and separate compliance metrics across business units. These reporting and configuration features may help teams present operational results in terms that fit their programs; their suitability for a particular audit or compliance obligation must be assessed separately.
On-premises LogRhythm SIEM capabilities
For its on-premises LogRhythm SIEM environment, Exabeam describes out-of-the-box generative AI collectors for ChatGPT, Google Gemini, and GitHub Copilot. It also describes a community MCP server that lets teams query, investigate, and triage security data using local generative AI models without moving data outside their environment. The announcement additionally includes an in-place migration from Elasticsearch to OpenSearch and a self-service reporting engine with AI governance and audit-ready compliance reporting.
Exabeam says its Open Agent and AI Security Community had more than 10,000 downloads since launching in June 2026. That is a company-reported community figure, not a measure of product adoption or security outcomes. The announcement also says Exabeam is trusted by more than 3,000 enterprises worldwide; that is a corporate scale claim, not an independently verified customer count.
Rank #3
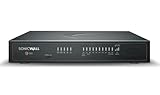
- APPLIANCE ONLY: Hardware unit sold without a service subscription — security services, firmware updates and support are NOT included and must be purchased separately to activate protection.
- PERFORMANCE: Up to 5 Gbps firewall inspection, 2.5 Gbps threat prevention and 2.5 Gbps IPSec VPN throughput driven by SonicWall's patented Reassembly-Free Deep Packet Inspection (RFDPI) engine.
- CONNECTIVITY: 8x1GbE + 2x5G SFP+ + 2x10G SFP in a desktop form factor; zero-touch deploy and manage on-box or via cloud Network Security Manager (NSM).
- THREAT PROTECTION: SonicOS 8 delivers intrusion prevention, gateway anti-malware, application control, TLS/SSL decryption, Capture ATP multi-engine sandboxing (RTDMI) and reputation-based content & DNS filtering with an active service subscription.
- BUILT FOR DISTRIBUTED & HIGH-END SMB: Secure SD-WAN, IPSec and SSL VPN plus Zero-Trust Network Access through Cloud Secure Edge keep distributed sites and remote workers protected.
How the cloud and on-premises approaches differ
Exabeam describes New-Scale as a cloud-native SIEM and analytics platform for threat detection, investigation, and response, with context-aware risk scoring, playbooks, visualizations, cloud collectors, and site collectors for on-premises log and context collection. Its Fusion data sheet describes SIEM, UEBA, Agent Behavior Analytics (ABA), and automated response, with telemetry coverage for Claude, ChatGPT, Gemini, and Microsoft Copilot, as well as bring-your-own-AI and open agent telemetry. It also says the MCP server gives enterprise agents monitored access to case data, risk scores, and investigation summaries.
| Evaluation question | Cloud New-Scale | On-premises LogRhythm SIEM |
|---|---|---|
| Where do data and AI workloads reside? | New-Scale is described as cloud-native; site collectors can collect on-premises logs and context. Confirm the data flows and workload locations for the intended deployment in Exabeam’s documentation. | The announcement describes local-model investigation through a community MCP server without moving security data outside the environment. Confirm the exact data paths and model setup before deployment. |
| What AI activity sources are named? | The Fusion data sheet lists Claude, ChatGPT, Gemini, Microsoft Copilot, bring-your-own-AI, and open agent telemetry. | The announcement names ChatGPT, Google Gemini, and GitHub Copilot collectors. |
| How are investigations supported? | Nova AI gathers context, runs secondary searches, and retrieves entity profiles; Related Cases groups connected incidents. The platform material also describes monitored MCP access to case data, risk scores, and summaries. | A community MCP server supports querying, investigating, and triaging security data using local generative AI models. |
| What should analysts review? | Define which findings, risk decisions, and response actions require analyst approval; Exabeam presents human judgment and response control as its intended operating model. | Set equivalent review and response controls for local-model workflows; the availability of local processing does not by itself establish that actions are safe or compliant. |
| What reporting or audit needs apply? | Executive Digest and Outcomes Navigator Overrides support security metrics, tailored risk scoring, and separated business-unit compliance metrics. | The announcement describes a self-service reporting engine with AI governance and audit-ready compliance reporting. A feature description is not a regulatory certification. |
Neither deployment choice should be treated as automatically compliant. Exabeam’s announcement and product material describe capabilities; they do not establish a legal or regulatory certification. Organizations should map actual data handling, access, retention, oversight, and reporting to their own obligations.
Does AI investigation replace a security analyst?
Exabeam says no: its stated model is to use AI for speed and scale without giving up human judgment, context, or control. Steve Wilson, Exabeam’s Chief AI and Product Officer, said, “The Agentic SOC gives security teams the speed and scale of AI without giving up human judgment, context, or control.” IDC Research Vice President for Security and Trust Michelle Abraham described the shift as changing where analysts’ time and judgment are applied, rather than removing analysts from the process.
Those statements express the intended operating model, not a guarantee about every product configuration. Teams should decide who validates AI-generated findings, which actions can be automated, how exceptions are escalated, and how activity is recorded. The release does not establish independent comparative performance or show that the reported case-time result generalizes beyond Exabeam’s own team.
How to evaluate the announcement for your SOC
- Map the environment. Identify where security logs, AI workloads, and investigation data must reside, including any systems that cannot send data outside your environment.
- Inventory AI activity. List the assistants, agents, tools, and non-human identities your team needs to monitor, then check that the relevant telemetry sources are supported for the specific deployment.
- Define investigation boundaries. Specify which searches and context-gathering tasks an agent may perform, what evidence analysts must see, and which decisions or response actions require approval.
- Check governance and reporting. Compare available logs, timelines, risk scoring, audit trails, and reports with internal policy and external obligations. Do not treat a local-model option or an “audit-ready” feature description as proof of compliance.
- Validate operational claims in your setting. Ask Exabeam for current feature availability, implementation details, and a way to assess outcomes using your own case mix and baseline. The announcement’s case-time comparison is a vendor-reported result, not a neutral benchmark.
What the announcement does—and does not—establish
The October 1, 2026 release documents Exabeam’s announced product direction: persistent AI-assisted investigation on New-Scale, AI-agent visibility, guided workflows through Claude Code and Codex, and local-model investigation options for on-premises LogRhythm SIEM. The supporting New-Scale documentation and Fusion data sheet describe platform and telemetry context.
The available material does not provide independent comparative effectiveness results, complete deployment or pricing specifications, or evidence of regulatory certification. Organizations should confirm details that affect architecture, data handling, availability, and compliance directly with Exabeam before making a deployment decision.
Crashes, No Sound, or Screen Glitches?
Random freezes, missing sound and display glitches usually trace back to one bad driver. Find and replace yours safely.Free scan · under a minutePC Slower Than It Used to Be?
A free scan shows the junk files, broken settings and background clutter dragging Windows down - then fixes them in one click.Free scan · Windows 10 & 11Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

