
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
Treat suspected attacker use of your IT provider’s remote monitoring and management (RMM) tool as a privileged third-party security incident. Coordinate over a trusted channel, isolate affected systems in a controlled way, preserve evidence, and establish with qualified responders which provider accounts, RMM systems, endpoints, and connected services may be exposed. Suspicion is not proof of compromise, but familiar software or a legitimate vendor name does not prove that an action was authorized.
What should you do first?
Start your incident-response plan and appoint an incident lead who can coordinate technical containment, business continuity, and communications. If the provider may be compromised, do not rely on it as the sole source of facts or the only team directing the response. Use an independent, qualified incident-response or digital-forensics team to help assess the situation.
Set up a trusted response channel
Contact your provider and response team using a known-good phone number or another out-of-band method. If email, chat, or identity services could be affected, do not use them as your only coordination channel. Limit response details to people who need them: CISA warns that attackers may monitor communications and react when they realize they have been detected. Confirm who is authorized to approve isolation and business-continuity decisions. See CISA’s #StopRansomware Guide.
Separate suspicion from confirmed compromise
Record what triggered concern, when it was noticed, and which systems or accounts are involved. Until evidence is assessed, describe the event as suspected or confirmed rather than presenting an unverified intrusion as fact. Do not delay containment of systems responders believe are at immediate risk while waiting for certainty.
#1 Best Overall

- Valued Carpenter Pencil Set: You will get 2 pcs solid carpenter pencils with 26 piece 2.8 mm refills, 1 replaceable sharpener, 1 plastic storage box.The complete carpenter pencils combination allows you to finish your work faster and more easily
- Deep Hole Marker Pencil: The deep-hole construction pencils adopts 45mm elongated tip design, which is more convenient to mark in the small hole or in other tight areas that other carpenter markers cannot reach
- Carpenter Pencils with Sharpener: The sharpener is screwed into the top of the work pencil, which won't get lost either. Built-in pencil sharpener that keep the lead with pointed and smooth to Improves line of sight in fine work
- Stronger Solid Lead: This work pencil is matched with a 2.8 mm thick lead , which is much thicker and stronger during the drawing process of construction work, it will not break or damage easily
- Marks on Various Surfaces: 3 colors solid construction pencil can marks on various surfaces,such as metal, plastic, wood, paper etc. Ideals for woodworkers, contractors, craftsmen, builders, merchants and masons
How should you contain access without destroying evidence?
CISA’s response checklist says: “Determine which systems were impacted, and immediately isolate them.” For an affected endpoint, isolation usually means disconnecting it from the network in a controlled way, under the incident lead’s direction. If several systems or subnets appear affected, responders may decide that network-level isolation, including at the switch level, is needed. Coordinate visible actions where feasible: an active attacker may notice them and move laterally or deploy ransomware.
Do not casually power off a computer just because it may be compromised. CISA cautions that shutting down can destroy volatile-memory evidence; when network disconnection is possible, preserve the system for responders to assess. Powering down is a fallback if disconnection cannot be achieved. Apply the same care to relevant cloud snapshots and logs, preserving them where applicable.
Rank #2

- Ergonomically Designed: Work in tight areas with a compact design that gets into tough spots
- Compact and Lightweight: Both tools are designed to fit into difficult to reach spaces. The 1/4" impact driver has a length of 5.55 in. and weighs just 2.8 lbs, while the 1/2" drill/driver measures only 7.5 in. and weighs 3.6 lbs
- Both the DEWALT impact driver and electric drill driver feature integrated LED work lights with a convenient 20-second delay, ensuring enhanced visibility in dimly lit or challenging work areas
- One-Handed Loading - Keep one hand free with a 1/4 in. hex chuck that accepts 1 in. bit tips
- Power drill cordless with 1/2" single sleeve ratcheting chuck provides tight bit gripping strength, making bit changes faster and more secure
| Decision | When it may fit | Key trade-off |
|---|---|---|
| Isolate individual hosts | The suspected impact is limited to identified endpoints or servers. | Can contain known systems while leaving the broader network available; responders still need to check for other affected devices. |
| Isolate a network segment or broader network | Multiple systems or subnets appear affected, or the incident lead believes attacker movement must be stopped more broadly. | May disrupt operations, but can limit access across more systems. Responders may need to isolate at the switch level. |
| Power down a device | Network disconnection is not possible and responders judge shutdown necessary. | Can interrupt attacker activity, but may destroy volatile-memory evidence. |
The appropriate action depends on observed scope and business needs; coordinate it with the incident lead rather than treating any one option as a universal rule.
What evidence and access should you investigate?
RMM software is dual-use: administrators use it for legitimate remote support, but attackers can abuse the same tools. CISA, NSA, and MS-ISAC describe RMM as a potential route into a service provider and, through that provider, customer networks in their joint advisory on malicious use of RMM software. A product name or installed agent alone does not establish whether activity was authorized.
Free tools Windows power users keep installed
One-click scans. No signup required.
Rank #3

- 【Great Compatibility】This Katerk 1/4 inch hex shank bit holder is specifically designed for 1/4 inch hex shank drill bits. It's compatible with most 1/4 fast hex handles, hex sockets, various electric screwdrivers, and handheld screwdrivers. The bit holder makes it a valuable addition for any handyman.
- 【Secure and Safe】Built with a secure backup nut design, each drill bit holder securely locks onto your bits, ensuring they stay firmly in place. Additionally, our bit holder incorporates a high-quality steel ball rolling design that holds up to several kilograms of weight, ensuring your various drill bits don't fall off.
- 【Easy One-Handed Operation】The bit holder for impact driver allows you to change bits single-handedly, simplifying your workflow. Its multi-color design further allows for quick identification of the drill bit you need.
- 【Compact and Convenient】Thanks to its compact size, this 1/4 inch bit holder is easy to carry around. The bit holder allows for easy attachment to various tools, making this a convenient addition to your construction accessories. The Katerk bit holder is cast from high-quality alloy material, promising a long product lifespan. Despite its rugged strength, the bit holder remains lightweight, making it portable.
- 【Cool Christmas Gift For Men Stocking Stuffers】 This screwdriver bit holder, driver bit holder, impact bit holder, can be given as a gift to your loved one, especially for anyone involved in construction or electrical work. It's a must-have for stocking stuffers for men and women, tools gifts for dad, tech gadgets for men, gifts for dad, gifts for him, gifts for husband, gifts for boyfriend, cool gadgets for men, and cool gifts for dad.
Preserve logs and system evidence
- Preserve relevant endpoint, server, identity, network, cloud, and provider-side logs. Ask the provider to preserve its records promptly.
- Have qualified responders determine whether system images or memory captures are appropriate before destructive remediation.
- Retain indicators responders identify, such as suspicious IP addresses, registry entries, and binaries.
- Build a timeline of unusual access and actions, including when they began, which identities were used, and what systems were reached.
CISA’s ransomware response guidance and its SimpleHelp advisory discuss preserving evidence and investigating affected systems. Coordinate with responders before wiping, rebuilding, or otherwise changing a system when feasible.
Map the RMM and identity pathway
- Inventory authorized RMM and remote-access tools, including any portable RMM executables that may not appear in the usual software inventory.
- Review RMM and identity logs for unexpected execution, unusual times, unfamiliar accounts, and tools running from memory.
- Audit administrator and third-party accounts, including publicly reachable RMM accounts, and identify credentials or tokens responders find exposed.
- Map the provider’s access to your endpoints, servers, backups, cloud services, and other systems. Ask the provider to establish any downstream or cross-customer impact with evidence rather than assumption.
CISA’s JCDC RMM Cyber Defense Plan explains the potential cascading risk of RMM exploitation. It quotes a figure of “more than 40% of all private sector payroll in the United States” to describe industries that could be affected by cascading exploitation; that figure is not a measure of RMM incidents or of businesses compromised.
Rank #4

- Long Nib and Deep Hole Marker: Our mechanical carpenter pencil with 45mm nib is designed for easy marking of deep holes or narrow areas. These construction pencils are the great choice for woodworking tools, construction tools, carpenter tools, contractor tools, wood carpentry tools and architect tools
- Extra Refills in 2 Colors for Versatile Marking: The construction mechanical pencil comes with 12 extra 2.8mm refills, including 6 red and 6 black refills. The black refill is suitable for light surfaces, while the red wax is perfect for dark surfaces. Our carpenter mechanical pencil makes sure that you'll have an ample supply for extended use
- Built-in Sharpener: Our construction pencil comes with a built-in sharpener to ensure the mechanical pencil tip is always sharp and ready for use. Never buy an extra pencil sharpener again. A great tool for any woodworker pencil, contractor pencils. The refill can easily be extended or retracted with a simple click of the pencils mechanical, allowing you to work more efficiently and accurately
- Portable Clip Design: Our deep hole construction pencil features a portable clip design, easy to carry and attach to your pocket or tool box, so that you can keep the carpenter pencils mechanical close at hand, making it a convenient tool to have on the go. Great gifts choice for carpenters
- Stronger Pencil Lead: The black refills are made of lead, sturdy and smooth. The red refills are made of wax, clear and light. These marking pencils are much thicker and stronger than normal pencils during the marking process of construction work, suitable for various surfaces, such as glasses, metal, boards, floors, walls, furniture, etc. The written marks can be easily wiped with a wet paper towel when needed
What should you ask your IT provider?
Ask for specific, evidence-backed answers and a timeline. CISA’s guidance on protecting managed service providers and their customers emphasizes monitoring, MFA, incident planning, and provider-customer security expectations (CISA announcement).
- Which RMM product and versions were involved, and which systems were running them?
- Were the RMM console, provider identities, or customer endpoints accessed or changed without authorization? What evidence supports the answer?
- Which accounts, systems, and customer environments may have been reachable from the affected provider systems?
- What containment, investigation, and patch actions have been completed, and when?
- Which logs, indicators, and other evidence can the provider preserve and share, and through what trusted channel?
- How is provider access being restricted while the incident is assessed, and how will access be restored safely?
If the provider itself may be compromised, have an independent incident-response team coordinate technical work. CISA guidance describes outside technical assistance and forensic analysis as response resources; what is available depends on location and circumstances.
Windows Errors? Fix Them Before They Spread
Repair common Windows errors and clear accumulated junk for a smoother, more stable PC - no reinstall needed.Free scan · no reinstallOutdated Drivers Are Slowing You Down
One free scan finds every outdated or missing driver and matches the right update for your exact hardware.Free scan · exact hardware matchBest Value
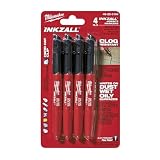
- Milwaukee Ink all Fine Point Marker, Black, 4 Per Pack
- 4 per pack Features Clog Resistant Marker Tip Writes through Dusty, Wet and Oily Surfaces Durable Marker Tip for Writing on Concrete, OSB and Rough Surfaces
- Clog resistant tip writes on dusty, wet and oily surfaces and is optimized for rough surfaces such as OSB, cinderblock and concrete
- Hard hat clip- attaches for easy access
- Quick dry time with reduced smearing and marking
How do product-specific advisories apply?
Use guidance for the exact product and version involved. Do not apply one vendor’s patch instructions to a different RMM tool, or assume an advisory’s version guidance is still current without checking the vendor and official alerts.
N-able N-central alert in Australia
Australia’s ACSC reported targeting of N-able N-central vulnerabilities CVE-2026-18556 and CVE-2026-18577 in an alert first published and updated on 19 August 2026. The alert said patches were released on 1 August 2026 and Hotfix 2 on 6 August, and advised upgrading to Hotfix 2, reviewing internet exposure, monitoring for suspicious activity, contacting a managing provider, and notifying ACSC if suspicious activity was detected. These details concern that alert and product; check the ACSC advisory and current vendor guidance for applicable instructions.
Historical SimpleHelp case
In an advisory dated 12 June 2025, CISA described ransomware actors exploiting unpatched SimpleHelp RMM to compromise customers of a utility billing software provider. It identified SimpleHelp versions 5.5.7 and earlier as affected by several vulnerabilities, including CVE-2024-57727, and linked the exploitation to downstream disruption. This is historical, product-specific information, not current patch guidance for every SimpleHelp deployment; consult the CISA advisory and current vendor notices.
How should you recover and report?
Before restoring affected services, have the incident lead and responders establish what systems and data were affected, whether data was accessed or exfiltrated, whether backups or recovery infrastructure were touched, and whether another access route remains. Follow your incident and communications plans for customer, regulator, insurer, law-enforcement, and government notifications as applicable. Notification duties and deadlines depend on jurisdiction, sector, data, contracts, and other facts; there is no universal deadline that fits every organization.
- Confirm containment and a clean recovery path. Have responders determine that unauthorized access has been removed and that the systems or backups selected for restoration are suitable.
- Remediate affected systems and access. Apply fixes for the exact affected product and version, remove unauthorized access, and rotate credentials or tokens responders find exposed.
- Restore deliberately. Restore from validated backups or other clean recovery sources under the organization’s incident plan, monitoring for signs of renewed access.
- Review provider permissions. Reassess third-party accounts and access scope, applying least privilege and auditing accounts used for external access.
- Reduce future exposure. Strengthen MFA, monitoring and log retention, network segmentation, and contractual security expectations for providers. CISA recommends phishing-resistant MFA for email, VPN, and accounts that access critical systems.
Keep the incident timeline, containment decisions, evidence, provider communications, and recovery approvals together in the incident record so the organization can support its operational and applicable reporting decisions.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

