
Secure software procurement is an accountability decision, not just a technical review: buyers can ask suppliers for evidence of secure development, put tailored security expectations into contracts, and make any accepted residual risk visible to the business owner. This article looks back at the 2025 policy frame from the perspective of 7 October 2026. The EU Cyber Resilience Act’s main requirements were not generally applicable in 2025; its obligations have staged application dates.
Why procurement is a security lever
Organizations influence software security before deployment, when they decide what to buy, what evidence to require, and which risks they are willing to accept. Procurement cannot guarantee that software will be vulnerability-free. It can, however, make supplier practices and buyer decisions more visible and accountable.
CISA’s Software Acquisition Guide for Government Enterprise Consumers, published in July 2024, recommends vetting products with internal security staff and using requests for information (RFIs), requests for proposals (RFPs), and contractual language to influence software purchases. It also emphasizes executive support for purchasing decisions. These are recommendations for enterprise buyers, not a universal legal mandate for every organization.
The accountability principle is straightforward: the people who select a product should not be able to leave its security consequences implicit. When an organization chooses a product despite a material security concern, CISA’s guide calls for documenting the decision and inherent risk and obtaining approval from senior business executives who own enterprise risk.
#1 Best Overall

- Ultra-Compact FIDO2 Security Key - Plug-and-stay or carry on a keychain. This USB-A hardware security key offers portable, always-on protection for desktop and mobile use. (Item Size: 0.75 X 0.74 IN x 0.25 IN)
- USB-A Hardware Key for All Devices - Works with USB-A ports on PC, Mac, Android, and other laptop/notebook device. Enables secure, cross-platform login with FIDO2.0 passkey support.
- FIDO Certified Security Key - Meets FIDO and FIDO2 standards. Works with Google, Microsoft, GitHub, Dropbox, and more. Please check service compatibility before purchase.
- Passwordless Login with Passkey - Supports passkey login via WebAuthn and CTAP2. Enjoy password-free sign-ins where supported. Not all websites or services currently support passkeys.
- Advanced Multi-Factor Authentication - Offers 200 FIDO2 passkey slots and 50 OATH-TOTP slots. Strong, flexible 2FA/MFA support across various apps and authentication platforms.
What buyers can do before signing
1. Define the risk the product introduces
Before a solicitation or purchase, identify the product’s role and deployment model, the data and systems it can access, its dependencies, and the consequences if it is compromised. Bring security reviewers into the decision before award. The review can then focus on the product’s actual use and exposure rather than treating every software purchase as equivalent.
2. Ask suppliers how they develop software securely
NIST’s Software Cybersecurity for Producers and Purchasers was issued under Executive Order 14028, Section 4(e), and is intended to help federal procurement staff know what information to request from software producers about secure development practices. Its purchaser-facing purpose makes it a useful basis for shaping evidence requests; it does not turn every recommendation into a legal obligation for public and private buyers alike.
Rank #2

- FIDO2 & Passkey Ready: Business-ready and FIDO2 L1 certified. This key is supported by major management suites and is ideal for both individual and enterprise deployment. Works seamlessly with Gmail, Facebook, GitHub, Dropbox, Coinbase, and more.
- Universal Connectivity (USB-A ): Features a built-in USB-A connector—simply unfold the key and plug it into your compatible PC or laptop for seamless authentication on the go.
- Dedicated Manager App: Use the Thetis Manager App for the initial hardware PIN setup. Setting the PIN on the device first ensures a smooth registration process. Once the PIN is configured, you can begin registering the key across your favorite FIDO2-compatible online services.
- Ultra-Durable & Portable: Featuring a rotating metal cover, this key is water, crush, and tamper-resistant. It fits easily on a keychain and requires no batteries or network connectivity.
- Check FIDO2 compatibility before purchase - Known limitations: ID Austria is not supported (requires FIDO2 Level 2). Windows Hello login only works with Windows Enterprise editions that support Entra ID, and NFC is NOT supported.
Ask suppliers to describe relevant development practices and provide evidence or attestations suited to the purchase. Treat an attestation as information about a supplier’s practices, not a guarantee that the software contains no vulnerabilities.
3. Make software-component information actionable
A software bill of materials (SBOM) is a formal record of software components and supply-chain relationships. NIST’s SBOM guidance describes requesting machine-readable access in applicable procurement actions and using repositories, contextual information, and vulnerability-detection integration to support monitoring.
Rank #3

- A FIDO security key with PUF technology provides a unique, hardware-rooted trust anchor that resists tampering and cyber attacks, offering stronger security than conventional designs.
- FIDO2 Certified Protection – Enjoy phishing-resistant security with FIDO2 certification, ensuring top-tier account safety across Windows, macOS, Linux, iOS iOS, Android and more.
- Easy to use & Portable – Designed with a compact USB-C interface, Clife key fits easily on your keychain for secure access anywhere. Simply plug in and authenticate with ease.
- Universal Compatibility – Works seamlessly with hundreds of FIDO2/U2F compliant services, including popular cloud, email, and social platforms.
- Backup recommended – To ensure continuous access, register a backup Clife security key as a spare in case your primary key is lost.
An SBOM is useful only if the buyer can do something with it. Clarify what format and access the supplier will provide, how updates will be handled, and how the information can connect to the organization’s software inventory and vulnerability processes. NIST cautions that acquirers unable to ingest, analyze, and act on SBOM data are unlikely to improve their supply-chain risk posture through the data alone.
4. Put risk-appropriate expectations in the contract
CISA identifies contract terms as one way enterprise buyers can influence supplier security. Tailor requirements to the product and its risk—for example, expectations for security-issue reporting, remediation, update support, or delivery of agreed evidence. The guidance supports using contracts as a lever, but does not establish a universal set of model clauses or a checklist that fits every transaction.
Rank #4

- Manufactured by Hirsch Secure, Inc. — formerly Identiv. PHISHING-RESISTANT SECURITY: FIDO Alliance-certified SecureKey stores site-specific cryptographic credentials on-device to help defend against phishing, password theft and replay attacks. PASSWORDLESS + MFA: Supports FIDO2, U2F and WebAuthn for passwordless sign-in, 2FA and MFA. USB-C + NFC: Works with compatible laptops, desktops and mobile devices across Windows, macOS, Linux, ChromeOS, Android and iOS. MULTI-PROTOCOL: Supports HOTP and PIV, with SecureKey Manager for FIDO2 PIN and device management. TAA COMPLIANT: Built for personal, business, enterprise and government use. Register a second key as backup.
5. Document exceptions and name the risk owner
If the business chooses a product with a material security concern, record the decision, the relevant risk, and the approval of the responsible enterprise risk owner. This connects risk acceptance to a named decision-making role instead of leaving security staff to absorb responsibility for a purchase they did not control.
6. Continue monitoring after award
Supplier information gathered during procurement can support ongoing vulnerability alerting and risk monitoring, where the organization has the capability to use it. Treat the award as the beginning of the supplier relationship, not the end of security review; establish how relevant updates and evidence will be used after deployment.
Free tools Windows power users keep installed
One-click scans. No signup required.
Best Value
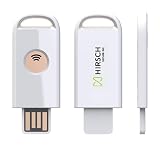
- Manufactured by Hirsch Secure, Inc. — formerly Identiv. PHISHING-RESISTANT SECURITY: FIDO Alliance-certified SecureKey stores site-specific cryptographic credentials on-device to help defend against phishing, password theft and replay attacks. PASSWORDLESS + MFA: Supports FIDO2, U2F and WebAuthn for passwordless sign-in, 2FA and MFA. USB-A + NFC: Works with compatible laptops, desktops and mobile devices across Windows, macOS, Linux, ChromeOS, Android and iOS. MULTI-PROTOCOL: Supports HOTP and PIV, with SecureKey Manager for FIDO2 PIN and device management. TAA COMPLIANT: Built for personal, business, enterprise and government use. Register a second key as backup.
Procurement guidance and product regulation are different mechanisms
Buyer guidance and product regulation can reinforce each other, but they do not impose the same duty on the same parties. NIST and CISA materials inform procurement and enterprise practice; the EU Cyber Resilience Act (CRA) establishes legal requirements for products with digital elements within its scope.
| Question | Procurement guidance | Cyber Resilience Act |
|---|---|---|
| Who is addressed? | NIST’s purchaser guidance is aimed at federal procurement staff; CISA’s acquisition guide addresses government enterprise consumers. Their recommendations can inform other buyers, but do not by themselves create a universal rule for every purchaser. | Economic operators responsible for products with digital elements within the Act’s scope. |
| What is the mechanism? | Buyer requests for secure-development information, SBOM access where appropriate, contract terms, product vetting, and documented risk acceptance. | Horizontal product cybersecurity requirements, including risk-based requirements and, where applicable, secure-by-default configurations and requirements concerning known exploitable vulnerabilities. |
| When does it apply? | Buyers can use the guidance to shape procurement practices; the cited sources do not set one universal effective date for all buyers. | Article 14 reporting obligations apply from 11 September 2026; Chapter IV (Articles 35–51) applies from 11 June 2026; the Act generally applies from 11 December 2027. |
| What should a buyer verify? | Which requirements fit the organization, product, and transaction, and who will own risk acceptance. | Whether the product and economic operator fall within the Act’s scope and which provisions apply on the relevant date. |
The CRA is Regulation (EU) 2024/2847, adopted on 23 October 2024 and published on 20 November 2024. Its staged timetable matters: the general application date is 11 December 2027, not 2025. The earlier dates for Article 14 and Chapter IV should not be confused with general application of the regulation.
Federal acquisition context is transaction-specific
The General Services Administration Acquisition Manual (GSAM) Subpart 504.70 describes federal agency responsibilities in managing cyber supply-chain risk for federal information systems. It is one part of a broader acquisition context, not a complete statement of every software-purchase obligation. For a particular federal transaction, buyers should identify the applicable acquisition provision and contract terms rather than infer a specific duty from the subpart alone.
Likewise, NIST’s federal purchaser guidance should not be described as a statute binding all public and private purchasers. The legal obligations for a particular buyer, supplier, or product depend on the applicable jurisdiction, contract, and rule.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
What accountability should look like
Accountability is strongest when security expectations are set before selection, supplier evidence is matched to the product’s exposure, and the buyer has a practical plan to use information such as an SBOM. It also requires a clear record when the business accepts risk. Procurement can shape supplier incentives and improve the quality of decisions; it cannot remove the need for technical review, ongoing monitoring, or jurisdiction-specific legal analysis.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

