Wfuzz
Wfuzz: A free, flexible HTTP fuzzer for security testing across request elements. Ranked #22 of 25 in Fuzz Testing Software by our editors (6.5/10); pricing: Free plan; best for HTTP request and parameter fuzzing.
At a glance
- Editor score6.5 / 10
- PricingFree plan
- Best forHTTP request and parameter fuzzing
- Free planYes
- Paid fromFree
- Input generation methodsgeneration
- Facts checked20 Sep 2026
Where it wins
- Fuzzes paths, parameters, forms, cookies, headers, and HTTP verbs
- Supports authentication, proxies, payload chaining, recursion, and filtering
- Includes Burp integration and a Python library for automation
Where it doesn't
- No verified coverage guidance for assessing test completeness
- No built-in crash triage for organizing failure results
- No CI/CD support for pipeline-based testing
Our verdict on Wfuzz
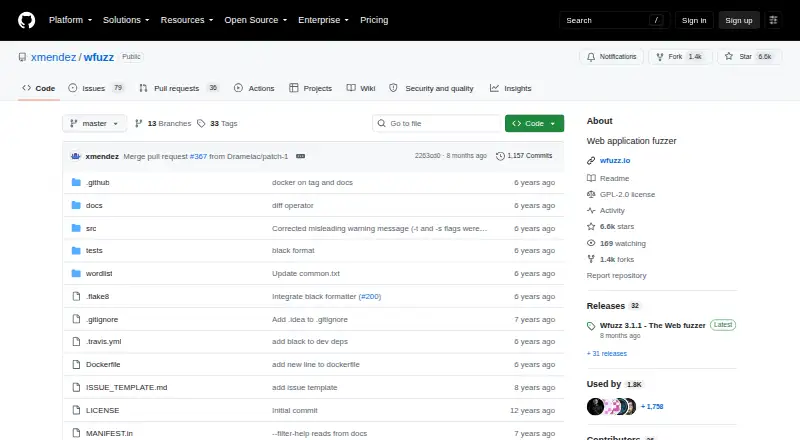
Wfuzz is an open-source web application fuzzer for penetration testers and security developers. It replaces the FUZZ keyword in HTTP requests with payloads, covering URL paths, files, query parameters, POST form data, cookies, custom headers, HTTP verbs, and authentication targets. The local execution model suits security teams and developers who want command-line control over HTTP request generation rather than a hosted testing service.
Its main strength is breadth within HTTP request fuzzing. Wfuzz supports Basic, NTLM, and Digest authentication, HTTP and SOCKS4/SOCKS5 proxies, payload iterators, encoders, chaining, recursive fuzzing, and response filtering. Burp integration connects it with an established web testing workflow, while the Python library supports automation. Installation is available through pip, source installation, or Docker, and the project is distributed under GPLv2. These options make it adaptable to different local environments, although the product remains focused on users comfortable configuring payloads and interpreting HTTP responses.
Wfuzz is a strong fit when the priority is flexible, low-cost fuzzing of web request components. It is less suitable for teams that need verified coverage guidance, built-in crash triage, or CI/CD support as part of a broader application security process. Choose it for targeted HTTP fuzzing and Python-based automation; consider an alternative when workflow orchestration, result management, or pipeline integration matters as much as request flexibility.
Your product? Our editors can test Wfuzz in depth and publish a review, labelled as paid · from $149/mo →
Wfuzz pricing
Wfuzz fact sheet
| Free plan | Yes |
|---|---|
| Paid from | Free |
| Input generation methods | generation |
| Target types | HTTP URLs, paths, files, query parameters, POST data, cookies, headers, HTTP verbs, authentication |
| Coverage guidance | Not verified |
| Crash triage | Not verified |
| Execution mode | Local |
| Supported languages | Python |
| CI/CD support | Not verified |
| Deployment | Self-hosted |
| Platforms | Windows, macOS |
| Support | Docs |
| Built for | Solo, Small business (editorial estimate) |
| Integrations | 1 integrations: Burp |
| Pricing | Free plan |
| Website | github.com |
| Facts checked | 20 Sep 2026 |
Wfuzz integrations
Wfuzz lists 1 integrations on its own site.
- Burp
Alternatives to Wfuzz
- MayhemMayhem brings broad hybrid fuzz testing, triage, and regression coverage to CI workflows.9.4
- OSS-FuzzA cloud-based continuous fuzzing service for qualifying open-source projects.9.2
- ClusterFuzzA broad, self-managed fuzzing platform for continuous security and stability testing.8.9


Used Wfuzz? Be the first to review it
The editor score above is our own research. What this page doesn't have yet is a reader's view — what you used Wfuzz for, what worked and what didn't. No stars are seeded and no review is paid for; an editor reads every one before it appears.
Write a reviewTwo minutes · verified accounts only · read by an editor before it appears
Featured on iTechGuides
Wfuzz is listed in our Fuzz Testing Software directory. Add the badge to your site — it links back to this page.
<a href="https://www.itechguides.com/products/wfuzz/"><img src="https://www.itechguides.com/best/badge/wfuzz.svg" alt="Featured on iTechGuides" width="230" height="46"></a>
Reviewed by iTechGuides Editors · Editorial team · Updated Oct 2026
Advertiser disclosure: iTechGuides is reader-supported. Vendors can pay for top positions in our rankings and for a place on other products' pages, and we may earn a commission when you click some links. Bought places stand at the number bought; this page and our disclosure say so. Paying vendors may get a fuller, more detailed review from our editors, and that review can change their score. How we rank.
Last updated · How we research and update