
ServiceNow Vulnerability Response
ServiceNow Vulnerability Response: A ServiceNow-centered workflow for importing, prioritizing, assigning, and tracking vulnerabilities. Ranked #6 of 32 in Vulnerability Management Software by our editors (8.8/10); pricing: Pricing on request; best for serviceNow-centric vulnerability programs.
At a glance
- Editor score8.8 / 10
- PricingPricing on request
- Best forServiceNow-centric vulnerability programs
- Remediation trackingYes
- Facts checked19 Sep 2026
Where it wins
- Correlates application vulnerability findings with CMDB records.
- Automates assignment and links remediation work to change requests.
- Supports imports across DAST, SAST, IAST, SCA, SBOM, and penetration testing.
Where it doesn't
- Relies on imports from supported scanners and external systems.
- Requires a separate subscription for Vulnerability Response.
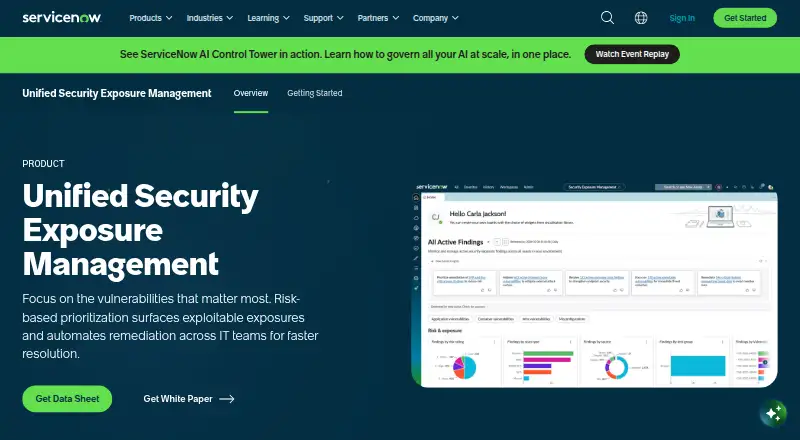
- ServiceNow identifies Unified Security Exposure Management as its next evolution.
Our verdict on ServiceNow Vulnerability Response
ServiceNow Vulnerability Response is an enterprise vulnerability-management application for security and IT teams. It brings findings from supported third-party scanners and other systems into ServiceNow, correlates application vulnerability data with CMDB records, and supports prioritization through configurable risk calculators and severity mapping. Its focus is the operational path from finding to remediation, making it most relevant to organizations that already run vulnerability work through ServiceNow rather than teams seeking a standalone scanning product.
The workflow covers assignment, remediation targets, status tracking, and closure. Rules can automatically assign vulnerable items and remediation tasks, and remediation work can be linked to change requests. Teams can track vulnerability items through open, investigation, resolution, and closure states. Integrations include Qualys, Tenable, Rapid7 InsightVM, the NIST National Vulnerability Database, CWE, Microsoft Security Response Center, and Red Hat. The application-security workflows also support imported DAST, SAST, IAST, SCA, SBOM, and penetration-testing data, with web-application vulnerability support through DAST and Tenable Web Application Scanning integrations. This breadth makes the product a fit for coordinating findings from multiple sources, while its described approach depends on scanner data being imported.
Vulnerability Response is available by separate subscription, and the vendor's pricing model is contact sales. ServiceNow documentation describes Unified Security Exposure Management as the next evolution of Vulnerability Response. Buyers should assess that product direction alongside the subscription and their existing ServiceNow environment. Choose Vulnerability Response if CMDB correlation, configurable prioritization, assignment, and remediation tracking inside ServiceNow are central requirements. Teams primarily looking for vulnerability discovery through built-in scanning, or seeking a workflow independent of ServiceNow, should consider alternatives that better match those needs.
Your product? Our editors can test ServiceNow Vulnerability Response in depth and publish a review, labelled as paid · from $149/mo →
ServiceNow Vulnerability Response pricing
ServiceNow Vulnerability Response fact sheet
| Free plan | Not verified |
|---|---|
| Paid from | Not verified |
| Deployment model | Cloud |
| Authenticated scanning | Not verified |
| Agent-based assessment | Not verified |
| Web application scanning | Yes |
| Remediation tracking | Yes |
| Risk prioritization | Standard |
| Deployment | Cloud |
| Platforms | Web |
| Integrations | 7 integrations: Qualys, Tenable, Rapid7 InsightVM, NIST National Vulnerability Database, CWE, Microsoft Security Response Center … |
| Pricing | Pricing on request |
| Website | servicenow.com |
| Facts checked | 19 Sep 2026 |
ServiceNow Vulnerability Response integrations
ServiceNow Vulnerability Response lists 7 integrations on its own site.
- Qualys
- Tenable
- Rapid7 InsightVM
- NIST National Vulnerability Database
- CWE
- Microsoft Security Response Center
- Red Hat
Alternatives to ServiceNow Vulnerability Response
- Rapid7 InsightVMHybrid vulnerability scanning with risk prioritization and remediation tracking.9.3
- ManageEngine Vulnerability Manager PlusA broad endpoint and network vulnerability program with a free entry tier.9.2
- Qualys Vulnerability ManagementContinuous assessment and risk-based prioritization, with a high published entry price.9.1


See all ServiceNow Vulnerability Response alternatives →
ServiceNow Vulnerability Response vs the competition
- ServiceNow Vulnerability Response vs Rapid7 InsightVM
- ServiceNow Vulnerability Response vs ManageEngine Vulnerability Manager Plus
- ServiceNow Vulnerability Response vs Qualys Vulnerability Management
- ServiceNow Vulnerability Response vs Tenable Security Center
- ServiceNow Vulnerability Response vs Ivanti Neurons for Risk-Based Vulnerability Management
- ServiceNow Vulnerability Response vs Zscaler Unified Vulnerability Management
Compare ServiceNow Vulnerability Response with any tool side by side →
Used ServiceNow Vulnerability Response? Be the first to review it
The editor score above is our own research. What this page doesn't have yet is a reader's view — what you used ServiceNow Vulnerability Response for, what worked and what didn't. No stars are seeded and no review is paid for; an editor reads every one before it appears.
Write a reviewTwo minutes · verified accounts only · read by an editor before it appears
Featured on iTechGuides
ServiceNow Vulnerability Response is listed in our Vulnerability Management Software directory. Add the badge to your site — it links back to this page.
<a href="https://www.itechguides.com/products/servicenow-vulnerability-response/"><img src="https://www.itechguides.com/best/badge/servicenow-vulnerability-response.svg" alt="Featured on iTechGuides" width="230" height="46"></a>
Reviewed by iTechGuides Editors · Editorial team · Updated Oct 2026
Advertiser disclosure: iTechGuides is reader-supported. Vendors can pay for top positions in our rankings and for a place on other products' pages, and we may earn a commission when you click some links. Bought places stand at the number bought; this page and our disclosure say so. Paying vendors may get a fuller, more detailed review from our editors, and that review can change their score. How we rank.
Last updated · How we research and update