scan4secrets
scan4secrets: A feature-rich self-hosted scanner for secrets, web exposure, and DAST workflows. Ranked #17 of 24 in Secrets Scanning Software by our editors (7.6/10); pricing: Free plan; best for self-hosted secrets plus web and DAST scanning.
At a glance
- Editor score7.6 / 10
- PricingFree plan
- Best forSelf-hosted secrets plus web and DAST scanning
- Free planYes
- Paid fromFree
- CI/CD scanningYes
- Facts checked22 Sep 2026
Where it wins
- Scans source trees, HTTP responses, live web apps, and CI logs
- Combines crawling, DAST, credential verification, and authenticated scanning
- Supports custom rules, CI severity gates, and seven report formats
Where it doesn't
- Self-hosted deployment requires teams to manage the scanning environment
- Command-line workflows may not suit teams seeking a visual-first product
- Optional vulnerability and misconfiguration scanning broadens scope beyond secrets
Our verdict on scan4secrets
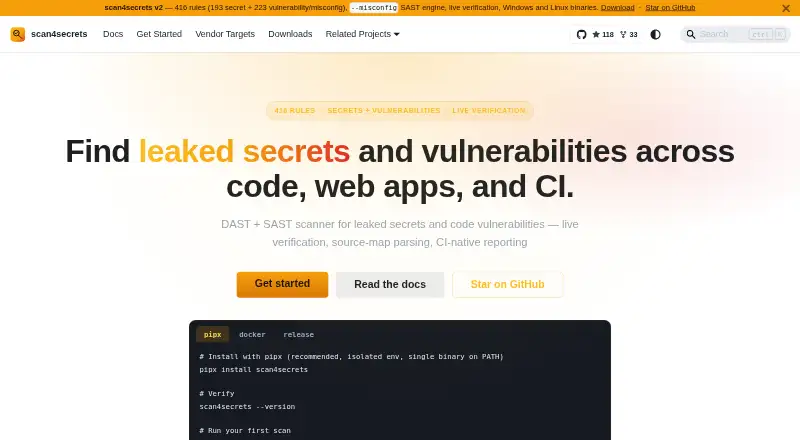
scan4secrets is an open-source command-line security scanner for developers and security teams that need to find exposed credentials across source trees, live web applications, HTTP responses, and CI logs. It is designed for self-hosted use and supports GitHub, GitLab, and Bitbucket workflows, with pre-commit scanning and CI fail gates based on finding severity. The scope extends beyond static secret detection to live crawling, DAST, credential verification against vendor APIs, and authenticated scans using cookies, headers, and proxies.
Its main strength is breadth within a security scanning workflow. Teams can enable optional vulnerability and misconfiguration scanning, define custom YAML detection rules and allowlists, and export results as SARIF, JSON, JSONL, CSV, HTML, Excel, or PDF. Integration options include GitHub Code Scanning, GitLab Security Dashboard, Sonar, Defect Dojo, Splunk, Datadog, and Microsoft Sentinel. Installation is available from source, through pipx, or as a Docker image, giving technical teams several ways to run the scanner in their own environment.
The trade-off is operational ownership: the verified platform model is self-hosted, and the command-line design places deployment and workflow management with the adopting team. scan4secrets is a strong fit for organizations that want open-source control, custom detection logic, web and DAST coverage, and flexible reporting in CI/CD. Teams looking for a managed service or a primarily visual security platform should consider whether a self-hosted command-line tool matches their operating model.
Your product? Our editors can test scan4secrets in depth and publish a review, labelled as paid · from $149/mo →
scan4secrets pricing
scan4secrets fact sheet
| Free plan | Yes |
|---|---|
| Paid from | Free |
| Supported VCS | GitHub, GitLab, Bitbucket |
| CI/CD scanning | Yes |
| Pre-commit scanning | Yes |
| Pull-request scanning | Yes |
| Push protection | Not verified |
| Custom detection rules | Yes |
| Repository limit | Not verified |
| Deployment | Self-hosted |
| Platforms | Windows, Linux |
| Support | Docs |
| Built for | Solo, Small business, Mid-market (editorial estimate) |
| Integrations | 7 integrations: GitHub Actions, GitLab CI, Jenkins, Docker, pre-commit, GitHub Code Scanning … |
| Pricing | Free plan |
| Website | scan4secrets.m14r41.in |
| Facts checked | 22 Sep 2026 |
scan4secrets integrations
scan4secrets lists 7 integrations on its own site.
- GitHub Actions
- GitLab CI
- Jenkins
- Docker
- pre-commit
- GitHub Code Scanning
- GitLab Security Dashboard
Alternatives to scan4secrets
- GitGuardianBroad secrets scanning with developer workflow controls, remediation, and enterprise deployment options.9.3
- TruffleHogDeep secret detection and credential verification for development and security teams.9.2
- KingfisherA broad, free scanner for exposed credentials across code, cloud, containers, and developer platforms.9.1

See all scan4secrets alternatives →
Used scan4secrets? Be the first to review it
The editor score above is our own research. What this page doesn't have yet is a reader's view — what you used scan4secrets for, what worked and what didn't. No stars are seeded and no review is paid for; an editor reads every one before it appears.
Write a reviewTwo minutes · verified accounts only · read by an editor before it appears
Featured on iTechGuides
scan4secrets is listed in our Secrets Scanning Software directory. Add the badge to your site — it links back to this page.
<a href="https://www.itechguides.com/products/scan4secrets/"><img src="https://www.itechguides.com/best/badge/scan4secrets.svg" alt="Featured on iTechGuides" width="230" height="46"></a>
Reviewed by iTechGuides Editors · Editorial team · Updated Oct 2026
Advertiser disclosure: iTechGuides is reader-supported. Vendors can pay for top positions in our rankings and for a place on other products' pages, and we may earn a commission when you click some links. Bought places stand at the number bought; this page and our disclosure say so. Paying vendors may get a fuller, more detailed review from our editors, and that review can change their score. How we rank.
Last updated · How we research and update