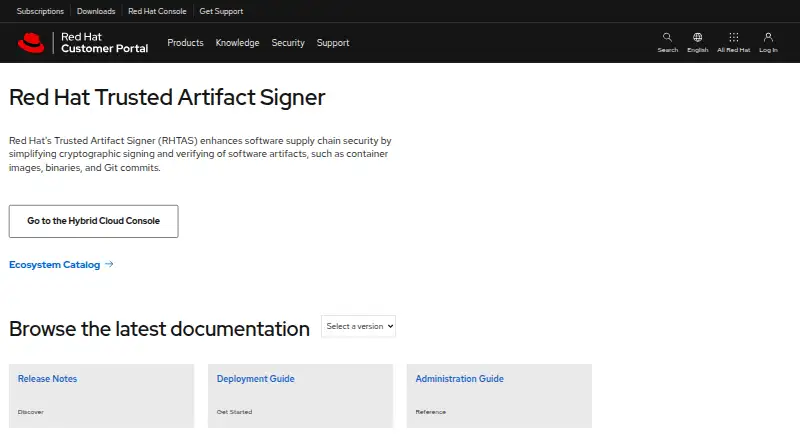
Red Hat Trusted Artifact Signer
Red Hat Trusted Artifact Signer: A broad code-signing platform for Red Hat environments and software supply chains. Ranked #27 of 28 in Code Signing Software by our editors (6.2/10); pricing: Pricing on request; best for red Hat environments signing build artifacts.
At a glance
- Editor score6.2 / 10
- PricingPricing on request
- Best forRed Hat environments signing build artifacts
- Supported targetscontainer images, binaries, documents, source-code commits, software bills of materials, build artifacts, AI/ML models
- Founded1993 · Raleigh, North Carolina, United States
- Facts checked20 Sep 2026
Where it wins
- Signs containers, binaries, commits, SBOMs, documents, and AI/ML models
- Short-lived certificates, transparency logging, timestamping, and provenance support
- Integrates with Podman, Quay, Ansible, and Red Hat security platforms
Where it doesn't
- Pricing uses a contact-sales subscription model
- Deployment is focused on Linux, OpenShift, and Red Hat Enterprise Linux
- Its broad feature set may exceed the needs of basic file signing
Our verdict on Red Hat Trusted Artifact Signer
Red Hat Trusted Artifact Signer is a self-managed enterprise deployment of Sigstore for signing and verifying software supply-chain artifacts. It is designed for organizations working with Red Hat Enterprise Linux or Red Hat OpenShift Container Platform, particularly teams that need to secure build and release workflows across containers, binaries, documents, source-code commits, software bills of materials, and AI/ML models. Command-line clients including cosign, gitsign, and rekor-cli support signing and verification activities within those workflows.
The main strength is breadth across the software supply chain. Trusted Artifact Signer issues short-lived certificates through a certificate authority, records signing events in a transparency log, and includes a timestamp authority. It also supports policy-based verification of container-image attestations and signatures, while AI/ML model signing and verification can be incorporated into CI/CD pipelines. These capabilities make it suited to teams that need more than a certificate for a single binary or installer. Integrations with Podman, Quay, Ansible, Red Hat Advanced Cluster Security, StoneSoup/HACBS, and Red Hat Trusted Content further align it with Red Hat-centered development and delivery environments.
Pricing follows a contact-sales subscription model rather than a self-serve plan structure, so buyers should evaluate the offering with Red Hat based on their deployment and supply-chain requirements. The self-managed approach also places it closer to platform infrastructure than to a lightweight signing utility: teams should be prepared to operate it within Linux or Red Hat environments and connect it to their existing CI/CD and verification policies. Choose Trusted Artifact Signer when artifact coverage, short-lived certificates, transparency records, and policy enforcement are central requirements. For a narrow signing workflow with minimal infrastructure involvement, a simpler alternative may be a better fit.
Your product? Our editors can test Red Hat Trusted Artifact Signer in depth and publish a review, labelled as paid · from $149/mo →
Red Hat Trusted Artifact Signer pricing
Red Hat Trusted Artifact Signer fact sheet
| Free plan | Not verified |
|---|---|
| Paid from | Not verified |
| Supported targets | container images, binaries, documents, source-code commits, software bills of materials, build artifacts, AI/ML models |
| Certificate provided | Yes |
| Cloud signing | Not verified |
| HSM key protection | Not verified |
| Trusted timestamping | Yes |
| CI/CD signing | Yes |
| Approval workflows | Not verified |
| Deployment | Self-hosted |
| Platforms | Linux |
| Support | Tickets, Live chat, Docs |
| Built for | Mid-market, Enterprise (editorial estimate) |
| Integrations | 6 integrations: Podman, Quay, Ansible, Red Hat Advanced Cluster Security, StoneSoup/HACBS, Red Hat Trusted Content |
| Pricing | Pricing on request |
| Website | access.redhat.com |
| Facts checked | 20 Sep 2026 |
Red Hat Trusted Artifact Signer integrations
Red Hat Trusted Artifact Signer lists 6 integrations on its own site.
- Podman
- Quay
- Ansible
- Red Hat Advanced Cluster Security
- StoneSoup/HACBS
- Red Hat Trusted Content
Alternatives to Red Hat Trusted Artifact Signer
- SignPathGoverned signing for teams shipping software across diverse artifact formats.9.4
- DigiCert Software Trust ManagerEnterprise signing governance for artifacts, approvals, keys, and release pipelines.9.2
- SignServerA flexible open-source signing server with enterprise controls for production deployments.9.0
See all Red Hat Trusted Artifact Signer alternatives →
Used Red Hat Trusted Artifact Signer? Be the first to review it
The editor score above is our own research. What this page doesn't have yet is a reader's view — what you used Red Hat Trusted Artifact Signer for, what worked and what didn't. No stars are seeded and no review is paid for; an editor reads every one before it appears.
Write a reviewTwo minutes · verified accounts only · read by an editor before it appears
Featured on iTechGuides
Red Hat Trusted Artifact Signer is listed in our Code Signing Software directory. Add the badge to your site — it links back to this page.
<a href="https://www.itechguides.com/products/red-hat-trusted-artifact-signer/"><img src="https://www.itechguides.com/best/badge/red-hat-trusted-artifact-signer.svg" alt="Featured on iTechGuides" width="230" height="46"></a>
Reviewed by iTechGuides Editors · Editorial team · Updated Sep 2026
Advertiser disclosure: iTechGuides is reader-supported. Vendors can pay for top positions in our rankings and for a place on other products' pages, and we may earn a commission when you click some links. Bought places stand at the number bought; this page and our disclosure say so. Paying vendors may get a fuller, more detailed review from our editors, and that review can change their score. How we rank.
Last updated · How we research and update