OWASP Nettacker
OWASP Nettacker: A broad open-source scanner for authorized reconnaissance and CVE checks. Ranked #27 of 34 in Vulnerability Scanning Software by our editors (6.2/10); pricing: Open source; best for open-source reconnaissance and CVE checks.
At a glance
- Editor score6.2 / 10
- PricingOpen source
- Best forOpen-source reconnaissance and CVE checks
- Paid fromFree
- Deployment modelOn_premises
- Facts checked20 Sep 2026
Where it wins
- Scans ports, services, subdomains, directories, and CVEs
- Supports IPv4, domains, HTTP/HTTPS URLs, and authenticated scanning
- Generates HTML, JSON, CSV, and text reports with comparison tools
Where it doesn't
- Does not provide verified continuous scanning
- Lacks compliance coverage
- Does not list integrations beyond its REST API and web interface
Our verdict on OWASP Nettacker
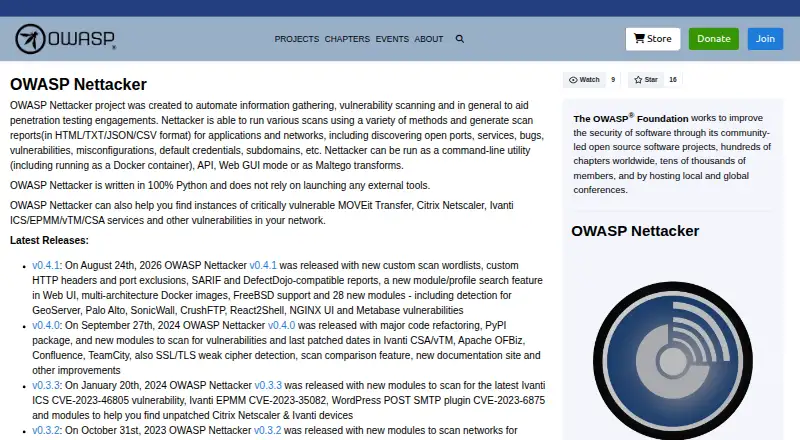
OWASP Nettacker is an open-source Python framework for automated penetration testing, information gathering, and vulnerability assessment. It is designed for security professionals, penetration testers, and ethical hackers conducting authorized internal or external assessments. The project scans IPv4 addresses, IPv4 ranges, IPv4 CIDR blocks, domains, and HTTP or HTTPS URLs, with deployment options spanning web, Windows, macOS, Linux, API, and self-hosted environments.
Its main strength is breadth within reconnaissance and vulnerability assessment. Nettacker combines port and service scanning, subdomain enumeration, vulnerability and CVE checks, directory and backup discovery, credential and brute-force modules, and support for multiple protocols. Multithreaded scanning, custom HTTP headers, and proxy support add control for varied assessment scenarios. Authenticated scanning is supported, while the command-line, REST API, and web interfaces give teams several ways to operate the framework. Reporting is available in HTML, JSON, CSV, and text formats, with scan history and report comparison for reviewing results over time.
Nettacker is a strong fit when an organization needs an open-source tool for targeted, authorized assessments and wants modular checks with flexible output. Its scope is less suitable for teams seeking verified continuous monitoring, compliance-focused coverage, or a broader integration ecosystem. Organizations prioritizing those capabilities should consider a vulnerability scanning product built around continuous scanning, compliance workflows, and native integrations. Teams comfortable operating an on-premises framework and interpreting reconnaissance and CVE findings will find Nettacker’s feature range more relevant than buyers looking for a managed, continuously operated service.
Your product? Our editors can test OWASP Nettacker in depth and publish a review, labelled as paid · from $149/mo →
OWASP Nettacker pricing
OWASP Nettacker fact sheet
| Free plan | Not verified |
|---|---|
| Paid from | Free |
| Deployment model | On_premises |
| Supported targets | IPv4 addresses, IPv4 ranges, IPv4 CIDR blocks, domains, HTTP and HTTPS URLs |
| Authenticated scanning | Yes |
| Continuous scanning | Not verified |
| Asset limit | Not verified |
| Compliance frameworks | Not verified |
| Deployment | Self-hosted |
| Platforms | Web, Windows, macOS, Linux |
| Support | Community, Docs |
| Built for | Solo, Small business, Mid-market, Enterprise (editorial estimate) |
| Pricing | Open source |
| Website | owasp.github.io |
| Facts checked | 20 Sep 2026 |
Alternatives to OWASP Nettacker
- VorninBroad cloud vulnerability coverage with a free tier for up to five assets.9.4
- IntruderBroad vulnerability coverage with a free tier and expansion paths for larger environments.9.3
- OpenVASA broad open-source scanner with authenticated testing, continuous scans and compliance features.9.0


See all OWASP Nettacker alternatives →
Used OWASP Nettacker? Be the first to review it
The editor score above is our own research. What this page doesn't have yet is a reader's view — what you used OWASP Nettacker for, what worked and what didn't. No stars are seeded and no review is paid for; an editor reads every one before it appears.
Write a reviewTwo minutes · verified accounts only · read by an editor before it appears
Featured on iTechGuides
OWASP Nettacker is listed in our Vulnerability Scanning Software directory. Add the badge to your site — it links back to this page.
<a href="https://www.itechguides.com/products/owasp-nettacker/"><img src="https://www.itechguides.com/best/badge/owasp-nettacker.svg" alt="Featured on iTechGuides" width="230" height="46"></a>
Reviewed by iTechGuides Editors · Editorial team · Updated Oct 2026
Advertiser disclosure: iTechGuides is reader-supported. Vendors can pay for top positions in our rankings and for a place on other products' pages, and we may earn a commission when you click some links. Bought places stand at the number bought; this page and our disclosure say so. Paying vendors may get a fuller, more detailed review from our editors, and that review can change their score. How we rank.
Last updated · How we research and update