OpenText Fortify Software Composition Analysis
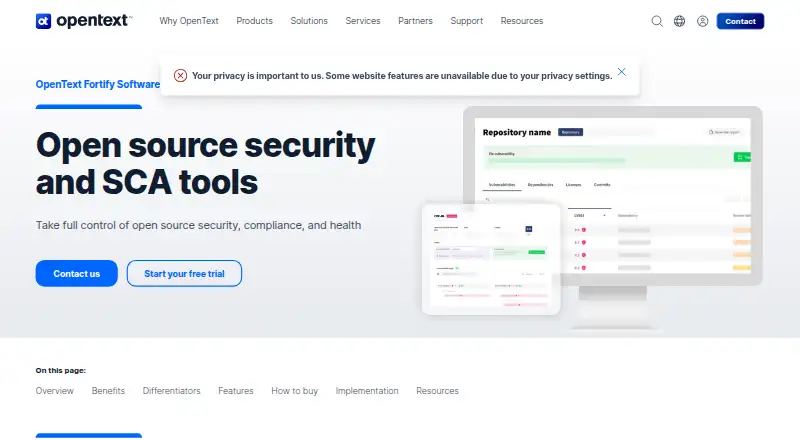
OpenText Fortify Software Composition Analysis: A broad SCA platform with free access, enterprise controls, and sales-led pricing. Ranked #12 of 65 in Software Composition Analysis Software by our editors (8.1/10); pricing: Free plan; best for organizations wanting established vendor backing.
At a glance
- Editor score8.1 / 10
- PricingFree plan
- Best forOrganizations wanting established vendor backing
- Free planYes
- SBOM generationYes
- Facts checked22 Sep 2026
Where it wins
- Scans vulnerabilities, licenses, dependencies, and project health
- Supports CycloneDX and SPDX SBOM workflows
- Adds reachability analysis, policy automation, and CI/CD scanning
Where it doesn't
- Premium and Enterprise pricing requires contact with sales
- Reachability analysis is limited to supported ecosystems
- Automated dependency fixes apply only to supported languages
Our verdict on OpenText Fortify Software Composition Analysis
OpenText Fortify Software Composition Analysis is a cloud-deployed platform for development, security, and compliance teams managing open-source and third-party dependency risk. It scans for vulnerabilities, license compliance issues, and dependency health concerns across ecosystems including Java, JavaScript, Python, .NET, Go, Ruby, Rust, PHP, Swift, and Linux package managers. Web, Windows, macOS, Linux, command-line, and API access support different operating environments and workflows.
The published plans separate core scanning from reporting and enterprise controls. The Free tier includes vulnerability management, license management, and project health. Premium adds vulnerability reports, license reports, API access, and chat and email support. Enterprise adds SBOM export, enterprise SSO, reachability analysis, and increased computation. The pricing model is contact sales, so organizations should expect a sales-led evaluation when comparing paid tiers. A free plan provides an entry point for teams that need foundational dependency and license oversight.
Its strongest fit is for organizations that need broad software supply-chain coverage within existing delivery processes. Integrations include CI/CD pipelines, CLI, API, webhooks, and Docker, while policy automation and project evaluation can support governance workflows. CycloneDX and SPDX support, dependency health metrics, pull requests for supported dependency fixes, and reachability analysis extend the platform beyond basic vulnerability lists. Teams should choose it when ecosystem breadth, SBOM workflows, and established OpenText vendor backing matter. Smaller teams seeking simple, transparent paid pricing or narrowly focused dependency scanning may prefer a more specialized option.
OpenText Fortify Software Composition Analysis pricing
All 3 OpenText Fortify Software Composition Analysis plans and prices →
OpenText Fortify Software Composition Analysis fact sheet
| Free plan | Yes |
|---|---|
| Paid from | Not verified |
| Supported ecosystems | C# / NuGet / Paket; Go / Go Modules / Go Dep / Bazel; Java and Kotlin / Gradle / Maven / Bazel; JavaScript / NPM / Yarn / Bower; Objective-C / CocoaPods; PHP / Composer; Python / Pip / Pipenv / UV / Poetry; Ruby / RubyGems; Rust / Cargo; Swift / CocoaPods; Scala / SBT |
| SBOM generation | Yes |
| Reachability analysis | Yes |
| Pull request scanning | Yes |
| Monitored projects | Not verified |
| Deployment options | Cloud |
| Deployment | Cloud |
| Platforms | Web, Windows, macOS, Linux |
| Compliance & security | SOC 2, ISO 27001, SSO/SAML |
| Support | Email, Live chat, Docs · 24/7 |
| Built for | Small business, Mid-market, Enterprise (editorial estimate) |
| Integrations | 7 integrations: GitHub, GitLab, Bitbucket, Azure DevOps, Jenkins, CircleCI … |
| Pricing | Free plan (source) |
| Website | opentext.com |
| Facts checked | 22 Sep 2026 |
OpenText Fortify Software Composition Analysis integrations
OpenText Fortify Software Composition Analysis lists 7 integrations on its own site.
- GitHub
- GitLab
- Bitbucket
- Azure DevOps
- Jenkins
- CircleCI
- API
Alternatives to OpenText Fortify Software Composition Analysis
- Snyk Open SourceBroad SCA coverage with reachability, SBOMs, pull-request scanning, and monitoring.9.4
- FOSSAA mature SCA platform covering dependencies, SBOMs, containers, licenses, and policy controls.9.3
- Safeguard SCAA budget-conscious SCA platform with reachability analysis, SBOMs, and remediation workflows.9.1

See all OpenText Fortify Software Composition Analysis alternatives →
Used OpenText Fortify Software Composition Analysis? Be the first to review it
The editor score above is our own research. What this page doesn't have yet is a reader's view — what you used OpenText Fortify Software Composition Analysis for, what worked and what didn't. No stars are seeded and no review is paid for; an editor reads every one before it appears.
Write a reviewTwo minutes · verified accounts only · read by an editor before it appears
Featured on iTechGuides
OpenText Fortify Software Composition Analysis is listed in our Software Composition Analysis Software directory. Add the badge to your site — it links back to this page.
<a href="https://www.itechguides.com/products/opentext-fortify-software-composition-analysis/"><img src="https://www.itechguides.com/best/badge/opentext-fortify-software-composition-analysis.svg" alt="Featured on iTechGuides" width="230" height="46"></a>
Reviewed by iTechGuides Editors · Editorial team · Updated Oct 2026
Advertiser disclosure: iTechGuides is reader-supported. Vendors can pay for top positions in our rankings and for a place on other products' pages, and we may earn a commission when you click some links. Bought places stand at the number bought; this page and our disclosure say so. Paying vendors may get a fuller, more detailed review from our editors, and that review can change their score. How we rank.
Last updated · How we research and update