OpenText Endpoint Forensics & Response
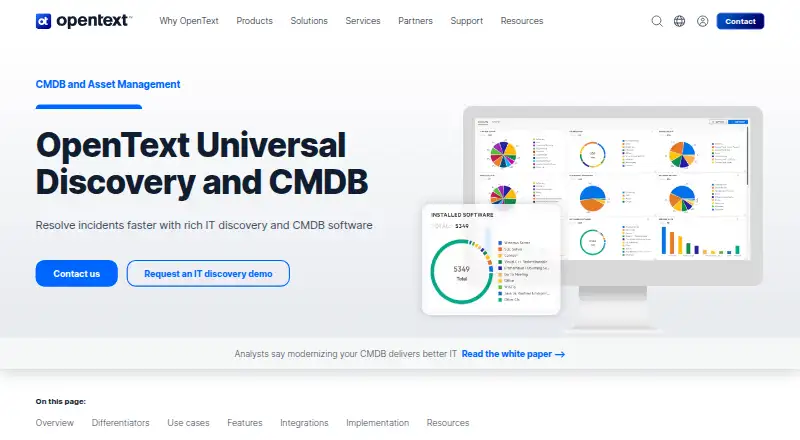
OpenText Endpoint Forensics & Response: A Windows-focused platform for endpoint triage, containment, remediation, and forensic investigation. Ranked #15 of 21 in Incident Response Software by our editors (7.6/10); pricing: Pricing on request; best for windows endpoint containment and forensics.
At a glance
- Editor score7.6 / 10
- PricingPricing on request
- Best forWindows endpoint containment and forensics
- Founded1991 · Waterloo, Ontario, Canada
- Facts checked20 Sep 2026
Where it wins
- Combines endpoint triage, isolation, remediation, and forensic investigation
- Supports YARA-based IoC scanning and near-real-time endpoint visibility
- Provides audit-ready reporting and chain-of-custody tracking
Where it doesn't
- Platform coverage is limited to web and Windows
- Designed as an add-on to an existing Endpoint Investigator deployment
- Pricing requires contact with sales and uses per-node term licensing
Our verdict on OpenText Endpoint Forensics & Response
OpenText Endpoint Forensics & Response combines digital forensic investigation with near-real-time incident response for enterprise SOC teams, government agencies, regulated industries, internal investigators, and incident responders. It supports endpoint evidence collection, artifact-driven triage, threat analysis, endpoint isolation, file and process remediation, registry search and live remediation, and YARA-based IoC scanning. Its focus is suited to teams investigating ransomware, insider threats, APTs, endpoint incidents, and compliance-driven audits.
Licensing is offered in one-year, two-year, and three-year terms, with term licenses using a per-node licensing model. The product is positioned as an add-on to an existing Endpoint Investigator deployment, which makes the surrounding OpenText environment an important purchase consideration. Integration options include SIEM, SOAR, and threat intelligence tools, while API access supports connection with broader operational workflows. Evidence tracking and audit logs also fit teams that need documented investigative activity.
The strongest differentiator is the combination of response actions and investigation depth. Teams can isolate endpoints, remediate files and processes, search and remediate the registry, scan with YARA, and maintain near-real-time visibility through five-minute check-ins. Deep-dive forensic investigation, audit-ready reporting, and chain-of-custody tracking extend the product beyond basic containment. Choose it when Windows endpoint forensics and evidence handling are priorities. Organizations needing broader verified platform coverage or a standalone deployment may prefer an alternative.
Questions about OpenText Endpoint Forensics & Response
What does OpenText Endpoint Forensics & Response run on? Web and Windows. It runs in the cloud and as a desktop app.
What does OpenText Endpoint Forensics & Response integrate with? 3 integrations: SIEM, SOAR and threat intelligence tools.
Who is OpenText Endpoint Forensics & Response built for? Enterprises (our editorial estimate).
Your product? Our editors can test OpenText Endpoint Forensics & Response in depth and publish a review, labelled as paid · from $149/mo →
OpenText Endpoint Forensics & Response pricing
All 3 OpenText Endpoint Forensics & Response plans and prices →
OpenText Endpoint Forensics & Response fact sheet
| Free plan | Not verified |
|---|---|
| Paid from | Not verified |
| Case management | Not verified |
| Evidence tracking | Yes |
| Responder collaboration | Not verified |
| On-call scheduling | Not verified |
| Audit log | Yes |
| API access | Yes |
| Deployment options | Not verified |
| Deployment | Cloud, Desktop |
| Platforms | Web, Windows |
| Built for | Enterprise (editorial estimate) |
| Integrations | 3 integrations: SIEM, SOAR, threat intelligence tools |
| Pricing | Pricing on request (source) |
| Website | opentext.com |
| Facts checked | 20 Sep 2026 |
OpenText Endpoint Forensics & Response integrations
OpenText Endpoint Forensics & Response lists 3 integrations on its own site.
- SIEM
- SOAR
- threat intelligence tools
Alternatives to OpenText Endpoint Forensics & Response
- TheHiveA broad incident response workspace covering triage, investigation, evidence, and reporting.9.4
- DFIR-IRISA focused case-management platform for open-source incident response teams.9.2
- LimaCharlieAffordable endpoint-centric response with telemetry, cases, containment, and automation.9.0
See all OpenText Endpoint Forensics & Response alternatives →
Used OpenText Endpoint Forensics & Response? Be the first to review it
The editor score above is our own research. What this page doesn't have yet is a reader's view — what you used OpenText Endpoint Forensics & Response for, what worked and what didn't. No stars are seeded and no review is paid for; an editor reads every one before it appears.
Write a reviewTwo minutes · verified accounts only · read by an editor before it appears
Featured on iTechGuides
OpenText Endpoint Forensics & Response is listed in our Incident Response Software directory. Add the badge to your site — it links back to this page.
<a href="https://www.itechguides.com/products/opentext-endpoint-forensics-response/"><img src="https://www.itechguides.com/best/badge/opentext-endpoint-forensics-response.svg" alt="Featured on iTechGuides" width="230" height="46"></a>
Reviewed by iTechGuides Editors · Editorial team · Updated Nov 2026
Advertiser disclosure: iTechGuides is reader-supported. Vendors can pay for top positions in our rankings and for a place on other products' pages, and we may earn a commission when you click some links. Bought places stand at the number bought; this page and our disclosure say so. Paying vendors may get a fuller, more detailed review from our editors, and that review can change their score. How we rank.
Last updated · How we research and update