Grype
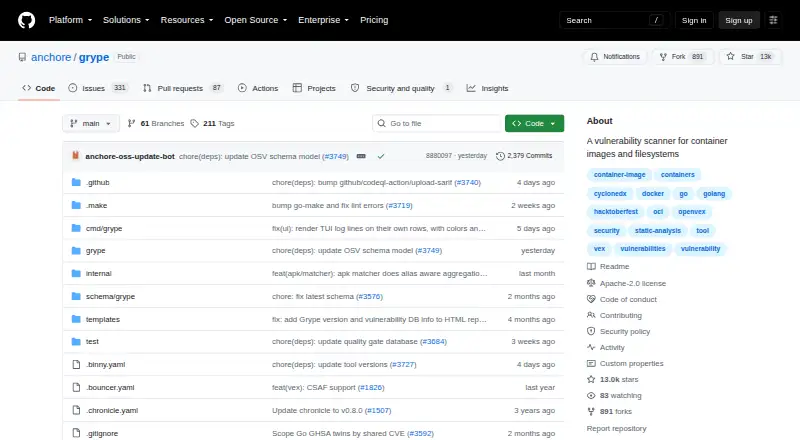
Grype: A focused, free scanner for container, filesystem, package, and SBOM vulnerabilities. Ranked #50 of 65 in Software Composition Analysis Software by our editors (5.3/10); pricing: Free plan; best for teams focused on container and SBOM vulnerability scans.
At a glance
- Editor score5.3 / 10
- PricingFree plan
- Best forTeams focused on container and SBOM vulnerability scans
- Free planYes
- Paid fromFree
- SBOM generationYes
- Founded2016 · Santa Barbara, California, United States
- Facts checked22 Sep 2026
Where it wins
- Scans containers, filesystems, archives, packages, and SBOMs
- Supports Syft JSON, SPDX, CycloneDX, and OpenVEX workflows
- Matches vulnerabilities across operating-system and language ecosystems
Where it doesn't
- No reachability analysis
- No pull-request scanning
- No license analysis or broader policy workflow
Our verdict on Grype
Grype is an open-source command-line vulnerability scanner from Anchore for teams that need focused analysis of container images, filesystems, packages, and software bills of materials. It runs locally on Linux, macOS, and Windows, and can be deployed in a self-hosted environment. Direct target scans use Syft internally to generate an SBOM before matching packages against known vulnerabilities, while existing Syft JSON, SPDX, and CycloneDX files can also be scanned.
Its strongest fit is breadth across scan inputs and package ecosystems without a paid plan structure. Grype can inspect images from Docker, Podman, Containerd, registries, and OCI sources, along with directories, files, archives, and individual packages identified through PURL or CPE identifiers. Matching strategies include ecosystem-specific, distribution-specific, and CPE approaches. Supported ecosystems include Alpine APK, Debian DPKG, RPM, Python, JavaScript, Java, Go, PHP, .NET, Dart, Ruby, Rust, Swift, GitHub Actions, and Bitnami. JSON, table, and other formatted outputs support different reporting workflows, and OpenVEX can filter or augment vulnerability results.
The trade-off is a narrow SCA scope. Grype does not provide reachability analysis, pull-request scanning, license analysis, or a broader policy workflow, so it is less suitable for teams seeking application-level prioritization or governance features in one platform. It is a sensible choice for engineers who want a free, open-source scanner that can run across container and SBOM workflows, especially where self-hosted operation and command-line output fit existing processes. Teams needing deeper dependency analysis, pull-request controls, or license governance should choose a broader SCA product instead.
Your product? Our editors can test Grype in depth and publish a review, labelled as paid · from $149/mo →
Grype pricing
Grype fact sheet
| Free plan | Yes |
|---|---|
| Paid from | Free |
| Supported ecosystems | Alpine, Debian, Ubuntu, RHEL, SUSE, Amazon Linux, PyPI, npm, Maven, Go modules, Composer, NuGet, Pub, RubyGems, Crates, Swift, GitHub Actions, Bitnami, Conda, WordPress plugins |
| SBOM generation | Yes |
| Reachability analysis | Not verified |
| Pull request scanning | Not verified |
| Monitored projects | Not verified |
| Deployment options | Self_hosted |
| Deployment | Self-hosted |
| Platforms | Windows, macOS, Linux |
| Support | Community, Docs |
| Built for | Small business, Mid-market, Enterprise (editorial estimate) |
| Integrations | 1 integrations: Syft |
| Pricing | Free plan |
| Website | github.com |
| Facts checked | 22 Sep 2026 |
Grype integrations
Grype lists 1 integrations on its own site.
- Syft
Alternatives to Grype
- Snyk Open SourceBroad SCA coverage with reachability, SBOMs, pull-request scanning, and monitoring.9.4
- FOSSAA mature SCA platform covering dependencies, SBOMs, containers, licenses, and policy controls.9.3
- Safeguard SCAA budget-conscious SCA platform with reachability analysis, SBOMs, and remediation workflows.9.1

Also Ranked In
Grype is ranked in 5 of our directories.
Used Grype? Be the first to review it
The editor score above is our own research. What this page doesn't have yet is a reader's view — what you used Grype for, what worked and what didn't. No stars are seeded and no review is paid for; an editor reads every one before it appears.
Write a reviewTwo minutes · verified accounts only · read by an editor before it appears
Featured on iTechGuides
Grype is listed in our Software Composition Analysis Software directory. Add the badge to your site — it links back to this page.
<a href="https://www.itechguides.com/products/grype/"><img src="https://www.itechguides.com/best/badge/grype.svg" alt="Featured on iTechGuides" width="230" height="46"></a>
Reviewed by iTechGuides Editors · Editorial team · Updated Oct 2026
Advertiser disclosure: iTechGuides is reader-supported. Vendors can pay for top positions in our rankings and for a place on other products' pages, and we may earn a commission when you click some links. Bought places stand at the number bought; this page and our disclosure say so. Paying vendors may get a fuller, more detailed review from our editors, and that review can change their score. How we rank.
Last updated · How we research and update