GraphQL-Cop
GraphQL-Cop: A focused GraphQL checker for common exposure, overload, CSRF, and debug-mode risks. Ranked #27 of 27 in API Security Testing Software by our editors (6.4/10); pricing: Free plan; best for focused GraphQL security checks.
At a glance
- Editor score6.4 / 10
- PricingFree plan
- Best forFocused GraphQL security checks
- Free planYes
- Paid fromFree
- Authorization testingNo
- Facts checked20 Sep 2026
Where it wins
- Covers introspection, GraphiQL, field suggestions, tracing, and debug modes
- Tests alias, batch-query, directive, and field-duplication overloading
- Supports Docker, custom headers, proxies, JSON, and cURL reproduction commands
Where it doesn't
- Does not test authentication, authorization, or input validation
- Focused on GraphQL rather than broader API discovery and testing
- Runs as a self-hosted command-line utility rather than a hosted service
Our verdict on GraphQL-Cop
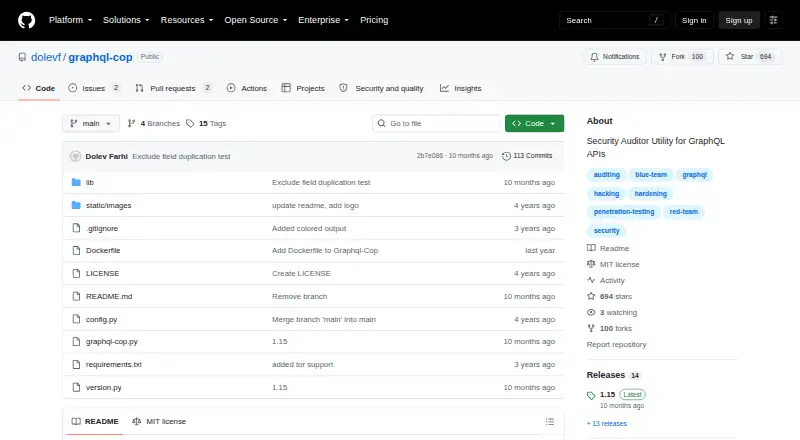
GraphQL-Cop is an open-source Python command-line utility for auditing GraphQL APIs against common security weaknesses. It is designed for security testing and CI/CD checks, with support for Windows, macOS, Linux, and Docker execution. Its scope suits teams that need focused GraphQL checks rather than a broad API security testing platform. The utility examines introspection exposure, GraphiQL and GraphQL UI availability, field suggestions, tracing, debug mode, and several request patterns associated with CSRF. It also supports endpoint wordlists and test exclusions.
The strongest part of GraphQL-Cop is its focused coverage of GraphQL-specific exposure and overload risks. Checks include alias overloading, field duplication, batch queries, directive overloading, GET-query and GET-mutation CSRF patterns, and denial-of-service conditions. Custom request headers and proxy support help fit the utility into security workflows, while JSON output and cURL reproduction commands provide structured results and reproducible request examples. These capabilities make it a practical fit for targeted command-line assessment and pipeline checks where GraphQL behavior is the primary concern.
Its narrow scope is also the main boundary for buyers. GraphQL-Cop does not cover API discovery, authentication testing, authorization testing, input validation testing, or business logic testing, so it should not be treated as a complete API security program. Teams needing those areas should choose a broader API testing product alongside or instead of it. Choose GraphQL-Cop when an open-source, self-hosted utility for focused GraphQL checks matches the workflow; avoid relying on it alone when coverage must extend beyond GraphQL or beyond the specific weakness categories it tests.
Your product? Our editors can test GraphQL-Cop in depth and publish a review, labelled as paid · from $149/mo →
GraphQL-Cop pricing
GraphQL-Cop fact sheet
| Free plan | Yes |
|---|---|
| Paid from | Free |
| API discovery | No |
| Authentication testing | No |
| Authorization testing | No |
| Input-validation testing | No |
| Business-logic testing | No |
| Deployment | Self-hosted |
| API formats | GraphQL |
| Deployment | Self-hosted |
| Platforms | Windows, macOS, Linux |
| Support | Docs |
| Built for | Solo, Small business, Mid-market (editorial estimate) |
| Pricing | Free plan |
| Website | github.com |
| Facts checked | 20 Sep 2026 |
Alternatives to GraphQL-Cop
- Levo.aiA full-lifecycle API security platform spanning discovery, testing, and runtime monitoring.9.4
- PyntBroad API security coverage with flexible integrations and a free entry plan.9.3
- Akto API Security PlatformA broad API security platform with a free plan and hybrid deployment options.9.2


See all GraphQL-Cop alternatives →
Used GraphQL-Cop? Be the first to review it
The editor score above is our own research. What this page doesn't have yet is a reader's view — what you used GraphQL-Cop for, what worked and what didn't. No stars are seeded and no review is paid for; an editor reads every one before it appears.
Write a reviewTwo minutes · verified accounts only · read by an editor before it appears
Featured on iTechGuides
GraphQL-Cop is listed in our API Security Testing Software directory. Add the badge to your site — it links back to this page.
<a href="https://www.itechguides.com/products/graphql-cop/"><img src="https://www.itechguides.com/best/badge/graphql-cop.svg" alt="Featured on iTechGuides" width="230" height="46"></a>
Reviewed by iTechGuides Editors · Editorial team · Updated Oct 2026
Advertiser disclosure: iTechGuides is reader-supported. Vendors can pay for top positions in our rankings and for a place on other products' pages, and we may earn a commission when you click some links. Bought places stand at the number bought; this page and our disclosure say so. Paying vendors may get a fuller, more detailed review from our editors, and that review can change their score. How we rank.
Last updated · How we research and update