Dockle
Dockle: A focused CI auditor for Docker image practices, not a vulnerability scanner. Ranked #23 of 26 in Container Security Software by our editors (6.6/10); pricing: Free plan; best for CI teams auditing Docker image best practices.
At a glance
- Editor score6.6 / 10
- PricingFree plan
- Best forCI teams auditing Docker image best practices
- Free planYes
- Paid fromNone
- Image scanningYes
- Facts checked22 Sep 2026
Where it wins
- Checks CIS Docker Benchmark and Docker best-practice requirements
- Outputs JSON or SARIF with configurable CI exit codes
- Supports registries, tar archives, and sensitive file detection
Where it doesn't
- Does not scan for vulnerability patches
- Does not provide runtime protection or Kubernetes security
- Does not generate SBOMs or enforce admission control
Our verdict on Dockle
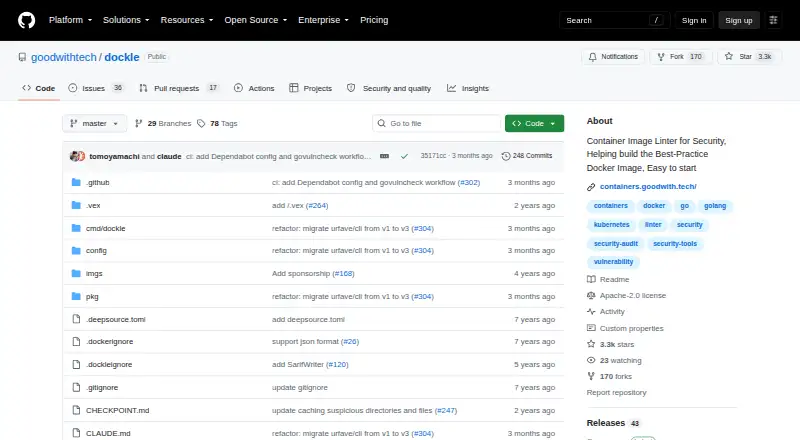
Dockle is an open-source command-line tool for auditing built container images against Docker best practices and CIS Docker Benchmark checkpoints. It suits CI teams that want repeatable checks on image configuration, sensitive files, and environment variables before deployment. Dockle runs locally, in a Docker container, or within continuous-integration workflows, and it analyzes images rather than Dockerfiles. Its self-hosted deployment model also fits teams that prefer to run checks within their own development and delivery environments.
Dockle’s strongest fit is automated policy checking in CI. Results can be emitted as list, JSON, or SARIF output, while configurable exit codes and alert levels help teams decide which findings should fail a pipeline. Ignore, accept, and reject rules provide control over individual checks and files. Integrations include GitHub Actions, Travis CI, CircleCI, Jenkins, and GitLab CI. For image access, Dockle supports Docker Hub, Amazon ECR, Google Container Registry, basic-authenticated self-hosted registries, and images saved as tar archives. These capabilities make it practical for teams auditing image hygiene across several delivery paths.
The scope is deliberately narrower than a full container security platform. Dockle does not support vulnerability patch scanning, runtime protection, Kubernetes security, admission control, or SBOM generation. The published guidance recommends Trivy for vulnerability scanning, so teams needing both configuration auditing and vulnerability analysis should pair Dockle with another tool or choose an alternative that covers both areas. Pick Dockle when CIS-oriented image checks and CI outputs are the priority; look elsewhere when runtime defenses, Kubernetes controls, or software inventory are core requirements.
Dockle pricing
Dockle fact sheet
| Free plan | Yes |
|---|---|
| Paid from | None |
| Image scanning | Yes |
| Runtime protection | Not verified |
| Kubernetes security | Not verified |
| Registry scanning | Not verified |
| Admission control | Not verified |
| SBOM generation | Not verified |
| Deployment model | Self_hosted |
| Deployment | Self-hosted |
| Platforms | Windows, macOS, Linux |
| Support | Docs |
| Built for | Solo, Small business, Mid-market (editorial estimate) |
| Integrations | 4 integrations: Docker Hub, Amazon ECR, Google Container Registry, Self-hosted registries |
| Pricing | Free plan |
| Website | github.com |
| Facts checked | 22 Sep 2026 |
Dockle integrations
Dockle lists 4 integrations on its own site.
- Docker Hub
- Amazon ECR
- Google Container Registry
- Self-hosted registries
Alternatives to Dockle
- Trend Vision One Container SecurityBroad container security coverage with transparent usage-based pricing.9.2
- Qualys Container SecurityBroad container coverage with a free visibility tier and sales-led paid access.9.1
- Wiz Container and Kubernetes SecurityA broad cloud security platform for prioritizing container and Kubernetes risks.9.0


Used Dockle? Be the first to review it
The editor score above is our own research. What this page doesn't have yet is a reader's view — what you used Dockle for, what worked and what didn't. No stars are seeded and no review is paid for; an editor reads every one before it appears.
Write a reviewTwo minutes · verified accounts only · read by an editor before it appears
Featured on iTechGuides
Dockle is listed in our Container Security Software directory. Add the badge to your site — it links back to this page.
<a href="https://www.itechguides.com/products/dockle/"><img src="https://www.itechguides.com/best/badge/dockle.svg" alt="Featured on iTechGuides" width="230" height="46"></a>
Reviewed by iTechGuides Editors · Editorial team · Updated Oct 2026
Advertiser disclosure: iTechGuides is reader-supported. We may earn a commission when you click some links. How we rank.
Last updated · How we research and update