Cosign
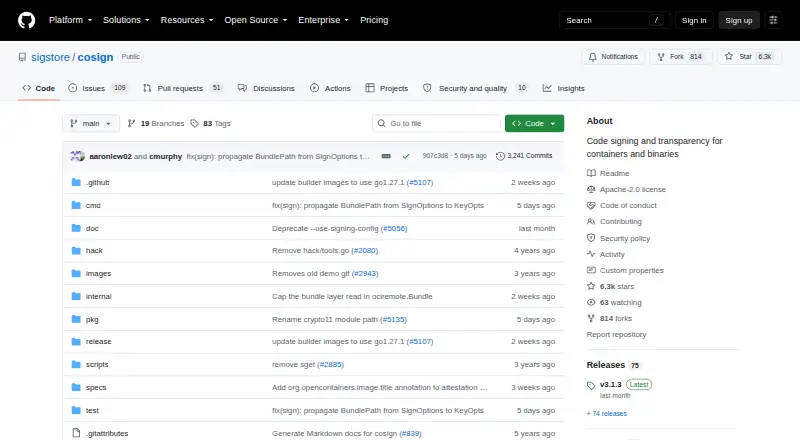
Cosign: A flexible open-source choice for signing cloud-native artifacts across modern registries and CI pipelines. Ranked #9 of 28 in Code Signing Software by our editors (8.3/10); pricing: Open source; best for container and cloud-native artifact signing.
At a glance
- Editor score8.3 / 10
- PricingOpen source
- Best forContainer and cloud-native artifact signing
- Paid fromFree
- Supported targetsOCI container images, blobs, binaries, scripts, configuration files, SBOMs, WASM modules, Tekton bundles, eBPF modules, and In-Toto attestations
- Facts checked20 Sep 2026
Where it wins
- Keyless signing with Fulcio certificates and Rekor transparency logging
- Supports containers, binaries, blobs, SBOMs, attestations, and more
- Works with hardware tokens, KMS providers, and bring-your-own PKI
Where it doesn't
- Platform coverage is limited to Linux and macOS
- Command-line workflows may require technical implementation effort
- No vendor-priced hosted plans or commercial tiers
Our verdict on Cosign
Cosign is an open-source command-line tool from the Sigstore project for signing and verifying OCI container images and a broad range of software artifacts. It is suited to development and security teams that need artifact integrity across container registries, automated build pipelines, and cloud-native delivery workflows. Supported targets include blobs, binaries, scripts, configuration files, SBOMs, WASM modules, Tekton bundles, eBPF modules, and In-Toto attestations.
Its ecosystem fit is a major strength. Cosign supports AWS Elastic Container Registry, GCP Artifact Registry, Docker Hub, Azure Container Registry, JFrog Artifactory, GitLab Container Registry, GitHub Container Registry, Harbor, and Cloudsmith. GitHub Actions and GitLab CI installation options support automated signing in build pipelines. Keyless signing uses Fulcio certificates and Rekor transparency logging, while encrypted key pairs, hardware tokens, KMS providers, and bring-your-own PKI support provide alternatives for different trust models. Offline verification using Sigstore bundles is also available.
Cosign stands out for the breadth of artifact types and signing approaches it covers without a vendor-priced hosted tier. Its feature set includes certificate-based signing, timestamping, HSM key protection, CI/CD signing, container registry storage, and attestations. That makes it a strong fit for teams building a software supply-chain signing workflow around containers and related artifacts. It is less suitable for organizations seeking a hosted interface, commercial plan tiers, or broader platform coverage beyond Linux and macOS. Teams that prefer a managed service or a non-command-line-first experience should consider an alternative.
Your product? Our editors can test Cosign in depth and publish a review, labelled as paid · from $149/mo →
Cosign pricing
Cosign fact sheet
| Free plan | Not verified |
|---|---|
| Paid from | Free |
| Supported targets | OCI container images, blobs, binaries, scripts, configuration files, SBOMs, WASM modules, Tekton bundles, eBPF modules, and In-Toto attestations |
| Certificate provided | Yes |
| Cloud signing | Not verified |
| HSM key protection | Yes |
| Trusted timestamping | Yes |
| CI/CD signing | Yes |
| Approval workflows | Not verified |
| Deployment | Self-hosted |
| Platforms | Linux, macOS |
| Support | Docs, Community |
| Built for | Solo, Small business, Mid-market, Enterprise (editorial estimate) |
| Integrations | 11 integrations: AWS Elastic Container Registry, GCP Artifact Registry, Docker Hub, Azure Container Registry, JFrog Artifactory, GitLab Container Registry … |
| Pricing | Open source |
| Website | github.com |
| Facts checked | 20 Sep 2026 |
Cosign integrations
Cosign lists 11 integrations on its own site.
- AWS Elastic Container Registry
- GCP Artifact Registry
- Docker Hub
- Azure Container Registry
- JFrog Artifactory
- GitLab Container Registry
- GitHub Container Registry
- Harbor
- Cloudsmith
- GitHub Actions
- GitLab CI
Alternatives to Cosign
- SignPathGoverned signing for teams shipping software across diverse artifact formats.9.4
- DigiCert Software Trust ManagerEnterprise signing governance for artifacts, approvals, keys, and release pipelines.9.2
- SignServerA flexible open-source signing server with enterprise controls for production deployments.9.0
Used Cosign? Be the first to review it
The editor score above is our own research. What this page doesn't have yet is a reader's view — what you used Cosign for, what worked and what didn't. No stars are seeded and no review is paid for; an editor reads every one before it appears.
Write a reviewTwo minutes · verified accounts only · read by an editor before it appears
Featured on iTechGuides
Cosign is listed in our Code Signing Software directory. Add the badge to your site — it links back to this page.
<a href="https://www.itechguides.com/products/cosign/"><img src="https://www.itechguides.com/best/badge/cosign.svg" alt="Featured on iTechGuides" width="230" height="46"></a>
Reviewed by iTechGuides Editors · Editorial team · Updated Oct 2026
Advertiser disclosure: iTechGuides is reader-supported. Vendors can pay for top positions in our rankings and for a place on other products' pages, and we may earn a commission when you click some links. Bought places stand at the number bought; this page and our disclosure say so. Paying vendors may get a fuller, more detailed review from our editors, and that review can change their score. How we rank.
Last updated · How we research and update