Cacomi
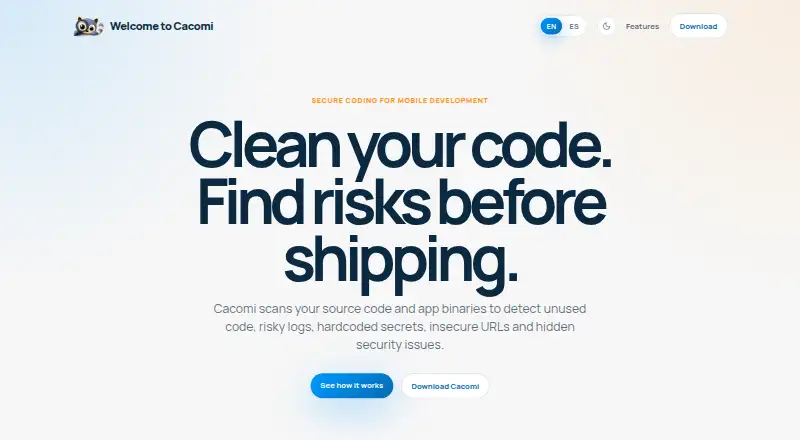
Cacomi: A Mac-based mobile SAST tool with source, binary, taint-flow, and AI analysis. Ranked #20 of 21 in Mobile Application Security Testing Software by our editors (6.8/10); pricing: Paid; best for mac users needing self-hosted mobile SAST.
At a glance
- Editor score6.8 / 10
- PricingPaid
- Best forMac users needing self-hosted mobile SAST
- Mobile platformsBoth
- Facts checked20 Sep 2026
Where it wins
- Scans mobile source code plus IPA, APP, and APK binaries
- Finds secrets, sensitive logs, insecure storage, and taint-flow risks
- Exports OWASP-aligned findings in PDF, SARIF, and JSON
Where it doesn't
- Runs only on macOS
- Does not perform dynamic analysis
- Does not replace penetration testing
Our verdict on Cacomi
Cacomi is a self-hosted static application security testing tool for developers building mobile applications on macOS. It analyzes native iOS and Android projects, along with Flutter projects and Python backends. Source-code and binary scanning cover IPA, APP, and APK files, making it suitable for teams that want security checks during development or before release without sending analysis away from the local Mac environment.
Its strongest capability is the breadth of mobile-focused static checks. Cacomi looks for hardcoded secrets and credentials, sensitive log and debug statements, insecure storage, weak cryptography, insecure URLs, risky permissions, unused code, and other security patterns. Taint-flow analysis adds data-flow visibility, while AI and ML usage discovery produces an AI BOM inventory. Findings align with OWASP MASVS and MASTG, and reports can be exported as PDF, SARIF, or JSON for documentation and security workflows.
The platform fit is clear but narrow: macOS is the supported platform, and the deployment model is self-hosted. Cacomi focuses on static analysis rather than runtime behavior, so it does not provide dynamic testing and should not be treated as a replacement for penetration testing. The product is described as pre-release and work in progress, which matters for teams seeking a mature, broad testing suite. Choose Cacomi for local mobile source and binary analysis on a Mac, especially when taint flow, AI inventory, and standards-aligned reports matter. Choose an alternative if dynamic analysis, broader platform coverage, or a complete penetration-testing workflow is required.
Your product? Our editors can test Cacomi in depth and publish a review, labelled as paid · from $149/mo →
Cacomi pricing
Cacomi fact sheet
| Free plan | Not verified |
|---|---|
| Paid from | Not verified |
| Mobile platforms | Both |
| Static binary analysis | Yes |
| Dynamic app analysis | No |
| Sensitive-data flow | Yes |
| Deployment model | Self_hosted |
| Included apps | Not verified |
| Deployment | Desktop |
| Platforms | macOS |
| Support | |
| Built for | Solo, Small business (editorial estimate) |
| Pricing | Paid |
| Website | cacomi-app.com |
| Facts checked | 20 Sep 2026 |
Alternatives to Cacomi
- AppknoxBroad hybrid testing for teams securing mobile apps across the development lifecycle.9.4
- OstorlabBroad mobile AppSec coverage with freemium entry and cloud delivery.9.3
- NowSecure PlatformDeep mobile runtime and binary analysis for teams securing release pipelines.9.2

Used Cacomi? Be the first to review it
The editor score above is our own research. What this page doesn't have yet is a reader's view — what you used Cacomi for, what worked and what didn't. No stars are seeded and no review is paid for; an editor reads every one before it appears.
Write a reviewTwo minutes · verified accounts only · read by an editor before it appears
Featured on iTechGuides
Cacomi is listed in our Mobile Application Security Testing Software directory. Add the badge to your site — it links back to this page.
<a href="https://www.itechguides.com/products/cacomi/"><img src="https://www.itechguides.com/best/badge/cacomi.svg" alt="Featured on iTechGuides" width="230" height="46"></a>
Reviewed by iTechGuides Editors · Editorial team · Updated Oct 2026
Advertiser disclosure: iTechGuides is reader-supported. Vendors can pay for top positions in our rankings and for a place on other products' pages, and we may earn a commission when you click some links. Bought places stand at the number bought; this page and our disclosure say so. Paying vendors may get a fuller, more detailed review from our editors, and that review can change their score. How we rank.
Last updated · How we research and update