
Bitsight Cyber Threat Intelligence
Bitsight Cyber Threat Intelligence: Broad CTI and exposure intelligence for organizations managing external risk. Ranked #11 of 32 in Threat Intelligence Platforms by our editors (8.2/10); pricing: Pricing on request; best for organizations combining CTI with exposure management.
At a glance
- Editor score8.2 / 10
- PricingPricing on request
- Best forOrganizations combining CTI with exposure management
- Free planNo
- Indicator enrichmentYes
- Founded2011 · Boston, Massachusetts, United States
- Facts checked20 Sep 2026
Where it wins
- Combines web, credential, vulnerability, ransomware, and brand intelligence
- Enriches indicators with contextual threat correlation and asset intelligence
- Connects with SIEM, SOAR, EDR, identity, TIP, and ticketing tools
Where it doesn't
- Pricing requires contacting sales
- Cloud deployment may not suit teams needing other delivery models
- Higher-tier capabilities add cost and packaging complexity
Our verdict on Bitsight Cyber Threat Intelligence
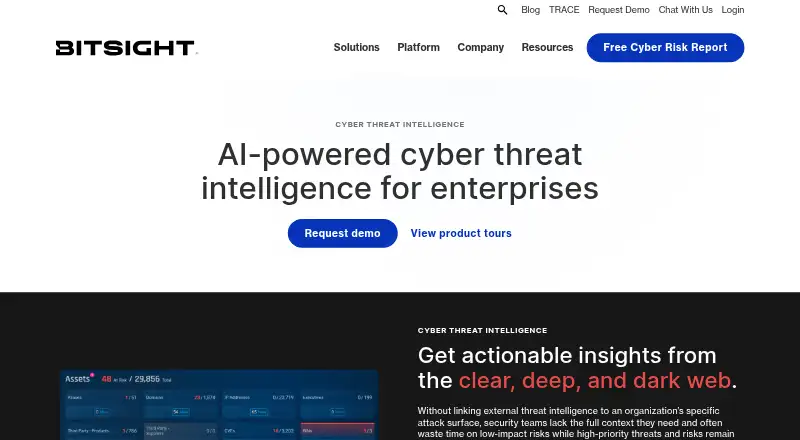
Bitsight Cyber Threat Intelligence is a cloud-based platform for enterprise security, SOC, incident response, and threat intelligence teams. It gathers clear, deep, and dark web intelligence, then connects indicators with organizational assets, compromised credentials, vulnerabilities, ransomware activity, adversary behavior, and brand threats. The platform also includes AI-assisted reports, summaries, alerts, workflows, APIs, and STIX/TAXII exchange. It is best suited to organizations that want threat intelligence tied directly to exposure management rather than a narrowly focused indicator feed.
Pricing is handled through contact with sales, and there is no free plan. The Basic plan includes rating and risk vectors, asset management, issue management and tracking, basic reports and alerts, and basic threat insights. Standard adds API and integrations, peer analytics, benchmarking, risk remediation, and advanced reports and alerts. Advanced adds subsidiary management, five MySubsidiary licenses, a subsidiary improvement plan, and Identity Intelligence. Teams should therefore map their needs to the plan structure before choosing a tier, particularly if integrations, benchmarking, subsidiaries, or identity intelligence are central requirements.
Its strongest fit is an existing security ecosystem: published integrations include Microsoft Sentinel, Splunk, Elastic, Sumo Logic, Palo Alto Cortex XSOAR, ThreatConnect, Anomali, MISP, CrowdStrike Falcon, SentinelOne, Microsoft Defender, and Okta. Intelligence can also be delivered through APIs and STIX/TAXII, supporting operational use across security tools. The trade-off is breadth: teams seeking exposure context across assets, vulnerabilities, credentials, phishing, and ransomware may find the coverage appropriate, while buyers wanting a lightweight standalone TIP or publicly priced entry plan should consider a more focused alternative.
Your product? Our editors can test Bitsight Cyber Threat Intelligence in depth and publish a review, labelled as paid · from $149/mo →
Bitsight Cyber Threat Intelligence pricing
All 3 Bitsight Cyber Threat Intelligence plans and prices →
Bitsight Cyber Threat Intelligence fact sheet
| Free plan | No |
|---|---|
| Paid from | Not verified |
| Indicator enrichment | Yes |
| STIX/TAXII support | Yes |
| Report management | Yes |
| Workflow automation | Yes |
| Case management | Not verified |
| Deployment | Cloud |
| Deployment | Cloud |
| Platforms | Web |
| Compliance & security | SOC 2 |
| Support | Email, Live chat, Tickets |
| Built for | Enterprise (editorial estimate) |
| Integrations | 19 integrations: Microsoft Sentinel, Splunk, Elastic, Sumo Logic, StrikeReady, Palo Alto Cortex XSOAR … See all → |
| Pricing | Pricing on request (source) |
| Website | bitsight.com |
| Facts checked | 20 Sep 2026 |
Bitsight Cyber Threat Intelligence integrations
Bitsight Cyber Threat Intelligence lists 19 integrations on its own site.
- Microsoft Sentinel
- Splunk
- Elastic
- Sumo Logic
- StrikeReady
- Palo Alto Cortex XSOAR
- D3 Security
- Swimlane
- ThreatConnect
- Anomali
- MISP
- CrowdStrike Falcon
- SentinelOne
- Microsoft Defender
- Okta
- Microsoft Entra ID
- Jira
- ServiceNow
- OpenCTI
See all Bitsight Cyber Threat Intelligence integrations →
Alternatives to Bitsight Cyber Threat Intelligence
- Anomali PlatformA broad enterprise TIP combining intelligence operations, telemetry, cases, automation, and AI.9.3
- Recorded Future Intelligence CloudA broad intelligence platform for teams that need risk context across security workflows.9.2
- Group-IB Threat Intelligence PlatformA broad cloud platform for actor research, dark-web monitoring, leaks, and intelligence operations.9.0
See all Bitsight Cyber Threat Intelligence alternatives →
Used Bitsight Cyber Threat Intelligence? Be the first to review it
The editor score above is our own research. What this page doesn't have yet is a reader's view — what you used Bitsight Cyber Threat Intelligence for, what worked and what didn't. No stars are seeded and no review is paid for; an editor reads every one before it appears.
Write a reviewTwo minutes · verified accounts only · read by an editor before it appears
Featured on iTechGuides
Bitsight Cyber Threat Intelligence is listed in our Threat Intelligence Platforms directory. Add the badge to your site — it links back to this page.
<a href="https://www.itechguides.com/products/bitsight-cyber-threat-intelligence/"><img src="https://www.itechguides.com/best/badge/bitsight-cyber-threat-intelligence.svg" alt="Featured on iTechGuides" width="230" height="46"></a>
Reviewed by iTechGuides Editors · Editorial team · Updated Oct 2026
Advertiser disclosure: iTechGuides is reader-supported. Vendors can pay for top positions in our rankings and for a place on other products' pages, and we may earn a commission when you click some links. Bought places stand at the number bought; this page and our disclosure say so. Paying vendors may get a fuller, more detailed review from our editors, and that review can change their score. How we rank.
Last updated · How we research and update