AFL++
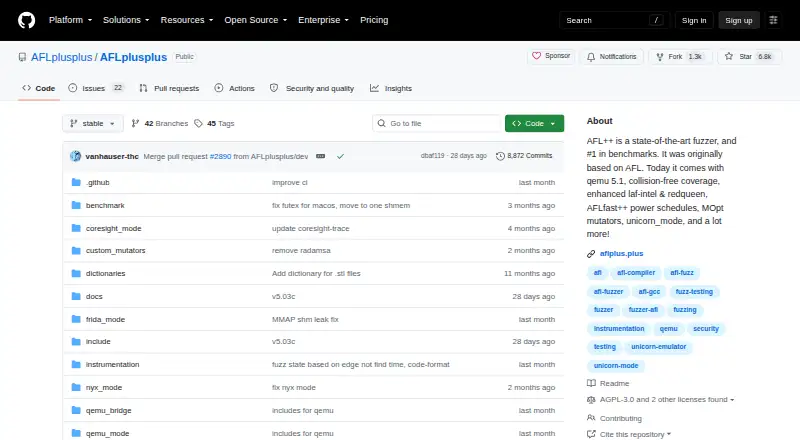
AFL++: A broad, free fuzzer for native code, binaries, libraries, and file-processing tools. Ranked #4 of 25 in Fuzz Testing Software by our editors (8.7/10); pricing: Free plan; best for general-purpose native and binary fuzzing.
At a glance
- Editor score8.7 / 10
- PricingFree plan
- Best forGeneral-purpose native and binary fuzzing
- Free planYes
- Paid fromFree
- Input generation methodsmutation
- Founded2019
- Facts checked20 Sep 2026
Where it wins
- Supports source and binary-only fuzzing across four platforms
- Combines persistent execution, custom mutators, and parallel fuzzing
- Includes crash triage, minimization, dictionaries, and CI support
Where it doesn't
- Local execution puts setup and operations on the user
- Its primary focus is native programs and selected binary targets
- Mutation-based input generation may not suit every testing strategy
Our verdict on AFL++
AFL++ is an open-source, coverage-guided fuzzer for developers and security researchers testing programs and libraries. It targets file-processing programs, command-line tools, native libraries, and selected binary targets. Supported target types include source-code targets, binary-only targets, file inputs, stdin inputs, Android native libraries, and Win32 PE binaries. AFL++ covers Linux, macOS, Android, and Windows, with language support for C, C++, Python, and Rust.
Its main strength is breadth within native and binary fuzzing. Source targets can use LLVM or GCC-plugin instrumentation, while QEMU, FRIDA, Unicorn, and related modes support binary-only targets. Persistent execution and in-memory test-case delivery can support faster target cycles, while custom mutators in C/C++ and Python extend input-generation workflows. User-supplied and automatically generated dictionaries add another way to shape mutation campaigns. Parallel fuzzing with corpus synchronization supports distributed work across fuzzing processes.
AFL++ also covers the operational parts of a fuzzing workflow: it collects crashes and hangs, supports crash exploration and test-case minimization, and provides a Docker image for installation and execution. Its CI/CD support fits teams that want fuzzing in development workflows, while local execution makes it a tool for environments where users manage the runtime themselves. Choose AFL++ for a free, open-source option with wide instrumentation and target coverage. An alternative may fit better when the priority is a hosted service, a managed interface, or testing approaches beyond mutation-focused native and binary targets.
Your product? Our editors can test AFL++ in depth and publish a review, labelled as paid · from $149/mo →
AFL++ pricing
AFL++ fact sheet
| Free plan | Yes |
|---|---|
| Paid from | Free |
| Input generation methods | mutation |
| Target types | source-code targets, binary-only targets, file inputs, stdin inputs, Android native libraries, Win32 PE binaries |
| Coverage guidance | Yes |
| Crash triage | Yes |
| Execution mode | Local |
| Supported languages | C, C++, Python, Rust |
| CI/CD support | Yes |
| Deployment | Self-hosted |
| Platforms | Linux, macOS, Android, Windows |
| Support | Community, Docs |
| Built for | Solo, Small business, Mid-market, Enterprise (editorial estimate) |
| Pricing | Free plan |
| Website | github.com |
| Facts checked | 20 Sep 2026 |
Alternatives to AFL++
- MayhemMayhem brings broad hybrid fuzz testing, triage, and regression coverage to CI workflows.9.4
- OSS-FuzzA cloud-based continuous fuzzing service for qualifying open-source projects.9.2
- ClusterFuzzA broad, self-managed fuzzing platform for continuous security and stability testing.8.9


AFL++ vs the competition
- AFL++ vs Mayhem
- AFL++ vs OSS-Fuzz
- AFL++ vs ClusterFuzz
- AFL++ vs EvoMaster
- AFL++ vs FuzzForge
- AFL++ vs Jazzer
Compare AFL++ with any tool side by side →
Also Ranked In
AFL++ is ranked in 4 of our directories.
Used AFL++? Be the first to review it
The editor score above is our own research. What this page doesn't have yet is a reader's view — what you used AFL++ for, what worked and what didn't. No stars are seeded and no review is paid for; an editor reads every one before it appears.
Write a reviewTwo minutes · verified accounts only · read by an editor before it appears
Featured on iTechGuides
AFL++ is listed in our Fuzz Testing Software directory. Add the badge to your site — it links back to this page.
<a href="https://www.itechguides.com/products/afl/"><img src="https://www.itechguides.com/best/badge/afl.svg" alt="Featured on iTechGuides" width="230" height="46"></a>
Reviewed by iTechGuides Editors · Editorial team · Updated Oct 2026
Advertiser disclosure: iTechGuides is reader-supported. Vendors can pay for top positions in our rankings and for a place on other products' pages, and we may earn a commission when you click some links. Bought places stand at the number bought; this page and our disclosure say so. Paying vendors may get a fuller, more detailed review from our editors, and that review can change their score. How we rank.
Last updated · How we research and update