
Windows Errors? Fix Them Before They Spread
Repair common Windows errors and clear accumulated junk for a smoother, more stable PC - no reinstall needed.Free scan · no reinstallOutdated Drivers Are Slowing You Down
One free scan finds every outdated or missing driver and matches the right update for your exact hardware.Free scan · exact hardware match/.well-known/ is a standardized web path, not a safety stamp. The FBI and CISA documented a fake page hosted at a URL under this directory, showing that malicious content can appear there—but not how often it happens. If you find an unexpected login page, payment prompt, redirect, or executable file in your site’s directory, treat it as a possible compromise: preserve evidence, investigate how it got there, and restrict access without breaking resources your site needs.
What is the `/.well-known/` directory?
RFC 8615 defines /.well-known/ as a path prefix for locating resources associated with a website’s origin. Published by the IETF in May 2019, the standard applies to supported URI schemes including HTTP and HTTPS. Individual applications define what a resource at a particular path means; the prefix itself does not prescribe one universal format or content type. RFC 8615
Sites use well-known URIs for specific purposes. For example, security.txt can publish a site’s security policy and contact details; OWASP describes serving it from /.well-known/security.txt. OWASP Web Security Testing Guide v4.2
The directory name does not make its contents trustworthy. A browser still receives what the site’s server serves at that URL. RFC 8615 warns that operators should control who can write well-known resources, including through filesystem and server-configuration permissions. It also notes that dot-directories can be hidden from administrators, making unauthorized files easier to overlook.
The Tool Desk
Outbyte PC Repair FREERepair Windows errors before they cause bigger problemsFix Now →Outbyte Driver Updater FREEFix the driver behind crashes, sound loss and screen glitchesFind Drivers →#1 Best Overall

- 1. 【Multi-Functional USB-C Hub & Security】** Upgraded design features a built-in **USB-C pass-through charging and data port**. Unlike basic fingerprint scanners, this allows you to simultaneously use your fingerprint login while keeping your USB-C port free for charging your laptop or connecting a wireless mouse/keyboard. Perfect for modern laptops with limited ports.
- 2. 【Premium Aluminum Build & Portability】** Crafted from a **durable aluminum alloy** casing, this scanner is built to withstand the rigors of daily travel and desk life. Included **3M adhesive backing** allows you to securely mount it to your laptop lid or desk, ensuring it stays put in your bag and is always ready for instant access.
- 3. 【Instant Windows Hello Login (<1 Sec)】** Experience **password-less login in under one second**. With full support for **Windows 10/11 and Windows Hello**, this biometric reader provides seamless, secure access to your device, apps, and websites. Just a touch and you're in—no more typing complex passwords in coffee shops or airports.
- 4. 【360° Touch & Data Pass-Through】** Equipped with **360-degree capacitive touch** technology, it reads your fingerprint accurately from any angle. The upgraded USB-C port supports **data synchronization**, allowing you to connect and read a flash drive or external hard drive through the scanner without any loss in speed.
- 5. 【Universal Compatibility for On-the-Go Pros】** Designed for modern hybrid workers. Simply plug-and-play on any **Windows 10/11 laptop or PC** with a USB-C port. No complicated setup required. The compact size and detachable cable (with the adhesive mount) make it the ideal security companion for business travel and hot-desking.
What phishing example did CISA and the FBI report?
The joint FBI/CISA advisory “Known Indicators of Compromise Associated with Androxgh0st Malware”, released January 16, 2024, describes threat actor capabilities that include setting up a fake, illegitimate page accessible through a URI. One example is printed in the advisory as https://chainventures.co[.]uk/.well-known/aas. The address is defanged here as in the advisory; do not visit it.
This is evidence that a fake page can be placed at a well-known URI, not evidence that attackers commonly use this directory for phishing. The advisory also discusses Androxgh0st targeting Laravel applications and Apache HTTP Server versions 2.4.49 or 2.4.50 in connection with CVE-2021-41773. It does not establish that those vulnerabilities caused the particular /.well-known/aas example.
Rank #2

- 📱 QR CODE SETUP GUIDE: Scan the QR code on the packaging to access the setup page with Windows drivers and installation instructions. The package includes the main item and a Japanese manual. On the website, tap the 🌐 World icon to switch to English, then scroll down to download the English manual.
- 🚀 INSTANT ACCESS: Login 10x faster than typing passwords - Under 1 second!
- 🛡️ HIGH-LEVEL SECURITY: Match-On-Chip technology = Your fingerprint NEVER leaves the device
- 🎯 WORKS EVERY TIME: 99.999% accuracy with 360° recognition - Touch from any angle!
- 💻 PLUG & PLAY MAGIC: Zero software installation - Works instantly with Windows 10/11 Hello
Can a website be hacked through its `/.well-known/` directory?
The path itself is not a vulnerability or an access-control mechanism. The risk is that someone gains the ability to write files or alter the server’s responses, then places malicious content at a path administrators may not routinely inspect. A familiar-looking URL or valid HTTPS connection does not show that a page is legitimate.
If you manage the site, investigate an unexpected file or page as a possible sign of unauthorized access. A phishing page may be only one visible symptom; establish how it was created and whether other files, accounts, or application data were affected.
Quick wins for a faster PC:
Scan for outdated or missing drivers - takes under a minuteDriver Scan →Clear out junk files and repair common Windows errorsFree Scan →Fix the driver behind crashes, sound loss and screen glitchesFind Drivers →Rank #3

- "Hot swappable Play Arrange with 1.5m Cablemail: Enjoy bother complimentary installation and flexible placement with a generous 1.5m USB cable, allowing accessible positioning for any computer arrange lacking driver demands"
- Tap Hook for Strengthened Security: Day night private data by simply poignant the transducer to instantly hook your computer
- "FIDO Licensed Multiple Function Security: Beyond Windowslogin, this reader serves as a FIDO U2F/FIDO2 security code for websites/apps like Two processor , providing immune 2FA security"
- "Sophisticated Controlled Breathing Ligheight: Board game with a smooth sensitive light club highlighting modifiable breathing consequences, reducing organ of sight strain while enhancing beauty"
- "Recognition & Immediate Loginumberebog: Knowledge extreme fast fingerprint scanning with recognition corner, facilitating secure passcode complimentary signin through Windowslogin for 10/11 PCs and laptops in under 1 second"
How should site owners investigate and remove an unexpected page?
- Preserve evidence first. Record the full path, capture the response or a screenshot without entering credentials, and preserve relevant files and logs. Check file ownership, timestamps, deployment history, and web-server or hosting logs. Timestamps alone do not prove when or how an intrusion occurred.
- Identify the write path. Review which deployment accounts, applications, plugins, and shared-hosting components can write to the site origin. Determine how the content was introduced before treating removal as a complete fix.
- Contain and remove unauthorized content. After preserving evidence, remove the malicious file or page and any unauthorized redirects or configuration changes. If the site is actively serving a credential-harvesting page, use your hosting provider’s incident process or an appropriate temporary block while investigating.
- Restore least-privilege access. Limit write permissions to the well-known resources the site actually uses. Review deployment credentials and server configuration so unrelated accounts or applications cannot write there.
- Patch exposed software. CISA advises prioritizing known exploited vulnerabilities in internet-facing systems and specifically warns not to run Apache HTTP Server 2.4.49 or 2.4.50. Confirm versions and apply supported security updates for the actual software in use.
- Check for other indicators. CISA recommends scanning for unrecognized PHP files, particularly in the site root and
/vendor/phpunit/phpunit/src/Util/PHP, and reviewing suspicious outbound GET or cURL requests to file-hosting sites, especially requests for.phpfiles. - Address potentially exposed secrets. If investigation indicates credentials or application secrets may have been exposed, review access and rotate or revoke affected credentials as appropriate to the confirmed incident.
How can you restrict access without breaking required resources?
Inventory the well-known paths your site intentionally serves before changing access rules. Then configure the server or application to deny requests by default and allow only the required resources. Blocking the entire prefix without checking dependencies can disable legitimate functions, while allowing broad write access creates unnecessary risk.
For applications that serve well-known resources, RFC 8615 also discusses application-specific precautions such as careful media-type handling, the X-Content-Type-Options: nosniff header, and Content Security Policy where active content is relevant. These measures can reduce certain content-handling risks; they do not clean an already compromised server or replace permission controls.
Quick Recap
Best Value
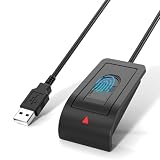
- Windows Hello Fingerprint Login: Designed for windows hello fingerprint reader compatibility on Windows 10/11 PCs, this usb fingerprint reader replaces passwords with fast one-touch biometric access. Enjoy convenient, secure login through your PC’s built-in Windows Hello system without extra software.
- Match-in-Sensor Security Protection: This fingerprint reader uses advanced biometric processing to verify fingerprints inside the sensor, helping protect your personal data. Your fingerprint information stays stored locally on your Windows device and is never uploaded or shared externally.
- Fast & Accurate Biometric Recognition: Built as a reliable fingerprint scanner for everyday computer security, this fingerprint reader for windows 11 provides quick recognition and stable performance. Access your PC, lock screens, and manage user accounts with a simple touch.
- Plug & Play Desktop Convenience: The usb fingerprint reader windows 11 solution connects easily through USB with no complicated drivers or third-party apps. The included 4ft cable provides flexible placement for desktops, workstations, and home office setups.
- Designed for Windows PC Security: This fingerprint scanner for pc supports password-free login through Windows Hello and works as a practical windows fingerprint reader for compatible systems. Compact design and angled sensor placement offer comfortable daily use.
Rank #4

- Instant Windows Hello Integration: Quickly unlock your Windows 10/11 PC with your fingerprint. No need to type passwords—just one touch for fast and secure access. Works directly with Windows Hello, no extra software needed.
- Plug & Play Simplicity: No drivers needed for genuine Windows systems—just plug it in and it works. Automatically recognized in most cases (95%+ compatibility). Tip: Manual driver update may be required for non-genuine systems.
- USB Fingerprint Reader: A compact metal fingerprint scanner for PCs and laptops that makes logging in quick and easy—just plug it into any USB port and start using it. Its ultra-portable design fits perfectly in your laptop bag.
- Microsoft-Certified Security: Fully supports Windows Hello and the Windows Biometric Framework for safe and reliable login. Features high accuracy (0.001% false acceptance / 0.1% false rejection) to keep your data secure. Also supports password and file encryption for most websites.
- Multi-User Flexibility: Store up to 10 fingerprints—perfect for shared devices at home or work. Enjoy fast and smooth access with lightning-speed authentication in under 0.5 seconds.
What does a complete response need to accomplish?
- Preserve enough evidence to understand the incident and its entry or write path.
- Remove unauthorized content and restore least-privilege write access.
- Address exposed software or credentials where the investigation confirms a risk.
- Keep the site’s legitimate well-known resources working.
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

