
An online/offline password attack is defined by where an attacker checks guesses. Online, candidates are sent to a live login service, where its defenses can limit attempts. Offline, candidates are tested against stolen password hashes without contacting that service, so login throttling cannot stop the work. The distinction determines which defenses can still help.
What is the difference between online and offline password attacks?
| Factor | Online guessing | Offline cracking |
|---|---|---|
| Where guesses are checked | At a live login service or other authentication endpoint. | Locally against stolen password hashes or equivalent verifier material. |
| What the attacker needs | Access to the service’s login endpoint. | A copy of the password hashes or equivalent material, commonly obtained in a database breach. |
| Does the service’s rate limit apply? | Yes. The service can slow, block, or otherwise constrain attempts. | No. Guesses are not passing through the login service. |
| Defender’s main leverage | Rate limiting, password blocklists, and other login protections. | Suitable salted password hashing with an appropriately high work factor, resistant passwords, and response to the compromise. |
Neither attack necessarily tests every possible character combination. Attackers can prioritize likely passwords, common patterns, or credentials exposed in other breaches. “Brute force” describes repeated guessing broadly; the practical guesses may be selected rather than exhaustive.
How do online brute-force defenses work?
With online guessing, every attempt has to reach the verifier. That gives the service an opportunity to count failures and constrain further requests. Rate limiting can slow attempts, while blocklists can reject passwords known to be common or compromised. OWASP describes these as relevant authentication measures in its Authentication Cheat Sheet.
NIST SP 800-63B-4 requires verifiers to implement controls against online guessing when applicable. For specified authenticator cases, it sets 100 consecutive failed attempts as an upper bound; agencies may set lower limits. This is not a universal recommendation that every consumer service allow 100 tries. The applicable requirement depends on the authenticator and context. See NIST SP 800-63B-4.
#1 Best Overall

- 【Strong Adsorption】The inspiration of the silicone phone suction case comes from the adhesive force of the octopus. Each suction cup phone mount is 3.15 inches long and 2.17 inches wide, with 24 independent suction cups providing a stronger and more stable suction force, so you don't have to worry about your phone falling during use.
- 【Back of Phone Suction Grip】Remove the adhesive film on the phone suction cup and stick it on the phone case. You can then fix the phone on any smooth surface, which is very convenient. (The phone suction cup cannot be removed and reused after being attached to the phone case. It is recommended to attach it to a regular phone case, not a valuable one.)
- 【Widely Used】Our non-slip silicone phone sticky grip mount attaches to almost any flat phone case and make it compatible with common mobile phones such as iPhone and Android.You can shoot, watch videos or video calls in the kitchen, gym, dance studio, bathroom and other places.
- 【Capture the Wonderful Picture】Whether you are a TikTok creator or just like to share videos and photos, this phone suction cup can help you hands-free capture wonderful videos and photos for sharing with friends.
- 【Note】You can fix the phone suction cup on a smooth surface such as a mirror or glass. If necessary, wipe the suction cup with a damp cloth to obtain stronger suction. Before releasing your hand, make sure the phone is firmly fixed. (Not applicable to rough walls, wooden surfaces, and other uneven surfaces)
Related attack names describe different guess patterns, not interchangeable defenses:
- Password guessing: repeated guesses directed at an account.
- Password spraying: a small set of common passwords tried across many accounts.
- Credential stuffing: usernames and passwords exposed elsewhere tried at another service.
Distinct passwords matter especially for credential stuffing: a password compromised at one site should not unlock an account at another. A password manager can help people generate and keep unique passwords, but it does not repair a service’s password storage.
Rank #2

- SUPERIOR COMFORT — Unlike traditional circular ear buds, the design of EarPods is defined by the geometry of the ear. Which makes them more comfortable for more people than any other ear bud–style headphones.
- HIGH-QUALITY AUDIO — The speakers inside EarPods have been engineered to maximize sound output and minimize sound loss, which means you get high-quality audio.
- BUILT-IN REMOTE — EarPods with USB-C plug also include a built-in remote that lets you adjust the volume, control the playback of music and video, and answer or end calls with a pinch of the cord.
- COMPATIBILITY — Works with all devices that have a USB-C port.
- INTEGRATED MICROPHONE — A built-in microphone precisely captures your voice while you’re on the phone, taking a FaceTime call, or summoning Siri — so you’re always heard loud and clear.
Why can attackers crack password hashes offline?
A password hash is a stored verifier derived from a password. If an attacker obtains the hash file, they can calculate candidate passwords and compare the resulting values with the stolen hashes without asking the website to authenticate. The website’s account lockout or rate limit cannot count those local calculations.
NIST SP 800-63B-4 (2025) describes current offline hash-computation capability as “many billions of hashes per second” in the absence of rate limiting. That is a broad qualitative statement, not a benchmark for every algorithm, configuration, or attacker. It should not be used to claim a fixed time to crack a particular password. Actual results depend on the password, hashing scheme and cost factor, and available computing resources.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
Rank #3

- Secure Hold: Our PopSockets adhesive phone grip gives your cell phone a secure, comfortable hold in hand to help prevent drops while texting, taking photos, or scrolling on the go. Designed to stick firmly to most phone cases and devices.
- Hands-Free Made Easy: Easily turn your PopSocket into a phone stand to prop up your phone anywhere, perfect for watching videos, video calls, or following recipes. A must-have phone holder that keeps your device secure and ready for anything.
- Compatibility: Works with all phones, tablets, and Kindles. Sticks best to smooth, hard plastic cases and may not adhere to silicone or textured cases. Easily swap your PopTop to change up your style.
- Black PopSockets: Simple, refined, and endlessly versatile. A timeless essential for any phone.
- Travel Must-Have for People On the Go: A must-have travel accessory for flights, flying, airports, air travel, airplanes, planes, international trips, cruises, and long travel days. Key gadget for your airport haul, travel accessories and must-haves.
How do salts and password hashing make offline cracking harder?
NIST’s password-storage requirement states: “Passwords SHALL be salted and hashed using a suitable password hashing scheme.” A salt is a unique value stored with the hash; it is not a secret key. NIST says salts should be at least 32 bits and selected to minimize collisions among stored hashes. OWASP explains in its Password Storage Cheat Sheet that unique salts prevent an attacker from reusing one calculation across multiple accounts.
Salting does not make a weak password uncrackable. It prevents precomputed hash lookup from applying directly and makes each account’s candidate calculations distinct. The hashing scheme’s cost factor adds work to each guess. NIST’s recommendation is: “The chosen cost factor SHOULD be as high as practical without negatively impacting verifier performance.” That balances resistance to offline guessing with acceptable authentication performance.
Rank #4

- [360 ° Flexible Rotation Design] Comes with a rotatable lanyard ring that supports 360 ° free rotation, effectively solving the problem of twisted and tangled lanyards
- [Wide compatibility] The ultra-thin 0.02-inch design does not block the charging port at all, and both wired and wireless charging can be used directly without removing the pad. Compatible with most smartphones such as iPhone, compatible with various wristbands, lanyards, crossbody straps, and keychains
- [Durable and Portable Material] Premium rust-resistant stainless steel material with good flexibility, which not only avoids scratching the phone case, but also has excellent anti rust and anti fading performance
- [Multi scenario Practical] Paired with a lanyard or wristband, hands-free use can be achieved. The phone is within reach and not easily dropped, ideal for daily commuting and outdoor activities. Suitable for full coverage phone cases, does not support half coverage phone cases
- [Quality Service] If you find any damage or other issues with the product upon receipt, please contact us immediately. We will handle it quickly
NIST also recommends recording the scheme and cost-factor reference so the verifier can migrate to a newer scheme or raise the work factor over time. It recommends an additional keyed hashing or encryption iteration using a secret key stored separately; when deployed, that added layer can make brute-force attacks impractical while the key remains secret. This is an additional control, not something every service necessarily uses.
Independent reader supportYour contribution helps us test, update, and keep practical guides available for everyone.What should users and service operators do?
If you use the account
- Use a distinct password for each service so a breach at one site does not directly expose another account.
- If a service reports a breach or you have evidence your password was exposed, change it there and anywhere else you reused it.
If you operate the authentication service
- Apply controls against online guessing, including appropriate attempt limiting and checks against common or compromised passwords.
- Store passwords using a suitable salted password-hashing scheme, with a cost factor high enough for the service’s performance constraints.
- Plan for hash-scheme and cost-factor migration; keep any additional secret key separate from the hash database if using a keyed iteration.
- After a hash compromise, treat the event as a storage and credential incident: assess exposure and require affected users to change credentials as appropriate. Online rate limits do not contain cracking of an already stolen hash file.
NIST SP 800-63B-4 also advises against mandatory periodic password changes absent evidence of compromise and against composition rules. Its guidance favors measures such as blocklists, secure storage, machine-generated passwords, and rate limiting. See NIST’s Strength of Passwords guidance. NIST notes that a hash’s size is independent of password length, while implementations still need reasonable processing limits.
The Tool Desk
Outbyte Driver Updater FREEScan for outdated or missing drivers - takes under a minuteDriver Scan →Outbyte PC Repair FREERepair Windows errors before they cause bigger problemsFix Now →Best Value
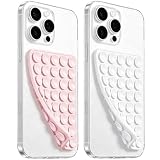
- 【PKYAA Double Sided Silicone Suction Phone Case Mount】PKYAA With Double Sided 40 Strong and Reliable individual suction cups, PKYAA provides a thicken and upgraded universal silicon suction mount for your phone.
- 【Friendly to Content Creators】If you are a content creator or an online influencer, you can create videos anywhere with this suction mount completely hands free with this silicone cell phone mount for cases.
- 【HANDS-FREE & Adhere to Mirrors】This Double Sided silicone suction phone case mount allows you to stick your phone to the mirror easily. No longer holding your phone in one hand to watch video tutorials while making up.
- 【Strong Grip on the Smooth Surface】You can easily hang your phone anywhere with a smooth surface. All you do is you clean off your phone and smooth surface. It is STURDY and it not only sticks to mirrors, it also sticks to windows, it sticks to refrigerators, tiles and other clean, flat surfaces.
- 【Press Down Firmly Every 30 Minutes】Use your palm or fingers to press the phone down firmly and check it's secure before letting go. Apply even pressure for a few seconds to allow the suction cup to adhere properly. To maintain the grip and prevent accidental falls, it's a good practice to periodically reapply pressure to the suction cup.
Why does the online/offline distinction matter?
Online defenses control the path into a live verifier; offline defenses make stolen verification data expensive to test and reduce the likelihood that guesses will succeed. Neither replaces the other: throttling cannot protect a copied hash file, and strong hash storage does not stop unlimited attempts against a poorly protected login.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

