
Recommended Free Tools
Babuk’s leaked source code included an encryptor for VMware ESXi, giving other actors code they could study and adapt. That creates a continuing risk to virtual-machine files—but the available sources do not establish a measurable rise in Babuk-derived attacks in 2026. For ESXi operators, the practical response is to harden the hypervisor and protect isolated, tested backups.
What Babuk’s leak means for VMware ESXi
Babuk is a ransomware family whose builder and source code became publicly available in 2021. The published code included executables for Windows and Linux as well as an ESXi encryptor, according to VMware Security Blog authors Giovanni Vigna and Oleg Boyarchuk in their September 28, 2022 analysis. VMware’s technical description of Babuk’s ESXi encryptor


A public codebase can lower the effort required for another actor to build or modify an encryptor. Microsoft Security Intelligence’s description of a later Babuk Linux variant says the widespread availability of the original Linux ELF source code enables actors to deploy high-speed, multithreaded encryption against VMware ESXi hosts. Microsoft’s page was published May 20, 2025, and its search-result listing reports an update on March 23, 2026. Microsoft Security Intelligence: Ransom:Linux/Babuk!rfn
This is a code-lineage and risk story, not proof of a quantified new wave. The cited sources do not provide a 2026 count of incidents using Babuk-derived code, identify a comparable earlier baseline, or attribute a measured year-over-year increase to Babuk. VMware reported an increase in ESXi-targeting ransomware in its own telemetry in 2022; that historical observation does not establish a 2026 trend.
How Babuk’s ESXi encryptor affects virtual machines
VMware’s 2022 analysis says the Babuk ESXi encryptor scans a target directory for selected virtual-machine-related file extensions and encrypts matching files using Sosemanuk. It drops a ransom note named “How To Restore Your Files.txt.” The listed extensions are:
.log.vmdk.vmem.vswp.vmsn
The behavior that stands out is that Babuk does not shut down ESXi virtual machines before encrypting files. VMware warns that encrypting files while VMs are running can risk corruption or complicate decryption. In other ESXi ransomware cases, some families have used ESXi utilities to shut down VMs before targeting their files. VMware’s October 2022 tactics article describes these as recurring behaviors across multiple families, not as a current census of active groups. VMware’s overview of ESXi ransomware tactics
Rank #2
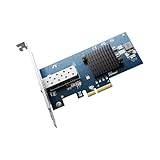
- GENUINE INTEL 82599EN, THE X520-DA1 SILICON: Sustained 10 Gigabit throughput for NAS transfers, VM migration and iSCSI storage; the link also steps down to 2.5G, 1G and 100M for a slower switch port
- NO VENDOR LOCK ON THE SFP+ CAGE: Third-party DAC twinax, AOC, 10GBASE-SR multimode and 10GBASE-LR single-mode optics all link up, unlike Intel-branded cards that reject modules they do not recognize
- PLUG AND PLAY ON PROXMOX, TRUENAS, UNRAID AND ESXI: Also detected by QNAP, Synology, Ubuntu, Debian and CentOS with no driver step; on Windows install the Intel Ethernet Adapter Complete Driver Pack
- ONLY FOUR PCIe LANES, BOTH BRACKETS IN THE BOX: Seats in any x4, x8 or x16 slot, leaving the rest of the board free; full-height and low-profile brackets both ship, for ATX towers, 1U and 2U racks, mini-ITX
- AIRFLOW, LIKE ANY 10G CARD: The passive heatsink runs warm by design, so give it case airflow or clip a small fan to it in a silent build; jumbo frames to 9KB and checksum offload run in hardware
Because ESXi hosts can support many virtual machines, an attack against the hypervisor or its storage can disrupt multiple systems at once. VMware’s 2022 analysis cautions that ESXi-targeting ransomware can cause infrastructure-level damage requiring substantial recovery and mitigation resources. The impact depends on which hosts, datastores, and workloads are affected and whether usable backups are available.
How to reduce ransomware risk on ESXi
No single control guarantees that a host will not be compromised or that every workload can be recovered. CISA’s #StopRansomware Guide recommends offline backups and hardening hypervisors and related infrastructure. CISA’s page did not provide a verifiable revision date in the material available here, so use it as general resilience guidance, not as a Babuk-specific response procedure. CISA #StopRansomware Guide
Harden the hypervisor and management plane
- Apply current vendor security updates to ESXi and related infrastructure, following the vendor’s applicable guidance and your change-control process.
- Restrict access to ESXi management interfaces to authorized administrators and trusted management networks; avoid exposing management access broadly to the internet.
- Protect administrative credentials, limit who can use them, and review access paths to the hypervisor and its management tools.
- Review the security of systems connected to the virtualization environment, since weaknesses in associated infrastructure can undermine host protections.
Keep backups isolated from production
Maintain backup copies that ransomware running in the production environment cannot readily alter or delete. An offline copy is one option; an external hard drive may suit some small or specific environments, but a consumer drive is not automatically an appropriate enterprise recovery solution. Choose media and procedures that match the size and criticality of the workloads.
- Isolation: Can an attacker using production or compromised administrator credentials reach, encrypt, or erase the backup?
- Recovery speed: How quickly can the organization restore essential services from that copy?
- Capacity and retention: Can it hold the required VM images and the needed history of restore points?
- Access control: Are backup administration and deletion permissions limited and protected?
- Operational fit: Can the organization reliably create, secure, monitor, and restore from the chosen backup arrangement?
Test restoration, not just backup completion
A successful backup job does not by itself prove that a VM can be restored in a usable state. Schedule recovery tests for representative workloads and confirm that staff know the restoration steps. Include the systems and dependencies needed to bring critical services back online, and update the recovery process when the environment changes.
Rank #4

- Note: Compatible with low-profile bracket only. Included full-height bracket is not compatible — please disregard.
- Controller: Realtek RTL8126 controller, equipped with RealWoW technology, supports wake-up and diagnostics, enhancing data stability, Scan the QR code on the NIC to download and install the driver.
- Interface: PCIe x1 lane, operable in PCIe X1, X4, X8 and X16 slots, not for PCI slots.
- System: Windows 8/10/11, Windows Server 2016/2019/2022, CentOS7/8/9, VMware ESXi 6, Ubuntu20/22, FreeBSD 13/14.
- Protocol: PXE, DPDK, WOL, iSCSI, Jumbo Frames, Auto MDIX, IEEE 802.1Q VLAN tagging, IEEE802.3bz (2.5G/5G BASE-T), Full Duplex flow control (IEEE 802.3x), NOT support FCoE.
What to do if an ESXi environment may be affected
If you suspect ransomware, treat the situation as an incident rather than assuming the note or file extension identifies the malware conclusively. Identify the affected hosts and workloads, preserve relevant evidence, and contain access in a way that limits further damage while supporting investigation and recovery. Involve qualified incident responders when the organization’s capability or the impact warrants it, and follow current CISA and vendor guidance.
Do not assume that Babuk’s public source code means a working decryption method is available for your files. The sources cited here establish neither a Babuk-specific recovery tool nor a current decryption success rate. Recovery depends on the particular malware, damage, available backups, and incident circumstances; no outcome is guaranteed.
Quick wins for a faster PC:
Repair Windows errors before they cause bigger problemsFix Now →Fix the driver behind crashes, sound loss and screen glitchesFind Drivers →Clear out junk files and repair common Windows errorsFree Scan →Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

