
The Tool Desk
Outbyte Driver Updater FREEFix the driver behind crashes, sound loss and screen glitchesFind Drivers →Outbyte PC Repair FREEClear out junk files and repair common Windows errorsFree Scan →Silent Skimmer is the name BlackBerry gave to a financially motivated campaign targeting businesses that host or build payment infrastructure. Reports published in 2023 described attackers exploiting vulnerable Telerik software to gain access to web servers and inject code into checkout pages to steal payment details. Unit 42 later reported a possibly related incident in May 2024, but the available reporting does not establish whether the activity continued after that date or who operated it.
What Silent Skimmer targeted—and when
BlackBerry described Silent Skimmer as opportunistic activity against businesses that host or create payment infrastructure, including online businesses and point-of-sale providers. A September 2023 report said the campaign initially focused on organizations in the Asia-Pacific region (APAC), and that businesses in Canada and the United States had also been targeted since October 2022. The reporting does not establish that every region was targeted throughout the same period. SecurityWeek’s September 19, 2023 report summarizes BlackBerry’s findings.
A November 2023 synopsis of BlackBerry’s threat report described targets in APAC, North America, and Latin America. That later account expands the reported geographic scope; it does not establish when activity began in each region. The synopsis is available from BlackBerry’s threat intelligence page.
There is no campaign-wide victim count, stolen-card total, or loss figure established in the reporting cited here. The dates describe reported activity and publication chronology, not the scale of impact.
#1 Best Overall

- 1. 【Multi-Functional USB-C Hub & Security】** Upgraded design features a built-in **USB-C pass-through charging and data port**. Unlike basic fingerprint scanners, this allows you to simultaneously use your fingerprint login while keeping your USB-C port free for charging your laptop or connecting a wireless mouse/keyboard. Perfect for modern laptops with limited ports.
- 2. 【Premium Aluminum Build & Portability】** Crafted from a **durable aluminum alloy** casing, this scanner is built to withstand the rigors of daily travel and desk life. Included **3M adhesive backing** allows you to securely mount it to your laptop lid or desk, ensuring it stays put in your bag and is always ready for instant access.
- 3. 【Instant Windows Hello Login (<1 Sec)】** Experience **password-less login in under one second**. With full support for **Windows 10/11 and Windows Hello**, this biometric reader provides seamless, secure access to your device, apps, and websites. Just a touch and you're in—no more typing complex passwords in coffee shops or airports.
- 4. 【360° Touch & Data Pass-Through】** Equipped with **360-degree capacitive touch** technology, it reads your fingerprint accurately from any angle. The upgraded USB-C port supports **data synchronization**, allowing you to connect and read a flash drive or external hard drive through the scanner without any loss in speed.
- 5. 【Universal Compatibility for On-the-Go Pros】** Designed for modern hybrid workers. Simply plug-and-play on any **Windows 10/11 laptop or PC** with a USB-C port. No complicated setup required. The compact size and detachable cable (with the adhesive mount) make it the ideal security companion for business travel and hot-desking.
How the reported attacks worked
Entry through vulnerable Telerik software
BlackBerry’s 2023 account said attackers exploited CVE-2019-18935, a .NET deserialization vulnerability in Progress Telerik UI for ASP.NET AJAX, to execute code remotely on targeted servers. This vulnerability was not exclusive to Silent Skimmer: CISA, the FBI, and MS-ISAC separately documented its exploitation by multiple actors on a U.S. government IIS server. See the joint CISA advisory.
In its later account of a potentially related incident, Unit 42 also described attempted exploitation of CVE-2017-11317 alongside CVE-2019-18935. The overlap is part of the basis for linking the activity, not proof that the incidents had the same operator.
Rank #2

- 📱 QR CODE SETUP GUIDE: Scan the QR code on the packaging to access the setup page with Windows drivers and installation instructions. The package includes the main item and a Japanese manual. On the website, tap the 🌐 World icon to switch to English, then scroll down to download the English manual.
- 🚀 INSTANT ACCESS: Login 10x faster than typing passwords - Under 1 second!
- 🛡️ HIGH-LEVEL SECURITY: Match-On-Chip technology = Your fingerprint NEVER leaves the device
- 🎯 WORKS EVERY TIME: 99.999% accuracy with 360° recognition - Touch from any angle!
- 💻 PLUG & PLAY MAGIC: Zero software installation - Works instantly with Windows 10/11 Hello
Post-exploitation access and tools
For the original campaign, BlackBerry described an attacker-controlled HTTP File Server hosted on a temporary virtual private server (VPS), where tools and post-exploitation payloads were stored. The VPS location reportedly varied with the victim’s geography. The toolset described in the report included downloader and remote-access scripts, web shells, exploits, Cobalt Strike beacons, and Fast Reverse Proxy (FRP). A PowerShell remote access trojan (RAT) could collect system information, transfer files, search for files, and connect to databases.
Payment-page skimming versus database theft
The original Silent Skimmer reporting described attackers injecting a web skimmer into checkout pages to collect billing and card details, with data exfiltration using Cloudflare. In this method, the payment page is the collection point: malicious code captures information as customers enter it.
Rank #3

- "Hot swappable Play Arrange with 1.5m Cablemail: Enjoy bother complimentary installation and flexible placement with a generous 1.5m USB cable, allowing accessible positioning for any computer arrange lacking driver demands"
- Tap Hook for Strengthened Security: Day night private data by simply poignant the transducer to instantly hook your computer
- "FIDO Licensed Multiple Function Security: Beyond Windowslogin, this reader serves as a FIDO U2F/FIDO2 security code for websites/apps like Two processor , providing immune 2FA security"
- "Sophisticated Controlled Breathing Ligheight: Board game with a smooth sensitive light club highlighting modifiable breathing consequences, reducing organ of sight strain while enhancing beauty"
- "Recognition & Immediate Loginumberebog: Knowledge extreme fast fingerprint scanning with recognition corner, facilitating secure passcode complimentary signin through Windowslogin for 10/11 PCs and laptops in under 1 second"
Unit 42 later investigated an incident involving a North American-headquartered multinational in late May 2024. In that case, a compiled Python executable connected to a victim database and wrote payment information to a CSV file. That is direct database collection, not checkout-page scraping. Unit 42 assessed the activity as possibly involving the same actor, citing infrastructure, tools, and tactics, techniques, and procedures (TTPs), while also noting differences in how payment data was collected. Its tracking label for the observed activity is CL-CRI-0941. Read the Unit 42 incident analysis for the technical account.
What is known about attribution and current activity
BlackBerry did not publicly identify the operator. Its report cited a Chinese-language developer repository, simplified Chinese in the PowerShell RAT, and an Asian command-and-control (C2) location as clues that the actor was likely Chinese-speaking and operated in Asia. Those indicators do not establish the operator’s identity, citizenship, physical location, or government sponsorship. Describing the activity as definitively conducted by Chinese nationals or a state-linked group goes beyond the evidence cited.
Rank #4

- Instant Windows Hello Integration: Quickly unlock your Windows 10/11 PC with your fingerprint. No need to type passwords—just one touch for fast and secure access. Works directly with Windows Hello, no extra software needed.
- Plug & Play Simplicity: No drivers needed for genuine Windows systems—just plug it in and it works. Automatically recognized in most cases (95%+ compatibility). Tip: Manual driver update may be required for non-genuine systems.
- USB Fingerprint Reader: A compact metal fingerprint scanner for PCs and laptops that makes logging in quick and easy—just plug it into any USB port and start using it. Its ultra-portable design fits perfectly in your laptop bag.
- Microsoft-Certified Security: Fully supports Windows Hello and the Windows Biometric Framework for safe and reliable login. Features high accuracy (0.001% false acceptance / 0.1% false rejection) to keep your data secure. Also supports password and file encryption for most websites.
- Multi-User Flexibility: Store up to 10 fingerprints—perfect for shared devices at home or work. Enjoy fast and smooth access with lightning-speed authentication in under 0.5 seconds.
Unit 42’s May 2024 incident was described as possibly involving the same actor, not as a confirmed identity match. The available sources establish related activity observed in May 2024; they do not establish whether Silent Skimmer or associated activity continued after then, or its status in 2026.
Independent reader supportYour contribution helps us test, update, and keep practical guides available for everyone.How payment businesses can reduce risk
Inventory and update Telerik installations
Identify internet-facing servers running Telerik UI for ASP.NET AJAX, then verify the installed versions and configuration. Progress Telerik’s guidance, updated January 5, 2021, said: “Only the upgrade to R1 2020 (2020.1.114) or later can prevent the known vulnerabilities at the time of writing.” That is a dated vendor recommendation, not a statement of the latest release today. Follow Progress Telerik’s current security guidance for your specific installation; Unit 42 also recommends upgrading to the latest available version.
Best Value
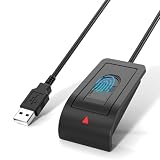
- Windows Hello Fingerprint Login: Designed for windows hello fingerprint reader compatibility on Windows 10/11 PCs, this usb fingerprint reader replaces passwords with fast one-touch biometric access. Enjoy convenient, secure login through your PC’s built-in Windows Hello system without extra software.
- Match-in-Sensor Security Protection: This fingerprint reader uses advanced biometric processing to verify fingerprints inside the sensor, helping protect your personal data. Your fingerprint information stays stored locally on your Windows device and is never uploaded or shared externally.
- Fast & Accurate Biometric Recognition: Built as a reliable fingerprint scanner for everyday computer security, this fingerprint reader for windows 11 provides quick recognition and stable performance. Access your PC, lock screens, and manage user accounts with a simple touch.
- Plug & Play Desktop Convenience: The usb fingerprint reader windows 11 solution connects easily through USB with no complicated drivers or third-party apps. The included 4ft cable provides flexible placement for desktops, workstations, and home office setups.
- Designed for Windows PC Security: This fingerprint scanner for pc supports password-free login through Windows Hello and works as a practical windows fingerprint reader for compatible systems. Compact design and angled sensor placement offer comfortable daily use.
Use advisory indicators as investigation leads
The CISA joint advisory provides technical details, indicators of compromise, and detection and mitigation recommendations for exploitation of CVE-2019-18935. Unit 42’s incident analysis includes observed paths, command examples, and detection queries for its later investigation. These are useful leads for checking relevant environments, not a complete detection recipe for every payment business or every variant of the activity.
If you suspect a compromise
Treat a possible intrusion as an incident-response matter, not merely a patching task. Investigate web-server activity and persistence, unexpected outbound connections, checkout-page scripts, and possible database access. The evidence differs by collection path: checkout-page injection points to reviewing payment-page code and related egress, while database theft calls for investigating server persistence and database activity. Preserve relevant logs and involve qualified incident responders when needed.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

