
Tesla raised its reported maximum bug-bounty award to $10,000 in August 2015 after security researchers Kevin Mahaffey and Marc Rogers presented findings about the Model S at DEF CON 23. The reported demonstration began with physical access to the car; it was not a remote takeover of a moving vehicle. The $10,000 figure was a program ceiling, not a confirmed payment to either researcher.
How Tesla’s bounty changed in 2015
| Date and stage | Scope or reported terms | What the figure means |
|---|---|---|
| June 2015 launch | Tesla’s Bugcrowd-administered program covered selected company web properties. Infosecurity Magazine reported awards of $25–$1,000, with amounts varying by vulnerability category. | These were reported initial-program terms, not current verified rates. Infosecurity Magazine, June 5, 2015 |
| August 2015 increase | After the Model S findings were presented at DEF CON 23, reports said Tesla increased the maximum to $10,000 for serious vulnerabilities. | This was the maximum available for qualifying findings, not evidence of a specific award. SecurityWeek, August 10, 2015; The Register, August 9, 2015 |
The initial program’s reported category ranges included $200–$500 for cross-site scripting, $100–$500 for cross-site request forgery, $500–$1,000 for SQL vulnerabilities, $1,000 for command injection, $100–$300 for business-logic issues, $500 for horizontal privilege escalation, and $500–$1,000 for vertical privilege escalation. Infosecurity Magazine reported those figures as part of the June 2015 web-property program; they should not be read as a current Tesla rate card.
What Mahaffey and Rogers reportedly found
SecurityWeek identified the researchers as Lookout co-founder and CTO Kevin Mahaffey and Cloudflare researcher Marc Rogers, and reported six vulnerabilities. Its account said the researchers had initial physical access to the Model S and could control infotainment functions, including actions normally available through the touchscreen or mobile app: opening or closing the trunks, locking or unlocking doors, and starting or stopping the car.
The reported issues also included weaknesses involving the WebKit-based browser, outdated HTTP and DNS proxy services on the internal network, X11 display systems without access control, and weak passwords in an encrypted instrument-cluster password file. SecurityWeek said the researchers found no private keys in the firmware bundle. Those details describe the 2015 report and its access conditions; they do not establish that Mahaffey and Rogers remotely controlled a moving car.
Recommended Free Tools
#1 Best Overall

- Compatible Key: This Tesla key fob cover fits select vehicle-shaped key fobs for Model 3, Model Y and Model S and should be matched by key shape
- Flexible TPU Fit: This Tesla key case uses lightweight flexible TPU to fit closely around the compatible key while providing a comfortable grip
- Functional Design: These Tesla accessories keep the original control areas identifiable and maintain access to the key attachment point
- Everyday Coverage: This Tesla key cover helps reduce scratches scuffs dust and minor bumps on the covered key surface during regular use
- Metal Keychain: This Tesla keychain features a leather-style accent for convenient attachment to a purse bag belt loop or existing key ring
Why the $10,000 figure needs context
The increase followed disclosure of serious vehicle-security findings and their public presentation at DEF CON 23. The Register reported that Tesla CTO JB Straubel announced the higher maximum. SecurityWeek described awards up to that amount for serious findings such as SQL injection, command injection, and vertical privilege escalation.
- A maximum is not a personal payout. The available reporting does not establish how much, if anything, Tesla paid Mahaffey or Rogers.
- The original scope was narrower. The June launch concerned selected Tesla web properties; the Model S findings and later statements about vehicle reporting should not be collapsed into one unchanged program scope.
- The 2015 demonstration was not the later remote-attack story. Its reported starting condition was physical access and its described impact centered on vehicle infotainment and connected controls.
How Tesla reportedly responded—and what happened later
SecurityWeek reported that Tesla delivered an over-the-air update to every Model S within two weeks of notification, addressing some of the disclosed vulnerabilities. That timeline is the publication’s account of the 2015 response.
Rank #2

- PRECISE FIT FOR MODEL 3/Y/S: This Tesla key fob cover is precision-molded to fit Tesla Model 3, Model Y, and Model S perfectly, with accurate cutouts for lock, unlock, frunk, and trunk buttons without removing the case
- FLEXIBLE TPU: Crafted from durable, flexible TPU, this Tesla key case helps reduce visible scratches, dust, and everyday scuffs while adding minimal bulk to your fob
- SLIM & SIGNAL-FRIENDLY: This Tesla key cover maintains an ultra-thin profile that is designed to allow normal keyless entry and remote command use
- PREMIUM LEATHER KEYCHAIN: Includes a sturdy metal chain with a leather accent - a stylish Tesla keychain that clips securely to your bag, belt loop, or backpack for quick and easy access
- COMPLETE PROTECTION SET: Combining a protective case and a matching chain, this Tesla accessories set offers all-in-one convenience, making it a practical choice for daily use or as a gift
A separate incident in 2016 involved Keen Security Lab, not the Mahaffey-Rogers DEF CON research. In a statement quoted by TechCrunch on September 20, 2016, Tesla said: “Within just 10 days of receiving this report, Tesla has already deployed an over-the-air software update (v7.1, 2.36.31) that addresses the potential security issues.” TechCrunch described conditions involving browser use and physical proximity to a malicious Wi-Fi hotspot. The 10-day claim belongs to that separate case, not the 2015 Model S fixes. TechCrunch, September 20, 2016
Independent reader supportYour contribution helps us test, update, and keep practical guides available for everyone.How to report a Tesla product-security issue today
Tesla’s product-security page, accessed October 4, 2026, directs vehicle and energy-product vulnerability reports to VulnerabilityReporting@tesla.com and describes Bugcrowd as its rewards platform. It also describes registration for pre-approved good-faith researchers and research-registered vehicles. The page does not state a current dollar maximum, so the 2015 $10,000 ceiling should not be treated as a present-day offer. Tesla Product Security
Do these 3 things before closing this tab:
1Clear out junk files and repair common Windows errors2Fix the driver behind crashes, sound loss and screen glitches3Repair Windows errors before they cause bigger problemsQuick Recap
Rank #4
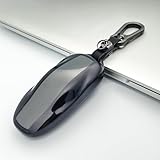
- Premium Material Construction: The Tesla key fob cover is made of waterproof TPU material, soft and easy to clean. The keychain is made of zinc alloy and leather, durable and beautiful. The ring is made of metal
- Vehicle Compatibility: This key holder case is designed specifically for Tesla Model S vehicles
- Important Product Notice: This product is a key cover only. The key fob is not included with your purchase
- Signal Protection and Durability: Key's signal will not be affected. Fobs are expensive so you need these holders to protect them from other things in your pocket. With these key covers, you will find that your key fobs are still very new after a long time
- Complete Package Contents: 1 Key Cover, 1 Keychain, 1 Ring included in the package
Rank #3

- 𝗕𝘂𝗶𝗹𝘁 𝗳𝗿𝗼𝗺 𝗚𝗲𝗻𝘂𝗶𝗻𝗲 𝗢𝗘𝗠 𝗞𝗲𝘆 𝗖𝗮𝗿𝗱 𝗖𝗼𝗿𝗲 – 𝗨𝗻𝗰𝗼𝗽𝘆𝗮𝗯𝗹𝗲 & 𝗦𝗲𝗰𝘂𝗿𝗲: No cloning. No hacking. No security gaps. The inner chip is identical to your Tesla key card, making this key impossible to duplicate. Drive with total peace of mind.
- 𝗧𝗮𝗽 𝗕-𝗣𝗶𝗹𝗹𝗮𝗿 𝘁𝗼 𝗟𝗼𝗰𝗸/𝗨𝗻𝗹𝗼𝗰𝗸 – 𝗦𝗮𝗺𝗲 𝗮𝘀 𝗢𝗿𝗶𝗴𝗶𝗻𝗮𝗹 𝗖𝗮𝗿𝗱: No buttons to press. Just tap the B-pillar – instant lock or unlock. Sensor recognition is lightning fast. Works exactly like your factory key card, without the fragile plastic.
- 𝗨𝗹𝘁𝗿𝗮-𝗟𝗶𝗴𝗵𝘁𝘄𝗲𝗶𝗴𝗵𝘁 & 𝗣𝗼𝗰𝗸𝗲𝘁-𝗥𝗲𝗮𝗱𝘆 – 𝟬.𝟴𝟭 𝗼𝘇: You’ll barely feel it in your pocket. No bulky fob, no cracked cards. At just 0.81 oz, this key disappears into your daily carry – ideal for minimalists and Tesla owners – daily commuting, family sharing, valet parking, and emergency key when phone/Blueetooth fails.
- 𝟭𝟬+ 𝗣𝗼𝗹𝗶𝘀𝗵𝗶𝗻𝗴 𝗣𝗿𝗼𝗰𝗲𝘀𝘀𝗲𝘀 – 𝗦𝗹𝗲𝗲𝗸 & 𝗦𝗺𝗼𝗼𝘁𝗵 𝗙𝗲𝗲𝗹: Precision-polished through over 10 steps. A stunning, smooth finish that feels natural in your hand and slides easily into any pocket or bag.
- 𝗦𝗶𝗺𝗽𝗹𝗲 𝟰-𝗦𝘁𝗲𝗽 𝗗𝗜𝗬 𝗣𝗮𝗶𝗿𝗶𝗻𝗴 – 𝗡𝗼 𝗗𝗲𝗮𝗹𝗲𝗿 𝗡𝗲𝗲𝗱𝗲𝗱: Pair in under 60 seconds: Controls > Locks > Keys > “+”. Tap on cup holder reader, then scan an already authenticated key. Done. No expensive programming.
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

