
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
No: VMware said on February 6, 2023, that it had found no evidence an unknown zero-day vulnerability was being used to spread the ESXiArgs ransomware. The evidence available at the time instead pointed to known vulnerabilities and outdated, unpatched, or unsupported ESXi hosts. Contemporaneous reporting named CVE-2021-21974, a vulnerability VMware had patched in February 2021.
Was ESXiArgs a zero-day?
VMware’s Security Response Center said on February 6, 2023: “VMware has not found evidence that suggests an unknown vulnerability (0-day) is being used to propagate the ransomware used in these recent attacks.” VMware’s ESXiArgs Q&A also said the attack did not exploit a new vulnerability.


That conclusion describes what VMware had found at that time; it does not mean every technical detail of every incident was known. But the available evidence did not support calling ESXiArgs a zero-day campaign. VMware instead pointed to reports involving end-of-general-support or outdated products and vulnerabilities already addressed in its security advisories.
What vulnerability was linked to the attacks?
CVE-2021-21974
SecurityWeek’s February 7, 2023 report identified CVE-2021-21974 as the vulnerability exploited in the campaign. It is a high-severity remote-code-execution flaw in ESXi that VMware patched in February 2021. This identification comes from contemporaneous secondary reporting; VMware’s statement and the CISA/FBI advisory support the broader conclusion that the attacks involved known vulnerabilities, rather than establishing that every compromised host was breached through this specific CVE.
Do these 3 things before closing this tab:
1Scan for outdated or missing drivers - takes under a minute2Repair Windows errors before they cause bigger problems3Fix the driver behind crashes, sound loss and screen glitchesWhy unpatched and end-of-life hosts mattered
The February 2023 joint advisory from the Cybersecurity and Infrastructure Security Agency (CISA) and the FBI said malicious actors may have exploited known vulnerabilities against unpatched, out-of-service, or out-of-date ESXi software. An ESXi host that has not received the applicable security fixes remains exposed to flaws those updates addressed. A host that has reached end of support may also lack a supported path to current security fixes.
What ESXiArgs did to virtual machines
The CISA/FBI advisory described ESXiArgs as ransomware targeting VMware ESXi servers. It reported that actors had compromised more than 3,800 servers globally in its February 2023 advisory. The malware encrypted virtual-machine configuration files, which could prevent affected VMs from being used, while leaving flat files unencrypted.
Rank #2
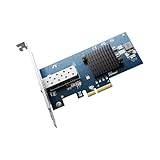
- GENUINE INTEL 82599EN, THE X520-DA1 SILICON: Sustained 10 Gigabit throughput for NAS transfers, VM migration and iSCSI storage; the link also steps down to 2.5G, 1G and 100M for a slower switch port
- NO VENDOR LOCK ON THE SFP+ CAGE: Third-party DAC twinax, AOC, 10GBASE-SR multimode and 10GBASE-LR single-mode optics all link up, unlike Intel-branded cards that reject modules they do not recognize
- PLUG AND PLAY ON PROXMOX, TRUENAS, UNRAID AND ESXI: Also detected by QNAP, Synology, Ubuntu, Debian and CentOS with no driver step; on Windows install the Intel Ethernet Adapter Complete Driver Pack
- ONLY FOUR PCIe LANES, BOTH BRACKETS IN THE BOX: Seats in any x4, x8 or x16 slot, leaving the rest of the board free; full-height and low-profile brackets both ship, for ATX towers, 1U and 2U racks, mini-ITX
- AIRFLOW, LIKE ANY 10G CARD: The passive heatsink runs warm by design, so give it case airflow or clip a small fan to it in a silent build; jumbo frames to 9KB and checksum offload run in hardware
That distinction created a limited possibility of recovery: in some cases, surviving flat files could be used to reconstruct encrypted configuration files. It did not mean the virtual-machine data was decrypted, that every VM could be restored, or that a reconstruction attempt would succeed.
What to do if an ESXi host may be vulnerable or compromised
1. Remove public exposure and restrict management access
Do not leave ESXi management interfaces directly reachable from the public Internet. Restrict management access to trusted administrative networks and tightly control which accounts and systems can reach the host. If compromise is suspected, involve your incident-response team before making changes that could destroy evidence or affect recovery.
Quick wins for a faster PC:
Scan for outdated or missing drivers - takes under a minuteDriver Scan →Repair Windows errors before they cause bigger problemsFix Now →2. Identify the version and support status
Determine the ESXi version, installed patches, and whether the release remains supported. VMware’s 2023 guidance was to upgrade to the latest available supported vSphere components to address disclosed vulnerabilities. An end-of-life host should not be treated as adequately secured simply because its configuration has not changed; plan migration to a supported release.
3. Apply applicable updates and review OpenSLP
Install the updates applicable to the specific ESXi release and follow VMware’s security guidance. VMware recommended disabling the OpenSLP service when it is not needed. In VMware’s 2023 guidance, OpenSLP was disabled by default in ESXi 7.0 U2c and later, and ESXi 8.0 GA and later; older or differently configured hosts may require an explicit configuration review.
Rank #4

- Note: Compatible with low-profile bracket only. Included full-height bracket is not compatible — please disregard.
- Controller: Realtek RTL8126 controller, equipped with RealWoW technology, supports wake-up and diagnostics, enhancing data stability, Scan the QR code on the NIC to download and install the driver.
- Interface: PCIe x1 lane, operable in PCIe X1, X4, X8 and X16 slots, not for PCI slots.
- System: Windows 8/10/11, Windows Server 2016/2019/2022, CentOS7/8/9, VMware ESXi 6, Ubuntu20/22, FreeBSD 13/14.
- Protocol: PXE, DPDK, WOL, iSCSI, Jumbo Frames, Auto MDIX, IEEE 802.1Q VLAN tagging, IEEE802.3bz (2.5G/5G BASE-T), Full Duplex flow control (IEEE 802.3x), NOT support FCoE.
4. Strengthen authentication and hardening
Follow vSphere security-hardening guidance, use multifactor authentication where supported for administrative access, and limit privileges to the people and services that require them. Patch status alone does not protect a management plane that is broadly reachable or weakly controlled.
5. Preserve backups and coordinate recovery
Keep offline backups of critical VM data and configuration. If an incident has occurred, preserve relevant evidence and coordinate recovery with incident-response personnel rather than assuming a reconstruction tool will restore the environment.
The Tool Desk
Outbyte PC Repair FREERepair Windows errors before they cause bigger problemsFix Now →Outbyte Driver Updater FREEFix the driver behind crashes, sound loss and screen glitchesFind Drivers →Can the CISA ESXiArgs-Recover script restore a server?
CISA released the open-source ESXiArgs-Recover script to automate attempts to reconstruct encrypted VM configuration files when the necessary flat files remained available. It is a recovery aid, not a decryptor and not a guarantee of restoration. Whether it can help depends on what files survived and the condition of the affected host. Use it as part of a supervised incident-response and recovery process, and retain backups as the primary recovery resource where available.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

