
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
XE Group’s activity has evolved from stealing payment-card data to targeting organizations through supply-chain software. In a VeraCore intrusion, investigators traced access from 2020 through renewed activity in 2023 and November 2024, when the group used webshells and exploited two previously unknown vulnerabilities.
The case is notable not only for the move to zero-day exploitation, but for the long-lived access and the uncertainty around what the attackers ultimately intended to do with it.
What is XE Group?
XE Group is a cybercriminal operation active since at least 2013. Earlier activity focused on e-commerce platforms, where the group used webshells and credit-card skimmers to steal payment data. Its later VeraCore operation targeted software used in warehouse management and order fulfillment, systems that can sit at the intersection of manufacturing, distribution, fulfillment, and retail.
That marks a change in the group’s observed targets and methods: from collecting payment data directly to gaining access to operational environments and their information. It does not, by itself, establish that every later operation had the same motive.
Quick wins for a faster PC:
Repair Windows errors before they cause bigger problemsFix Now →Scan for outdated or missing drivers - takes under a minuteDriver Scan →Clear out junk files and repair common Windows errorsFree Scan →#1 Best Overall

- STYLISHLY SMALL, SLIM & DISCREET: Measuring just 3 1/8" x 4 7/16", our RFID front pocket wallet is designed to be super thin and exceptionally slim. Its modern, minimalist profile fits perfectly in your pocket, purse, or travel pack without adding bulk.
- SURPRISINGLY SPACIOUS: Though slim, it features 8 slots to easily organize your essentials. Comfortably holds your driver's license, credit cards, debit cards, and membership cards, keeping everything you need right at your fingertips.
- ADVANCED RFID BLOCKING: Our slim wallets for men and women are outfitted with advanced RFID SECURE Technology. They block electronic signals to keep your identity protected while you travel, shop, or explore, safeguarding you from digital theft.
- DURABLE & STYLISH FAUX LEATHER: Crafted from premium synthetic leather, this minimalist wallet sleeve combines a luxurious look and feel with everyday functionality. Its durable construction is designed to withstand the rigors of daily use, travel, and shopping.
- THE PERFECT UNISEX GIFT: With its sleek design and practical security features, this wallet is a popular choice for both men and women. It arrives ready for gifting, making it an ideal present for the frequent traveler, minimalist, or anyone in your life!
How did the operation evolve?
| Period | Reported activity |
|---|---|
| 2013 onward | XE Group was identified targeting e-commerce platforms with credit-card skimmers. Earlier campaigns exploited known weaknesses, including Telerik UI for ASP.NET, and installed webshells to steal payment data. |
| 2020 | In the VeraCore environment, attackers used SQL injection to obtain valid credentials, then exploited an upload-validation flaw to place a webshell on an IIS server. They also used obfuscated Transact-SQL to extract database credentials. |
| 2023 | Investigators observed the group return to the environment and interact with a newer webshell, retrieving configuration files and browsing application directories. |
| November 2024 | An endpoint-detection system identified activity through a webshell. The attackers uploaded another ASPXSpy variant, attempted remote-system access, performed reconnaissance, and used obfuscated PowerShell to load a remote-access payload. |
| February 2025 | CyberScoop published an account based on a joint investigation by Intezer and Solis Security. |
| September 2025 | Virus Bulletin scheduled the researchers’ conference analysis, which highlighted long-lived access and little observed impact. |
Intezer and Solis Security traced the foothold to 2020 and documented later activity through November 2024—a span of more than four years. That timeline does not establish uninterrupted, hands-on control throughout; it shows that access planted earlier could be used again years later.
Which VeraCore vulnerabilities were involved?
The case involved two flaws later assigned CVE identifiers. The Hacker News reported the following CVSS scores in its 2025 coverage; scores describe severity, not whether a particular system is currently exposed.
Rank #2

- Ultra-thin: This wallet measures 4.3 x 3 x 0.5 inches and can hold at least 11 cards and 15-20 bills. Even when it's packed full, it's only 0.8 inches thick,It can perfectly conceal itself in your pocket without any noticeable bulge.
- Rfid Blocking: Our wallets are equipped with German Instiute Certified RFID Security technology, a unique metal composite, engineered specifically to block 13.56 MHz or higher RFID signals to protect the valuable information and privac.
- Lifetime After-sales Service: Regardless of the circumstances, if any GSOIAX brand wallet has a quality issue during your use, we promise to provide a full, unconditional, refund within 24 hours!
- Durable Surface: Crafted from premium 3-layer leather, our wallets outperform 2-layer alternatives in durability. Specially treated leather exterior delivers enhanced scratch resistance to guard against minor scuffs from everyday items like keys and buttons.
- Perfect Gifts For Him: This Money Clips Wallets for men comes in classy gift box package. It's a good idea to send the mens wallets as the gifts in birthday,anniversaries, Fathers Day,Valentine's Day,Christmas and other special occasions to someone you love.
| Vulnerability | Reported behavior | Reported severity and status |
|---|---|---|
| CVE-2024-57968 | An unrestricted upload flaw allowed a remote authenticated user to upload a dangerous file into an unintended folder. In the incident, the upload weakness was used to place an ASPX webshell. | The Hacker News listed CVSS 9.9. Advantive disabled the vulnerable upload feature in November 2024; subsequent reporting identified VeraCore 2024.4.2.1 as the fixed version. |
| CVE-2025-25181 | A SQL-injection flaw that could allow remote attackers to execute arbitrary SQL commands. In the reported chain, SQL injection was used to obtain credentials. | The Hacker News listed CVSS 5.8 and reported that no patch was publicly available at the time of its 2025 coverage. That historical statement does not establish the vulnerability’s current patch status. |
“Zero-day” describes the flaws as previously unknown when exploited, not their status today. Once identified, vulnerabilities may receive CVE numbers and fixes; defenders should check current vendor guidance and vulnerability records rather than assume a 2025 status remains accurate.
How did the intrusion work?
- Obtain credentials: SQL injection exposed valid credentials and database information.
- Authenticate and exploit the upload path: The attackers used credentials to access VeraCore, then abused the upload-validation weakness to place an ASPX webshell on the IIS server.
- Use the webshell for access and reconnaissance: The webshell supported file operations, access to configuration files, and exploration of application and network resources. Later activity included attempts to reach remote systems.
- Attempt to load a remote-access payload: Obfuscated PowerShell was used to reflectively load shellcode and attempt a Meterpreter or other remote-access connection. The reporting describes an attempted payload delivery, not proof that all intended actions succeeded.
The combination matters: SQL injection helped supply credentials, while the upload flaw provided a route to persistent code execution. A webshell can then act as a bridge between an application compromise and further discovery or access.
Rank #3

- RFID Blocking Technology: This credit card holder is made of aluminum shells and ABS plastic, designed with RFID-blocking technology to help protect your credit, ID, debit, and driver's license cards from unauthorized scanning
- Slim Compact: Slim and compact design measures 4.3 x 3 x 0.86 inches, ideal for front pockets or purses
- Card Organizer: With 7 accordion-style slots, this wallet can hold up to 10 standard credit cards or over 20 business cards
- Artistic Expression: Features a variety of artistic designs on the aluminum shell, inspired by famous paintings, flowers, and animals, to complement your personal style
- Thoughtful Gift Idea: Makes a thoughtful gift for any occasion, combining functionality and style
What tradecraft should defenders recognize?
- Dormant webshells: A webshell planted during an initial breach may be used again after a long gap, so a clean-looking recent activity window does not rule out an older foothold.
- Credential reuse: Credentials obtained from a database can turn an application weakness into authenticated access. Treat credentials stored in or exposed through the application as potentially compromised.
- Native-tool reconnaissance: Investigators reported use of Windows utilities such as
arpandnetstatto map network connections and nearby systems. These tools are legitimate, so context and unusual execution patterns matter. - PowerShell payload activity: Obfuscated PowerShell and reflective shellcode loading can be useful detection signals, especially when launched by a web-facing application process or from an unexpected account.
- Supply-chain exposure: Warehouse and fulfillment platforms connect operational workflows. Access to one organization’s system may reveal information or create opportunities affecting partners, though the report does not quantify downstream impact in this incident.
Was XE Group conducting espionage or ordinary cybercrime?
The available reporting does not settle the motive of the VeraCore operation. Virus Bulletin’s 2025 abstract describes multiple zero-day vulnerabilities and little evidence of monetization or destruction. It raises intelligence collection, failed lateral movement, and staging for a later operation as possibilities, not confirmed explanations.
XE Group’s earlier payment-card skimming is evidence of financial theft in its historical activity. It is not proof that the VeraCore intrusion was a financial crime, just as prolonged access and information collection do not prove espionage.
Rank #4
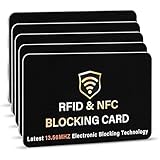
- SECURE YOUR WALLET FROM e-PICKPOCKETING: Prevent potential identity and financial theft through your contactless cards. This is the simplest and most effective prevention solution! Block RFID and NFC signals, protect your personal information, and enjoy peace of mind wherever your travels or business take you.
- JAMMING CHIP: An antenna and jamming chip makes up the main components of the card. The antenna will sense incoming radio waves and draw power for the chip to create a jamming signal. Lifetime usage as the card does not require battery.
- BROAD WORKING DISTANCE: With a 2.4” working distance, your entire wallet stays protected. The premium RFID blocking card helps secure cards within 1.2” on either side, providing reliable protection against electronic pickpocketing.
- ULTRA-THIN & COMPACT: At the size of a standard credit card and at only 0.03” thick, the card will fit into any wallet, purse or card case. Keep your wallet compact with no added bulk from this card. Best for travel, business, and everyday use.
- TEST THE CARD: Test the card is working at your local supermarket. At the self-service checkout machines, combine the card and a contactless card on the payment reader. Payment with the contactless card will be blocked and an error message should occur on the reader.
Is XE Group from Vietnam?
CyberScoop’s account says historical indicators—including Vietnamese-linked email addresses and the pseudonym “XeThanh”—suggest likely Vietnamese origins. This is an assessment, not definitive identification. The reporting also argues that the group’s limited efforts to conceal identity make state alignment less likely than it would be for actors using stricter operational security; that too is an assessment, not proof that no state relationship exists.
Independent reader supportYour contribution helps us test, update, and keep practical guides available for everyone.What should organizations do?
The incident demonstrates why defenders should investigate the application’s history, not only block the most recent activity. For VeraCore and other internet-facing business applications, prioritize these actions:
Free tools Windows power users keep installed
One-click scans. No signup required.
Best Value
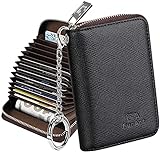
- Special Design: Multi-color optional and wear-proof classic business card holder looking.
- Plenty of Space: 16 card slots only measuring 4.1" x 3.0" x 1.1", including 13 credit card slots, 2 cash slots
- Protect Information Leakage: Prevents your vital information/cards from unnoticed scan with 2 outer layers RFID blocking materials.
- Extra Key Chain & Portable: Extra corns with key chain for your keys or lanyard. Portable use for shopping, traveling, etc.
- Great Gift: Practical compact wallet is the perfect gift. Give a thoughtful surprise to Men/Women on birthdays, holidays, celebrations, or any special occasion (e.g. Valentine's Day, Christmas, etc.).
- Inventory exposed instances. Identify internet-facing VeraCore deployments, their versions, and any upload features reachable from outside the organization.
- Apply vendor fixes and mitigations. For the upload flaw, reporting identifies VeraCore 2024.4.2.1 as fixed and says Advantive disabled the vulnerable feature in November 2024. Verify the currently supported remediation with the vendor. For CVE-2025-25181, check current vendor and vulnerability-database status; the cited 2025 report’s unpatched status may have changed.
- Rotate potentially exposed credentials. Replace credentials accessible through the affected application or database, and investigate whether they were reused elsewhere.
- Hunt IIS and application directories. Look for unexpected ASPX files, suspicious changes to upload locations, and webshell activity. Include old files and access patterns in the review, not just artifacts created during the latest alert window.
- Review historical logs and endpoint alerts. Search for earlier webshell requests, configuration-file access, database reconnaissance, and unusual outbound connections. The reported case included activity in 2020, 2023, and 2024.
- Monitor execution context. Alert on web application processes spawning PowerShell or native network utilities in unusual ways, and investigate Meterpreter-like or other unexpected remote-access behavior.
- Use endpoint detection and response. In the reported incident, EDR detected and mitigated most of the observed post-exploitation actions. It can help contain activity, but it does not replace patching, credential rotation, or historical hunting.
Public reporting does not state a victim count, total financial loss, or total number of compromised organizations. Those figures should not be inferred from the single described VeraCore environment.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

