
Recommended Free Tools
Password hashing lets an application verify a password without storing the original. It uses a password, a unique salt, and a deliberately costly password-hashing scheme to create a verifier. At sign-in, the application processes the submitted password with the same scheme and parameters, then compares the result with the saved verifier. If an attacker steals the password database, the salt and cost make guessing harder—but they do not make weak passwords impossible to crack.
What a password hash is—and is not
A password hash is a verifier, not encrypted text. Encryption is designed to be reversed with the right key; password hashing is designed to let a system check a candidate password without recovering the original. NIST describes password hashing schemes as taking a password, a salt, and a cost factor as inputs to generate a password hash. NIST SP 800-63B-4
The saved value is therefore not a copy of the password in a different format. When someone signs in, the application derives a value from the submitted password and compares it with the account’s stored verifier. A match is evidence that the candidate is correct; the verifier itself is not decrypted.
How password hashing works
When an account is created
- The application accepts the password and generates a salt for that password.
- It passes the password, salt, and selected cost parameters to a password-hashing scheme.
- It stores the resulting verifier along with the salt and enough algorithm and parameter information to verify the password later and upgrade the verifier when needed.
When the user signs in
- The application retrieves the account’s salt and stored scheme parameters.
- It runs the submitted password through the same scheme using those values.
- It compares the new result with the saved verifier. If they match, the password is accepted; the application has not decrypted the stored value.
The algorithm reference and cost factor matter as much as the derived value: without them, the service may not know how to verify an older account after its password-storage configuration changes. NIST recommends storing a reference to the scheme and its cost factor to support migration. NIST SP 800-63B-4
#1 Best Overall

- Pack of 1 padlock & 3 keys attached to removable circle rings , smooth functioning. Go to Ace Hardware,Home Depot,Locksmith if you need more keys alike.
- The padlocks can be used for gates,locker,toolboxes,ammo box,suitcase, garage,flight,Pelican Case,etc.
- Indoor and outdoor lock providing general security and protection for your valuables.
- International products have separate terms, are sold from abroad and may differ from local products, including fit, age ratings, and language of product, labeling or instructions.
What the salt and cost factor do
Salt: a different input for each password
A salt is a non-secret value stored with the verifier. It should be generated for each password and chosen to minimize collisions. NIST requires a salt of at least 32 bits and says the salt and resulting hash are stored for each password. Because accounts with the same password have different salts, their stored results differ; salts also frustrate precomputed lookup tables. The salt does not need to be hidden. NIST SP 800-63B-4
Cost factor: more work for every guess
A cost factor configures how much computation, memory, or both the hashing scheme uses. If a database is copied, an attacker can try password guesses offline. A deliberately costly scheme makes each guess more expensive. NIST states that the purpose is to raise the cost of guessing attacks, and advises increasing cost factors over time as computing performance improves, while keeping verifier performance acceptable. A salt and high cost slow guessing; neither guarantees that a weak or reused password will resist it. NIST SP 800-63B-4
Rank #2

- Heavy duty outdoor lock; Maximum security combination lock is best used as a gate lock, shed lock, or storage lock.Note: Measure your door's backset, cross bore and thickness to ensure you find the right fit.Control Method:Application
- Set your own four digit combination lock for easy combination recall; No combination change tool required, Shackle seal and hinged dial cover for superior weather resistance
- Padlock is constructed with a zinc body and reinforced body bumper for strength and reliability; Shackle seal and covered dials for superior weather protection; One directional dial feature for low light applications
- Tough-Cut octagonal boron steel shackle is 50% harder than hardened steel; Roller pin cylinder provides maximum pick and pry resistance
- 2-1/4 inch (57 millimeter) wide lock body; 3/8 inch (10 millimeter) diameter shackle with 1-1/2 inch (38 millimeter) length, 15/16 inch (24 millimeter) width; Extended shackle for application flexibility
Which password-hashing algorithm should an application use?
OWASP recommends Argon2id when available. If it is unavailable, its guidance lists scrypt; bcrypt is identified for legacy systems where Argon2 and scrypt are unavailable. OWASP also identifies PBKDF2 for cases that require FIPS-140-validated implementations. The example settings below are OWASP guidance, not universal guarantees or substitutes for measuring the service’s own verification latency and capacity. Check current guidance and maintained library behavior before deployment. OWASP Password Storage Cheat Sheet
| Scheme | When to consider it | OWASP example guidance | Implementation consideration |
|---|---|---|---|
| Argon2id | Preferred when available | At least 19 MiB memory, two iterations, and one degree of parallelism | Measure the configuration in the application environment and tune within current guidance. |
| scrypt | When Argon2id is unavailable | CPU/memory cost parameter 2^17, block size 8, parallelization 1 | Confirm that the maintained library supports the needed parameters. |
| bcrypt | Legacy systems where Argon2 and scrypt are unavailable | Work factor of at least 10 | OWASP notes a common 72-byte input limit; handle the chosen implementation’s limit deliberately. |
| PBKDF2 | Cases requiring FIPS-140-validated implementations | 600,000 or more iterations with HMAC-SHA-256 | Use a validated implementation when compliance requires it. |
These parameters can change as standards, libraries, and hardware evolve. Calibrate verification latency and resource use against expected traffic, follow applicable compliance requirements, and review settings periodically. Do not design a custom password-hashing algorithm. OWASP also cautions against using fast general-purpose hashes such as SHA-256 alone for password storage: their speed makes large numbers of guesses easier to test. OWASP Password Storage Cheat Sheet
Do these 3 things before closing this tab:
1Clear out junk files and repair common Windows errors2Scan for outdated or missing drivers - takes under a minute3Repair Windows errors before they cause bigger problemsRank #3
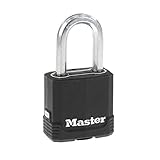
- Outdoor lock; Heavy duty padlock with key is best used for outdoor storage and fences, self-storage units & lockers, tools, job boxes and more.Note: Measure your door's backset, cross bore and thickness to ensure you find the right fit.Note: Measure your door's backset, cross bore and thickness to ensure you find the right fit.
- Key lock features Dual Armor construction: laminated steel lock body with weather resistant cover and Tough-Cut octagonal boron-carbide shackle is 50% harder than hardened steel
- 4-Pin cylinder and dual ball bearing locking for increased pick and pry resistance; Covered keyway and shackle for added weather protection
- 1-7/8 in. (48 mm) wide lock body; 5/16 in. (8 mm) diameter shackle with 1-1/2 in. (38 mm) length, 13/16 in. (21 mm) width; Extended shackle for application flexibility
- Includes one padlock with two keys
When a pepper adds another defense layer
A pepper is a secret used in a keyed operation alongside password hashing. Unlike a salt, it must not be stored in the password database. NIST says that when this additional key is used, it should be generated by an approved random bit generator and stored separately from the hashes, preferably in a hardware-protected area such as an HSM or TEE. NIST SP 800-63B-4
A pepper can add defense in depth if it is protected and managed properly. It also creates an operational dependency: losing or mishandling the key can affect verification. It is not a substitute for unique salts or a suitable password-hashing scheme.
Rank #4

- JOBSITE-TOUGH SECURITY: A layered laminated steel body with stacked steel plates helps resist prying and heavy abuse.
- HARDENED STEEL SHACKLE: Thick 1/4in (6.2mm) shackle helps resist cutting and sawing attempts.
- PROTECTIVE BUMPER BASE: Helps absorb knocks and reduces metal-on-metal scuffs on doors, hasps, and equipment.
- DUAL BALL-BEARING LOCKING: Ball-bearing mechanism helps resist pulling/prying and holds up under repeated use.
- MULTIPLE SHACKLE SIZES: Select the right fit for your hardware, with standard clearance or longer reach for thicker latches and chains.
Password-storage mistakes to avoid
- Storing passwords in plaintext: A database leak would expose the passwords directly. OWASP says passwords should never be stored in plaintext. OWASP Password Storage Cheat Sheet
- Using a fast hash alone: A general-purpose hash such as SHA-256 is designed to be fast, which helps attackers test guesses quickly. Use a password-hashing scheme designed to make guesses costly.
- Reusing one salt: Generate a salt for each password rather than applying one shared salt to every account.
- Treating the salt as a secret: Store it with the verifier. Protect a pepper separately if the design uses one.
- Leaving cost settings unchanged forever: Review them as computing performance and service capacity change.
- Ignoring library input limits: With bcrypt, account for the common 72-byte limit and ensure the application handles inputs consistently rather than silently truncating them.
What a database leak still means
Hashing limits what a stolen password database immediately reveals: the attacker does not simply read the original passwords from properly stored verifiers. But a copy of the database gives an attacker material for offline guessing, where attempts do not need to go through the legitimate sign-in service. Unique salts prevent straightforward reuse of precomputed results across accounts, and a suitable cost raises the effort per guess. Password strength still matters, and hashing is not a guarantee that every password will remain secret.
Quick Recap
Best Value

- 1-9/16 in. (40 mm) wide lock body; 1/4 in. (6.35 mm) diameter shackle with 1 in. (25 mm) length,1 in. (25 mm) width
- Key lock features a durable solid brass body and a hardened steel shackle for strength and security
- 4-pin cylinder and dual locking lever mechanism provides pick and pry resistance
- Indoor and outdoor lock:Lock with key is best used for residential gates , fences, sheds, workshops , garages, tool boxes and more
- Includes one padlock with two keys
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.
The Tool Desk
Outbyte PC Repair FREEClear out junk files and repair common Windows errorsFree Scan →Outbyte Driver Updater FREEFix the driver behind crashes, sound loss and screen glitchesFind Drivers →
