
iTechGuides is reader-supported. When you buy through links on our site, we may earn an affiliate commission. As an Amazon Associate I earn from qualifying purchases. Learn more
Network admission control (NAC) is the process of checking a user or device against network-access policy when it connects, then granting, restricting, quarantining, or denying access. A policy may consider identity alone or also the device’s type, configuration, and security posture. IEEE 802.1X is a common mechanism used to control network access, but NAC is the broader policy and enforcement approach—not another name for 802.1X.
What network admission control means
NAC makes an access decision at the point a user or device attempts to join a network. The decision can depend on credentials and, where configured, endpoint information such as operating-system characteristics or required security applications. The result is not necessarily all-or-nothing: policy may provide normal access, limit the device to selected resources, isolate it, direct it to remediation resources, or deny access.
Cisco describes NAC broadly as a security solution that enforces policy on devices and users connecting to a network. NIST’s glossary gives a narrower, context-specific definition, sourced to NIST SP 800-41 Rev. 1: a feature offered by some firewalls that allows access based on user credentials and health checks on a telework client. That glossary wording is one specific usage, not the only way the term is used. Cisco’s NAC guide and the NIST glossary entry illustrate the distinction.
Do these 3 things before closing this tab:
1Scan for outdated or missing drivers - takes under a minute2Repair Windows errors before they cause bigger problems3Fix the driver behind crashes, sound loss and screen glitchesHow NAC works with 802.1X
One common NAC design uses IEEE 802.1X, a standard for port-based network access control. In a typical arrangement, the connecting endpoint runs a supplicant; a switch or wireless access point acts as the authenticator; and an authentication service evaluates the request. The authenticator controls the network port and relays authentication exchanges. A RADIUS server, such as Microsoft Network Policy Server (NPS), can authenticate the request and apply authorization policy.
#1 Best Overall

- FAST, STABLE CONNECTION: Simply plug in and keep the smart outlet connected to your stable 2.4GHz network. Enhanced WiFi + Bluetooth connection is faster and more stable. Note: Don't support 5G WiFi.
- HAND-FREE VOICE CONTROL: Smart plugs that work with Alexa & Google Home Assistant. Just use simple voice commands to control your devices. Tips: please connect smart plug to the GHome app first—cannot link directly to Alexa/Google Home.
- SCHEDULES & AUTO-OFF TIMER: Easy to set timers and add schedules to connected devices circularly or randomly, making them work as scheduled like auto-off and auto-on.
- APP REMOTE & GROUP CONTROL: Use your smartphone to turn home appliances on and off anytime, anywhere. Set up a group for all outlet timer indoor, control them with just one tap, and manage multiple smart outlet plugs simultaneously.
- CERTIFIED SAFETY & COMPACT DESIGN: This wifi outlet plug combines assured reliability and a small size. It is ETL and FCC certified, rated at 10A, 1200W, and 120V, and its space-saving compact design fits perfectly into any corner of your home.
- The endpoint requests access. Its supplicant participates in the 802.1X authentication exchange.
- The authenticator relays the exchange. The switch or access point controls the port and forwards the request to the authentication service.
- The service evaluates policy. It checks the available credentials and other configured conditions, then returns an authorization decision.
- The network applies the decision. Depending on the design and policy, access may be permitted, limited, or denied; posture-based implementations may also isolate a noncompliant device or provide a path to remediation.
802.1X distinguishes a controlled port, used for protected network access, from an uncontrolled port that carries authentication and key-management traffic. The exact permitted traffic and response to a failed check depend on the implementation. See the IEEE 802.1X standard page and Microsoft’s guidance on 802.1X wireless access and NPS.
What NAC can check and do
NAC policy can extend beyond proving who is connecting. A deployment may assess endpoint posture, for example whether an operating system or required security application meets policy. Its enforcement options are configuration- and product-dependent; not every NAC system performs every check or offers every response.
Rank #2

- WIDE APPLICATION-- The board can be widely used for controlling industry equipment and electrical appliances, such as lights, air-conditioning or refrigerator at your home.
- REMOTELY CONTROLLING YOUR DEVICES-- You can feel to enjoy the remote controlling of your other devices with the Ethernet controller board. The board has integrated the web server, you can control electrical appliances via opening the page on your devices like computer, pad or smart phone when you are in office.
- WITH 16 CHANNEL RELAY-- This Ethernet controller board comes with 16-channel relay. So, you could control up to 16 devices remotely on LAN or WAN at the same time, meet your different requirements.
- RJ45 INTERFACE-- This module is equipped with RJ45 interface, via RJ45 telecommunications connection for network control. It features high stability and high precision, easy to install and operate.
- UNIQUE CONNECT CONTROL-- The module as server can accept client control when connect to remote server as client.
- Allow: provide the access permitted by policy.
- Restrict: limit access to selected network resources.
- Isolate or quarantine: separate a device from ordinary network access.
- Remediate: allow access to resources used to address a failed requirement, if the deployment supports that workflow.
- Deny: block access when policy requires it.
NIST’s NCCoE describes an implementation example involving posture checks and separation of noncompliant machines; it is an example of how such controls can be deployed, not a guarantee of behavior across NAC products. NIST SP 1800-26, Volume C.
The Tool Desk
Outbyte Driver Updater FREEScan for outdated or missing drivers - takes under a minuteDriver Scan →Outbyte PC Repair FREERepair Windows errors before they cause bigger problemsFix Now →NAC and 802.1X are not the same thing
802.1X standardizes port-based access control. NAC describes the wider policy and enforcement process that decides what connecting users and devices may access. A NAC deployment may use 802.1X, but the terms are not interchangeable; NAC policy can include identity, posture checks, and different enforcement outcomes.
Rank #3
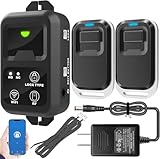
- ✅ The main feature of this kit is that it allows you to open the door simply by pressing the wireless RF remote instead of moving to the door physically when someone visits. The remote communicates with the wireless receiver, which can program up to 40 remotes, and it has a range of 160 feet.
- ✅ EASY USE: Transmits data to a cloud platform through the Wi-Fi Router, which enables you to remotely control the connected appliances via free Tuya Smart App. You can download the iOS version in App Store and the Android version in Google Play.
- ✅ SHARE CONTROL: Share control with your family and friends. Also you can DIY set this by yourself easy handling and can be activated immediately and stably.
- ✅ TIMING FUNCTION: Another feature available if to set timing schedules for the appliances, which can include countdown, scheduled on/off. It’s simple, giving you one less thing to worry about in your busy life.
- ✅ Attention: Specialized for the electric access control lock
NAC and ZTNA: different scopes of access
Network access control generally governs a user or device’s connection to a network. Zero trust network access (ZTNA) is commonly framed around identity-based access to particular applications. The approaches can complement one another: one governs network admission, while the other can govern access to specific applications. The actual scope depends on the product and deployment. Cisco’s NAC guide presents NAC and ZTNA as complementary approaches.
Independent reader supportYour contribution helps us test, update, and keep practical guides available for everyone.What a NAC deployment depends on
A working deployment is more than an access switch. With 802.1X, it depends on compatible network devices, an authentication service and its policy configuration, and correct network setup. Microsoft’s deployment guidance identifies compatible switches or wireless access points and NPS/RADIUS infrastructure as components to plan for. Microsoft Learn: plan an 802.1X authenticated wireless deployment.
Rank #4
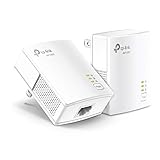
- 𝐄𝐱𝐭𝐞𝐧𝐝 𝐘𝐨𝐮𝐫 𝐄𝐭𝐡𝐞𝐫𝐧𝐞𝐭 𝐂𝐨𝐧𝐧𝐞𝐜𝐭𝐢𝐨𝐧 𝐓𝐡𝐫𝐨𝐮𝐠𝐡 𝐘𝐨𝐮𝐫 𝐄𝐥𝐞𝐜𝐭𝐫𝐢𝐜𝐚𝐥 𝐒𝐲𝐬𝐭𝐞𝐦 - This device is meant for for areas where thick walls block Ethernet connections, where routers or range extenders do not work. Compatible with all TP-Link powerline adapters.
- 𝐀𝐕𝟏𝟎𝟎𝟎 𝐒𝐩𝐞𝐞𝐝𝐬 𝐔𝐩 𝐭𝐨 𝟕𝟓𝟎 𝐅𝐞𝐞𝐭 - Powered by HomePlug AV2, delivers AV1000 powerline speeds through existing electrical wiring. Speeds cannot exceed your internet plan's limit and may be lower due to wiring quality, distance, and interference.
- Ideal for multi-story homes, basements, attics, and garages.
- 𝐂𝐡𝐞𝐜𝐤 𝐛𝐞𝐟𝐨𝐫𝐞 𝐲𝐨𝐮 𝐛𝐮𝐲 - Adapters must be plugged directly into wall outlets on the same electrical circuit. Does not work with power strips, surge protectors, or extension cords. Place away from large appliances, such as washing machines, refrigerators, and air conditioners.
- 𝐀𝐝𝐯𝐢𝐬𝐨𝐫𝐲 - Performance may be limited or blocked in homes with AFCI breakers, which are standard in many homes built after 2000. Powerline may also not work with routers or gateways using modified, open-source (e.g., DD-WRT), or non-standard firmware.
When evaluating a design, check these areas:
- Enforcement points: determine whether policy must cover wired, wireless, VPN, or remote access connections.
- Identity and authentication: confirm the supported methods and how they fit existing identity and authentication systems.
- Endpoint coverage: decide whether posture assessment is needed and how unmanaged, guest, IoT, or medical devices will be handled.
- Enforcement options: verify that the design supports the required restrictions, isolation, remediation, or denial actions.
- Compatibility: check the exact switch and access-point models, firmware, RADIUS infrastructure, and identity systems against the chosen design.
- Operations: define how policies, exceptions, guest access, and incident response will be managed.
Capabilities such as device profiling, posture assessment, guest management, incident response, and integrations are common considerations, but their availability varies by implementation. A switch is one possible enforcement component, not a complete NAC system by itself.
Quick Recap
Best Value

- HARDWARE PLUS SECURITY SERVICES: FortiGate-60F Firewall Appliance bundled with 1 year of FortiCare Premium and FortiGuard Unified Threat Protection.
- UNIFIED THREAT PROTECTION (UTP): Secures against advanced online threats with comprehensive web filtering and anti-botnet technologies.
- OPTIMIZED FOR MEDIUM-SIZED BUSINESSES: Tailored for businesses needing robust security without the infrastructure of larger enterprises.
- RELIABLE CUSTOMER SUPPORT: FortiCare Premium ensures high-quality support and service continuity.
- EFFECTIVE PROTECTION: Employs advanced filtering technologies to safeguard against sophisticated threats.
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

