
The Tool Desk
Outbyte PC Repair FREERepair Windows errors before they cause bigger problemsFix Now →Outbyte Driver Updater FREEScan for outdated or missing drivers - takes under a minuteDriver Scan →Android security-state libraries return evidence about particular properties—not a universal certificate that a phone, app, user, or transaction is safe. Google Play Integrity can report app recognition, Play entitlement, and device-integrity labels; Android key attestation concerns a key pair and its attestation chain. Each can inform a server’s risk decision, but neither answers every security question.
What Google Play Integrity checks
Play Integrity helps a backend assess whether a request comes from an app recognized by Google Play, whether that app has a Play entitlement, and whether the device meets specified integrity criteria. Its verdicts are separate claims: a positive result for one does not imply a positive result for the others.
App recognition: appIntegrity
PLAY_RECOGNIZEDmeans the app package and signing certificate match a version distributed by Google Play. It does not certify that the app’s code is secure or behaves benignly.UNRECOGNIZED_VERSIONmeans the package name or certificate does not match Google Play’s records.UNEVALUATEDmeans a prerequisite for evaluation was not met. It is not the same as a finding that the app is malicious.
Play entitlement: accountDetails.appLicensingVerdict
This field can return LICENSED, UNLICENSED, or UNEVALUATED. A licensed result indicates a Google Play entitlement, such as obtaining or updating the app through Google Play. It is an install-channel and entitlement signal, not proof of a person’s identity or a general fraud assessment. An unlicensed result can reflect sideloading or a lack of Play entitlement; it does not, by itself, establish harmful behavior. Google documents a caveat for some older devices: a user may remain licensed after uninstalling and later obtaining the same app elsewhere.
Device integrity: deviceIntegrity.deviceRecognitionVerdict
The device verdict can contain one or more labels, or no label if none of the criteria are met. MEETS_DEVICE_INTEGRITY denotes a genuine, certified Android device. For Android 13 and later, Google describes this label as including hardware-backed proof that the bootloader is locked and the loaded operating system is a certified manufacturer image.
#1 Best Overall

- 【Strong Adsorption】The inspiration of the silicone phone suction case comes from the adhesive force of the octopus. Each suction cup phone mount is 3.15 inches long and 2.17 inches wide, with 24 independent suction cups providing a stronger and more stable suction force, so you don't have to worry about your phone falling during use.
- 【Back of Phone Suction Grip】Remove the adhesive film on the phone suction cup and stick it on the phone case. You can then fix the phone on any smooth surface, which is very convenient. (The phone suction cup cannot be removed and reused after being attached to the phone case. It is recommended to attach it to a regular phone case, not a valuable one.)
- 【Widely Used】Our non-slip silicone phone sticky grip mount attaches to almost any flat phone case and make it compatible with common mobile phones such as iPhone and Android.You can shoot, watch videos or video calls in the kitchen, gym, dance studio, bathroom and other places.
- 【Capture the Wonderful Picture】Whether you are a TikTok creator or just like to share videos and photos, this phone suction cup can help you hands-free capture wonderful videos and photos for sharing with friends.
- 【Note】You can fix the phone suction cup on a smooth surface such as a mirror or glass. If necessary, wipe the suction cup with a damp cloth to obtain stronger suction. Before releasing your hand, make sure the phone is firmly fixed. (Not applicable to rough walls, wooden surfaces, and other uneven surfaces)
An absent label is not a diagnosis. Google lists possible explanations that include signs of attack such as hooking or root, an emulator that does not pass the checks, and other evaluation conditions. The result alone does not tell a developer which explanation applies.
Optional device labels
MEETS_BASIC_INTEGRITYis a weaker baseline. Its criteria allow a locked or unlocked bootloader and a verified or unverified boot state.MEETS_STRONG_INTEGRITYhas different requirements by Android version. On Android 13 and later, Google specifies a recent security update—within the last year across all partitions, including operating-system and vendor patches. On Android 12 and earlier, the label instead relies on hardware-backed proof of boot integrity and does not itself require a recent patch.
Check the Android SDK version before interpreting the stronger label. On Android 13 and later, Google says these optional labels are returned only for a licensed app.
Rank #2

- SUPERIOR COMFORT — Unlike traditional circular ear buds, the design of EarPods is defined by the geometry of the ear. Which makes them more comfortable for more people than any other ear bud–style headphones.
- HIGH-QUALITY AUDIO — The speakers inside EarPods have been engineered to maximize sound output and minimize sound loss, which means you get high-quality audio.
- BUILT-IN REMOTE — EarPods with USB-C plug also include a built-in remote that lets you adjust the volume, control the playback of music and video, and answer or end calls with a pinch of the cord.
- COMPATIBILITY — Works with all devices that have a USB-C port.
- INTEGRATED MICROPHONE — A built-in microphone precisely captures your voice while you’re on the phone, taking a FaceTime call, or summoning Siri — so you’re always heard loud and clear.
Optional environment and abuse signals
With the relevant configuration and prerequisites, Play Integrity can also provide signals about app access risk, Play Protect, recent device activity, and device recall. Availability is not universal: these checks are optional, can depend on Android version or eligibility, and may be unavailable when prerequisites fail.
- App access risk can flag other apps with permissions that could capture the screen, draw overlays, or control the device. It does not, by itself, prove that a specific app has abused those permissions.
- Play Protect can indicate protection status and the presence of known risky apps.
- Recent device activity provides approximate levels of integrity-token request volume for an app. It is an activity signal, not a device-wide security score.
- Device recall is a beta feature that can return app-defined device flags across reinstall or reset. Its beta status and eligibility matter when designing a control around it.
What Android key attestation verifies
Key attestation is a different mechanism from Play Integrity. It can increase confidence that an app-used key pair is stored in a hardware-backed keystore and provides encoded properties about that key and its attestation chain. It is not a complete inspection of the phone’s operating system, app, or user activity.
Free tools Windows power users keep installed
One-click scans. No signup required.
Rank #3

- Secure Hold: Our PopSockets adhesive phone grip gives your cell phone a secure, comfortable hold in hand to help prevent drops while texting, taking photos, or scrolling on the go. Designed to stick firmly to most phone cases and devices.
- Hands-Free Made Easy: Easily turn your PopSocket into a phone stand to prop up your phone anywhere, perfect for watching videos, video calls, or following recipes. A must-have phone holder that keeps your device secure and ready for anything.
- Compatibility: Works with all phones, tablets, and Kindles. Sticks best to smooth, hard plastic cases and may not adhere to silicone or textured cases. Easily swap your PopTop to change up your style.
- Black PopSockets: Simple, refined, and endlessly versatile. A timeless essential for any phone.
- Travel Must-Have for People On the Go: A must-have travel accessory for flights, flying, airports, air travel, airplanes, planes, international trips, cruises, and long travel days. Key gadget for your airport haul, travel accessories and must-haves.
Google’s Android Developers guidance, “Verify hardware-backed key pairs with key attestation,” calls for validation on a separate trusted server—not on a potentially compromised device. The relying party should verify the certificate signatures and trust anchor, check certificate revocation, and inspect the attestation extension. Only the first occurrence of the key-attestation extension in a chain should be trusted. A chain that has not been validated against a trusted anchor is not reliable evidence merely because it was returned by the device.
How the two mechanisms differ
| Question | Google Play Integrity | Android key attestation |
|---|---|---|
| What is primarily evaluated? | App recognition, Play entitlement, device labels, and configured optional signals | Properties of an app-used key and its certificate/attestation chain |
| Who interprets the evidence? | Google returns verdicts; the app backend validates request binding and applies policy | The relying party validates the chain, trust anchor, revocation status, and attestation extension, typically server-side |
| What limits the result? | Android version, Play state, configuration, and evaluation prerequisites | Hardware support and correct, trustworthy chain validation |
| What is a sound conclusion? | A risk signal for a protected action, not an all-clear | Evidence about key properties, not an all-device security score |
Neither mechanism necessarily answers broader device-posture questions. Google’s Android Enterprise guidance lists checks such as OS security patch level, encryption, management state, screen-lock quality, and developer-options state separately from Play Integrity.
Rank #4

- [360 ° Flexible Rotation Design] Comes with a rotatable lanyard ring that supports 360 ° free rotation, effectively solving the problem of twisted and tangled lanyards
- [Wide compatibility] The ultra-thin 0.02-inch design does not block the charging port at all, and both wired and wireless charging can be used directly without removing the pad. Compatible with most smartphones such as iPhone, compatible with various wristbands, lanyards, crossbody straps, and keychains
- [Durable and Portable Material] Premium rust-resistant stainless steel material with good flexibility, which not only avoids scratching the phone case, but also has excellent anti rust and anti fading performance
- [Multi scenario Practical] Paired with a lanyard or wristband, hands-free use can be achieved. The phone is within reach and not easily dropped, ideal for daily commuting and outdoor activities. Suitable for full coverage phone cases, does not support half coverage phone cases
- [Quality Service] If you find any damage or other issues with the product upon receipt, please contact us immediately. We will handle it quickly
Why a pass is not a security guarantee
A verdict is evidence about the property it was designed to evaluate, within its prerequisites and limits. For example, app recognition does not inspect whether the recognized app has a vulnerability; Play entitlement does not establish the account holder’s identity; and a device-integrity label does not certify every app or action on that device. Key attestation is narrower still: it concerns an attested key and the properties encoded in its extension.
Google’s Play Integrity overview says: “The Play Integrity API works best when used alongside other signals as part of your overall anti-abuse strategy and not as your sole anti-abuse mechanism.” A server should therefore treat a verdict as one input to a policy, not as a universal safe/unsafe switch. Google’s reviewed official documentation does not provide a quantified real-world false-positive rate, bypass rate, or overall accuracy figure for these checks.
PC Slower Than It Used to Be?
A free scan shows the junk files, broken settings and background clutter dragging Windows down - then fixes them in one click.Free scan · Windows 10 & 11Crashes, No Sound, or Screen Glitches?
Random freezes, missing sound and display glitches usually trace back to one bad driver. Find and replace yours safely.Free scan · under a minuteBest Value
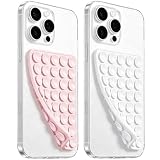
- 【PKYAA Double Sided Silicone Suction Phone Case Mount】PKYAA With Double Sided 40 Strong and Reliable individual suction cups, PKYAA provides a thicken and upgraded universal silicon suction mount for your phone.
- 【Friendly to Content Creators】If you are a content creator or an online influencer, you can create videos anywhere with this suction mount completely hands free with this silicone cell phone mount for cases.
- 【HANDS-FREE & Adhere to Mirrors】This Double Sided silicone suction phone case mount allows you to stick your phone to the mirror easily. No longer holding your phone in one hand to watch video tutorials while making up.
- 【Strong Grip on the Smooth Surface】You can easily hang your phone anywhere with a smooth surface. All you do is you clean off your phone and smooth surface. It is STURDY and it not only sticks to mirrors, it also sticks to windows, it sticks to refrigerators, tiles and other clean, flat surfaces.
- 【Press Down Firmly Every 30 Minutes】Use your palm or fingers to press the phone down firmly and check it's secure before letting go. Apply even pressure for a few seconds to allow the suction cup to adhere properly. To maintain the grip and prevent accidental falls, it's a good practice to periodically reapply pressure to the suction cup.
How to use the signals in an application
- Define the protected action and the risk. Decide what you need to reduce—such as abuse of a sensitive endpoint—before selecting a verdict. Do not collect a signal simply because it is available.
- Bind the verdict to the request. Google recommends request binding to reduce tampering and replay exposure: use
requestHashfor standard requests or a server-managed nonce for classic requests. Values placed in either field are visible in cleartext to the app and Google, so encrypt or hash sensitive data rather than putting it there directly. - Verify on the backend. Check the returned request details against the original request and the action’s freshness requirements before applying a policy. For key attestation, validate the certificate chain, trust anchor, revocation status, and extension on a trusted server.
- Start with observation. Google recommends reviewing audience telemetry before enforcing a new policy. This helps show how verdicts behave for the app’s actual users and reduces the risk of unexpectedly excluding legitimate users.
- Choose graduated responses. Use tiers suited to the action: for example, allow, ask for additional verification, limit a sensitive operation, or deny when evidence and risk justify it. Where possible, give users an actionable way to recover from a decision.
- Plan for unavailable evidence. Distinguish a negative verdict from an unevaluated or unavailable one. Missing prerequisites, account or store state, environment conditions, and technical issues can affect results. Define a deliberate fallback instead of silently treating every missing result as either safe or malicious.
- Prepare for operational changes. Account for API disruption and revoked device attestation keys in monitoring and incident plans. Standard Play Integrity requests use caching and Play-managed protections; classic requests trigger a fresh assessment, have higher latency and use more user data and battery, and require developers to mitigate replay themselves.
Google characterizes standard-request latency as a few hundred milliseconds on average and classic-request latency as a few seconds on average. These are descriptions of API behavior, not measurements of security effectiveness; actual timing can vary.
What to conclude from a result
- A recognized app is one whose package and signing certificate match Google Play’s distribution records—not one certified as vulnerability-free.
- A device label describes criteria for that label and Android version; it is not a verdict on every component or activity.
- A key-attestation chain supports claims about the attested key only when the relying party validates it correctly.
- A missing or unevaluated signal needs context; its absence alone does not establish compromise.
These definitions reflect Google’s Android Developers and Google Play documentation as checked on October 4, 2026. Verdict definitions and optional-signal availability can change, so implementations should follow the current documentation for their target Android versions.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

