
Do these 3 things before closing this tab:
1Clear out junk files and repair common Windows errors2Scan for outdated or missing drivers - takes under a minute3Repair Windows errors before they cause bigger problemsYes—Spring Boot can keep running through an AWS RDS password rotation, but changing an environment variable or secret alone does not update a DataSource or connection pool that is already running. Arrange for new database connections to obtain current credentials, either with the AWS Secrets Manager SQL Connection driver, an application-managed pool replacement, or IAM database authentication. Existing database sessions are separate: rotating a password does not reauthenticate them, and AWS says single-user rotation does not drop open connections.
Why a running Spring Boot app can keep using the old password
Spring Boot’s standard spring.datasource.* settings are used to configure a DataSource. In common Spring Boot JDBC and JPA applications, that DataSource uses HikariCP, which Boot prefers when it is present. Once the DataSource and pool have been created, changing an environment variable or the value stored in Secrets Manager does not, by itself, guarantee that Spring rebinds the setting or rebuilds the pool.
This distinction matters because a pool can continue serving already-open database sessions while failing to create replacement connections with an outdated password. A successful query on a borrowed connection is therefore not proof that the application’s next new connection will authenticate after rotation.
Spring Boot’s current SQL DataSource documentation is for 4.0, while its externalized-configuration documentation includes 3.4. The general distinction between startup configuration and a running DataSource applies to the approach here, but exact setup depends on the Boot version, JDBC driver, pool version, RDS engine, and deployment. If you define your own DataSource bean, it takes over from Boot’s DataSource auto-configuration.
Recommended Free Tools
#1 Best Overall

- 【Strong Adsorption】The inspiration of the silicone phone suction case comes from the adhesive force of the octopus. Each suction cup phone mount is 3.15 inches long and 2.17 inches wide, with 24 independent suction cups providing a stronger and more stable suction force, so you don't have to worry about your phone falling during use.
- 【Back of Phone Suction Grip】Remove the adhesive film on the phone suction cup and stick it on the phone case. You can then fix the phone on any smooth surface, which is very convenient. (The phone suction cup cannot be removed and reused after being attached to the phone case. It is recommended to attach it to a regular phone case, not a valuable one.)
- 【Widely Used】Our non-slip silicone phone sticky grip mount attaches to almost any flat phone case and make it compatible with common mobile phones such as iPhone and Android.You can shoot, watch videos or video calls in the kitchen, gym, dance studio, bathroom and other places.
- 【Capture the Wonderful Picture】Whether you are a TikTok creator or just like to share videos and photos, this phone suction cup can help you hands-free capture wonderful videos and photos for sharing with friends.
- 【Note】You can fix the phone suction cup on a smooth surface such as a mirror or glass. If necessary, wipe the suction cup with a damp cloth to obtain stronger suction. Before releasing your hand, make sure the phone is firmly fixed. (Not applicable to rough walls, wooden surfaces, and other uneven surfaces)
Choose how new connections will get valid credentials
| Approach | How new connections get credentials | Main trade-off |
|---|---|---|
| AWS Secrets Manager SQL Connection driver | The driver retrieves and caches credentials from a Secrets Manager secret; its documented default cache refresh is hourly and it also refreshes when the secret rotates. This does not reauthenticate an already-open database session. | Less custom refresh code, but verify engine and wrapped-driver support, pool behavior, permissions, networking, and endpoint configuration. |
| Application-managed refresh and pool replacement | Your application detects new credentials, creates and validates a replacement DataSource or pool, then directs new work to it while old work drains. | Provides lifecycle control but requires careful concurrency, shutdown, error handling, and monitoring. Spring does not prescribe one universal safe hot-swap recipe. |
| IAM database authentication | The application obtains an expiring IAM authentication token for a new connection instead of using a static database password. | Avoids static password rotation, but requires a supported engine, IAM permissions, token generation, and pool integration that accounts for token expiry. |
Use the Secrets Manager SQL Connection driver
This is a documented route when the chosen RDS engine and JDBC-driver combination is supported. It lets the connection path retrieve credentials from Secrets Manager rather than relying only on a password fixed in the application’s startup configuration. The hourly cache refresh is a documented default, not a promise that every connection in a pool is immediately replaced when a secret changes.
- Confirm compatibility. Check the driver’s current supported database engines and wrapped JDBC drivers against your RDS engine and the JDBC driver your application uses. Also verify the exact library release with your Spring Boot and pool versions; do not assume every combination is covered.
- Provide connection details. Configure the secret identifier and the ordinary JDBC connection details needed by the application. An RDS-managed master-password secret does not provide the database endpoint and port, so supply those separately.
- Grant narrowly scoped access. The runtime identity needs permission to retrieve the specific secret. If that secret uses a customer-managed KMS key, the identity may also need appropriate decrypt permission. Configure network access from the application to Secrets Manager and RDS; the required route depends on where the app runs.
- Verify pool behavior. Test that creation of a new physical connection uses refreshed credentials after rotation. Account for how the selected driver and pool interact with the driver’s credential cache, and do not assume a cache refresh changes credentials on existing sessions.
- Handle transient authentication failures. Use bounded retries with backoff when opening a connection, so a brief secret/database synchronization window does not cause an unbounded retry loop or prolonged request failure.
Replace the pool explicitly when you need lifecycle control
If the Secrets Manager driver does not fit your engine, driver, or pool setup, the alternative is application-managed refresh. Treat this as a deliberate DataSource lifecycle, not as an automatic Spring Boot feature and not as a blind password mutation on a live pool.
Rank #2

- SUPERIOR COMFORT — Unlike traditional circular ear buds, the design of EarPods is defined by the geometry of the ear. Which makes them more comfortable for more people than any other ear bud–style headphones.
- HIGH-QUALITY AUDIO — The speakers inside EarPods have been engineered to maximize sound output and minimize sound loss, which means you get high-quality audio.
- BUILT-IN REMOTE — EarPods with USB-C plug also include a built-in remote that lets you adjust the volume, control the playback of music and video, and answer or end calls with a pinch of the cord.
- COMPATIBILITY — Works with all devices that have a USB-C port.
- INTEGRATED MICROPHONE — A built-in microphone precisely captures your voice while you’re on the phone, taking a FaceTime call, or summoning Siri — so you’re always heard loud and clear.
- Read and detect a changed secret. Use an application component or deployment mechanism to learn when the credential version changes. Keep credentials out of source code and logs.
- Build a second DataSource or pool. Configure it with the new credentials while leaving the current pool available. Validate it by opening a real database connection before directing application work to it.
- Switch new work safely. Use a controlled indirection in your application to send new connection requests to the replacement pool. The swap must be safe for concurrent requests and transactions.
- Drain and close the old pool. Allow in-flight work to finish according to your application’s transaction and shutdown policy, then close the old pool. Define what happens if validation or the switch fails rather than discarding the only working pool.
- Observe the transition. Monitor connection-creation failures, pool health, database authentication errors, and the age of connections during rotation. Set limits on retry frequency and duration.
There is no universal safe instruction to edit credentials on an already-live HikariCP pool: behavior depends on the exact pool and integration. Validate your chosen refresh and replacement mechanism against the pool version you deploy.
Choose a rotation mode that fits availability and operations
| Rotation mode | What to plan for | Operational trade-off |
|---|---|---|
| Single-user | AWS documents a brief possible interval between changing the database password and updating the secret. The chance of denial is described as low, but connection attempts during the interval may fail; use bounded retries. | Simpler user management. Existing open connections are not dropped by rotation, while new connections use the new credentials after rotation. |
| Alternating-user | Maintain and validate the two-user and privilege arrangement required by the rotation strategy. | Offers another account path during updates, but adds user and permission management. AWS documents that RDS Proxy does not support alternating-user rotation. |
For RDS-managed master-password secrets, AWS sets rotation to every seven days by default; that schedule can be changed. The master account is generally not the right routine application identity: use a dedicated least-privilege database user for application access.
Rank #3

- Secure Hold: Our PopSockets adhesive phone grip gives your cell phone a secure, comfortable hold in hand to help prevent drops while texting, taking photos, or scrolling on the go. Designed to stick firmly to most phone cases and devices.
- Hands-Free Made Easy: Easily turn your PopSocket into a phone stand to prop up your phone anywhere, perfect for watching videos, video calls, or following recipes. A must-have phone holder that keeps your device secure and ready for anything.
- Compatibility: Works with all phones, tablets, and Kindles. Sticks best to smooth, hard plastic cases and may not adhere to silicone or textured cases. Easily swap your PopTop to change up your style.
- Black PopSockets: Simple, refined, and endlessly versatile. A timeless essential for any phone.
- Travel Must-Have for People On the Go: A must-have travel accessory for flights, flying, airports, air travel, airplanes, planes, international trips, cruises, and long travel days. Key gadget for your airport haul, travel accessories and must-haves.
Consider IAM database authentication instead of a rotating password
For supported RDS engines, IAM database authentication replaces the static password with a signed token used to authenticate a connection. The application must be able to generate a suitable token when establishing a connection, and the token expires. Configure the pool integration so token creation occurs at connection authentication time rather than treating one token as a permanent password for future connections. Check engine support, IAM policy, signing-region configuration, and the pool’s connection lifecycle for your deployment.
Independent reader supportYour contribution helps us test, update, and keep practical guides available for everyone.Validate the full rotation before relying on it
- Confirm the runtime role can retrieve the intended secret and, where applicable, decrypt it with the configured key.
- Verify application-to-Secrets-Manager and application-to-RDS connectivity from the actual runtime network.
- In a nonproduction environment, complete a real rotation and confirm that a newly created connection succeeds with the current credentials.
- Check what happens to in-flight transactions and old pooled sessions while new connections are being created.
- Exercise retry limits, pool recovery or replacement, monitoring, and rollback behavior.
- Test the failure path when Secrets Manager is temporarily unreachable, so the application responds predictably rather than creating an uncontrolled retry storm.
AWS’s guidance distinguishes existing and new connections: open sessions are not dropped by single-user rotation, and new connections use the new credentials after rotation. The application still needs a way to supply those credentials when it creates connections.
Quick Recap
Best Value
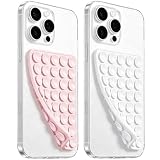
- 【PKYAA Double Sided Silicone Suction Phone Case Mount】PKYAA With Double Sided 40 Strong and Reliable individual suction cups, PKYAA provides a thicken and upgraded universal silicon suction mount for your phone.
- 【Friendly to Content Creators】If you are a content creator or an online influencer, you can create videos anywhere with this suction mount completely hands free with this silicone cell phone mount for cases.
- 【HANDS-FREE & Adhere to Mirrors】This Double Sided silicone suction phone case mount allows you to stick your phone to the mirror easily. No longer holding your phone in one hand to watch video tutorials while making up.
- 【Strong Grip on the Smooth Surface】You can easily hang your phone anywhere with a smooth surface. All you do is you clean off your phone and smooth surface. It is STURDY and it not only sticks to mirrors, it also sticks to windows, it sticks to refrigerators, tiles and other clean, flat surfaces.
- 【Press Down Firmly Every 30 Minutes】Use your palm or fingers to press the phone down firmly and check it's secure before letting go. Apply even pressure for a few seconds to allow the suction cup to adhere properly. To maintain the grip and prevent accidental falls, it's a good practice to periodically reapply pressure to the suction cup.
Rank #4

- [360 ° Flexible Rotation Design] Comes with a rotatable lanyard ring that supports 360 ° free rotation, effectively solving the problem of twisted and tangled lanyards
- [Wide compatibility] The ultra-thin 0.02-inch design does not block the charging port at all, and both wired and wireless charging can be used directly without removing the pad. Compatible with most smartphones such as iPhone, compatible with various wristbands, lanyards, crossbody straps, and keychains
- [Durable and Portable Material] Premium rust-resistant stainless steel material with good flexibility, which not only avoids scratching the phone case, but also has excellent anti rust and anti fading performance
- [Multi scenario Practical] Paired with a lanyard or wristband, hands-free use can be achieved. The phone is within reach and not easily dropped, ideal for daily commuting and outdoor activities. Suitable for full coverage phone cases, does not support half coverage phone cases
- [Quality Service] If you find any damage or other issues with the product upon receipt, please contact us immediately. We will handle it quickly
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

