
Outdated Drivers Are Slowing You Down
One free scan finds every outdated or missing driver and matches the right update for your exact hardware.Free scan · exact hardware matchWindows Errors? Fix Them Before They Spread
Repair common Windows errors and clear accumulated junk for a smoother, more stable PC - no reinstall needed.Free scan · no reinstalliTechGuides is reader-supported. When you buy through links on our site, we may earn an affiliate commission. As an Amazon Associate I earn from qualifying purchases. Learn more
To split-tunnel WireGuard over udp2raw, route only the destination networks you want through WireGuard, and keep the udp2raw server’s IP routed over your ordinary network connection. WireGuard handles the inner traffic routes; udp2raw carries WireGuard’s outer packets using a separate transport mode. Mixing up those two layers can send udp2raw into the tunnel it is supposed to keep alive.
Understand the two routing layers
Applications first create ordinary IP traffic for destinations such as a private subnet. WireGuard selects which peer should receive that traffic, encrypts it, and encapsulates it in UDP. udp2raw then transports those outer UDP packets between a local listener and a remote udp2raw server using a selected mode.
In this arrangement, the WireGuard client’s peer endpoint points to the local UDP listener. The udp2raw client targets the remote udp2raw server, whose udp2raw process forwards packets to the WireGuard UDP listener. The WireGuard project says its tunnel does not itself support TCP; it identifies udp2raw as an example of an upper obfuscation layer for UDP-to-TCP transformation. See WireGuard’s known limitations and udp2raw’s project documentation.
That distinction matters: split tunneling controls which inner destinations enter WireGuard. A separate route must ensure the outer udp2raw server address does not enter WireGuard.
#1 Best Overall

- 【AC1200 Dual-band Wireless Router】Simultaneous dual-band with wireless speed up to 300 Mbps (2.4GHz) + 867 Mbps (5GHz). 2.4GHz band can handles some simple tasks like emails or web browsing while bandwidth intensive tasks such as gaming or 4K video streaming can be handled by the 5GHz band.*Speed tests are conducted on a local network. Real-world speeds may differ depending on your network configuration.*
- 【Easy Setup】Please refer to the User Manual and the Unboxing & Setup video guide on Amazon for detailed setup instructions and methods for connecting to the Internet.
- 【Pocket-friendly】Lightweight design(145g) which designed for your next trip or adventure. Alongside its portable, compact design makes it easy to take with you on the go.
- 【Full Gigabit Ports】Gigabit Wireless Internet Router with 2 Gigabit LAN ports and 1 Gigabit WAN ports, ideal for lots of internet plan and allow you to connect your wired devices directly.
- 【Keep your Internet Safe】IPv6 supported. OpenVPN & WireGuard pre-installed, compatible with 30+ VPN service providers. Cloudflare encryption supported to protect the privacy.
Choose which destinations use WireGuard
WireGuard’s AllowedIPs participates in cryptokey routing. For outgoing traffic, destination addresses select the peer; for incoming traffic, source addresses are checked against that peer’s allowed prefixes. Put only the remote address ranges you intend to reach through the tunnel in the peer’s configuration. The exact configuration syntax and how routes are installed vary by operating system and WireGuard client.
For example, a peer intended to carry traffic for a particular private network should be associated with that network’s prefix, rather than an all-IPv4 route. AllowedIPs = 0.0.0.0/0 represents all IPv4 destinations, so it is not an IPv4 split-tunnel route. A full-tunnel policy may also include an all-IPv6 route; check the client’s settings and generated routes rather than assuming an IPv4 prefix covers IPv6.
Rank #2

- Please update the firmware upon initial setup of the router, as it greatly enhances the device's performance and ensures a superior user experience.*** 【WiFi 6 Standard with ultra-low latency】Wi-Fi 6 speeds up to 6 Gbps to let you enjoy smoother 4K streaming, gaming, video calls and more, DDR4 1GB / eMMC 8GB
- 【High Speed Gaming Router】Dominate with uninterrupted performance with the ultimate MT6000 gaming internet router, equipped with 8-stream Wi-Fi 6 technology, the Flint 2 delivers blazing speeds, ensuring a stable and high-speed connection during intense multiplayer battles.
- 【Rapid OpenVPN & Wireguard speed】Wireguard VPN and OpenVPN speeds up to 900Mbps and 880Mbps respectively, giving you complete control over your gaming, streaming and working bandwidth. Actual speed may differ depending on internet service provider, network environment, VPN server location, VPN service provider, etc.
- 【AdGuard Home Supported】Enabling the use of a DNS server for blocking unwanted tracking and offers a convenient web interface for filtering selected digital advertisements. Users can take full control of their online experience and enjoy a clutter-free browsing environment with ease.
- 【Mass device connectivity】Experience enhanced online connectivity with our higher storage capacity, catering to over a hundred devices and fulfilling the requirements of DIY users seeking to install additional plugins. Enjoy stable and reliable connections, ensuring seamless performance and accommodating a wide range of digital needs.
WireGuard’s technical paper explains destination selection and inbound source validation in its discussion of cryptokey routing. Use the documentation for your platform to confirm how the chosen prefixes translate into installed routes.
Keep the udp2raw server outside the tunnel
If a broad route or operating-system VPN policy sends the udp2raw server’s own address into WireGuard, the transport packets needed to sustain WireGuard can be captured by WireGuard itself. This routing loop can prevent the tunnel from connecting or cause it to stall.
Rank #3

- 【DUAL BAND AX TRAVEL ROUTER】Products with US, UK, EU Plug; Dual band network with wireless speed 574Mbps (2.4G)+2402Mbps (5G); 2.5G Multi-gigabit WAN port and a 1G gigabit LAN port; USB 3.0 port; Wi-Fi 6 offers more than double the total Wi-Fi speed with the MT3000 VPN Router.
- 【VPN CLIENT & SERVER】OpenVPN and WireGuard are pre-installed, compatible with 30+ VPN service providers (active subscription required). Simply log in to your existing VPN account with our portable wifi device, and Beryl AX automatically encrypts all network traffic within the connected network. Max. VPN speed of 150 Mbps (OpenVPN); 300 Mbps (WireGuard). *Speed tests are conducted on a local network. Real-world speeds may differ depending on your network configuration.*
- 【OpenWrt 21.02 FIRMWARE】The Beryl AX is a portable wifi box and mini router that runs on OpenWrt 21.02 firmware. It supports more than 5,000 ready-made plug-ins for customization. Simply browse, install, and manage packages with our no-code interface within Beryl AX's Admin Panel.
- 【PROTECT YOUR NETWORK SECURITY】Our pocket wifi, unlike other vulnerable portable wifi hotspot for travel purposes supports WPA3 protocol–Preventive measures against password brute-force attacks; DNS over HTTPS & DNS over TLS–Protecting domain name system traffic and preventing data eavesdropping from malicious parties; IPv6–Built-in authentication for privacy protection, eliminating the need for network address translation.
- 【VPN CASCADING AT EASE】Surpassing the mediocre performance of most VPN routers for home usage, the Beryl AX is capable of hosting a VPN server and VPN client at the same time within the same device, enabling users to remote access local network resources like Wi-Fi printers or local web servers, and accessing the public internet as a VPN client simultaneously.
Add a route exception so the udp2raw server IP continues through the physical interface and the ordinary gateway. udp2raw’s wiki documents a Linux route-exception pattern. Treat it as a pattern, not a copy-and-paste command: substitute the actual server IP and default gateway, and account for the interface and routing setup on your machine. If the server’s address changes, the exception may need updating.
After applying the exception, inspect the active route for the udp2raw server address and confirm it uses the normal gateway rather than the WireGuard interface. Also confirm that the intended private or remote destination prefixes still use WireGuard.
Rank #4
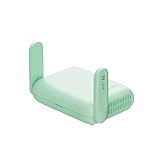
- 【DUAL BAND WIFI 7 TRAVEL ROUTER】Products with US, UK, EU, AU Plug; Dual band network with wireless speed 688Mbps (2.4G)+2882Mbps (5G); Dual 2.5G Ethernet Ports (1x WAN and 1x LAN Port); USB 3.0 port. Enjoy gaming and streaming across up to 120 devices.
- 【HIGH SPEED VPN CLIENT & SERVER】Max. VPN speed of 1100 Mbps (WireGuard); 1000 Mbps (OpenVPN-DCO). OpenVPN and WireGuard are pre-installed, compatible with 30+ VPN service providers (active subscription required). Simply log in to your existing account with our portable wifi device, and Beryl 7 automatically encrypts all network traffic within the connected network. *Speed tests are conducted on a local network. Real-world speeds may differ depending on your network configuration.*
- 【OpenWrt 21.02 FIRMWARE】The Beryl 7 (GL-MT3600BE) is a high-performance Wi-Fi 7 travel router, built with OpenWrt 21.02 (Kernel 5.4.281) for maximum customization and advanced networking capabilities. With 512MB storage, total customization with open-source freedom and flexible installation of OpenWrt plugins.
- 【PERFECT PORTABLE WIFI ROUTER FOR TRAVEL】The Beryl 7 is an ideal international wireless portable wifi travel router. With its mini size and travel-friendly features, the pocket Wi-Fi router is the perfect companion for travelers in need of a secure internet connectivity on the go. portable wi-fi for traveling, hotels or cruise ships.
- 【PROTECT YOUR NETWORK SECURITY】Our pocket wifi, unlike other vulnerable portable wifi hotspot devices for travel purposes supports WPA3 protocol–Preventive measures against password brute-force attacks; DNS over HTTPS & DNS over TLS–Protecting domain name system traffic and preventing data eavesdropping from malicious parties; IPv6–Built-in authentication for privacy protection, eliminating the need for network address translation.
Set up the udp2raw transport
udp2raw documents a client/server arrangement in which a local UDP listener forwards traffic to a server-side UDP service through a selected raw mode. Its sample commands require root privileges. The exact command line and WireGuard endpoint arrangement should be checked against the current project example and the operating system in use; the project’s wiki index links to examples but does not itself provide every configuration detail.
Do these 3 things before closing this tab:
1Clear out junk files and repair common Windows errors2Scan for outdated or missing drivers - takes under a minute3Repair Windows errors before they cause bigger problems- Decide which traffic belongs in the tunnel. Identify the remote destination prefixes, then configure the WireGuard peer so only those destinations select it.
- Start the remote udp2raw process. Configure it to forward to the WireGuard UDP listener on the server. Confirm that the chosen raw mode is allowed by the server’s network and firewall.
- Start the local udp2raw client. Configure its local UDP listener and point it at the remote udp2raw server. Review the project’s privilege requirements before running its examples.
- Point the WireGuard peer at the local listener. WireGuard should send its UDP endpoint traffic to the local udp2raw listener, not directly to the remote WireGuard listener.
- Protect the outer route. Add and verify a route exception for the udp2raw server IP through the ordinary gateway.
- Check routes and connectivity in layers. Verify the udp2raw server is reachable over the ordinary connection, then check that WireGuard can establish and that only the configured destination prefixes use it.
Choose a raw mode that fits the network
udp2raw documents FakeTCP, UDP, and ICMP modes. The available material does not establish one mode as universally best; the network’s filtering, client/server compatibility, privileges, and firewall behavior determine what is viable.
Best Value

- 【DUAL BAND WIFI 7 TRAVEL ROUTER】Products with US, UK, EU, AU Plug; Dual band network with wireless speed 688Mbps (2.4G)+2882Mbps (5G); Dual 2.5G Ethernet Ports (1x WAN and 1x LAN Port); USB 3.0 port.
- 【NETWORK CONTROL WITH TOUCHSCREEN SIMPLICITY】Slate 7’s touchscreen interface lets you scan QR codes for quick Wi-Fi, monitor speed in real time, toggle VPN on/off, and switch providers directly on the display. Color-coded indicators provide instant network status updates for Ethernet, Tethering, Repeater, and Cellular modes, offering a seamless, user-friendly experience.
- 【OpenWrt 23.05 FIRMWARE】The Slate 7 (GL-BE3600) is a high-performance Wi-Fi 7 travel router, built with OpenWrt 23.05 (Kernel 5.4.213) for maximum customization and advanced networking capabilities. With 512MB storage, total customization with open-source freedom and flexible installation of OpenWrt plugins.
- 【VPN CLIENT & SERVER】OpenVPN and WireGuard are pre-installed, compatible with 30+ VPN service providers (active subscription required). Simply log in to your existing VPN account with our portable wifi device, and Slate 7 automatically encrypts all network traffic within the connected network. Max. VPN speed of 100 Mbps (OpenVPN); 540 Mbps (WireGuard). *Speed tests are conducted on a local network. Real-world speeds may differ depending on your network configuration.*
- 【PERFECT PORTABLE WIFI ROUTER FOR TRAVEL】The Slate 7 is an ideal portable internet device perfect for international travel. With its mini size and travel-friendly features, the pocket Wi-Fi router is the perfect companion for travelers in need of a secure internet connectivity on the go in which includes hotels or cruise ships.
| Mode | What to consider |
|---|---|
| FakeTCP | Simulates some TCP features but remains UDP-based. The README warns it can be distinguished from real TCP. It requires kernel TCP packet processing to be blocked; the documented -a option can manage an iptables rule automatically. Review the implications for the platform and firewall before enabling it. |
| UDP | Use only where the network permits the UDP traffic pattern. The documentation does not establish that it will work through a network that blocks UDP. |
| ICMP | Use only where the network and both endpoints permit the required ICMP traffic. The documentation does not establish that it is available or preferred on every network. |
FakeTCP is not ordinary TCP, and neither it nor the other modes guarantees access through every blocked network or past every form of inspection. Follow the project’s current README for the mode’s options and firewall handling.
Troubleshoot a tunnel that connects but stalls
Check packet size and MTU if the tunnel establishes but larger transfers hang or fail. udp2raw warns that its raw-socket path does not support IP fragmentation, so packets exceeding the path MTU can cause warnings or delivery problems. Check the MTU on both ends and adjust cautiously; the project documentation does not support one universal MTU value for every route.
If udp2raw reports a “Huge packet” warning and GRO is involved, the project suggests trying --fix-gro. Confirm the warning’s context and the option’s current behavior in the project documentation before changing a live configuration.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
Quick Recap
- No connection: Verify that the local WireGuard endpoint targets the udp2raw listener, the client targets the correct remote udp2raw server, and the remote process forwards to the WireGuard UDP listener.
- Traffic loops or drops when WireGuard starts: Check the route to the udp2raw server IP. It must use the ordinary gateway, not the WireGuard interface.
- Only some destinations work: Inspect the configured
AllowedIPsprefixes and the routes installed by your client. A destination outside those prefixes will not be selected for that WireGuard peer. - Large transfers fail: Check MTU and packet-size warnings at both ends; fragmentation is not supported by udp2raw’s raw-socket path.
- FakeTCP mode fails unexpectedly: Review whether required privileges and firewall handling are in place, and remember that FakeTCP is not indistinguishable from normal TCP.
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

