Synopsys Coverity
Synopsys Coverity: Deep C/C++ analysis and safety compliance for regulated engineering teams. Ranked #14 of 27 in AI Code Security Scanners by our editors (8.1/10); pricing: Pricing on request; best for safety-critical C/C++ development.
At a glance
- Editor score8.1 / 10
- PricingPricing on request
- Best forSafety-critical C/C++ development
- Free planNo
- Facts checked27 Sep 2026
Where it wins
- Path-sensitive analysis models dependencies, dataflow and control flow
- Incremental pull-request scans and CI policy-based build breaks
- MISRA, AUTOSAR and CERT analyses with compliance reports
Where it doesn't
- Quote-based pricing requires a sales conversation
- No free plan is offered
- Focused C/C++ scope may not fit polyglot teams
Our verdict on Synopsys Coverity
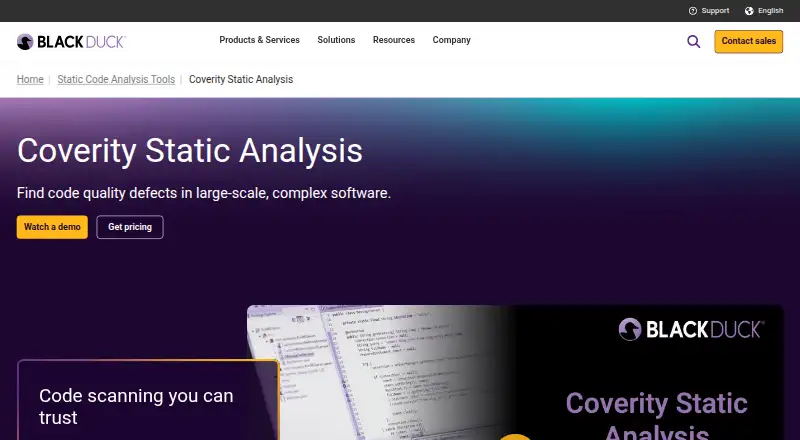
Synopsys Coverity is a static-analysis product for finding security vulnerabilities, quality defects and coding-standard violations in software. It is aimed at development and security teams managing large, safety-critical or regulated codebases, particularly C and C++ projects. Its analysis builds models across dependencies, compilers, dataflow and control flow, then supports incremental scans for commits and pull requests as well as full scans in CI/CD pipelines.
Pricing is quote-based, so adoption starts with a sales conversation rather than a published self-service plan. Coverity does not offer a free plan. Deployment options include cloud and self-hosted environments, with support for on-premises or private-cloud setups. The ecosystem includes Black Duck Bridge, the Code Sight IDE plug-in, CI/CD tools and source code management systems. Teams can also use the Point-and-Scan desktop application or command-line interface, while Code Sight provides issue descriptions and remediation guidance inside the IDE.
The product’s strongest depth is standards-driven analysis for regulated engineering. It covers MISRA, AUTOSAR, CERT C/C++, DISA STIG, ISO 26262, ISO 23434, ISO/IEC TS 17961, Hyundai Secure Coding, OWASP Top 10, CWE Top 25 and PCI DSS, with PDF compliance and trend reports. The Coverity Qualification Kit addresses safety-critical tool qualification, and custom checker extensibility can accommodate proprietary frameworks. Choose Coverity when path-sensitive C/C++ analysis, policy build breaks and safety evidence are central requirements. Teams seeking broad language coverage, a free entry tier or a wider modern application-security platform may find its specialized focus less suitable.
Your product? Our editors can test Synopsys Coverity in depth and publish a review, labelled as paid · from $149/mo →
Synopsys Coverity pricing
Synopsys Coverity fact sheet
| Free plan | No |
|---|---|
| Paid from | Not verified |
| Secrets detection | Not verified |
| Dependency scanning | Not verified |
| IDE integrations | Not verified |
| CI integrations | Not verified |
| AI fix suggestions | Not verified |
| Deployment model | Not verified |
| Supported languages | Not verified |
| Deployment | Cloud, Self-hosted |
| Platforms | Windows, macOS, Linux |
| Support | Community, Docs |
| Built for | Mid-market, Enterprise (editorial estimate) |
| Integrations | 4 integrations: Black Duck Bridge, Code Sight IDE plug-in, CI/CD tools, source code management systems |
| Pricing | Pricing on request (source) |
| Website | blackduck.com |
| Facts checked | 27 Sep 2026 |
Synopsys Coverity integrations
Synopsys Coverity lists 4 integrations on its own site.
- Black Duck Bridge
- Code Sight IDE plug-in
- CI/CD tools
- source code management systems
Alternatives to Synopsys Coverity
- Checkmarx OneEnterprise AppSec coverage from code scanning through governance and remediation.9.3
- OpenText Fortify Software Security PlatformA broad, hybrid AppSec suite for organizations standardizing security across the SDLC.9.2
- Snyk CodeBroad developer SAST with IDE, CI/CD, pull-request checks and AI-assisted fixes.9.1
See all Synopsys Coverity alternatives →
Used Synopsys Coverity? Be the first to review it
The editor score above is our own research. What this page doesn't have yet is a reader's view — what you used Synopsys Coverity for, what worked and what didn't. No stars are seeded and no review is paid for; an editor reads every one before it appears.
Write a reviewTwo minutes · verified accounts only · read by an editor before it appears
Featured on iTechGuides
Synopsys Coverity is listed in our AI Code Security Scanners directory. Add the badge to your site — it links back to this page.
<a href="https://www.itechguides.com/products/synopsys-coverity/"><img src="https://www.itechguides.com/best/badge/synopsys-coverity.svg" alt="Featured on iTechGuides" width="230" height="46"></a>
Reviewed by iTechGuides Editors · Editorial team · Updated Oct 2026
Advertiser disclosure: iTechGuides is reader-supported. Vendors can pay for top positions in our rankings and for a place on other products' pages, and we may earn a commission when you click some links. Bought places stand at the number bought; this page and our disclosure say so. Paying vendors may get a fuller, more detailed review from our editors, and that review can change their score. How we rank.
Last updated · How we research and update