ShadowStrike Phantom
ShadowStrike Phantom: A research-focused Windows defender for teams comfortable with pre-alpha software. Ranked #22 of 23 in Ransomware Protection Software by our editors (6.8/10); pricing: Open source; best for windows teams wanting open-source research depth.
At a glance
- Editor score6.8 / 10
- PricingOpen source
- Best forWindows teams wanting open-source research depth
- Paid fromFree
- Facts checked20 Sep 2026
Where it wins
- Kernel-level monitoring with attack-chain correlation and threat scoring
- Memory inspection covers injection, hollowing, shellcode, and ROP activity
- STIX/TAXII ingestion, honeypots, and backup-integrity checks
Where it doesn't
- Pre-alpha and explicitly not intended for production use
- Windows 10/11 x64 only
- Rollback and restoration are not established capabilities
Our verdict on ShadowStrike Phantom
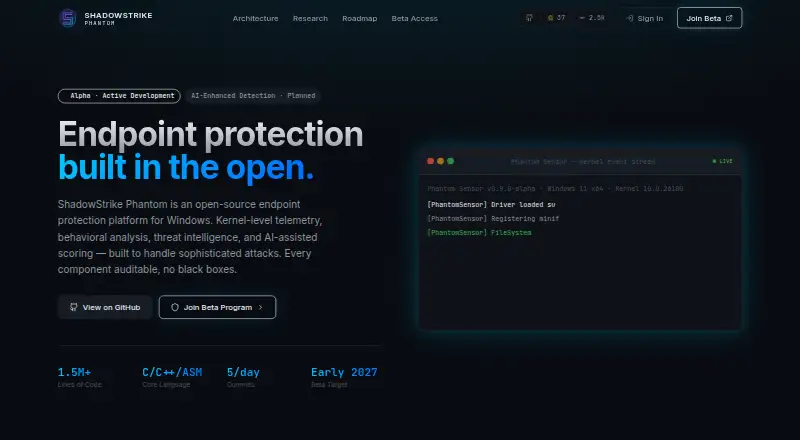
ShadowStrike Phantom is an open-source endpoint protection platform for Windows 10/11 x64. It is aimed at Windows teams that want visibility into ransomware behavior, malware activity, and attack chains, with detection infrastructure intended for endpoint, EDR, and XDR tiers. The project is currently pre-alpha, and the vendor states that it is not for production use, making it better suited to research, evaluation, and development environments than operational protection.
Its technical scope is broader than a basic ransomware blocker. Phantom combines a WDM minifilter driver for kernel-level file-system monitoring with user-space scanning, behavioral analysis, threat scoring, memory inspection, malware emulation, and on-device machine-learning classification. Ransomware-focused controls include honeypots, shadow-copy protection, backup-integrity checks, and entropy analysis. Memory inspection targets injection, process hollowing, shellcode, heap-spray, and ROP activity, while attack-chain correlation is designed to connect related behavior rather than treating individual events in isolation.
Threat-intelligence workflows are supported through STIX and TAXII ingestion, giving the platform a defined fit with those intelligence exchange formats. Anti-tamper controls and driver self-protection add protection around the detection components themselves. The main trade-offs are deployment scope and maturity: Phantom is Windows-only, operates as an on-premises product, and does not establish rollback or restoration as a verified capability. Windows teams seeking open-source research depth and advanced detection concepts should consider it for non-production evaluation. Organizations needing production-ready ransomware recovery, broader operating-system coverage, or a mature deployment should choose an alternative.
Your product? Our editors can test ShadowStrike Phantom in depth and publish a review, labelled as paid · from $149/mo →
ShadowStrike Phantom pricing
ShadowStrike Phantom fact sheet
| Free plan | Not verified |
|---|---|
| Paid from | Free |
| Rollback or recovery | Not verified |
| Behavioral detection | Yes |
| Automatic isolation | Not verified |
| Immutable recovery copy | Not verified |
| EDR included | Not verified |
| Deployment | On_premises |
| Operating system coverage | Windows |
| Deployment | Self-hosted |
| Platforms | Windows |
| Support | Community, Docs |
| Built for | Solo, Small business, Mid-market, Enterprise (editorial estimate) |
| Integrations | 2 integrations: STIX, TAXII |
| Pricing | Open source |
| Website | shadowstrike.dev |
| Facts checked | 20 Sep 2026 |
ShadowStrike Phantom integrations
ShadowStrike Phantom lists 2 integrations on its own site.
- STIX
- TAXII
Alternatives to ShadowStrike Phantom
- ManageEngine Ransomware Protection PlusA low-cost Windows option covering detection, isolation, rollback, and endpoint backups.9.4
- AEGISA technical, cross-platform platform for ransomware detection, response, and recovery.9.2
- Kaseya Ransomware ProtectionA layered endpoint-and-backup approach for organizations seeking ransomware prevention and recovery.9.0

See all ShadowStrike Phantom alternatives →
Used ShadowStrike Phantom? Be the first to review it
The editor score above is our own research. What this page doesn't have yet is a reader's view — what you used ShadowStrike Phantom for, what worked and what didn't. No stars are seeded and no review is paid for; an editor reads every one before it appears.
Write a reviewTwo minutes · verified accounts only · read by an editor before it appears
Featured on iTechGuides
ShadowStrike Phantom is listed in our Ransomware Protection Software directory. Add the badge to your site — it links back to this page.
<a href="https://www.itechguides.com/products/shadowstrike-phantom/"><img src="https://www.itechguides.com/best/badge/shadowstrike-phantom.svg" alt="Featured on iTechGuides" width="230" height="46"></a>
Reviewed by iTechGuides Editors · Editorial team · Updated Oct 2026
Advertiser disclosure: iTechGuides is reader-supported. Vendors can pay for top positions in our rankings and for a place on other products' pages, and we may earn a commission when you click some links. Bought places stand at the number bought; this page and our disclosure say so. Paying vendors may get a fuller, more detailed review from our editors, and that review can change their score. How we rank.
Last updated · How we research and update