
Recommended Free Tools
Biometric data is difficult to secure because it identifies your body rather than something you can simply replace. A stolen password can be changed; a compromised face, fingerprint, iris pattern or voiceprint usually cannot. Treat biometrics as sensitive, non-secret data: collect only what a defined purpose requires, protect templates throughout their lifecycle, test for spoofing and unequal error rates, limit retention, and pair biometric checks with a physical authenticator for high-value access.
Why a biometric breach is unusually difficult to fix
Biometrics are identifiers, not secrets
NIST SP 800-63B states that “Biometric characteristics do not constitute secrets.” A face can appear in a photograph, and a fingerprint can be recovered as a latent mark. Anyone who obtains a biometric sample may be able to attempt impersonation, link records belonging to the same person, or use the sample to attack another system.
For that reason, NIST recommends using biometrics with a physical authenticator in multi-factor authentication rather than treating a fingerprint or face scan as a standalone factor. A hardware security key or another possession factor can limit the damage if a biometric template is exposed.
Replacement is limited
Passwords, access tokens and cards can be revoked and reissued. You cannot readily issue a new face or fingerprint. A breach therefore creates long-term exposure and makes template protection, strict access controls, short retention periods and verified deletion more important than they are for ordinary credentials.
#1 Best Overall
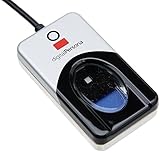
- Target Applications - Desktop PC security, Mobile PCs, Custom applications
- Indoor, home and office use
- Blue LED - soft, cool blue glow fits into any environment; doesn't compete in low light environments
- Small form factor - conserves valuable desk space
- Rugged construction - high-quality metal casing weighted to resist unintentional movement
The principal risks of biometric systems
Spoofing and presentation attacks
Cameras and sensors can be presented with artificial, altered or replayed characteristics. Examples include photographs, masks, lifted fingerprints, synthetic voices and manipulated video. NIST SP 800-63A requires presentation-attack detection for remote biometric collection and points to ISO/IEC testing methods. A system should document the attack scenarios tested, the detection method and the operating threshold; a marketing claim that a system is “highly accurate” is not a substitute for measured anti-spoofing performance.
Database compromise
Central biometric repositories concentrate valuable information. A successful intrusion can create monetary, personal and reputational harm, while also triggering legal duties. NIST’s SP 1800-28 guidance addresses identifying and protecting data assets, and SP 1800-29 covers detection, response and recovery. Minimize raw images and recordings, use protected templates where the application allows, and separate biometric systems from general identity records when practical.
Surveillance and function creep
Identification at a location can reveal that a person attended a healthcare provider, religious service, political event, union meeting or other sensitive place. The FTC warns that biometric surveillance can expose where people went and which services or meetings they attended. A collection originally justified for building entry can therefore become a tracking system if secondary uses, sharing or retention are not tightly constrained.
Unequal errors and discrimination
Biometric systems can have different false-match and false-non-match rates across demographic groups. A false match may allow the wrong person into an account or facility; a false non-match can deny access or impose repeated identity checks on particular populations. NIST SP 800-63A calls for demographic performance testing and meaningful reporting of limitations before and after deployment.
Rank #2

- New replacement old Red Logo Digital persona URU4500, HID , USB reader. Original HID Brand
- Small form factor
- Metal Casing resists unintentional movement.
- SuperiorRed "Flash" indicates that a fingerprint image has been captured, 512 dpi / 8-bit grayscale (256 gray levels) ESD resistance
- Encrypted fingerprint data
Deceptive claims and weak governance
The FTC has warned that unsupported accuracy claims, failure to assess foreseeable harms, inadequate vendor oversight, insufficient staff training and lack of post-deployment monitoring can create unfair or deceptive practices. Governance is part of security: an accurate sensor used for an unjustified purpose can still create unacceptable privacy and civil-rights risks.
National-security exposure
The U.S. Department of Justice identifies bulk biometric data among sensitive information whose access by foreign adversaries can create national-security risks. Organizations handling large datasets should include foreign access, cross-border transfers, subcontractors and remote administration in their threat model.
A practical biometric-security lifecycle
1. Define purpose and necessity
Write down the specific outcome the biometric is meant to achieve, such as identity proofing or access control. Compare it with less intrusive alternatives, including passwords, hardware keys, staffed verification or ordinary access cards. Do not collect a biometric merely because a device makes collection easy.
2. Explain the system before collection
Publish what is collected, whether the system keeps a raw sample or a derived template, how data is protected, who receives it, how long it is retained, and how an individual can request deletion. NIST SP 800-63A says providers must give clear, publicly available information about all biometric uses, storage and protection, and removal consistent with applicable law.
Rank #3

- High-quality metal casing
- Soft, cool blue glow fits into any environment
- Small form factor
- Works well with dry, moist, or rough fingerprints
3. Obtain explicit, informed consent
Consent should identify the purpose and material consequences in understandable language, without bundling unrelated uses. Keep a record tied to the relevant account or transaction, and provide a practical non-biometric option where the legal and operational context requires one.
4. Minimize and isolate data
- Prefer a protected template to retaining a full-resolution photograph, recording or scan when the use case permits.
- Collect only the fields and samples needed for the stated purpose.
- Separate biometric repositories from general customer or employee records when feasible.
- Restrict exports and prohibit unapproved copies in development, analytics and support environments.
5. Protect data technically
Use strong encryption in transit and at rest, managed keys, least-privilege access, multi-factor administrator authentication, immutable audit logs and continuous monitoring. Review who can retrieve or re-enroll a template, not only who can query a matching service. SP 1800-28 provides an architecture-oriented reference for identifying and protecting assets.
6. Test liveness and demographic performance
Run documented presentation-attack tests and measure false-match and false-non-match rates for the populations that will use the system. Record the data, test method, thresholds and confidence limits. Re-test after camera, model, firmware or threshold changes, and disclose material limitations to affected people and decision-makers.
7. Control vendors and onward disclosure
Contracts should specify permitted purposes, security controls, subcontractors, location of processing, breach notice, audit rights, deletion and return of data, and assistance with individual requests. Vet affiliates and service providers before deployment; train staff who enroll users or handle exceptions; and monitor production behavior for function creep.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
Rank #4

- Certified to Microsoft’s highest fingerprint security standards (ESS & SDCP) for robust, hardware-isolated authentication. Supports next-gen Windows features, including Copilot Recall and Windows Hello with ESS support.
- Windows Hello ready for fast, password free fingerprint login to Windows and Microsoft 365 accounts
- On device fingerprint storage keeps biometric data securely within the key. Supports privacy regulations (GDPR, BIPA, CCPA) through on device biometric processing; TAA compliant.
- Reliable wired USB fingerprint authentication with USB C and USB A compatibility for desktop PCs.
- Consistent, all condition 360° fingerprint recognition.
8. Set retention and deletion rules
Choose a short, purpose-linked schedule and trigger deletion when the purpose, account or legal basis ends. Define how backups, caches and vendor copies are removed, and keep evidence that destruction occurred. Illinois BIPA requires a public retention and destruction policy and provides a three-year backstop after the last interaction when the initial purpose has not already ended.
9. Prepare for incidents
A breach playbook should cover detection, containment, credential and template isolation, forensic preservation, legal notification analysis, communications, recovery and lessons learned. NIST SP 1800-29 treats response and recovery as part of the same lifecycle as protection. Because a biometric cannot simply be reset, consider compensating controls such as disabling biometric-only access, requiring a hardware authenticator and re-enrolling users with a safer method.
10. Review necessity continuously
At each renewal, expansion or major system change, ask whether the original purpose still exists, whether a less intrusive method now works, whether error disparities remain acceptable and whether retention can be shortened. A completed deployment is not the end of biometric risk management.
Independent reader supportYour contribution helps us test, update, and keep practical guides available for everyone.How privacy law treats biometric data
Requirements depend on the jurisdiction, the purpose of processing and whether the system identifies a person. The examples below are not legal advice and do not replace a local assessment.
Free tools Windows power users keep installed
One-click scans. No signup required.
Best Value

- BIOMETRIC SECURITY: USB fingerprint reader provides advanced biometric authentication to secure your computer and protect sensitive data with your unique fingerprint.
- ONE-TOUCH COMPUTER LOCK: Instantly lock your Windows computer with a single touch using the Win + L shortcut, providing quick security when stepping away from your desk.
- FAST AND ACCURATE SCANNING: High-precision optical sensor delivers reliable fingerprint recognition with quick response time for seamless login and authentication.
- PLUG AND PLAY CONVENIENCE: Simple USB connection with easy setup process allows you to start using fingerprint security within minutes without complex installation.
- COMPACT DESIGN: Sleek and portable biometric scanner features a space-saving footprint that fits comfortably on any desk without cluttering your workspace.
| Issue | UK GDPR | Illinois BIPA |
|---|---|---|
| Definition or trigger | Biometric data used to uniquely identify a natural person is special-category data under Article 9. | “Biometric identifier” includes a retina or iris scan, fingerprint, voiceprint, or scan of hand or face geometry. |
| Legal basis or consent | Identification use generally requires an Article 6 lawful basis and an Article 9 condition. | Written notice describing collection and purpose and a written release are required before collection or use. |
| Retention and deletion | Specific retention and deletion duties depend on the applicable principles, policies and circumstances; not stated as a single period in the cited guidance. | A publicly available retention/destruction policy is required; a three-year backstop applies after the last interaction when the purpose has not ended sooner. |
| Sale and onward disclosure | Restrictions depend on the lawful basis, transparency and other UK GDPR requirements; no single prohibition is stated in the cited guidance. | Section 15 limits sale and disclosure of biometric identifiers and information. |
| Security | Appropriate technical and organizational measures are required under the risk-based framework; exact controls depend on context. | Protection must be at least as strong as that used for other confidential and sensitive information. |
| Individual rights and remedies | Rights and regulator remedies depend on the processing context and applicable UK GDPR provisions; not stated as a single biometric-specific rule here. | Statutory duties apply to collection, disclosure, retention and destruction; available remedies and litigation exposure should be reviewed with Illinois counsel. |
UK GDPR: identification biometrics are special category
The UK Information Commissioner’s Office explains that Article 9(1) includes “biometric data for the purpose of uniquely identifying a natural person” among special categories of personal data. An organization must therefore identify both an Article 6 lawful basis and an Article 9 condition, document necessity and proportionality, and provide transparent information about the processing.
Illinois BIPA: written notice, release and policy
Section 15 of Illinois BIPA requires written notice of collection and purpose, a written release, limits on sale and disclosure, safeguards for the information, and a public retention and destruction policy. The statute’s definition covers retina or iris scans, fingerprints, voiceprints and scans of hand or face geometry. Organizations operating across states should not assume that a policy designed for another jurisdiction satisfies BIPA.
Questions to ask before approving a biometric deployment
- What precise problem does the biometric solve, and why is a less intrusive method inadequate?
- Is the system performing verification against a claimed identity or identification among many people?
- What raw samples, templates, logs and metadata are stored?
- Can a person use a physical authenticator or another accessible alternative?
- What are the measured false-match, false-non-match and presentation-attack results for the intended population?
- Who can enroll, re-enroll, export, delete or override a match?
- Which vendors, affiliates and subprocessors can access the data, from which countries?
- When exactly is each copy deleted, including backups and test environments?
- How will the organization respond if templates, keys or matching services are compromised?
- What evidence will demonstrate consent, testing, access reviews, deletion and incident exercises?
Bottom line
Biometric security is not a matter of buying a better scanner. It requires a defensible purpose, informed consent, minimized and protected templates, tested anti-spoofing and demographic performance, strict retention and vendor controls, and a response plan that recognizes a face or fingerprint cannot be reset. Use biometrics as one part of multi-factor security—not as a secret—and verify the legal requirements for every jurisdiction in which the system operates.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

