
To verify Android security state, check cryptographic evidence rather than relying on the Android version or a security-patch date shown in settings. An app can validate a hardware-backed Key Attestation certificate chain and inspect its RootOfTrust data. For an image or device inspected directly, verify the AVB chain against the expected signing root and examine version and patch metadata for each relevant partition. These checks answer different questions: offline image verification does not prove that image is running, and runtime attestation is not a complete review of every partition or fix.
What does Android security-state verification establish?
Android Verified Boot establishes a chain of trust rooted in protected hardware. It verifies executable code and data before use; larger filesystems may also be checked continuously with dm-verity. A failed boot-time check can prevent boot, while runtime verification errors have separate handling. The Android Open Source Project describes the requirement this way: “Verified Boot requires cryptographically verifying all executable code and data that is part of the Android version being booted before it’s used.”
Keep three questions separate: whether the boot chain is trusted, whether the relevant software reports the required version and patch levels, and whether a specific set of vulnerabilities has actually been fixed. Boot-state evidence addresses the first question. Partition metadata informs the second. The third requires comparing the device’s declared levels and build with the relevant security bulletins and OEM release information.
How can an app verify the state of the running device?
An app should not treat a client-provided flag such as “verified” or “not rooted” as proof. Instead, use a key with attestation, obtain its certificate chain, and have a trusted backend validate and interpret the chain and its structured attestation extension. Apply any required revocation or provisioning checks as part of the backend’s policy.
#1 Best Overall

- 【Strong Adsorption】The inspiration of the silicone phone suction case comes from the adhesive force of the octopus. Each suction cup phone mount is 3.15 inches long and 2.17 inches wide, with 24 independent suction cups providing a stronger and more stable suction force, so you don't have to worry about your phone falling during use.
- 【Back of Phone Suction Grip】Remove the adhesive film on the phone suction cup and stick it on the phone case. You can then fix the phone on any smooth surface, which is very convenient. (The phone suction cup cannot be removed and reused after being attached to the phone case. It is recommended to attach it to a regular phone case, not a valuable one.)
- 【Widely Used】Our non-slip silicone phone sticky grip mount attaches to almost any flat phone case and make it compatible with common mobile phones such as iPhone and Android.You can shoot, watch videos or video calls in the kitchen, gym, dance studio, bathroom and other places.
- 【Capture the Wonderful Picture】Whether you are a TikTok creator or just like to share videos and photos, this phone suction cup can help you hands-free capture wonderful videos and photos for sharing with friends.
- 【Note】You can fix the phone suction cup on a smooth surface such as a mirror or glass. If necessary, wipe the suction cup with a damp cloth to obtain stronger suction. Before releasing your hand, make sure the phone is firmly fixed. (Not applicable to rough walls, wooden surfaces, and other uneven surfaces)
- Validate the certificate chain. Confirm that the chain is valid under the trust policy your service expects. The chain is evidence to evaluate, not a boolean the client can assert.
- Parse RootOfTrust. Record
verifiedBootKey,deviceLocked,verifiedBootState, andverifiedBootHash. Compare the key or root with the expected trust root for the device or policy. - Interpret the fields together. A locked state, boot state, and boot hash provide different evidence. Do not infer patch freshness from lock status, or assume every state called Verified means the manufacturer’s factory root was used.
- Check version-gated patch tags if policy requires them. Attestation may contain OS, vendor, and boot patch-level tags. AOSP documents
vendorPatchLevelandbootPatchLevelas present in attestation versions 3 or later. A missing tag is not evidence of a zero or current patch level. - Evaluate app identity separately.
AttestationApplicationIdreflects the platform’s belief about packages allowed to use the key, including package names and versions and signing-certificate digests. It is app-identity evidence, not a substitute for RootOfTrust evaluation.
How should RootOfTrust states be interpreted?
The state and lock fields describe the boot configuration and verification result. Their meaning depends on the trust root expected by the app or device policy.
| Evidence | What it supports | Limit |
|---|---|---|
deviceLocked = true |
The attestation says the bootloader is locked and a signed image successfully passed Verified Boot. | Identify the signing root and consider the state and hash too. Lock status alone says nothing conclusive about patch coverage. |
| Verified / GREEN | A chain extends from a hardware-protected root through the bootloader and verified partitions. | Compare the root key with policy; an approved test-device exception is documented. |
| SelfSigned / YELLOW | Verification used a user-configured root. | This is not equivalent to verification under the factory root. |
| Unverified / ORANGE | The bootloader is unlocked, so the chain of trust cannot be established and software may be freely modified. | Integrity must be assessed out of band. |
| Failed / RED | Verification failed. | Other RootOfTrust values are not guaranteed. |
LOCKED and UNLOCKED describe flashing and enforcement states. A locked device verifies against a root of trust; an unlocked device can boot modified software after a warning. Because a user-configured root is possible, a successful verification state does not by itself identify the signer as the manufacturer.
Rank #2

- SUPERIOR COMFORT — Unlike traditional circular ear buds, the design of EarPods is defined by the geometry of the ear. Which makes them more comfortable for more people than any other ear bud–style headphones.
- HIGH-QUALITY AUDIO — The speakers inside EarPods have been engineered to maximize sound output and minimize sound loss, which means you get high-quality audio.
- BUILT-IN REMOTE — EarPods with USB-C plug also include a built-in remote that lets you adjust the volume, control the playback of music and video, and answer or end calls with a pinch of the cord.
- COMPATIBILITY — Works with all devices that have a USB-C port.
- INTEGRATED MICROPHONE — A built-in microphone precisely captures your voice while you’re on the phone, taking a FaceTime call, or summoning Siri — so you’re always heard loud and clear.
How do you verify an image or device under direct inspection?
For an image, build, or device you can inspect directly, start with the expected root of trust. A valid signature proves a relationship to a key; it does not prove that the key belongs to the expected OEM or is authorized by your policy.
- Establish the expected signing root. Obtain it from a trusted release source or device policy. Determine whether the policy expects a manufacturer root, a delegated key, or an explicitly authorized user root.
- Inspect the AVB metadata and chain. Use appropriate AOSP tooling to verify the relevant partition hashes and signatures, rollback indexes, and actual
vbmetachain. AVB supports delegated partition updates and rollback protection, so do not assume one signature check covers every relevant partition. - Record partition-specific version and patch properties. Check the applicable system, system_ext, product, boot, vendor, and other partitions in the device’s topology. AOSP examples include
com.android.build.system.security_patchandcom.android.build.vendor.security_patch; the bootloader can obtain AVB properties fromvbmeta. - Compare the reported levels with release information. Match each relevant partition’s patch level and build to the device vendor’s bulletin and build details. Android’s SPL requirements are cumulative, but a metadata value alone does not prove that every claimed fix was correctly integrated.
- Keep offline and runtime conclusions distinct. An offline image can be valid without being the image currently booted. Runtime attestation binds evidence to the running device, but does not replace a full image review when policy requires one.
Why aren’t Android version and patch date enough?
AVB stores OS-version and security-patch values as separate metadata, and values can differ by partition. A single displayed patch date cannot establish the state of every relevant partition. Nor does a patch date prove signature validity, show that the inspected image is the one currently running, or establish that all fixes associated with that level are present.
Rank #3

- Secure Hold: Our PopSockets adhesive phone grip gives your cell phone a secure, comfortable hold in hand to help prevent drops while texting, taking photos, or scrolling on the go. Designed to stick firmly to most phone cases and devices.
- Hands-Free Made Easy: Easily turn your PopSocket into a phone stand to prop up your phone anywhere, perfect for watching videos, video calls, or following recipes. A must-have phone holder that keeps your device secure and ready for anything.
- Compatibility: Works with all phones, tablets, and Kindles. Sticks best to smooth, hard plastic cases and may not adhere to silicone or textured cases. Easily swap your PopTop to change up your style.
- Black PopSockets: Simple, refined, and endlessly versatile. A timeless essential for any phone.
- Travel Must-Have for People On the Go: A must-have travel accessory for flights, flying, airports, air travel, airplanes, planes, international trips, cruises, and long travel days. Key gadget for your airport haul, travel accessories and must-haves.
For a concrete device, the expected values depend on its model, build fingerprint, bootloader policy, partition layout, attestation version, OEM trust roots, and vendor release information. Check the applicable Android release and device-specific documentation rather than applying one device’s expected values to another.
Quick Recap
Best Value
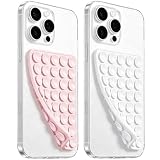
- 【PKYAA Double Sided Silicone Suction Phone Case Mount】PKYAA With Double Sided 40 Strong and Reliable individual suction cups, PKYAA provides a thicken and upgraded universal silicon suction mount for your phone.
- 【Friendly to Content Creators】If you are a content creator or an online influencer, you can create videos anywhere with this suction mount completely hands free with this silicone cell phone mount for cases.
- 【HANDS-FREE & Adhere to Mirrors】This Double Sided silicone suction phone case mount allows you to stick your phone to the mirror easily. No longer holding your phone in one hand to watch video tutorials while making up.
- 【Strong Grip on the Smooth Surface】You can easily hang your phone anywhere with a smooth surface. All you do is you clean off your phone and smooth surface. It is STURDY and it not only sticks to mirrors, it also sticks to windows, it sticks to refrigerators, tiles and other clean, flat surfaces.
- 【Press Down Firmly Every 30 Minutes】Use your palm or fingers to press the phone down firmly and check it's secure before letting go. Apply even pressure for a few seconds to allow the suction cup to adhere properly. To maintain the grip and prevent accidental falls, it's a good practice to periodically reapply pressure to the suction cup.
Rank #4

- [360 ° Flexible Rotation Design] Comes with a rotatable lanyard ring that supports 360 ° free rotation, effectively solving the problem of twisted and tangled lanyards
- [Wide compatibility] The ultra-thin 0.02-inch design does not block the charging port at all, and both wired and wireless charging can be used directly without removing the pad. Compatible with most smartphones such as iPhone, compatible with various wristbands, lanyards, crossbody straps, and keychains
- [Durable and Portable Material] Premium rust-resistant stainless steel material with good flexibility, which not only avoids scratching the phone case, but also has excellent anti rust and anti fading performance
- [Multi scenario Practical] Paired with a lanyard or wristband, hands-free use can be achieved. The phone is within reach and not easily dropped, ideal for daily commuting and outdoor activities. Suitable for full coverage phone cases, does not support half coverage phone cases
- [Quality Service] If you find any damage or other issues with the product upon receipt, please contact us immediately. We will handle it quickly
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

